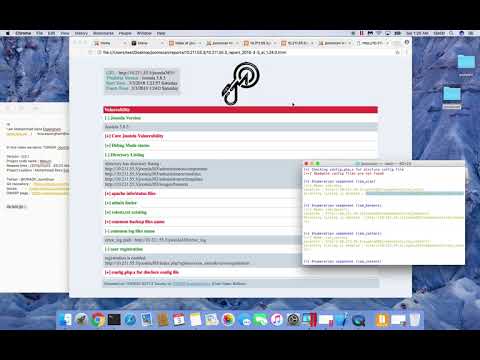
 安全软件
点击放大
joomscan - OWASP Joomla Vulnerability Scanner Project https:/
项目说明
! 0.0.7
!Perl
![GPLv3 License]()
![Twitter]()
![Leader]()
![Leader]()
<br>
![Black Hat Arsenal USA]()
![Black Hat Arsenal ASIA]()
<img src=" width="200"><img src=" width="500">
======
OWASP JoomScan Project
======
OWASP Joomla! Scanner (JoomScan) is an open source project, de with the aim of automating the task of detection and reliability assurance in Joomla CMS deployments. Implemented in Perl, this tool enables seamless and effortless scanning of Joomla installations, while leaving a minimal footprint with its lightweight and modular architecture. It not only detects known offensi, but also is able to detect many misconfigurations and admin-le that can be exploited by ad to compromise the system. Furthermore, OWASP JoomScan provides a user-friendly interface and compiles the final reports in both text and HTML formats for ease of use and minimization of reporting o.
<br>
OWASP JoomScan is included in Kali Linux distributions.
* Read More:
WHY OWASP JOOMSCAN ?
Automated ...<br>
* enumerator<br>
* enumerator (based on )<br>
*Components enumerator (1209 most popular by default)<br>
*Components enumerator (based on )(+1030 exploit)<br>
*Firewall detector<br>
*Reporting to Text & HTML output<br>
*Finding common log files<br>
*Finding common backup files<br>
INSTALL
git clone
cd joomscan
perl joomscan.pl
For Docker installation and usage
# Build the docker image
docker build -t rezasp/joomscan .
# Run a new docker container with reports directory mounted at the host
docker run -it -v /path/to/reports:/home/joomscan/reports --name joomscan_cli rezasp/joomscan
# For accessing the docker container you can run the following command
docker run -it -v /path/to/reports:/home/joomscan/reports --name joomscan_cli --entrypoint /bin/bash rezasp/joomscan
JOOMSCAN ARGUMENTS
Usage: joomscan.pl [options]
--url | -u <URL> | The Joomla URL/domain to scan.
--enumerate-components | -ec | Try to enumerate components.
--cookie <String> | Set cookie.
--user-agent | -a <user-agent> | Use the specified User-Agent.
--random-agent | -r | Use a random User-Agent.
--timeout <time-out> | set timeout.
--about | About Author
--update | Update to the latest .
--help | -h | This help screen.
-- | Output the current and exit.
OWASP JOOMSCAN USAGE EXAMPLES
Do default checks...<br>
<br>
or<br>
<br>
<br>
Enumerate installed components...<br>
<br>
or<br>
<br>
<br>
Set cookie<br>
<br><br>
Set user-agent<br>
<br>
or<br>
<br>
<br><br>
Set random user-agent<br>
<br>
or<br>
<br>
<br>
Set proxy<br>
<br>
or<br>
<br>
<br><br>
Update Joomscan...<br>
<br><br>
OWASP PAGE
GIT REPOSITORY
ISSUES
PROJECT LEADERS
* Mohammad Reza Espargham [ reza[dot]espargham[at]owasp[dot]org ]
* Ali Razmjoo [ ali[dot]razmjoo[at]owasp[dot]org ]
<br><br>
OWASP JoomScan introduction (Youtube)
![OWASP JoomScan introduction]()
项目信息
开发语言:Raku
Star 数:1197
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕OWASP Joomla Vulnerability Scanner Project
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | joomscan - OWASP Joomla Vulnerability Scanner Project https:/ |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:33:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 352 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |