 安全软件
点击放大
CORScanner - 🎯 Fast CORS misconfiguration vulnerabilities scann
项目说明
About CORScanner
CORScanner is a python tool designed to discover CORS misconfigurations of websites. It helps website administrators and penetration testers to check whether the domains/urls they are targeting ha CORS policies.
Features
* Fast. It uses gevent instead of Python threads for concurrency, which is much faster for network scanning.
* Comprehensive. It covers all the common types of CORS misconfigurations we know.
* Flexible. It supports self-define features (e.g. file output), which is helpful for large-scale scanning.
* 🆕 CORScanner supports installation via pip (
pip install corscanner or pip install cors)* 🆕 CORScanner can be used as a library in your project.
Two useful references for understanding CORS systematically:
* USENIX security 18 paper: We Still Don’t Ha Cross-Domain Requests: an Empirical Study of CORS
* 中文详解:绕过浏览器SOP,跨站窃取信息:CORS配置安全漏洞报告及最佳部署实践
<details><summary>Please consider citing our paper if you do scentific research (Click me). </summary>
<p>
*Latex :*
*Word :*
Jianjun Chen, Jian Jiang, Haixin Duan, Tao Wan, Shuo Chen, Vern Paxson, and Min Yang. "We Still Don’t Ha Cross-Domain Requests: an Empirical Study of CORS." In 27th USENIX Security Symposium (USENIX Security 18), pp. 1079-1093. 2018.
</p>
</details>
Screenshots
!CORScanner
Installation
CORScanner depends on the requests, gevent, tldextract, colorama and argparse python modules.
Python :
* Both Python 2 (2.7.x) and Python 3 (3.7.x) are supported.
CORScanner as a library
or use the short name:
You can also use CORScanner via the corscanner or cors command: cors -://www.instagram.com
Usage
Short Form | Long Form | Description
------------- | ------------- |-------------
-u | --url | URL/domain to check it's CORS policy
-d | --headers | Add headers to the request
-i | --input | URL/domain list file to check their CORS policy
-t | --threads | Number of threads to use for CORS scan
-o | --output | Save the results to json file
-v | -- | Enable the mode and display results in realtime
-T | --timeout | Set requests timeout (default 10 sec)
-p | --proxy | Enable proxy (http or socks5)
-h | --help | show the help message and exit
Examples
* To check CORS misconfigurations of specific domain:
`python cors_scan.py -u example.com
* To enable more debug info, use -v:
python cors_scan.py -u example.com -v
* To save scan results to a JSON file, use -o:
python cors_scan.py -u example.com -o output_filename
* To check CORS misconfigurations of specific URL:
python cors_scan.py -u
* To check CORS misconfiguration with specific headers:
python cors_scan.py -u example.com -d "Cookie: test"
* To check CORS misconfigurations of multiple domains/URLs:
python cors_scan.py -i top_100_domains.txt -t 100
* To enable proxy for CORScanner, use -p
To use socks5 proxy, install PySocks with pip install PySocks
* To list all the basic options and switches use -h switch:
Misconfiguration types
This tool covers the following misconfiguration types:
Misconfiguration type | Description
------------------------ | --------------------------
Reflect_any_origin | Blindly reflect the Origin header value in Access-Control-Allow-Origin headers in responses, which means any website can read its secrets by sending cross-orign requests.wwww.example.com
Prefix_match | trusts example.com.evil.com, which is an attacker's domain.wwww.example.com
Suffix_match | trusts e.com, which could be registered by an attacker.wwww.example.com
Not_escape_dot | trusts wwwaexample.com, which could be registered by an attacker.wwww.example.com
Substring match | trusts example.co, which could be registered by an attacker.wwww.example.com
Trust_null | trusts null, which can be forged by iframe sandbox scriptsgithub.io
HTTPS_trust_HTTP | Risky trust dependency, a MITM attacker may steal HTTPS site secrets
Trust_any_subdomain | Risky trust dependency, a subdomain XSS may steal its secrets
Custom_third_parties | Custom unsafe third parties origins like , see more in origins.json file. Thanks !_`, which can also work in Chrome and Firefox. See more in Ad CORS Exploitation Techniques. Thanks .
Special_characters_bypass| Exploiting browsers’ handling of special characters. Most can only work in Safari except
Welcome to contribute more.
Exploitation examples
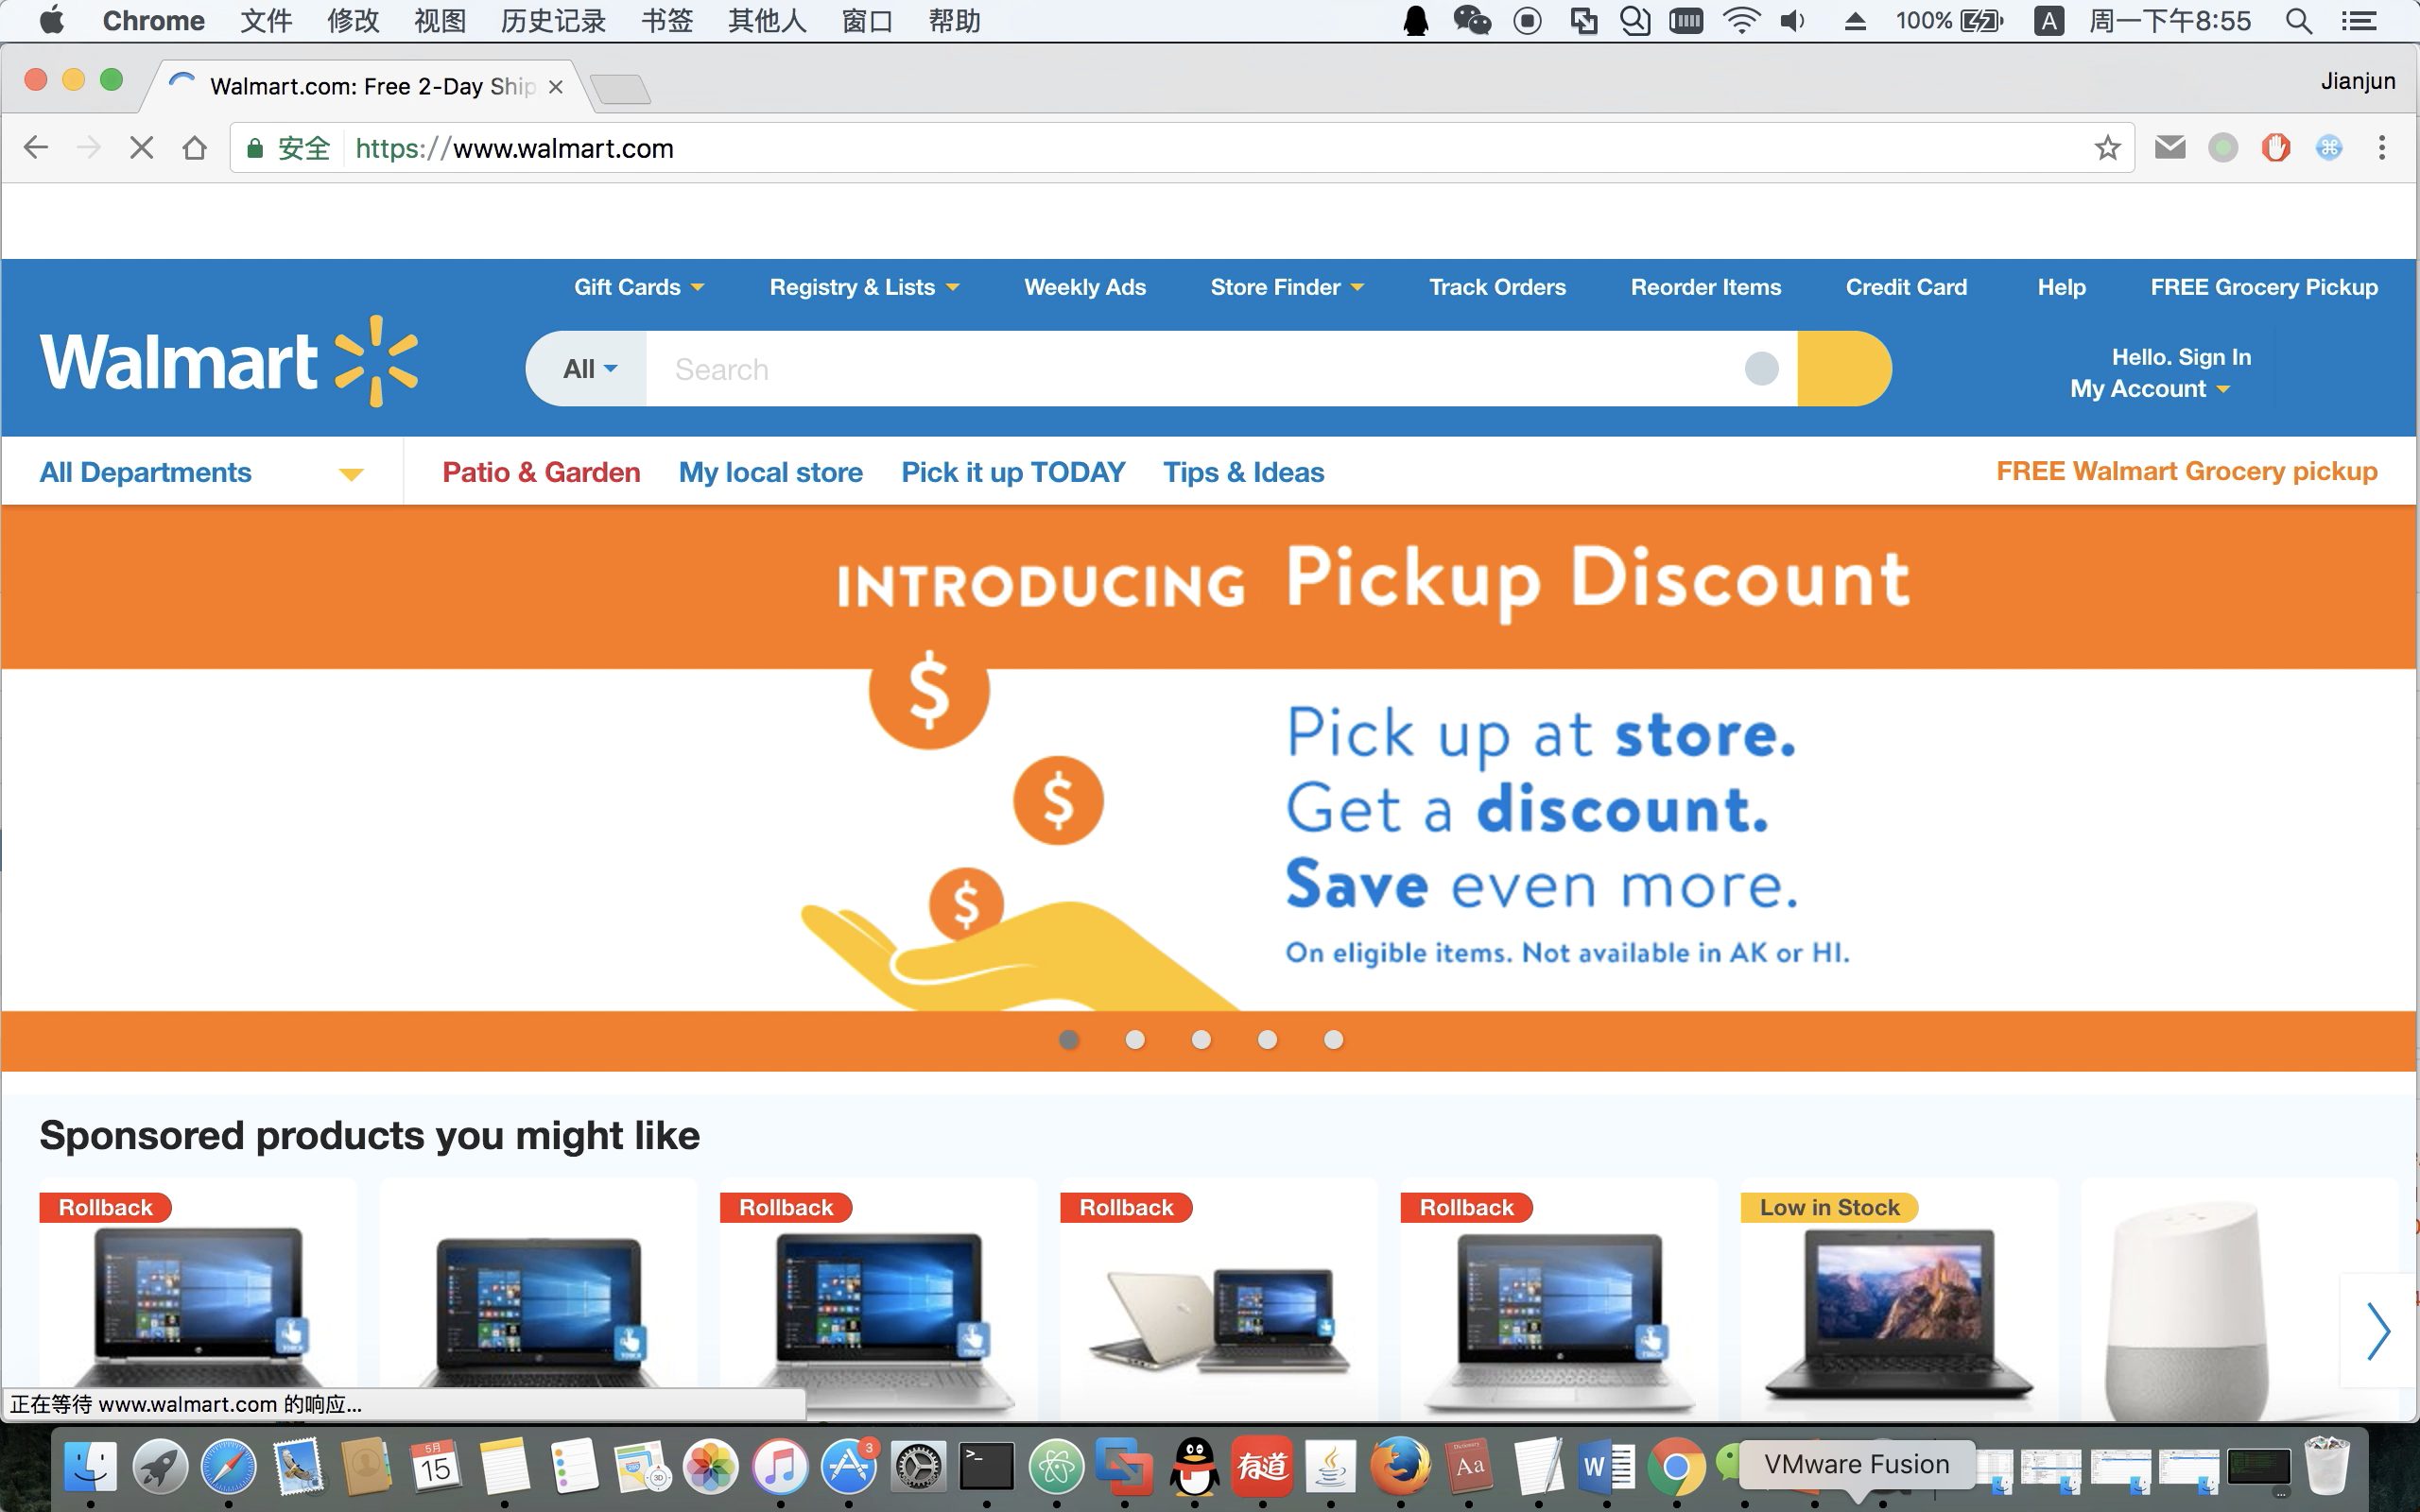
Here is an example about how to exploit "Reflect_any_origin" misconfiguration on Walmart.com(fixed). Localhost is the malicious website in the video.
Walmart.com video on Youtube:
![Walmart_CORS_misconfiguration_exploitation]()
Here is the exploitation code:
If you ha how the demo works, you can read Section 5 and Section 6 of the CORS paper and know how to exploit other misconfigurations.
License
CORScanner is licensed under the MIT license. take a look at the LICENSE for more information.
Credits
This work is inspired by the following excellent researches:
* James Kettle, “Exploiting CORS misconfigurations for Bitcoins and bounties”, AppSecUSA 2016*
* E, “Misconfigured CORS and why web appsec is not getting easier”, AppSecUSA 2016*
* Von Jens Müller, "CORS misconfigurations on a large scale", CORStest*
项目信息
开发语言:Python
Star 数:1164
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🎯 Fast CORS misconfiguration vulnerabilities scanner展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | CORScanner - 🎯 Fast CORS misconfiguration vulnerabilities scann |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:34:05 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 471 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |