 安全软件
点击放大
vigolium - Vigolium - High-fidelity vulnerability scanner fus
项目说明
<p align="center">
<img alt="" src=" height="140" />
<br />
<strong> - High-fidelity scanner fusing agentic AI with nati, modularity, and precision</strong>
<p align="center">
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
</p>
</p>
***
provides two complementary scanning modes:
scan): Fast, powerful, and flexible. Deterministic, multi-phase scanning with 317 modules across content discovery, browser/SPA spidering, and acti audit, co injection, access control, file/path, API/protocol, framework-specific, cloud/infra, and out-of-band (OAST) classes. agent): Thoroughly audits your codebase. AI-dri that autonomously plans attacks, selects modules, generates custom extensions, and triages results, combining deep source-code audit with autonomous and targeted scanning.Installation
Quick Install (Recommended)
npm
Windows
The npm install abo on Windows. Alternatively, download<>_windows_amd64.zip from the
releases page, extract it, and
put .exe somewhere on your PATH.
> Windows ships as x64 only; on Windows ARM it runs under emulation. The shell
> installer above is POSIX-only, so update is not a on
> Windows — re-run the npm install or download the newer zip to upgrade.
<details>
<summary>Other method like Docker or Build from source</summary>
Docker
Build from Source
Requires Go 1.27+ and bun 1.3.11+. See HACKING.md for prerequisites and build details.
</details>
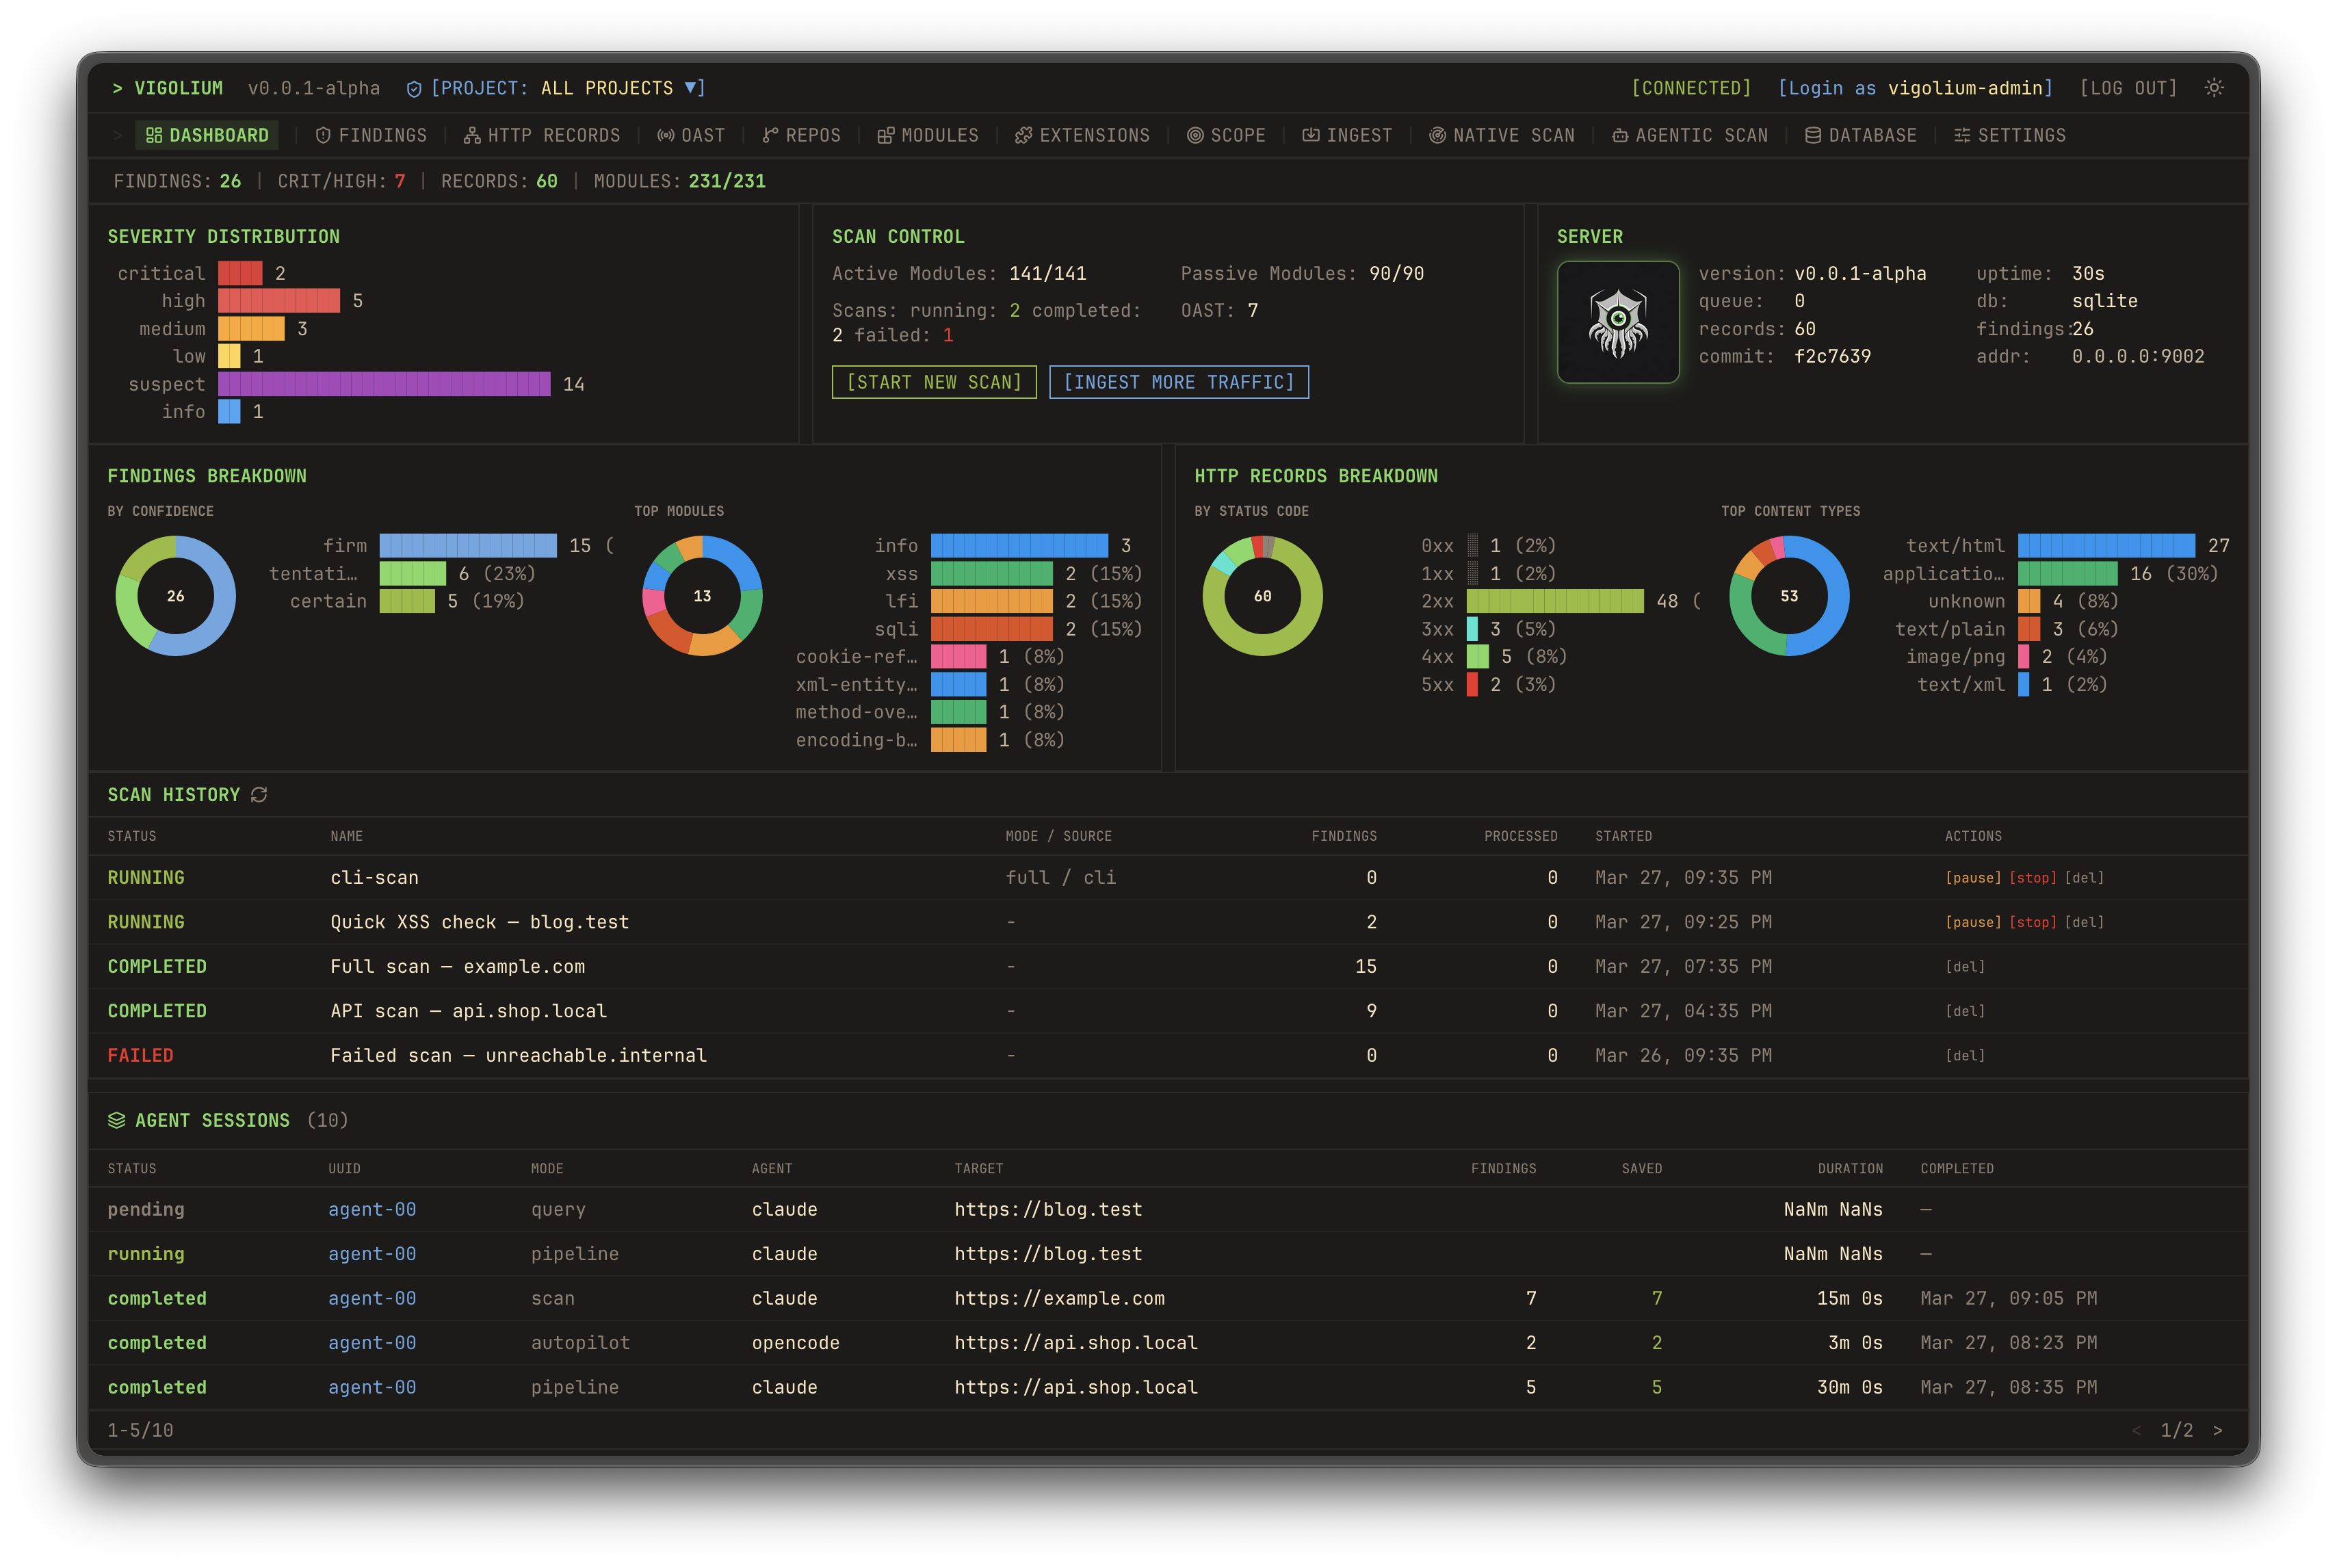
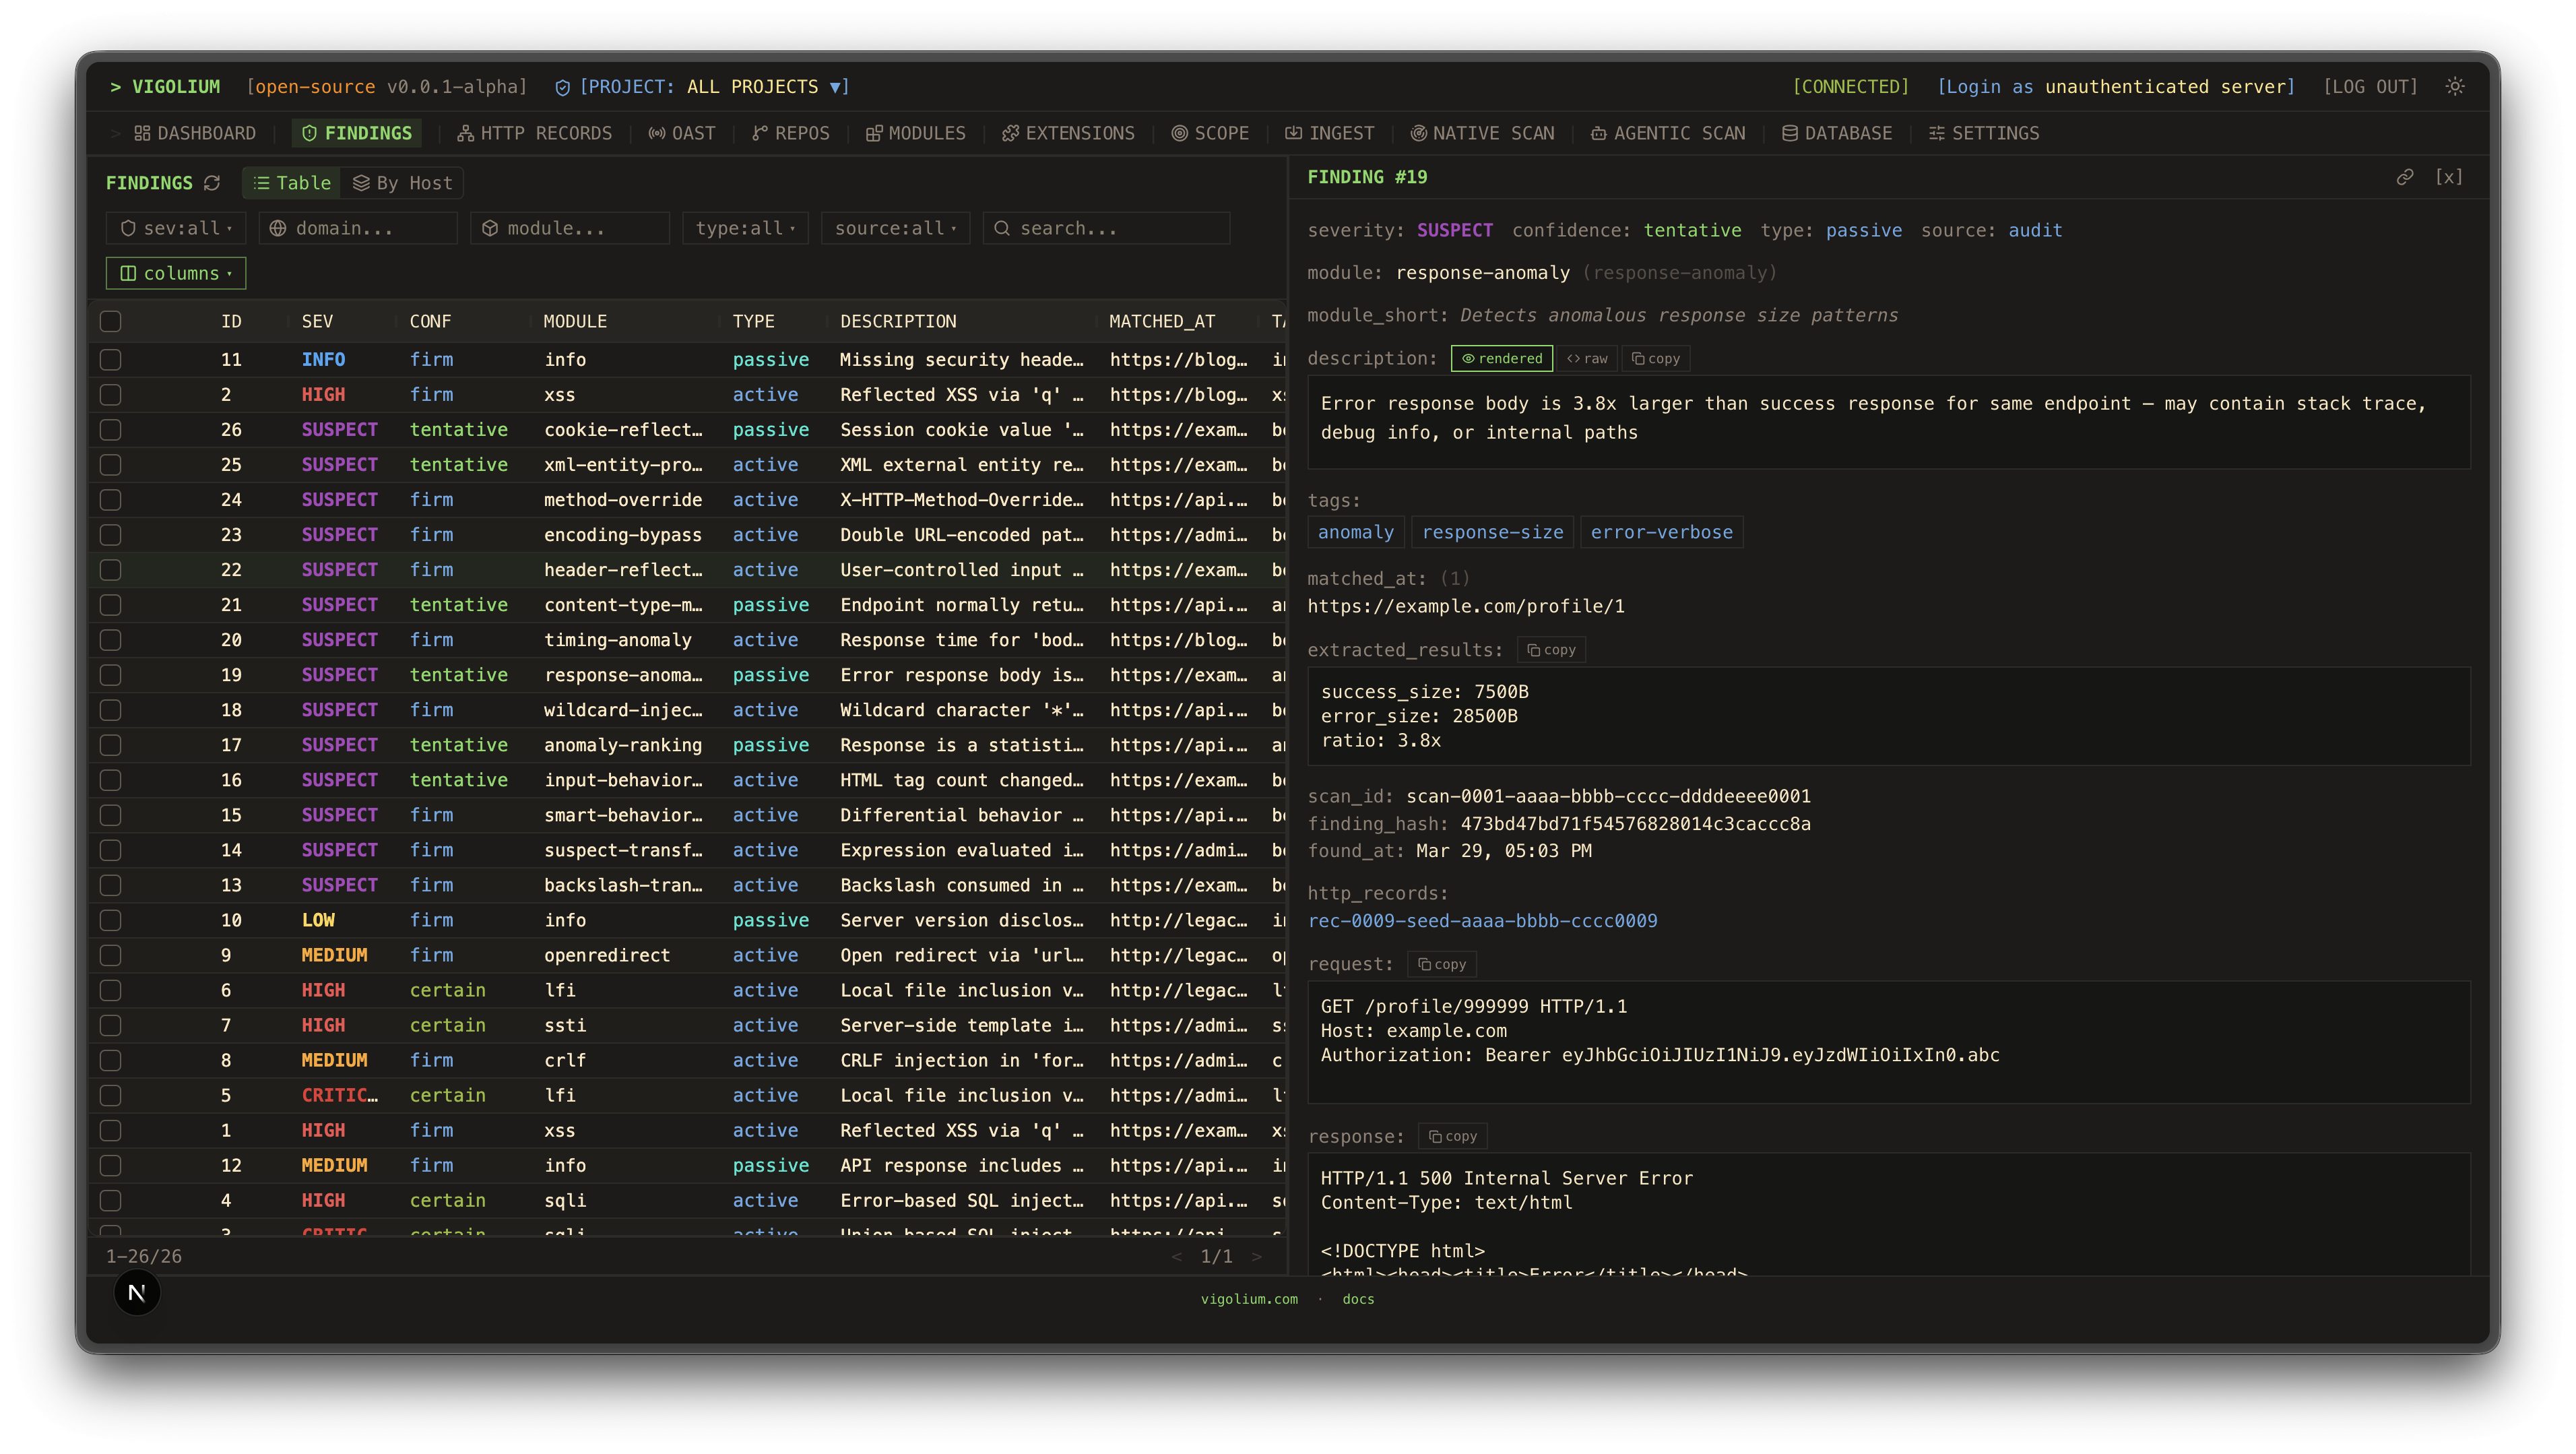
| UI Dashboard | Traffic Dashboard |
|:---:|:---:|
| !Dashboard 1 | !Dashboard 2 |
| Static Reports | Static Reports |
|:---:|:---:|
| !Static Report 1 | !Static Report 2 |
| Native scan | Agentic Scan |
|:---:|:---:|
| !Native scan | !Agentic Scan |
Sponsor
<p align="center">
<a href=" alt="Daytona" src=" height="28" /></a>
<br />
<sub>Thank you to <a href=" for sponsoring the sandbox infrastructure</sub>
</p>
Key Features
Native Scan
Agentic Scan
pkg/olium engine: turn-based loop, built-in tool registry, skills support, and pluggable provider drivers (no subprocess SDK pools)--discover), with --diff/--last-commits for change-focused runsaudit, piolium, and the unified audit dispatcher run foreground source-code audits sharing one finding schema and DB taggingopenai-compatible (default), openai-codex-oauth, openai-api-key, openai-responses, anthropic-api-key, anthropic-oauth, anthropic-cli, anthropic-compatible, anthropic-, google-. Same modes exposed over the REST API with SSE streaming and an OpenAI-compatible chat endpointQuick Start: Native Scan
See the architecture o for the full pipeline and the strategies guide for strategies, profiles, and pace configuration. For a quick command reference, see docs..com/getting-started/cheat-sheet.
Server Mode
See running the server for ser, ingestion for ingestion workflows, and the API o for the full REST API reference.
> Proxy integrations: forward li traffic to a running server with the burp- extension for Burp Suite or the caido- plugin for Caido. Both serve the same bridge protocol (-B/--burp-bridge-url, alias --caido-bridge-url), and ingested traffic is labelled with the proxy it came from.
Authenticated Scanning
supports multi-session authenticated scanning for IDOR/BOLA testing and pri escalation checks:
Auth files support static headers, bearer tokens, and automated login flows with token extraction from cookies, JSON responses, or headers. Preset examples are a in public/presets/sessions/. See the authentication guide for the full guide.
> The --auth / --auth-file flags were pre named --session / --session-file. The old names still work as deprecated aliases.
Agentic Scan
AI-dri where agents autonomously plan, execute, and triage assessments with the native scan engine underneath:
Agentic scan modes:
pkg/olium/autopilot.Run directly; the server adds prep, auth setup, and a frozen context bundle around the same loop--discover). Master agent analyzes inputs, selects modules, generates custom JS extensions, runs code audit and SAST, executes scans, and triages results agent audit — a unified dispatcher that runs the embedded (claude/codex) and/or piolium (Pi-nati, selected with --driver {auto|both|audit|piolium} (default auto: preflight the audit leg and run it when the resolved claude/codex CLI is on PATH, the binary is embedded, and the chain has an audit-supported mode; otherwise fall back to piolium without launching audit. A mid-run audit failure surfaces rather than switching drivers). Separate harnesses; do not route through olium. Per-dri rows under one parent AgenticScan with post-pass findings dedup. There is no standalone agent piolium subcommand — piolium runs via --dri> Standalone audit CLIs: the agentic security audit also ships as standalone CLIs you can run independently of : (the harness behind agent audit) and piolium (the Pi-nati behind agent audit --dri).
See the agent mode guide for the full guide.
⚡ Cloud Console
A cloud-based solution for teams that want the power of without managing infrastructure. Console is the upgraded, fully-featured of , led by an ad autonomous agent that drives the whole engagement — reasoning about the target, choosing its own attack paths, and confirming what it finds — with hosted scanning and shared results layered on top of the open-source core, so you can focus on fixing instead of maintaining tooling.
> Interested? Get in touch for a demo.
Native Scan Layers
The native scan pipeline is composed of modular layers, each documented separately:
| Layer | Description | Docs |
|-------|-------------|------|
| Content Discovery (Deparos) | Adapti/file enumeration with fingerprint-based soft-404 detection | docs..com/nati/phases/discovery |
| Browser Spider (Spitolas) | Chromium-dri crawler with CDP traffic capture | docs..com/nati/phases/spidering |
| Audit | Acti scanning with insertion point extraction and DiffScan framework | docs..com/nati/phases/audit |
| Scanner Modules | 208 active and 117 passi co OWASP Top 10 and beyond | docs..com/nati/modules-reference |
Documentation
Full documentation lives at docs..com. Release notes and history are in the CHANGELOG. Quick links:
| Topic | Link |
|-------|------|
| Setup Agents | docs..com/getting-started/setup-agent |
| Start a Native Scan | docs..com/getting-started/nati |
| Start an Agentic Scan | docs..com/getting-started/agentic-scan |
| Start an Agentic Audit | docs..com/getting-started/agentic-security-audit |
| Quickstart | docs..com/getting-started/quickstart |
| Cheat Sheet | docs..com/getting-started/cheat-sheet |
| Server & Ingestion | docs..com/getting-started/ser |
| Writing Extensions | docs..com/customization/writing-extensions |
Ja Engine
Run Ja/TypeScript code directly or write custom scan modules and hooks without recompiling:
The JS engine exposes session-aware HTTP APIs for authenticated testing:
See writing extensions for the extension authoring guide and pkg/jsext/.d.ts for the full TypeScript API definitions.
CLI Reference
<details>
<summary>Expand the full commands & flags reference</summary>
Commands
Flags
</details>
Repository Layout
The platform/ directory contains external tooling, UI Dashboard and is not part of the core scanner. No changes should be made to it.
Benchmarks
is continuously benchmarked against intentionally applications and also heavily tested against real-world targets through bug bounty and responsible disclosure programs.
Run benchmarks with make test-canary (Docker apps) or make test-integration (XSS).
De
See HACKING.md for the full build guide, codebase map, and module de guide.
Security
is an offensi tool, and two parts of it are intentionally permissive: agent mode runs with no sandbox (the LLM has full shell, file, and network access on the host) and extensions can run arbitrary commands. Run agent mode in a disposable container/ to the engagement, and treat untrusted extensions like untrusted code. See SECURITY.md before you start, and report in itself pri to contact@.com.
License
is released under the MIT License.
Crafted with ♥ by , with as a core initial contributor.
项目信息
开发语言:Go
Star 数:1104
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | vigolium - Vigolium - High-fidelity vulnerability scanner fus |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:34:24 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 97 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |