 安全软件
点击放大
medusa - AI-first security scanner. NEW in v2026.7: Claude
项目说明
🐍 MEDUSA - AI Security Scanner
![PyPI]()
![Downloads]()
![Python]()
![License: AGPL-3.0]()
![Tests]()
![Windows]()
![macOS]()
![Linux]()
AI-first security scanner with 40,000+ detection patterns for AI/ML, agents, and LLM applications.
🤖 Works out of the box - no tool installation required.
🚨 200 CVEs: Log4Shell, Spring4Shell, XZ Utils, LangChain RCE, MCP-Remote RCE, React2Shell
🔥 medusa scan --git <URL> — Scan any repo for AI supply chain attacks (repo poisoning, prompt injection, MCP tool poisoning)
🔐 medusa secrets scan — Find leaked API keys in your Claude / Cursor / Copilot / shell history. 21 issuer types. Interacti redaction.
🚀 v2026.7.0: Claude Code compromise detection, an always-on AI attack-signature scanner, native Rust & PHP security rules, and rule-le — on top of 40,000+ detection patterns.
---
🎯 What is MEDUSA?
MEDUSA is an AI-first security scanner with 40,000+ detection patterns that works out of the box. Simply install and scan - no external tool installation required. MEDUSA's built-in rules detect in AI/ML applications, LLM agents, MCP servers, RAG pipelines, and traditional code.
✨ Key Features
medusa scan --git <URL> - Scan any GitHub repo for AI supply chain attacks in secondsmedusa secrets scan + purge - Find API keys / tokens / private keys leaked into Claude Code / Cursor / Copilot / Zed / Gemini chat histories *and* your bash / zsh / psql / mysql / python REPL history. 21 issuer types (Anthropic, OpenAI, PyPI, GitHub PATs, AWS, GCP, Stripe, Slack…). Interactive [y/n/s/a/q] purge with mandatory byte-identical backup and JSONL-safe redaction. Local-only, no telemetry.pip install - no tool installation needed.medusa.yml for project-specific settings🆕 What's New in v2026.7.0
Claude Code supply-chain detection, broader language co, and rule-le.
| | Change | Details |
|---|---|---|
| 🛡️ | Claude Code compromise detection | medusa scan --git now structurally vets .claude/ — poisoned hooks (curl\|bash, base64→exec, credential exfil, reverse shells), o permissions (Bash(*), bypassPermissions), wildcard-tool subagents, and dropper skills — *before* you clone. |
| 🎯 | Always-on attack-signature scanner | Closes a false-negative gap — jailbreak / prompt-injection payloads in data files (.jsonl/.csv) and prose are now caught regardless of LLM-context confidence, plus in / bidi (Trojan Source, C) recovery. |
| 🦀 | Native Rust security rules | 22 out-of-box rules (no toolchain needed) — TLS disabled, command injection, untrusted deserialization, raw SQL, unsafe memory ops, weak crypto, SSRF. |
| 🐘 | Native PHP security rules | 16 out-of-box rules — SQLi, command/e, LFI/RFI, path tra, unserialize() object injection, unrestricted upload, reflected XSS, SSRF, weak crypto. |
| 🔬 | Rule diagnostics (--trace-rules) | Per-rule firing log + timing (rule-trace.jsonl, slow_rules.csv) and a hang-sur heartbeat — found & fixed a real catastrophic-backtracking ReDoS, plus a ReDoS/nested-set lint that blocks bad patterns at author time. |
| ⚡ | Engine + accuracy | Scan-engine perf quick-wins, context-aware screening mode for --git target , large-file byte-cap sampling, and a documentation-placeholder secret-FP fix. |
<details>
<summary>Previous releases</summary>
v2026.5.12 — Biggest pattern release: 9,600 → 40,000+ detection patterns har from 8,466 AI-security research papers, false-positi; structural rule-integrity scanner.
v2026.5.10 — Security hardening: VS Code extension command-injection fix, --fail-on cached-findings bug, tool-cache stale-path fix, user-home MCP configs made opt-in.
v2026.5.9 — Agentic-commerce co: UCPScanner + AP2Scanner + 45 hand-tuned positi rules.
v2026.5.8 — medusa secrets: scan AI chat & shell histories for leaked credentials (21 issuer types) with interactive [y/n/s/a/q] purge.
v2026.5.7 — Indirect PI rules (101/102), supply chain import scanner, macOS/Windows multiprocessing fix.
v2026.5.5 — security hardening release (arg defenses, git SSRF, HMAC cache integrity, markdown XSS fix).
</details>
External Linters (optional): MEDUSA auto-detects bandit, eslint, shellcheck, etc. if installed. See Optional Tools Guide.
---
🔐 Scan your AI chat history for leaked secrets
> Your PyPI token might be in your Claude chat history right now.
De paste API keys, tokens, and credentials into AI assistants every day —
"deploy this with pypi-AgEI...", "use my ghp_... to push", "the AWS key is AKIA...".
The assistants keep those con in plaintext on disk. Anyone with read access
to $HOME — or any future malware with shell access — can grep -r 'sk-\|ghp_\|AKIA' ~/
and harvest production credentials in seconds.
medusa secrets scan finds them. medusa secrets purge cleans them up.
30-second tour
The original file is backed up byte-for-byte before any change. JSONL stays
parseable after redaction. The redaction marker ([REDACTED-MEDUSA-...-<run-id>])
is unique per run so you can trace it back to the scan that produced it.
Commands
What's detected (21 issuers)
AI pro: Anthropic, OpenAI, HuggingFace, Replicate, Cohere
Package registries: PyPI, npm
Source forges: GitHub PAT (classic + fine-grained + OAuth + App), GitLab PAT
Cloud: AWS access keys, GCP ser JSON
Payments / comms: Stripe li keys, Slack bot/user tokens, SendGrid, Twilio, Discord webhooks
Cryptography: PEM-encoded private keys (RSA, DSA, EC, OpenSSH, PGP)
Safety properties
~/.medusa/secrets-scan/ mode 0o600. No network, no telemetry, ne to project trees.cp restores it.os.replace swap. Either the rewrite lands or the original stays.📖 Full secrets-scanner guide →
---
🚀 Quick Start
Installation
En (Recommended):
Platform Notes:
py -m medusa if medusa command is not foundScan Any GitHub Repo
MEDUSA automatically detects 28+ AI editor config files that are known attack :
| Risk Level | Files Detected |
|------------|----------------|
| Critical (RCE) | .cursorrules, .cursor/mcp.json, .clinerules/, .windsurfrules, .codex/config.toml, .kiro/settings/mcp.json, ./settings.json, mcp.json |
| High | CLAUDE.md, GEMINI.md, AGENTS.md, AGENT.md, SKILL.md, .github/copilot-instructions.md, CON.md, .amazonq/rules/, .roo/rules/, .augment/rules/ |
Known attacks detected: Clinejection, CurXecute (C), IDEsaster (C), ToxicSkills, CamoLeak, RoguePilot, AIShellJack, Cacheract
Optional: AI Model Scanning
Optional: External Linters
MEDUSA auto-detects external linters if installed (bandit, eslint, shellcheck, etc.) and uses them automatically to enhance scan co.
See Installation Guide → for platform-specific instructions.
> Note: External linters are optional. MEDUSA's 40,000+ built-in rules work without them. For installation support, please refer to each tool 's documentation.
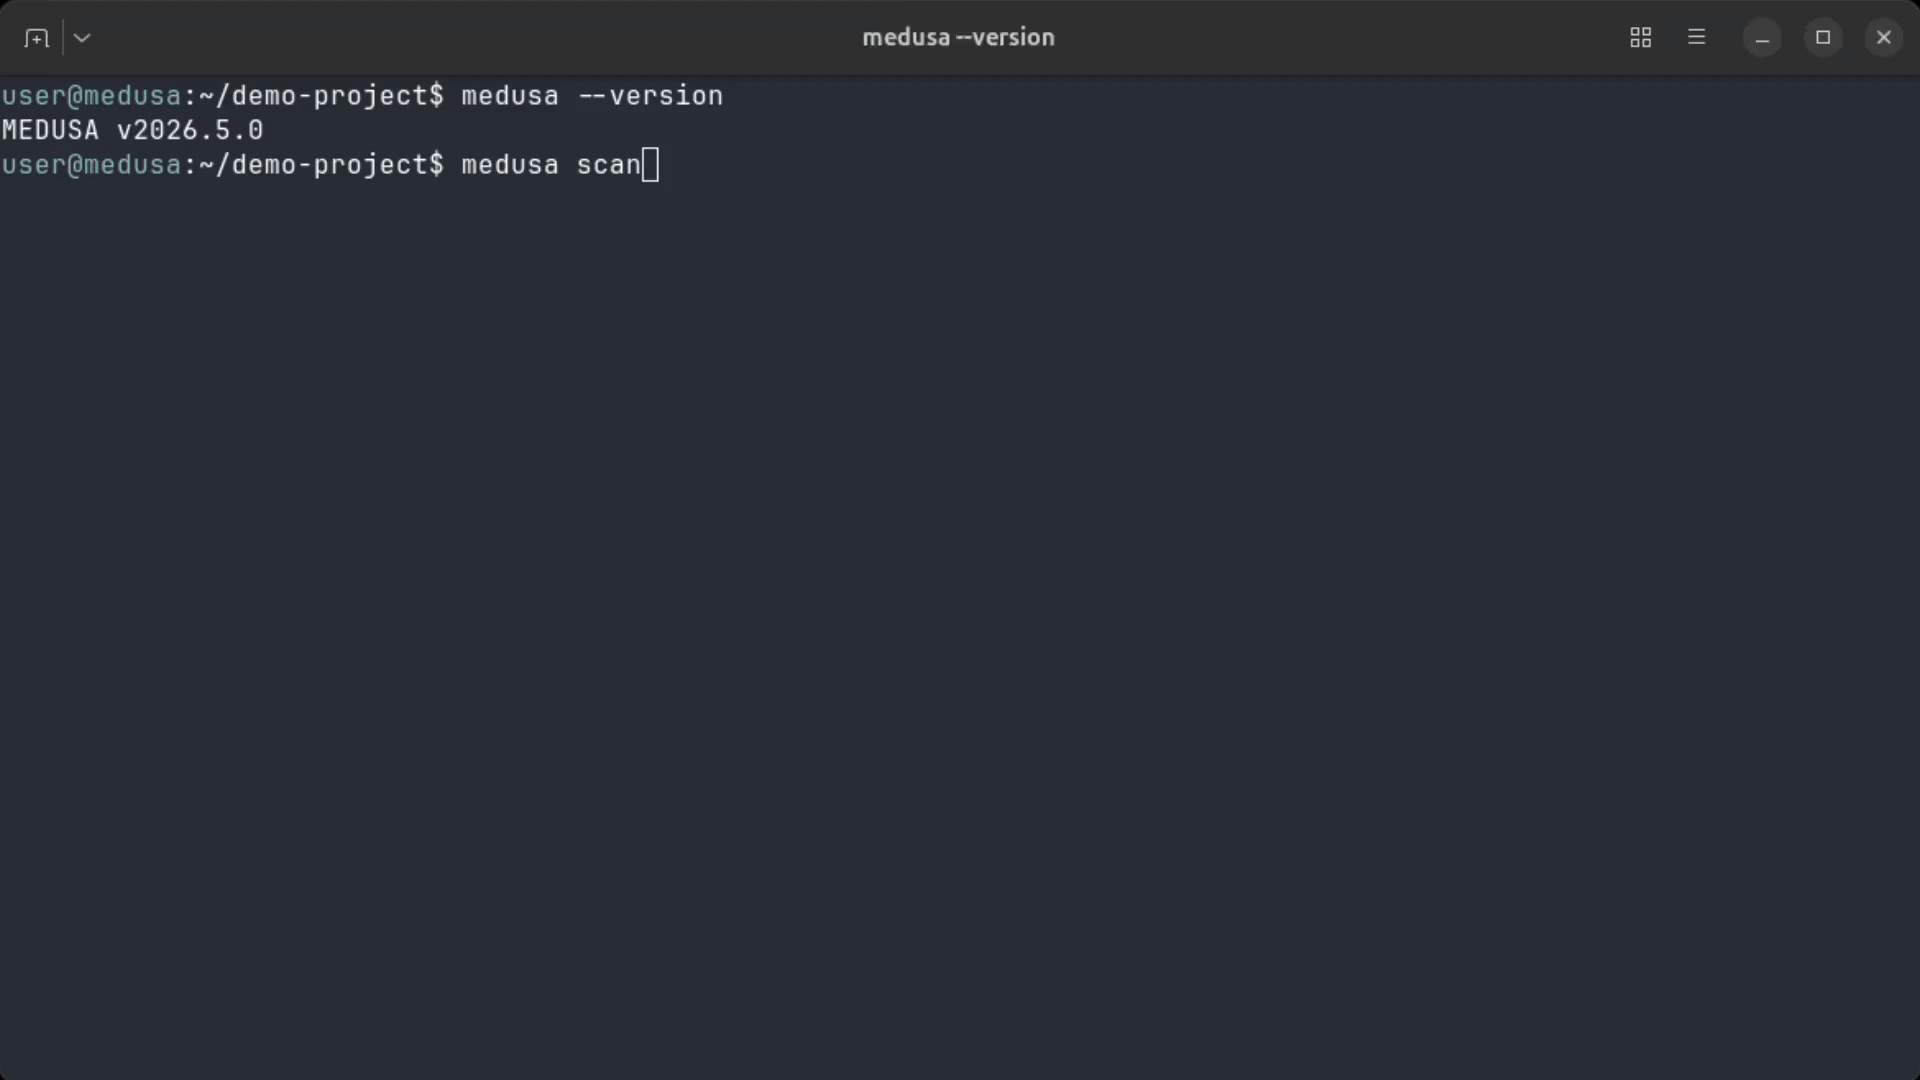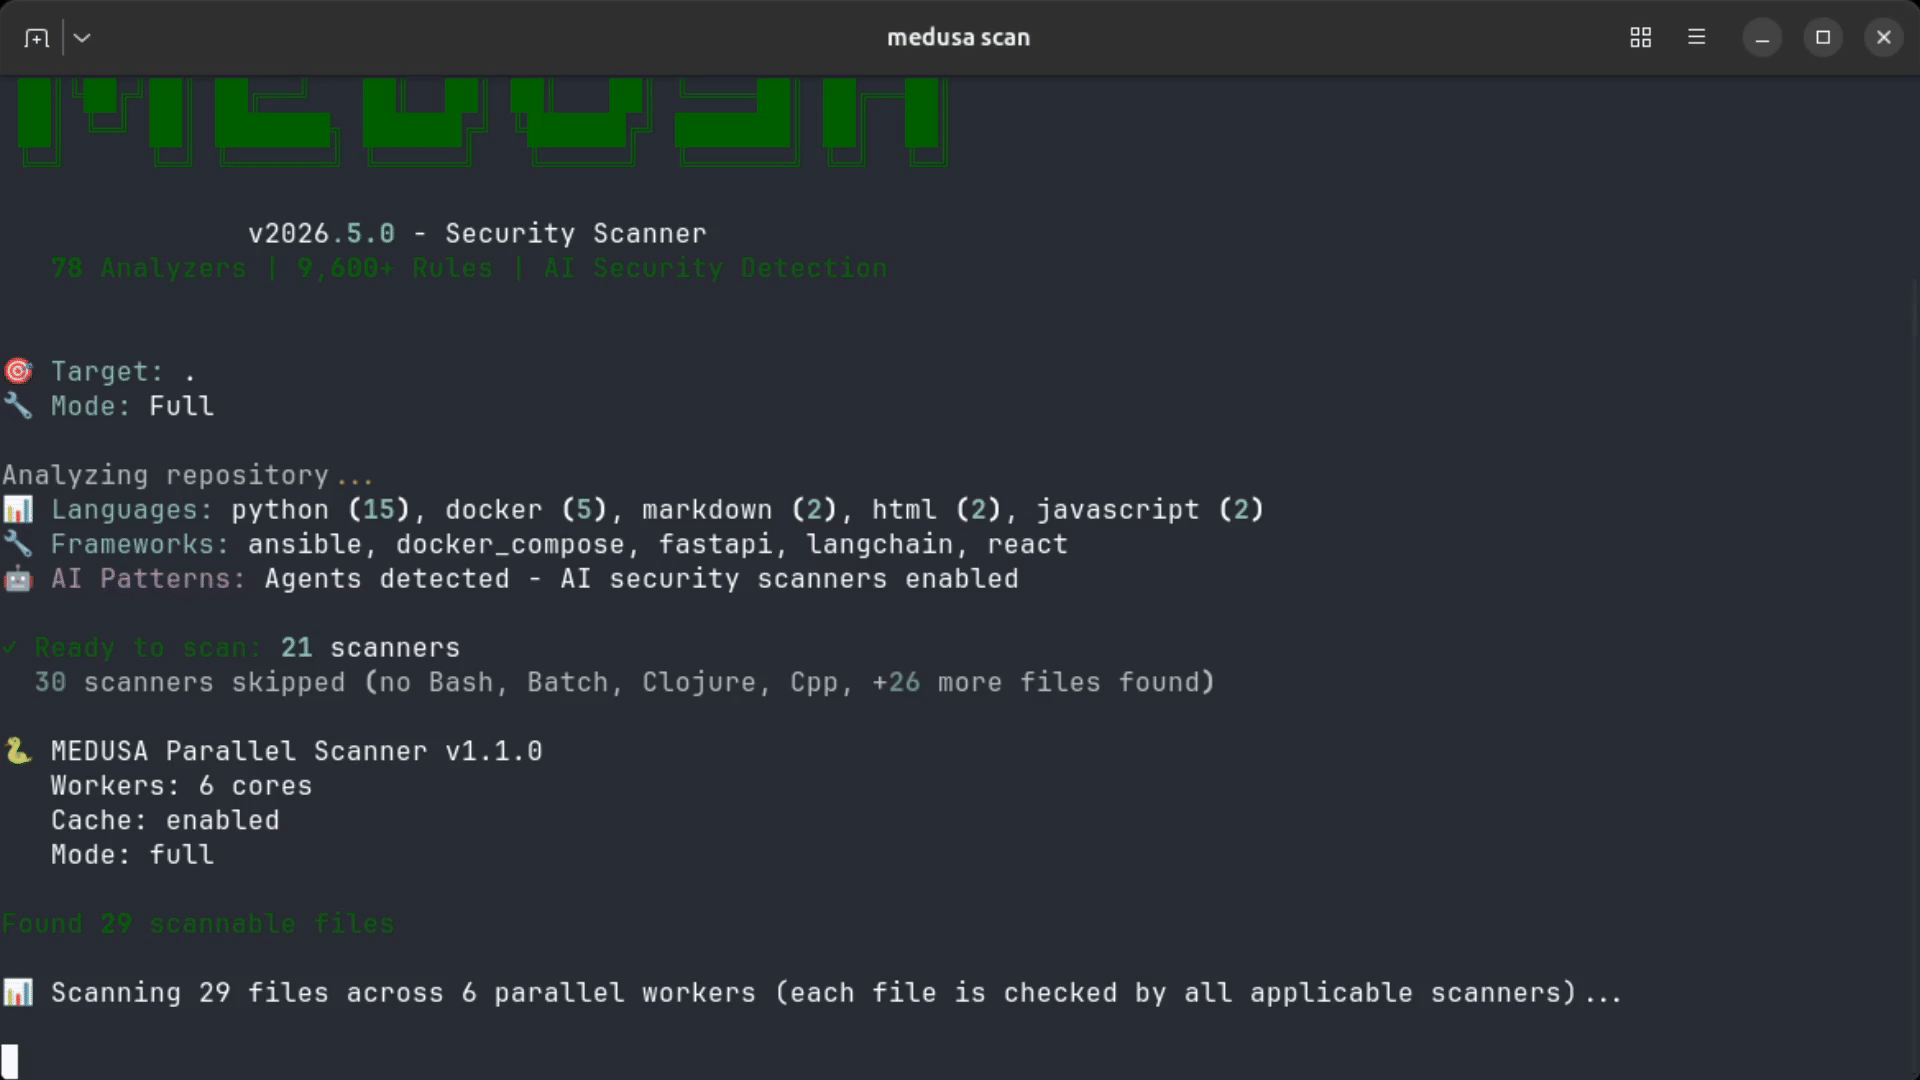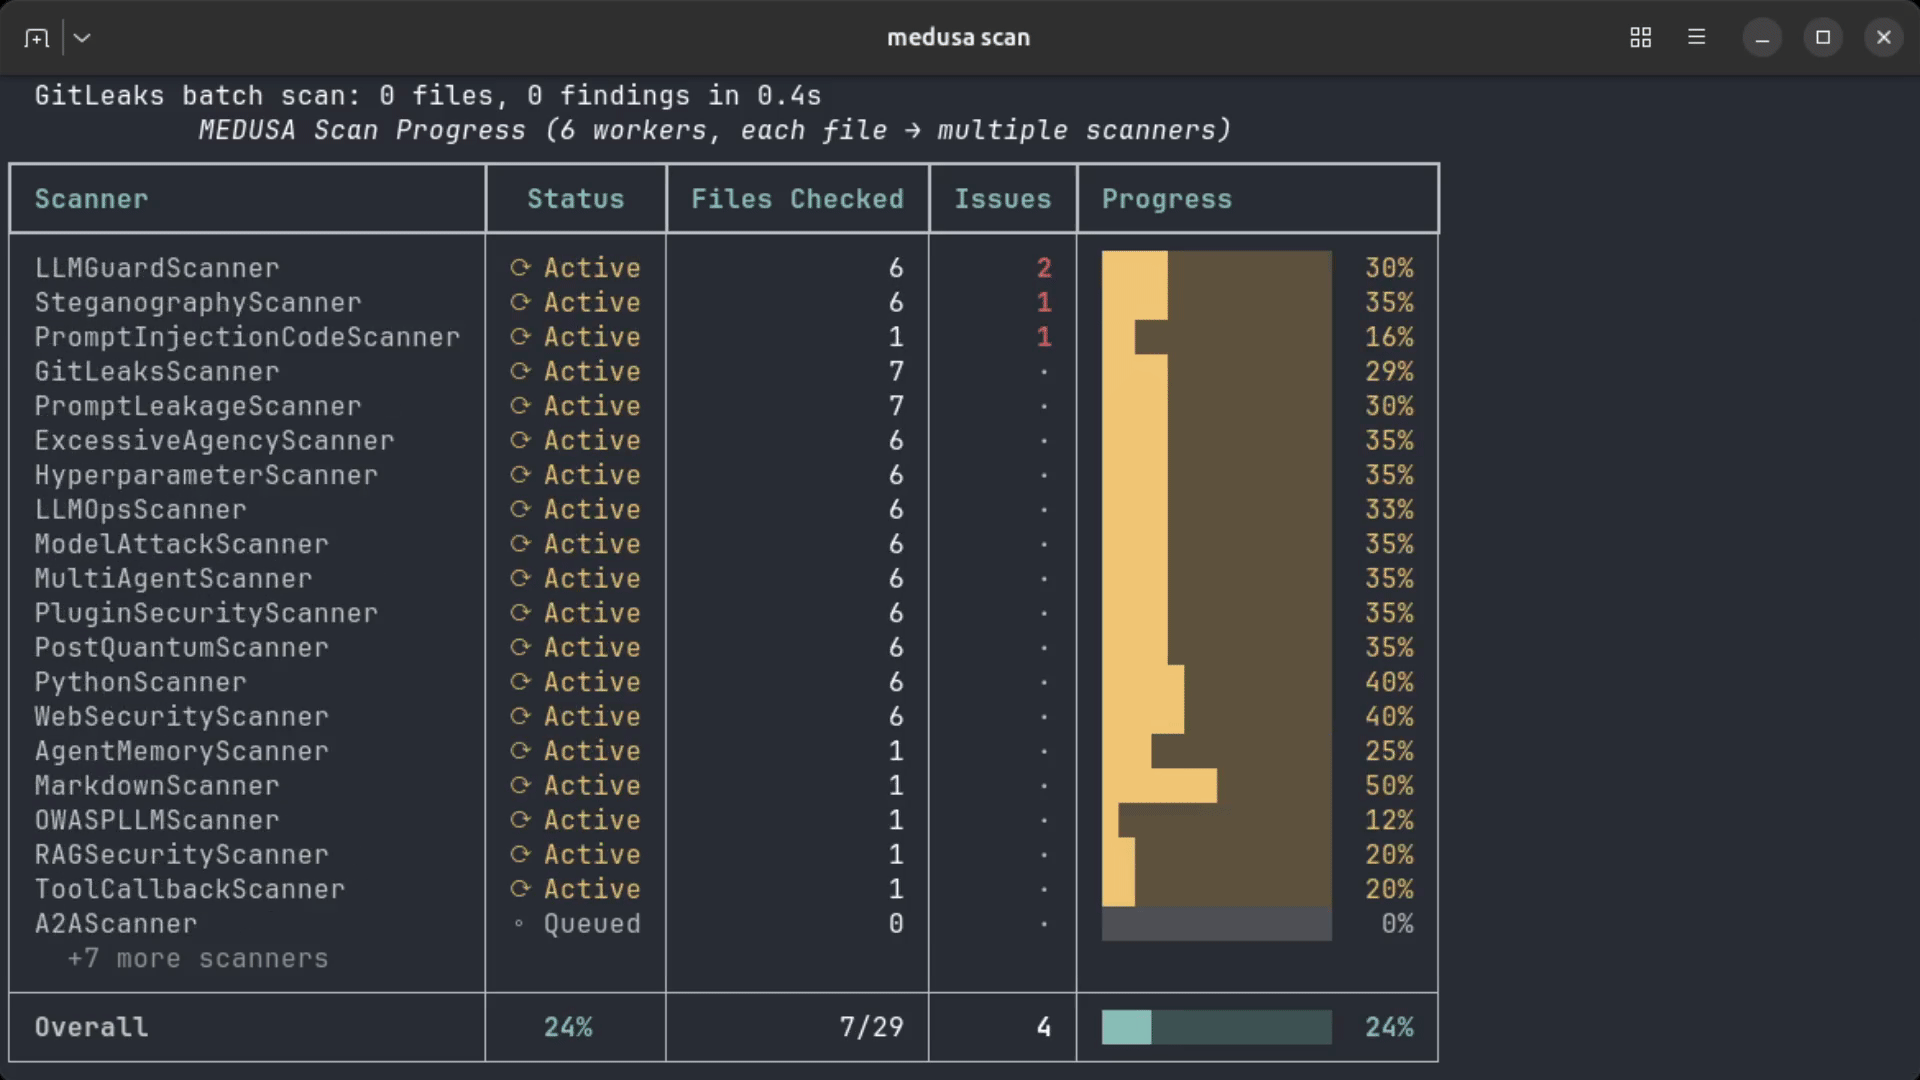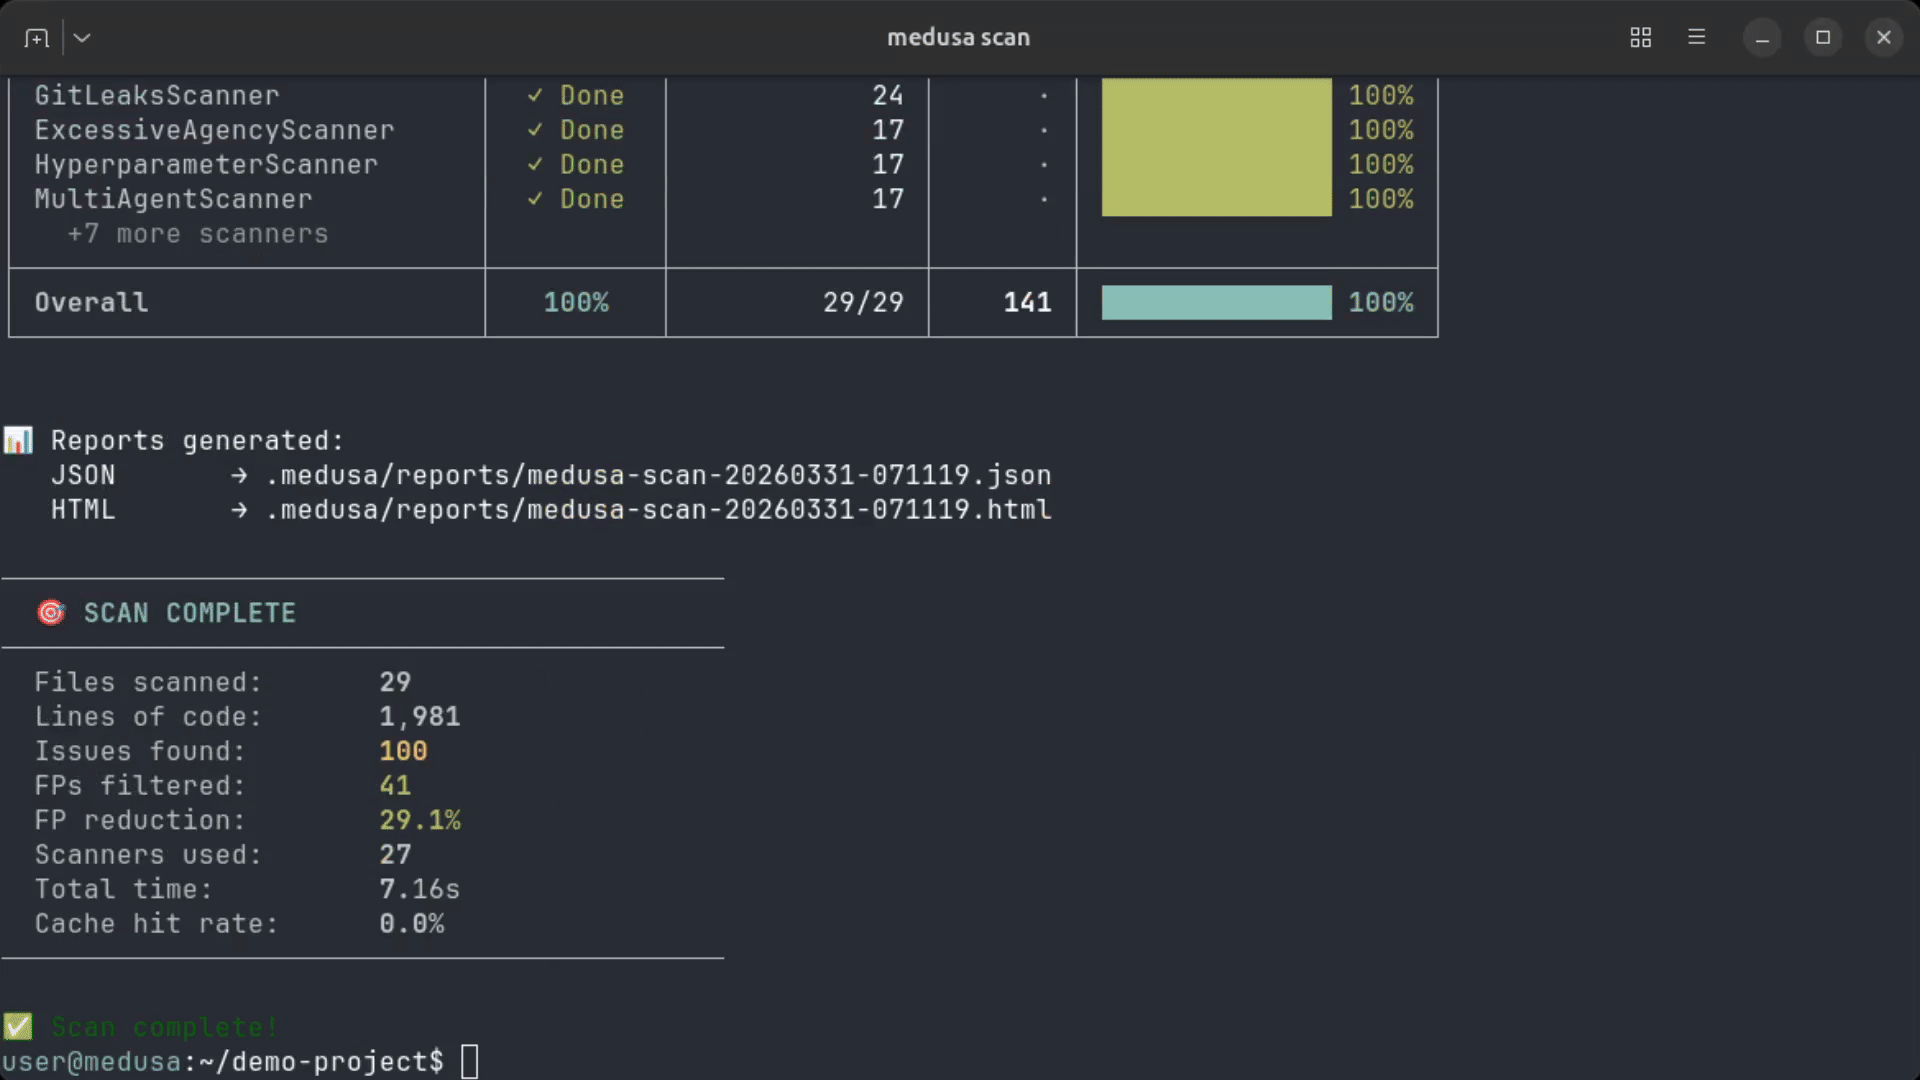
Demo
<di="center">
!MEDUSA in action
</div>
📊 Report Formats
MEDUSA generates beautiful reports in multiple formats:
JSON - Machine-readable for CI/CD integration
HTML - Stunning glassmorphism UI with interacti
Markdown - Documentation-friendly for GitHub/wikis
All Formats - Generate e at once
---
📚 Language Support
MEDUSA supports 79 scanner types co AI/ML security, all major programming languages, and file formats:
Backend Languages (9)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Python | Bandit |
.py || Ja/TypeScript | ESLint |
.js, .jsx, .ts, .tsx || Go | golangci-lint |
.go || Ruby | RuboCop |
.rb, .rake, .gemspec || PHP | Nati (+ PHPStan optional) |
.php || Rust | Nati (+ Clippy optional) |
.rs || Java | Checkstyle |
.java || C/C++ | cppcheck |
.c, .cpp, .cc, .cxx, .h, .hpp || C# | Roslynator |
.cs |J (3)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Kotlin | ktlint |
.kt, .kts || Scala | Scalastyle |
.scala || Groovy | CodeNarc |
.groovy, .gradle |Functional Languages (5)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Haskell | HLint |
.hs, .lhs || Elixir | Credo |
.ex, .exs || Erlang | Elvis |
.erl, .hrl || F# | FSharpLint |
.fs, .fsx || Clojure | clj-kondo |
.clj, .cljs, .cljc |Mobile De (2)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Swift | SwiftLint |
.swift || Objective-C | OCLint |
.m, .mm |Frontend & Styling (3)
| Language | Scanner | Extensions |
|----------|---------|------------|
| CSS/SCSS/Sass/Less | Stylelint |
.css, .scss, .sass, .less || HTML | HTMLHint |
.html, .htm || Vue.js | ESLint |
.vue |Infrastructure as Code (4)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Terraform | tflint |
.tf, .tfvars || Ansible | ansible-lint |
.yml (playbooks) || Kubernetes | kubeval |
.yml, .yaml (manifests) || CloudFormation | cfn-lint |
.yml, .yaml, .json (templates) |Configuration Files (4)
| Language | Scanner | Extensions |
|----------|---------|------------|
| JSON | built-in |
.json || TOML | taplo |
.toml || XML | xmllint |
.xml || Protobuf | buf lint |
.proto |Shell & Scripts (4)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Bash/Shell | ShellCheck |
.sh, .bash || PowerShell | PSScriptAnalyzer |
.ps1, .psm1 || Lua | luacheck |
.lua || Perl | perlcritic |
.pl, .pm |Documentation (2)
| Language | Scanner | Extensions |
|----------|---------|------------|
| Markdown | markdownlint |
.md || reStructuredText | rst-lint |
.rst |Other Languages (5)
| Language | Scanner | Extensions |
|----------|---------|------------|
| SQL | SQLFluff |
.sql || R | lintr |
.r, .R || Dart | dart analyze |
.dart || Solidity | solhint |
.sol || Docker | hadolint |
Dockerfile* |Total: 79 scanner types — 41 language/tool scanners + 38 AI/ML security scanners — co 100+ file extensions
---
🚨 React2Shell C (NEW in v2025.8)
MEDUSA now detects C "React2Shell" - a CVSS 10.0 RCE affecting React Ser and Next.js.
Scans: package.json, package-lock.json, yarn.lock, pnpm-lock.yaml
Fix: Upgrade to React 19.0.1+ and Next.js 15.0.5+
---
🤖 AI Agent Security
MEDUSA provides industry-leading AI security scanning with 40,000+ detection patterns for the agentic AI era. Updated for OWASP Top 10 for LLM Applications 2025 and includes detection for 200+ CVEs across AI coding editors and MCP servers.
Full AI Security Documentation
AI Security Co
| Category | Patterns | Detects |
|----------|----------|---------|
| Prompt Injection | 800+ | Direct/indirect injection, jailbreaks, role manipulation |
| MCP Ser | 400+ | Tool poisoning, schema poisoning, ATPA, sampling injection, rug-pull |
| Repo Poisoning | 150+ | Weaponized AI editor configs, Clinejection, CurXecute, IDEsaster, CamoLeak |
| RAG Security | 300+ | injection, document poisoning, tenant isolation |
| Agent Security | 500+ | Excessi, memory poisoning, HITL bypass |
| Model Security | 400+ | Insecure loading, checkpoint exposure, ad attacks |
| Supply Chain | 350+ | Dependency confusion, typosquatting, lock file backdoors |
| Traditional SAST | 1,400+ | SQL injection, XSS, command injection, secrets |
AI Attack Co
<table>
<tr><td>
Context & Input Attacks
Memory & State Attacks
Tool & Action Attacks
</td><td>
Workflow & Routing Attacks
RAG & Knowledge Attacks
Ad Attacks
</td></tr>
</table>
Supported AI Files (28+)
Quick AI Security Scan
---
🎮 Usage
Basic Commands
Install Commands
> Note: MEDUSA v2026.2+ no longer installs external linters. Install them via your package manager (apt, brew, npm, pip) if needed. MEDUSA auto-detects and uses any installed linters.
Init Commands
Additional Commands
Scan Options Reference
| Option | Description |
|--------|-------------|
| TARGET | Directory or file to scan (default: .) |
| -g, --git URL | Clone and scan a remote git repo (GitHub URL or user/repo shorthand) |
| -w, --workers N | Number of parallel workers (default: auto-detect) |
| --quick | Quick scan (changed files only, requires git) |
| --force | Force full scan (ignore cache) |
| --no-cache | Disable result caching |
| --fail-on LEVEL | Exit with error on se: critical, high, medium, low |
| -o, --output PATH | Custom output directory for reports |
| --format FORMAT | Output format: json, html, sarif, junit, text (can specify multiple) |
| --no-report | Skip generating HTML report |
Install Options Reference
| Option | Description |
|--------|-------------|
| --check | Check tool status |
| --ai-tools | Install AI security tools (modelscan) |
| --debug | Show detailed debug output |
> v2026.2+ Change: MEDUSA no longer manages external linter installation. The --all flag is deprecated. Install external linters via your system package manager if needed.
---
⚙️ Configuration
.medusa.yml
MEDUSA uses a YAML configuration file for project-specific settings:
Generate Default Config
This creates .medusa.yml with sensible defaults and auto-detects your IDE.
---
🤖 IDE Integration
MEDUSA supports 5 major AI coding assistants with nati. Initialize with medusa init --ide all or select specific platforms.
Supported Platforms
| IDE | Context File | Commands | Status |
|-----|-------------|----------|--------|
| Claude Code | CLAUDE.md | /medusa-scan, /medusa-install | ✅ Full Support |
| Gemini CLI | GEMINI.md | /scan, /install | ✅ Full Support |
| OpenAI Codex | AGENTS.md | Nati commands | ✅ Full Support |
| GitHub Copilot | .github/copilot-instructions.md | Code suggestions | ✅ Full Support |
| Cursor | Reuses CLAUDE.md | MCP + Claude commands | ✅ Full Support |
Quick Setup
Claude Code
What it creates:
CLAUDE.md - Project context file.claude/agents/medusa/agent.json - Agent configuration.claude/commands/medusa-scan.md - Scan slash command.claude/commands/medusa-install.md - Install slash commandUsage:
Gemini CLI
What it creates:
GEMINI.md - Project context file.gemini/commands/scan.toml - Scan command config.gemini/commands/install.toml - Install command configUsage:
OpenAI Codex
What it creates:
AGENTS.md - Project context (root level)Usage:
GitHub Copilot
What it creates:
.github/copilot-instructions.md - Security standards and best practicesHow it helps:
Cursor
What it creates:
.cursor/mcp-config.json - MCP ser.claude/ structure (Cursor is VS Code fork)Usage:
---
🔧 Ad Features
System Load Monitoring
MEDUSA automatically monitors system load and adjusts worker count:
Smart Caching
Hash-based caching skips unchanged files:
Parallel Processing
Multi-core scanning for massi:
---
📊 Example Workflow
New Project Setup
CI/CD Integration
> Note: No tool installation step needed - MEDUSA's 40,000+ built-in rules work immediately.
---
🏗️ Architecture
Scanner Pattern
All scanners follow a consistent pattern:
Auto-Registration
Scanners automatically register themselves:
Se Mapping
Unified se levels across all tools:
---
🧪 Testing & Quality
Dogfooding Results
MEDUSA scans itself — and real-world projects:
Performance Benchmarks
| Project Size | Files | Time | Speed |
|--------------|-------|------|-------|
| Small (MEDUSA self-scan) | 473 | ~8s | 59 files/s |
| Medium | 1,000 | ~45s | 22 files/s |
| Large (OpenClaw) | 4,124 | ~3.3h | 0.34 files/s* |
*Large project time dominated by external tool subprocesses (Semgrep, Tri). Built-in pattern scanning is near-instant.
---
🗺️ Roadmap
✅ Completed (v2026.5.0)
medusa scan --git <URL> - Scan any GitHub repo for AI supply chain attacks🔮 Upcoming
---
🤝 Contributing
We welcome contributions! Here's how to get started:
Adding New Scanners
See docs/de/adding-scanners.md for a guide on adding new language support.
---
📜 License
AGPL-3.0-or-later - See LICENSE file
MEDUSA is free and open source software. You can use, modify, and distribute it freely, but any modifications or deri works (including SaaS deployments) must also be released under AGPL-3.0.
For commercial licensing options, contact:
---
Coming Soon
MEDUSA Professional adds runtime protection for production LLM applications - blocking prompt injection, jailbreaking, and data exfiltration attempts in real-time before they reach your models.
| Feature | Open Source | Professional | Enterprise |
|---------|-------------|--------------|------------|
| Static scanning (40,000+ patterns) | Yes | Yes | Yes |
| Runtime proxy filters (1,100+) | - | Yes | Yes |
| REST API & webhooks | - | Yes | Yes |
| Custom rules & SSO | - | - | Yes |
| Price | Free | $99/dev/mo | $499/50 devs/mo |
The runtime proxy is currently in private beta. If you're protecting production LLM applications and want early access, reach out to .
---
🙏 Credits
De:
Built With:
Inspired By:
---
📖 Guides
---
📞 Support
---
📈 Statistics
: 2026.5.5
Release Date: 2026-04-03
Detection Patterns: 40,000+ AI security rules
Analyzers: 79 specialized scanners
FP Filter Patterns: 514 intelligent filters (96.8% reduction rate)
C: 200 critical (37+ AI editor CVEs)
Repo Poisoning: 28+ AI editor config file types detected
Language Co: 46+ file types
Platform Support: Linux, macOS, Windows
AI Integration: Claude Code, Gemini CLI, GitHub Copilot, Cursor, OpenAI Codex
Standards: OWASP Top 10 for LLM 2025, MITRE ATLAS
Downloads: 11,500+ on PyPI
---
🌟 Why MEDUSA?
pip install && scan)SAST
---
🐍🐍🐍 MEDUSA - Multi-Language Security Scanner 🐍🐍🐍
One Command. Complete Security.
---
Last Updated: 2026-04-03
Status: Production Ready
Current : v2026.5.5 - Security Hardening
项目信息
开发语言:Python
Star 数:998
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an always-on AI attack-signature scanner and native Rust & PHP rules. Also: medusa scan --git to vet any repo, medusa secrets scan for leaked API keys. 40,000+ patterns, zero setup.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | medusa - AI-first security scanner. NEW in v2026.7: Claude |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:34:30 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 421 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |