 安全软件
点击放大
Dark-Moon - Open-source autonomous AI penetration testing. 50
项目说明
<di="center">
<a href="
<img src="docs/pics/hero.png" alt="DarkMoon — autonomous AI penetration testing on a local model" width="100%" />
</a>
DarkMoon
Open-source autonomous AI penetration testing — finds, exploits and qualifies every on your own infrastructure
<p>
<a href=" src=" alt="GitHub stars"></a>
<a href=" src=" alt="Latest release"></a>
<a href=" src=" alt="License GPLv3"></a>
<a href="#quick-start"><img src=" alt="Made with local LLM"></a>
<a href=" src=" alt="Autonomous AI pentesting"></a>
</p>
⭐ Star DarkMoon · 🚀 Quick Start · 🧩 Integrations · 📊 Benchmark · 🔒 Darkmoon Pro · ▶️ Install & Run (OSS) · ▶️ Demo (Pro)
</div>
DarkMoon is autonomous AI penetration testing for your own infrastructure. Point it at an authorized target and it runs the whole assessment on its own, then documents every finding with the exact command and raw output.
---
<di="center">
See the open source engine (CLI)
The open source Darkmoon is a command line tool. This is what you get when you clone the repo. You launch an assessment from the command line and watch every agent, command and finding stream past in real time.
</div>
<table>
<tr>
<td width="50%" ="top">
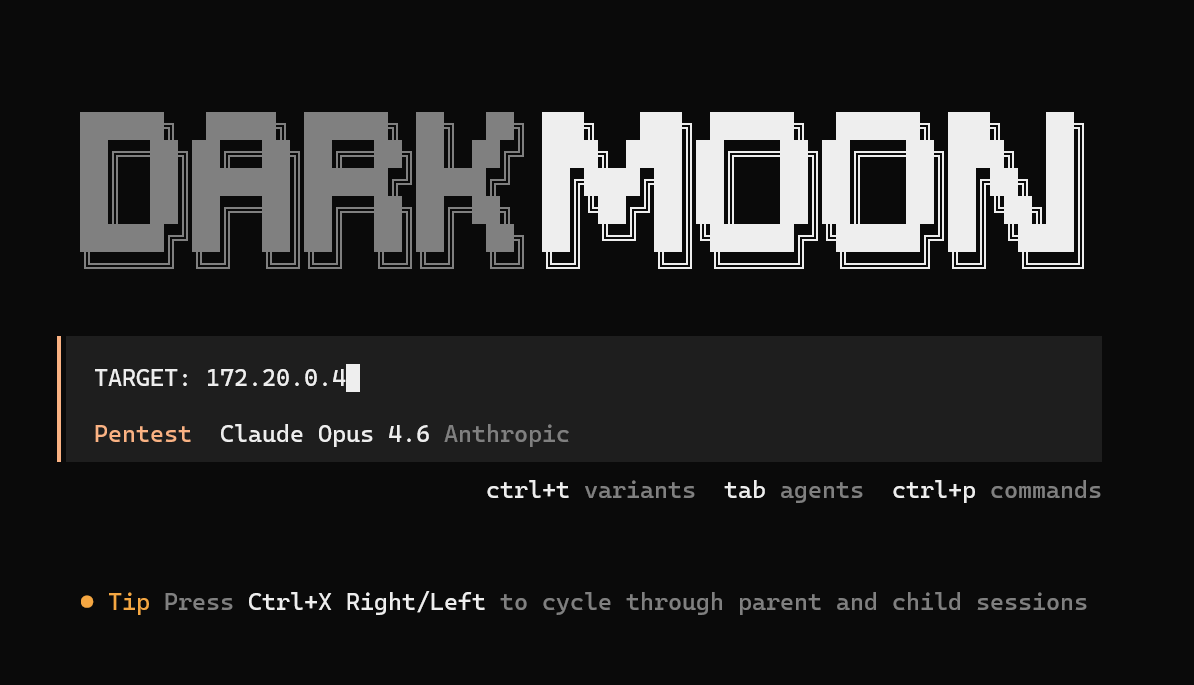
<img src="docs/pics/start-assesment.png" alt="Launching a DarkMoon assessment from the command line with a single TARGET line" />
<p align="center"><b>Kick off a run from the CLI.</b> One <code>TARGET</code> line and DarkMoon takes over the whole assessment.</p>
</td>
<td width="50%" ="top">
<img src="docs/pics/sub-agent-1.png" alt="A DarkMoon sub-agent state machine in the terminal detecting C and moving straight to exploitation" />
<p align="center"><b>Autonomous agents reason and exploit, live in your terminal.</b> Here a sub-agent flags C and pivots straight to exploitation.</p>
</td>
</tr>
<tr>
<td width="50%" ="top">
<img src="docs/pics/enumeration.png" alt="DarkMoon recon and en model summary printed in the terminal" />
<p align="center"><b>Recon and en model.</b> DarkMoon fingerprints the stack and confirms the attack surface before it strikes.</p>
</td>
<td width="50%" ="top">
<img src="docs/pics/log.png" alt="Live MCP output stream in the terminal with timestamped commands and raw responses" />
<p align="center"><b>Live MCP stream.</b> Every command the agent runs and its raw output, timestamped, with <code>./darkmoon.sh --log <session></code>.</p>
</td>
</tr>
</table>
<di="center">
<img src="docs/pics/matrix.png" alt="Signal detection matrix in the terminal mapping detected technologies to the agents DarkMoon dispatches" width="80%" />
<p><b>Signal to agent dispatch.</b> DarkMoon decides which specialist agents to deploy from exactly what it detects on the target.</p>
As featured in Help Net Security · Cyber Security News · DevOps.com · SecurityBrief · LinuxLinks · IT Brief · ChannelLife
</div>
---
Quick Start
install.sh configures your LLM provider interactively (no need to edit docker-compose.yml) and builds the full stack:
Supports cloud pro (Anthropic, OpenAI, OpenRouter…) and local models (Ollama, llama.cpp). Then run your first assessment and watch it live:
Prerequisites: Docker & Docker Compose, and an LLM API key (or a local model). GPU setup, en and the full flags reference live in the Full Documentation.
---
Feature grid
| | |
|---|---|
| 🧠 50 specialist agents | One agentic system reasons, plans and dispatches specialist agents across every surface it discovers. |
| 🌐 Every surface | Web, APIs, Acti, Kubernetes, cloud (AWS, Azure, GCP), CI/CD, databases, IoT firmware and AI/LLM endpoints, chained end to end. |
| 🔒 Privacy Gateway | Re local tokenization turns real IPs, hosts, URLs and credentials into deterministic placeholders, rehydrated only locally at the moment a tool runs. |
| 🏠 Local model | Run the whole assessment on a local LLM (Ollama, llama.cpp) so your infrastructure stay on your own perimeter. |
| 🧾 E, not scores | Every finding ships with the exact command and raw output; the Pro retest re-runs the exploit to confirm a fix. |
| 🛡️ Security by design | The AI never runs a command directly, every action flows through a controlled, logged MCP interface. |
| 🤖 Pentests your AI too | A dedicated LLM agent probes AI/LLM inference endpoints for the OWASP LLM Top 10 with garak-backed probes. |
| ♾️ CI/CD native | Trigger a pentest in the pipeline and get findings back as artifacts. |
| 🔌 MCP | Orchestrate 140+ offensi over MCP. |
| 🔧 Fix it (Pro) | The paid Pro tier turns findings into human-re pull requests, retested against the original exploit. |
Built for security teams, De engineers, red teamers and ethical hacking professionals.
---
🧩 DarkMoon e
<p align="center">
<img src="docs/pics/integrations.svg" alt="DarkMoon integrations: GitHub, GitLab, Jenkins, VS Code, JetBrains, n8n, Grafana, Splunk — OSS + Pro" width="100%" />
</p>
Run DarkMoon where you already build — in CI/CD, your IDE, automation and SecOps. Integrations marked OSS + Pro work with the open-source edition (local CLI + JSON); the Pro-only ones consume the DarkMoon Pro REST API (li, remediation→PR).
| Platform | What it does | Get it | Edition | Tutorial |
|---|---|---|---|---|
| GitHub Actions | Fail the pipeline on findings by se | GitHub Marketplace | OSS + Pro | ▶ Watch |
| GitLab CI/CD | Findings as Code Quality + SAST reports | CI/CD Catalog | OSS + Pro | ▶ Watch |
| Jenkins | Findings as Warnings-NG issues in the build | Plugin .hpi (Releases) | OSS + Pro | ▶ Watch |
| VS Code | Browse and launch assessments from the editor | VS Code Marketplace | OSS + Pro | ▶ Watch |
| JetBrains | Findings in an IDE tool window | JetBrains Marketplace | OSS + Pro | ▶ Watch |
| n8n | Automate campaigns, retests and alerts | npm n8n-nodes-darkmoon | Pro | ▶ Watch |
| Grafana | Security-posture dashboards | Self-host (Releases) | Pro | ▶ Watch |
| Splunk | SOC ingestion (HEC) + "Send to Darkmoon" alert action | App (Releases) — Splunkbase pending | OSS + Pro | ▶ Watch |
| SDK / CLI | Build your own integration on the shared contract | npm /client | OSS + Pro | ▶ Watch |
Every integration emits safe metadata only (se, status, MITRE, ids) — ne, secrets or tokens. Full guides on docs.dark-moon.org; source under ASCIT31.
---
🔒 Darkmoon Pro — paid edition: web dashboard and automated remediation
> 🔒 These are Darkmoon Pro features (paid). The open source edition is the CLI shown above; the web dashboard and the automated remediation to pull requests are not in the open source build.
The screenshots below are the paid Darkmoon Pro web dashboard. They are not part of the open source repository you clone. The open source edition is the command line tool shown in the section above.
<table>
<tr>
<td width="50%" ="top">
<img src="docs/pics/dashboard.png" alt="Darkmoon Pro web dashboard showing projects, targets, campaigns and by se" />
<p align="center"><b>Pro: live web dashboard.</b> Projects, targets and campaigns at a glance, with every finding bucketed by se.</p>
</td>
<td width="50%" ="top">
<img src="docs/pics/.png" alt="Darkmoon Pro finding detail with CVSS, MITRE ATT&CK and ISO 27001 mapping and EXPLOITED status" />
<p align="center"><b>Pro: findings with CVSS and ATT&CK mapping.</b> Each finding carries CVSS, MITRE ATT&CK and ISO 27001 mapping with an <code>EXPLOITED</code> status backed by a real exploit.</p>
</td>
</tr>
<tr>
<td width="50%" ="top">
<img src="docs/pics/markdown-report-1.png" alt="Darkmoon Pro structured web report with management summary, exportable to Markdown and PDF" />
<p align="center"><b>Pro: exportable web reports.</b> A management summary in plain language plus full technical detail, exportable to Markdown and PDF.</p>
</td>
<td width="50%" ="top">
<img src="docs/pics/infra-orbital.gif" alt="Darkmoon Pro orbital attack-surface map: an animated infrastructure graph with exposure rings, per-node badges and the MITRE attack path racing from the internet-facing entry to the database" />
<p align="center"><b>Pro: orbital attack-surface map.</b> A live 3D graph of nodes, connections and per-node , with the MITRE attack path walked across the whole target, and every finding linked to its proposed remediation as a re pull request. Renders in the browser and in VR.</p>
</td>
</tr>
<tr>
<td width="50%" ="top">
<img src="docs/pics/scheduler.png" alt="Darkmoon Pro campaign scheduler for recurring automated pentest campaigns with focus, se and recurrence" />
<p align="center"><b>Pro: scheduled recurring runs.</b> Recurring automated campaigns with FOCUS, se and recurrence built into the web dashboard.</p>
</td>
<td width="50%" ="top">
<img src="docs/pics/campaign.png" alt="Darkmoon Pro campaign view listing the 57 with se and status" />
<p align="center"><b>Pro: campaign view.</b> Every in a campaign with its se and confirmation status.</p>
</td>
</tr>
</table>
🔒 Pro: from finding to fix (automated remediation, paid)
> 🔒 Paid Pro feature. The open source engine finds and pro. Automated remediation into pull requests is a only in Darkmoon Pro.
In the paid Pro tier, every finding flows _finding → sandbox- fix → human-re pull request, retested against the original exploit_, and is ne. On our OWASP Juice Shop demo run, the Pro remediation agent fixed findings end-to-end with a clean li (a fix only counts when the original exploit is re-run and confirmed closed). See the remediation benchmark, the remediation agent docs and the 57 open PRs on ASCIT31/juice-shop.
<di="center">
<a href="
<img src="docs/pics/darkmoon-youtube.png" alt="Watch the demo of the Darkmoon Pro web dashboard running a full autonomous penetration test" width="70%" />
</a>
▶️ Watch the demo (shows the Darkmoon Pro web dashboard)
</div>
🔒 Pro: deploy on any cloud in one click — no box, no marketplace
> 🔒 Paid Pro feature. The open source edition is the CLI shown abo cloud pro ships with Darkmoon Pro (a valid Pro license key is required) and is not part of the open source build.
<di="center">
<a href=" src=" alt="AWS" height="42" /></a>
<a href=" src=" alt="Google Cloud" height="42" /></a>
<a href=" src=" alt="Azure" height="42" /></a>
<a href=" src=" alt="O" height="36" /></a>
</div>
<p align="center">"Do you sell a hardware box?" <b>No.</b> One command turns any cloud VM into a dedicated Darkmoon <b>Pro</b> appliance in your own tenancy — it creates the machine, opens the dashboard port and installs e for you. <b>No proprietary hardware, no cloud marketplace, no lock-in</b> — the same packaged Docker images run on every cloud and on your own bare metal.</p>
<di="center">
Cloud deployment guide → · Docs · Appliance
</div>
---
What is DarkMoon?
DarkMoon is an open-source AI penetration testing platform. Point it at a target you are authorized to test, and it runs the whole assessment on its own: it reasons, plans, and dispatches 50 specialist agents that execute real offensi through a controlled MCP layer, then reports every with the exact command, the raw output and the proof behind it.
It does not replace the pentester. It clears the repetitive part of an assessment with e, so your experts spend their time on judgment, not toil.
---
📊 Benchmark: 57 real on OWASP Juice Shop
Real, reproducible black-box run against OWASP Juice Shop with a cloud frontier model (Anthropic Claude). DarkMoon also runs fully local (Ollama / llama.cpp) behind the Privacy Gateway — so nothing leaves your infrastructure; local-model co depends on the model you run.
| Metric | Result |
|---|---|
| found | 57 (8 critical / 24 high / 21 medium / 4 low) |
| Wall-clock time | 28.5 min |
| Proof-of-exploitation | command + raw output per finding |
| LLM | Anthropic Claude (cloud frontier); local models supported |
Reproduce it and compare tools yourself: ASCIT31/Darkmoon-Benchmarks.
🆚 How DarkMoon compares
| | DarkMoon | strix | shannon | PentAGI |
|---|:--:|:--:|:--:|:--:|
| Runs on local LLM (data ne) | ✅ | ❌ cloud | ❌ cloud | partial |
| Privacy Gateway (local tokenization) | ✅ | ❌ | ❌ | ❌ |
| Acti + Kubernetes | ✅ | ❌ | ❌ | partial |
| Proof-of-exploitation | ✅ | ✅ | ✅ | ✅ |
| Open source | ✅ GPL-3.0 | ✅ | ✅ | ✅ |
*Compiled from public repos/docs (2026-08); corrections welcome via PR.*
---
How It Works
DarkMoon operates as a strategic AI security agent orchestrator aligned with ISO 27001, NIST SP 800-115, and MITRE ATT&CK methodologies.
When you provide a target, the platform automatically:
1. 🔍 Discovers the target en (ports, services, protocols)
2. 🧠 Fingerprints the technology stack (frameworks, CMS, APIs)
3. 🎯 Models the attack surface
4. 🚀 Deploys specialized sub-agents based on detected technologies
5. 🔬 Executes an intelligent scanning loop with reacti
6. ✅ findings with e (requests, payloads, responses)
7. 📝 Generates a structured audit report
Sub-Agent Orchestration
DarkMoon dynamically selects and dispatches specialized agents depending on the technologies discovered:
| Detected Technology | Agent Triggered |
|---|---|
| WordPress, Drupal, Joomla, Magento, PrestaShop, Moodle | CMS-specific agent |
| PHP, Node.js, Flask, ASP.NET, Spring Boot, Ruby on Rails, Go | Stack-specific agent |
| GraphQL | GraphQL agent |
| LLM / AI inference endpoint (OpenAI-compatible, Ollama, vLLM, TGI) | LLM agent |
| Acti | AD agent |
| Kubernetes | Kubernetes agent |
| AWS, Azure, GCP | Cloud-provider agent |
| Entra ID (Microsoft identity) | Identity agent |
| GitHub, GitLab, Jenkins | SCM & CI/CD agent |
| Terraform, Ansible | Infrastructure-as-Code agent |
| Docker, container registries | Container agent |
| HashiCorp Vault | Secrets agent |
| PostgreSQL, MySQL, MSSQL, Oracle | Database agent |
| Redis, RabbitMQ, Kafka, MQTT | Messaging & cache agent |
| Firmware / IoT images | Firmware agent |
| Headless browser required | Headless browser agent |
Multiple agents can execute in parallel across hybrid architectures.
Planes that require credentials to be meaningful (cloud accounts, CI/CD, secret stores, databases, Acti, Kubernetes) are ne on inference. They fire only when a concrete artifact is found (a key, a token, a reachable metadata endpoint) or when you authorize them explicitly, and are otherwise flagged in the report.
> Note: For the complete list of agents, their structure, lifecycle, and how to create custom agents, see Full Documentation, AI Agents.
Architecture O
The AI reasons and plans. The MCP controls what can be executed. The Toolbox runs isolated tools inside Docker. The AI ne touches the system, this is security by design.
> Note: For the full architecture breakdown (deployment diagrams, network flows, security boundaries), see Full Documentation, Architecture.
---
Scope Definition
DarkMoon supports flexible scope definition directly from the command line.
Quick pentest (zero config):
Bug bounty mode (flags activate automatically):
Key flags include FOCUS, EXCLUDE, CREDS, TOKEN, NOISE, SE, FORMAT, and more, all interpreted naturally by the AI.
> Note: For the complete flags reference, asset types, EXCLUDE/FOCUS free-form syntax, and ad multi-target scoping, see Full Documentation, Scope Definition.
---
Integrated Toolbox
DarkMoon ships with a purpose-built Docker image containing 140+ security tools compiled and optimized in a multi-stage build:
| Category | Tools (examples) |
|---|---|
| Port scanning | Naabu (discovery), nmap (targeted service probes) |
| Web scanning | Nuclei, ffuf, dirb, sqlmap, Arjun, wafw00f |
| Recon & crawling | Subfinder, Katana, Waybackurls, httpx |
| CMS | WPScan, CMSeeK, WhatWeb |
| Acti | NetExec, BloodHound, Impacket (30+ scripts) |
| Kubernetes | kubectl, Kubescape, Kubeletctl, kube-bench, rbac-police |
| Cloud CLIs | aws, az, gcloud, gsutil, bq |
| Databases & cache | psql, mysql, redis-cli, sqlite3 |
| Firmware / IoT | binwalk, unsquashfs, sasquatch, firmwalker |
| Cracking | hashcat, john, 7z2john |
| Network | Hydra, curl, dig, SNMP tools |
| Browser | Lightpanda (headless) |
All tools are directly accessible, no path configuration needed.
> Note: For the complete tools list with installation details and how to add new tools, see Full Documentation, Toolbox.
---
📖 Documentation Guide
DarkMoon's Full Documentation covers e you need to operate the platform. Here is a quick reference to the most important sections:
| Topic | What You'll Find | Link |
|---|---|---|
| GPU & Dri | NVIDIA troubleshooting for Docker, WSL, and nati | GPU Guide |
| En | LLM provider configuration, API keys, model selection | En Config |
| Startup & Build | install.sh behavior, docker compose build, stack management | Build & Launch |
| Scope & Flags | TARGET syntax, bug bounty mode, FOCUS/EXCLUDE, credentials | Scope Definition |
| Assessment Workflow | Step-by-step: discovery, fingerprinting, agents, reporting | Assessment Engine |
| Real-Time Session Logs | Monitor commands executed by the MCP server live | Session Logs |
| AI Agents | Agent structure, lifecycle, how to create or modify agents | AI Agents |
| Architecture | Deployment diagrams, security boundaries, execution flow | Architecture |
| Toolbox | Complete tool list, adding tools, Docker image internals | Toolbox |
| MCP Workflows | Workflow structure, creating custom workflows, best practices | MCP Workflows |
| A Tools List | Full table of 142 security tools with paths and sources | Tools List |
| Training Labs | Recommended labs to train DarkMoon | Pentester Labs |
| Remediation Agent (Pro) | Findings → sandbox- fix → pull request for human review (ne) | Remediation Agent |
| n8n (Pro) | Community node to trigger a pentest, pull findings and review fix PRs from an n8n workflow | n8n Node |
---
Use Cases
DarkMoon is designed as a security testing platform for:
---
Example Prompts
> Note: For more prompt examples including DVGA, Juice Shop, and headless browser scenarios, see Full Documentation, Prompt Examples.
---
Contributing
DarkMoon is open source and welcomes contributions. Whether you want to add new agents, integrate tools, create workflows, or impro, see CONTRIBUTING.md for guidelines.
---
License
This project is licensed under the GNU General Public License v3.0. See LICENSE for details.
---
<di="center">
Built by ASC-IT with 💚 for the global security community
🔒 Open Source · 🤖 AI-Powered · 🇫🇷 Made in France
⭐ Star us on GitHub · 📖 Full Documentation · ▶️ Watch the Demo (Pro dashboard)
</div>
项目信息
开发语言:Python
Star 数:994
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Open-source autonomous AI penetration testing. 50 specialist agents across web, API, cloud, Active Directory, Kubernetes, CI/CD and AI/LLM (OWASP LLM Top 10). Runs on a local LLM behind a Privacy Gateway. Integrates with GitHub, GitLab, Jenkins, VS Code, JetBrains, n8n, Grafana & Splunk.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Dark-Moon - Open-source autonomous AI penetration testing. 50 |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:34:32 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 371 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |