 安全软件
点击放大
Cybermes - Autonomous Offensive Security, Bug Bounty & Red Te
项目说明
<di="center">
Cybermes
Autonomous Offensi & Bug Bounty Automation Framework
<p align="center">
<a href=" target="_blank" rel="noopener noreferrer">
<img src=" alt="Zyrexnn%2FCybermes | Trendshift" width="250" height="55"/>
</a>
</p>
![Release]()
![Go: 1.22+]()
![Python: 3.11+]()


<img src="assets/bannerterbaru.jpeg" alt="Cybermes Architecture & Operational Pipeline" width="100%" style="border-radius: 8px; margin: 18px 0;">
<p align="center">
<b>Cybermes</b> is an offensi assistant and automation framework designed for authorized bug bounty hunting, reconnaissance, research, and structured reporting.
<br>
It combines native Go performance utilities, 200+ modular offensi playbooks, token-optimized streaming pipelines, and full Model Context Protocol (MCP) support for AI coding en.
</p>
Installation • Architecture • Why Cybermes? • Features • Workspace Structure • Toolchain • Documentation
</div>
---
Installation & Setup
Cybermes can be used directly through your AI assistant via Model Context Protocol (MCP) or executed as a standalone CLI / pipeline.
1. MCP Ser (Recommended for AI Workflows)
Cybermes includes a high-performance native Go MCP server (cybermes-mcp) that exposes 10+ security tools and context pro directly to AI coding en (Google Antigravity / Gemini, Kilo Code, Cursor, Claude Desktop, Windsurf, Cline, Roo Code, OpenCode, Claude Code CLI, Continue.dev, Zed, Hermes, and Codex).
#### Uni Auto-Installer (1-Click)
#### Global Installation (No NPX Startup Latency)
#### Local Interactive MCP Manager & Optimizer
#### Manual Client Configuration
To manually register the MCP server in your client configuration (mcpServers section):
> For client-specific paths, direct flags (--kilo, --gemini, --global, --dry-run), and nati setup, see the MCP Integration Guide.
---
2. Standalone CLI Installation
If you plan to run Cybermes directly from the terminal or in headless CI/CD pipelines:
#### Windows (Nati)
*(For WSL2 or manual setups, refer to the Windows Installation Guide)*
#### Linux / macOS
#### Docker Container
---
3. En Health Check
system dependencies, path bindings, and tool integrity:
---
4. Running an Assessment
> Local Testing: Run the included mock application in examples/:
>
---
Architecture & Operational Pipeline
Cybermes provides two distinct operational workflows tailored to different execution en:
1. Autonomous Hermes CLI Workflow: Fully autonomous terminal/headless execution where the local Hermes engine reasons, spawns subprocesses, filters streaming outputs via smart_pipe, and executes loops directly on the OS.
2. Model Context Protocol (MCP) Ser: Client-Ser exposing 10+ high-performance native Go tools and 200+ security SOPs o 2.0 stdio to external AI coding assistants and IDEs (Gemini/Antigravity, Claude Desktop, Cursor, Windsurf, Cline, Roo Code).
1. 🤖 Autonomous Hermes CLI Workflow
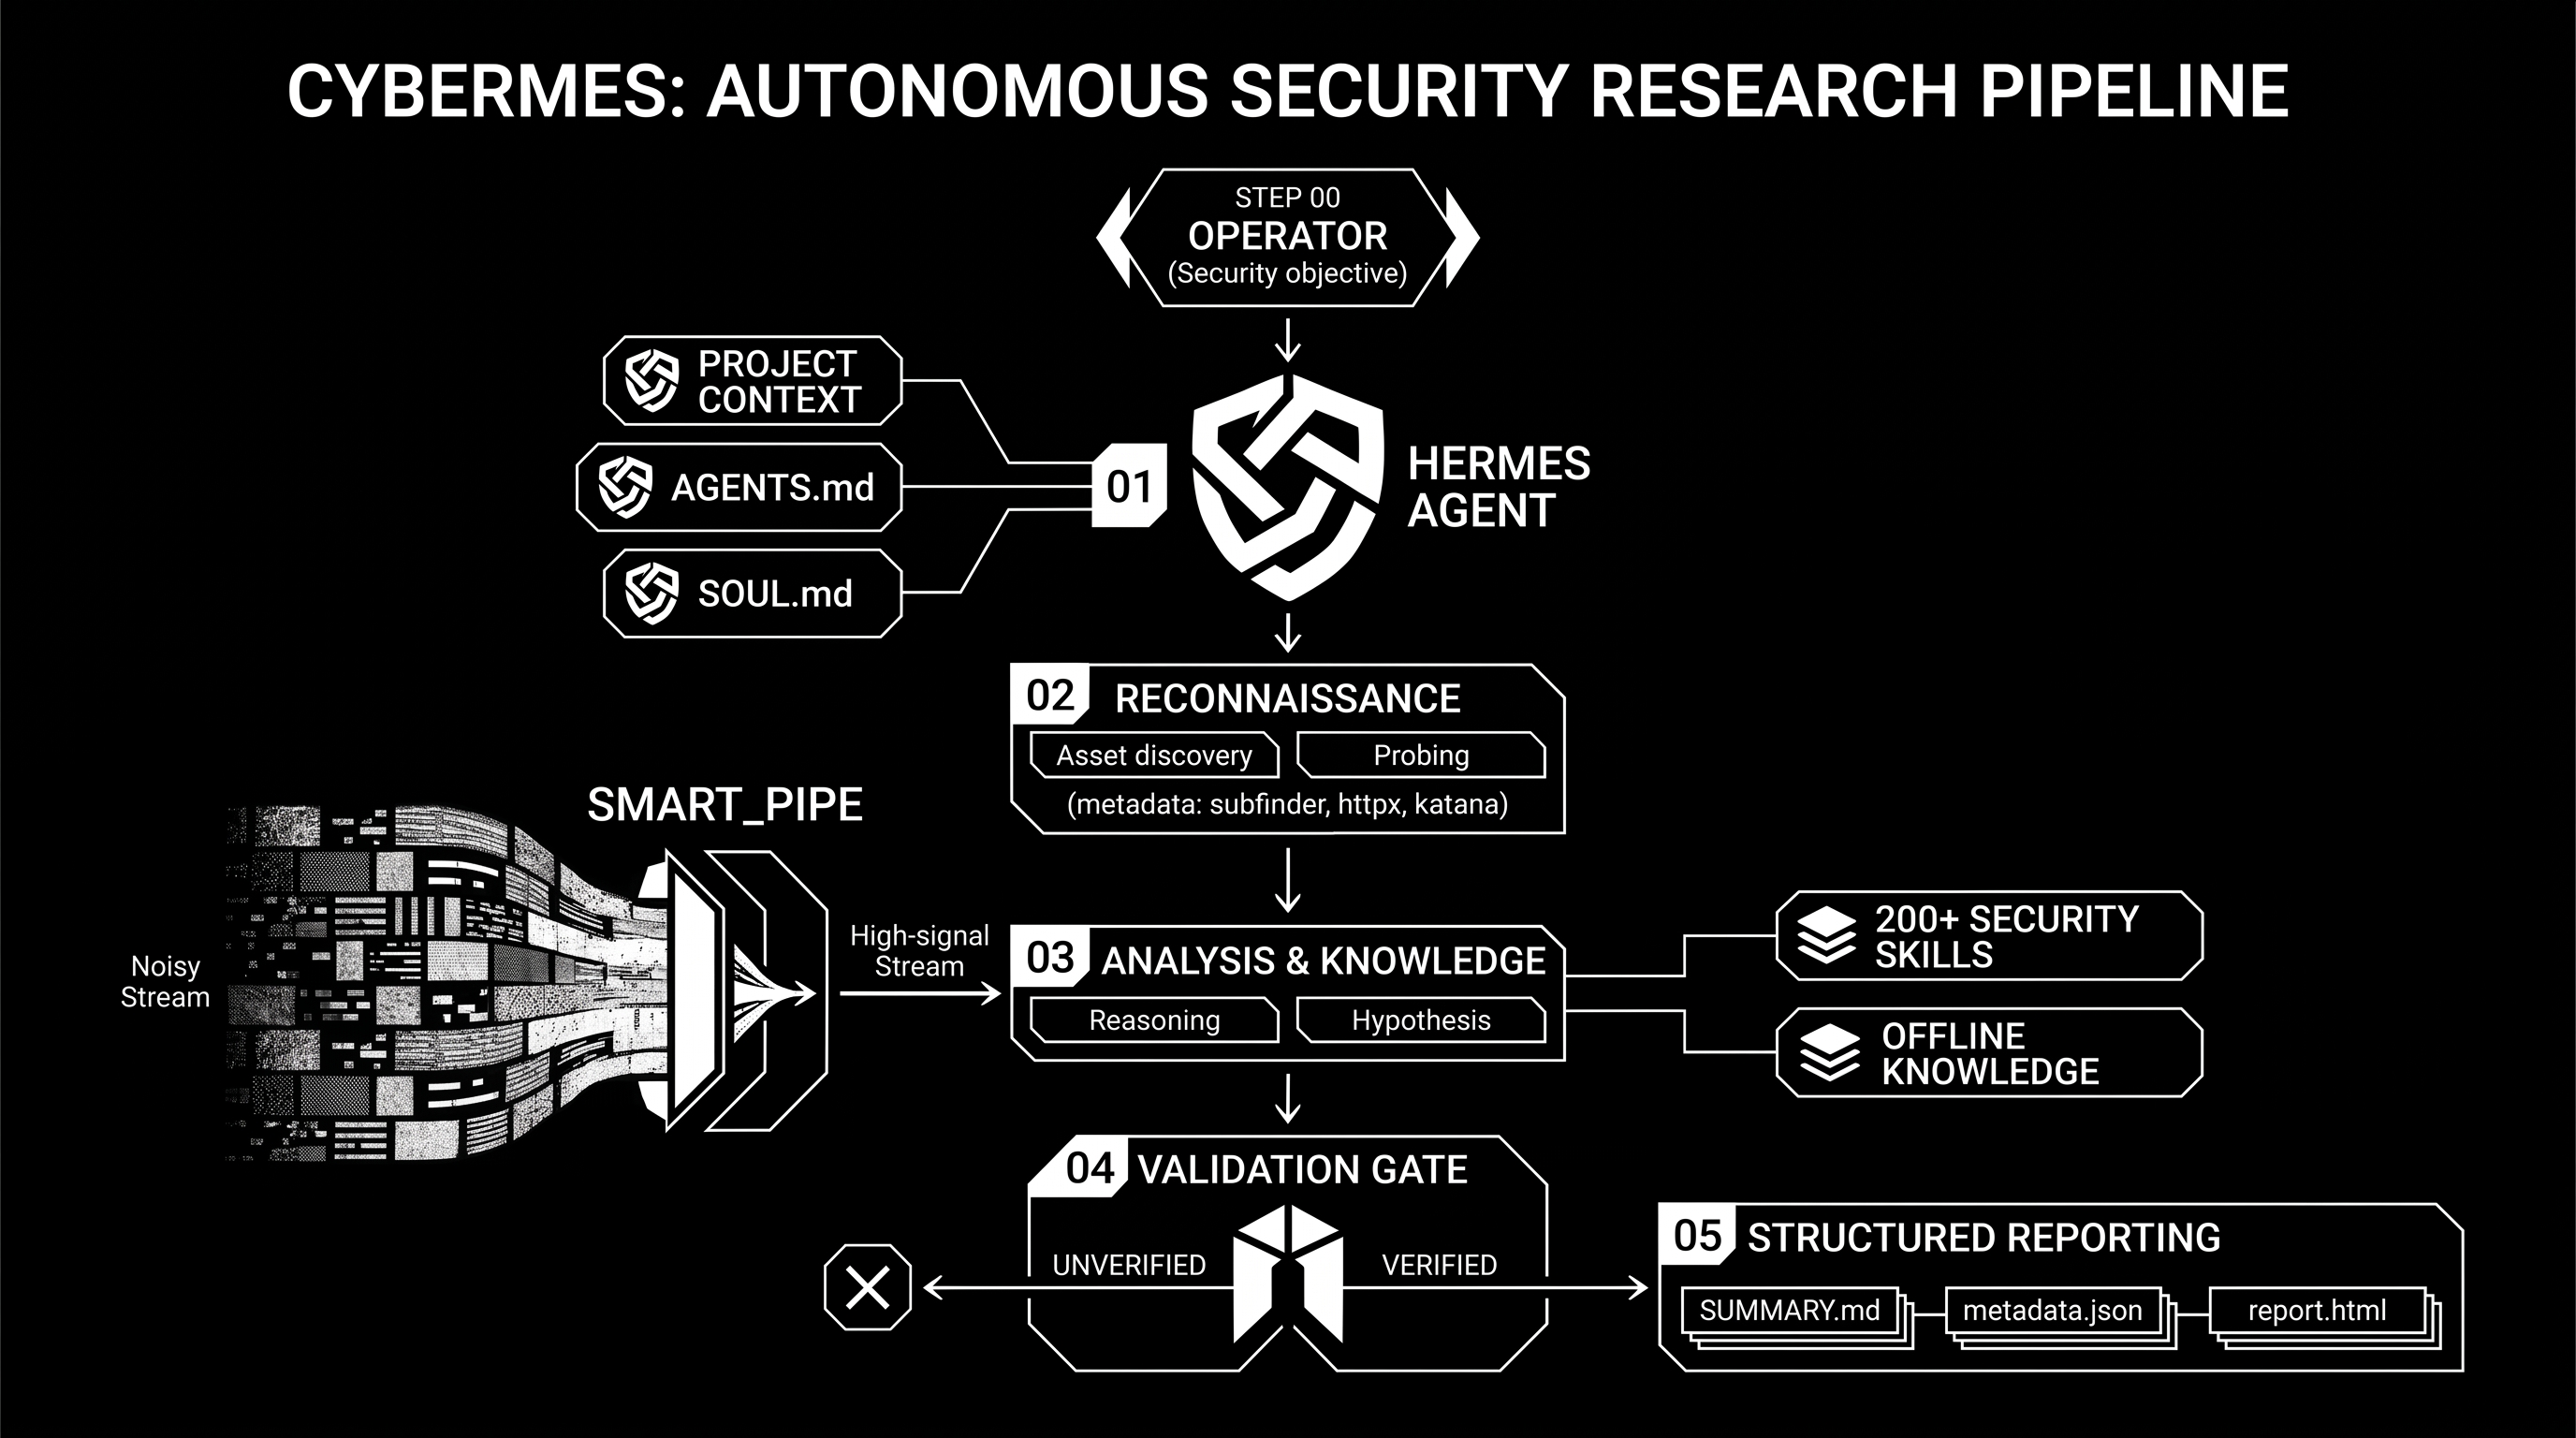
The standalone CLI mode utilizes the built-in Hermes Agent engine (hermes.exe / cybermes) as an autonomous reasoning brain. The operator provides a target prompt, and Hermes autonomously maps the attack surface, invokes CLI binaries, filters outputs through smart_pipe to prevent LLM context saturation, hypotheses with standalone PoC scripts, and produces executi.
<di="center">
<img src="assets/cybermes_hermes_workflow.jpeg" alt="Cybermes Hermes CLI Workflow" width="85%" style="max-width: 800px; border-radius: 8px; margin: 12px 0; border: 1px solid #30363d;">
</div>
#### Hermes CLI Execution Flow:
#### Hermes Pipeline Stages:
1. Target Ingestion & Scope : Operator issues a single CLI prompt. Hermes resol boundaries and initializes target workspace directories (recon/<TARGET_SLUG>/ and reports/<TARGET_SLUG>/).
2. Autonomous Toolchain Orchestration: Hermes spawns external reconnaissance tools (subfinder, httpx, katana, ffuf) in sequence.
3. High-Speed Stream Filtering (smart_pipe): Raw outputs are archived to disk in recon/ while smart_pipe streams only relevant endpoints, HTTP status codes, and leaked secrets into Hermes' context window.
4. Hypothesis & Skill Retrieval: Hermes queries the offline database (search_knowledge) and loads relevant offensi from skills/.
5. Deterministic PoC Gate: Hermes writes and executes a non-destructi (pocs/poc_<vuln>.py), capturing raw HTTP request/response e.
6. Report Compilation: Calls native Go aggregate_reports and generate_pdf.py to compile SUMMARY.md, metadata.json, interactive report.html, and REPORT_<target>.pdf.
---
2. 🔌 Cybermes MCP Ser
In the MCP workflow, Cybermes operates as a nati 2.0 server (cybermes-mcp) pro specialized security tools, prompts, and context pro directly to external AI assistants and IDEs (Cursor, Antigravity / Gemini, Claude, Windsurf, VS Code / Cline). The external model acts as the reasoning engine while Cybermes handles high-speed tool execution, local knowledge lookups, and reporting.
<di="center">
<img src="assets/cybermes_mcp_workflow.jpeg" alt="Cybermes MCP Ser" width="85%" style="max-width: 800px; border-radius: 8px; margin: 12px 0; border: 1px solid #30363d;">
</div>
#### MCP Protocol Execution Flow:
#### MCP Tooling & Interaction Lifecycle:
1. Handshake & Discovery: AI Client starts cybermes-mcp and discovers exposed tools, schemas, and resource templates.
2. En & Scope Assessment: The AI invokes cybermes_ and cybermes_check_en to inspect target authorization and system tool health.
3. Structured Recon & Secret Mining: AI executes cybermes_recon_crawl, cybermes_http_probe, or cybermes_scan_secrets. The MCP ser compiled routines and returns clean, structured JSON results without context bloat.
4. On-Demand Playbook & Exploit Lookup: When a is identified, the AI calls cybermes_search_knowledge and cybermes_get_skill to retrie exploitation steps in sub-50ms.
5. Deterministic E Recording & Aggregation: AI logs findings with cybermes_record_finding / cybermes_record_e and compiles target deli via cybermes_aggregate_report.
---
3. ⚖️ Hermes CLI MCP Comparison
| Feature / Dimension | 🤖 Hermes CLI Workflow | 🔌 Cybermes MCP Workflow |
| :--- | :--- | :--- |
| Primary Interface | Terminal / PowerShell / Docker CLI | AI Coding Editors / IDEs / Web Chat (JSON-RPC) |
| Reasoning Engine | Built-in Hermes Autonomous Agent (hermes.exe) | Host AI Client (Gemini, Claude 3.7, GPT-4o, etc.) |
| Execution Model | Autonomous sub-process loop from CLI prompt | Modular Tool & Context calls requested by the AI |
| Token Optimization | OS pipe streaming via Go smart_pipe | Nati schema with compact response filters |
| Knowledge Access | CLI binary execution (search_knowledge) | In-memory MCP tools (cybermes_search_knowledge, cybermes_get_skill) |
| Deli Output | Direct filesystem generation in reports/<TARGET_SLUG>/ | Programmatic management via cybermes_aggregate_report |
---
Why Cybermes?
| Challenge | Traditional Approach | Cybermes Solution |
| :--- | :--- | :--- |
| AI Assistant Integration | Manual copy-pasting of terminal outputs or fragile custom wrappers. | Native Go MCP Server (cybermes-mcp): Standardized JSON-RPC 2.0 integration exposing 10+ security tools directly to AI clients. |
| LLM Token & Context Noise | Fuzzer/crawler outputs flood context with thousands of lines of 404s and static assets. | High-Speed Stream Filter (smart_pipe): Pure Go filter that archives raw logs to disk while streaming only high-signal endpoints, status codes, and secrets. |
| Exploit | Speculative or pattern-matched alerts without reproducible . | Zero-False-Positive PoC Gate: Requires standalone, non-destructi scripts (pocs/poc_<name>.py) and raw HTTP traces before logging findings. |
| Payload & Methodology Retrieval | Manually searching external wikis, repositories, and cheat sheets online. | Sub-50ms Local Knowledge Base (search_knowledge): Instant offline query engine across 200+ SOP playbooks, PayloadsAllTheThings, and HackTricks datasets. |
| Structured Deli | Unorganized text dumps requiring tedious manual report compilation. | Multi-Format Report Aggregator: Automated generation of SUMMARY.md, metadata.json, standalone interactive HTML, and print-ready REPORT_<target>.pdf. |
| OS & En Portability | Most offensi assume Kali/Linux, complicating Windows setups. | Nati Support: Automated nati for Windows (PowerShell), Linux, macOS, and Docker with a built-in health check and repair tool (doctor.py). |
---
Core Features
smart_pipe), credential scanning (secret_scan), offline knowledge retrieval (search_knowledge), and report aggregation (aggregate_reports).cybermes-mcp) exposing security tools and context pro to AI assistants like Claude Desktop, Cursor, Windsurf, and VS Code / Cline.skills/ co API security (IDOR/BOLA, JWT, BPLA), web (SSRF, XSS, SQLi, Race Conditions), and cloud misconfigurations.subfinder, httpx, katana, ffuf, nuclei, and sqlmap.SUMMARY.md), JSON metrics (metadata.json), standalone HTML dashboards, and PDF reports (REPORT_<target>.pdf).---
Target Workspace & Deli
Every target assessment creates a dedicated directory structure under reports/ and recon/:
---
Toolchain
| Tool | Type | Purpose | Standard Syntax |
| :--- | :--- | :--- | :--- |
| smart_pipe | Go Binary | Stream output filter & context token optimizer | katana -u <url> \| smart_pipe --target <slug> --tool katana |
| secret_scan | Go Binary | Multi-pattern credential leak scanner | secret_scan recon/<slug>/ |
| search_knowledge| Go Binary | Sub-50ms offline exploit & payload search | search_knowledge "jwt algorithm confusion" |
| aggregate_reports| Go Binary | Markdown findings indexer & report compiler | aggregate_reports <slug> |
| cybermes-mcp | Go Binary / NPX | Native MCP Server for AI assistants | npx -y cybermes-mcp |
| subfinder | External | Passi discovery | subfinder -d <target> -silent |
| httpx | External | Web probing & technology fingerprinting | httpx -u <url> -tech-detect |
| katana | External | Web crawler & SPA endpoint miner | katana -u <url> -depth 3 |
| ffuf | External | High-speed web fuzzer | ffuf -u <url>/FUZZ -w <wordlist> |
| nuclei | External | Template-based scanner | nuclei -u <url> -tags cve |
| sqlmap | Python | Automated SQL injection auditor | sqlmap -u "<url>?id=1" --batch |
| doctor.py | Python | En health check & auto-repair | python tools/doctor.py --fix |
| generate_pdf.py | Python | PDF and HTML executi generator | python tools/generate_pdf.py <slug> |
---
Documentation
Detailed guides and references are a in the docs/ directory:
---
Acknowledgments & Upstream Credits
Cybermes integrates and builds upon foundational work from the open-source and offensi research communities:
| Project / Tool | Maintainer / Author | Contribution / Reference |
| :--- | :--- | :--- |
| HackTricks | | Pri escalation, service exploitation & offensi base |
| PayloadsAllTheThings | | Web application payloads and bypass |
| ProjectDiscovery Suite | ProjectDiscovery Team | Core toolchain (nuclei, httpx, subfinder, katana) |
| SQLMap | Bernardo Damele & Mirosla | Automated SQL injection auditor |
| Claude-BugHunter | -96 | Bug bounty engagement patterns & playbooks |
| Strix Framework | Strix Security Team | Autonomous multi-agent coordination architecture |
| FFuF | | High-speed web fuzzer |
| Hermes-Agent | NousResearch | Autonomous agent core framework |
*(See ATTRIBUTION.md for full license notices and upstream details)*
---
Contributors
Thank you to e who helps build, maintain, and research Cybermes:
<di="center">
<table>
<tr>
<td align="center" width="160px">
<a href="
<img src=" width="80px" height="80px" alt="Zyrexnn" style="border-radius: 50%; border: 3px solid #00d2ff; box-shadow: 0 0 14px rgba(0, 210, 255, 0.7); padding: 2px;" /><br />
<sub><b>Zyrexnn</b></sub>
</a><br />
<a href=" src=" alt="Project Lead" /></a>
</td>
<td align="center" width="130px">
<a href="
<img src=" width="65px" height="65px" alt="msarg44" style="border-radius: 50%; border: 2px solid #2ea44f; padding: 2px;" /><br />
<sub><b>msarg44</b></sub>
</a><br />
<a href=" src=" alt="Fork / PR" /></a>
</td>
<td align="center" width="130px">
<a href="
<img src=" width="65px" height="65px" alt="Mortify4315" style="border-radius: 50%; border: 2px solid #2ea44f; padding: 2px;" /><br />
<sub><b>Mortify4315</b></sub>
</a><br />
<a href=" src=" alt="Fork / PR" /></a>
</td>
<td align="center" width="130px">
<a href="
<img src=" width="65px" height="65px" alt="sizoune" style="border-radius: 50%; border: 2px solid #2ea44f; padding: 2px;" /><br />
<sub><b>sizoune</b></sub>
</a><br />
<a href=" src=" alt="Fork / PR" /></a>
</td>
<td align="center" width="130px">
<a href="
<img src=" width="65px" height="65px" alt="xsoft" style="border-radius: 50%; border: 2px solid #8957e5; padding: 2px;" /><br />
<sub><b>xsoft</b></sub>
</a><br />
<a href=" src=" alt="Accepted Issue" /></a>
</td>
<td align="center" width="130px">
<a href="
<img src=" width="65px" height="65px" alt="Muzakie-ID" style="border-radius: 50%; border: 2px solid #8957e5; padding: 2px;" /><br />
<sub><b>Muzakie-ID</b></sub>
</a><br />
<a href=" src=" alt="Accepted Issue" /></a>
</td>
</tr>
</table>
</div>
| Contributor | Type | Contribution | Reference |
| :--- | :--- | :--- | :--- |
| | Project Lead | Creator, Core Architecture & Offensi | Main |
| | Fork / PR | Playwright PDF rendering engine fix | #1 |
| | Fork / PR | Windows Python launcher fallback & Long Path documentation | #4, #5 |
| | Fork / PR | Target-specific PDF report filename & Docker gateway crash-loop fix | #17, #20 |
| | Accepted Issue | Linux setup audit, Docker config mounts & workflow diagnostic report | #7 |
| -ID | Accepted Issue | Windows PowerShell setup & script parser bug report | #10 |
Want to contribute? Check out our Contributing Guide and Contributors List.
---
License
This project is licensed under the Apache License 2.0.
Third-party research materials, datasets, and upstream tools referenced or incorporated within this repository retain their respecti licenses (see ATTRIBUTION.md).
---
Legal & Ethical Disclaimer
> IMPORTANT: Cybermes is de exclusively for authorized security testing, legitimate bug bounty research, and academic security education.
>
> Testing against targets without explicit, prior written permission from the target owner is illegal and strictly prohibited. The maintainers assume no liability and are not responsible for any misuse, damage, or legal consequences resulting from this tool.
项目信息
开发语言:Python
Star 数:917
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Autonomous Offensive Security, Bug Bounty & Red Teaming Agent Framework powered by Hermes Agent, specialized reasoning skills, and multi-model LLM orchestration.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Cybermes - Autonomous Offensive Security, Bug Bounty & Red Te |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:35:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 80 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |