 安全软件
点击放大
Garud - An automation tool that scans sub-domains, sub-dom
项目说明
<h1 align="center">
<br>
<a href=" src=".github/img/garud.png" width="500px" alt="Garud"></a>
</h1>
<h4 align="center">An automation tool that scans sub-domains, sub-domain takeover and then filters out xss, ssti, ssrf and more injection point parameters.</h4>
<p align="center">
<a href="#"><img src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href=" src="
<a href="#"><img src="
<a href=" src="
</p>
---
I made this tool to automate my recon and save my time. It really give me headache always type such command and then wait to complete one command and I type other command. So I collected some of the tools which is widely used in the bugbounty field. In this script I used Assetfinder, subfinder, amass, httpx, sublister, gauplus and gf patterns and then it uses dirsearch, dalfox, nuclei and kxss to find some low-hanging fruits.<br/>
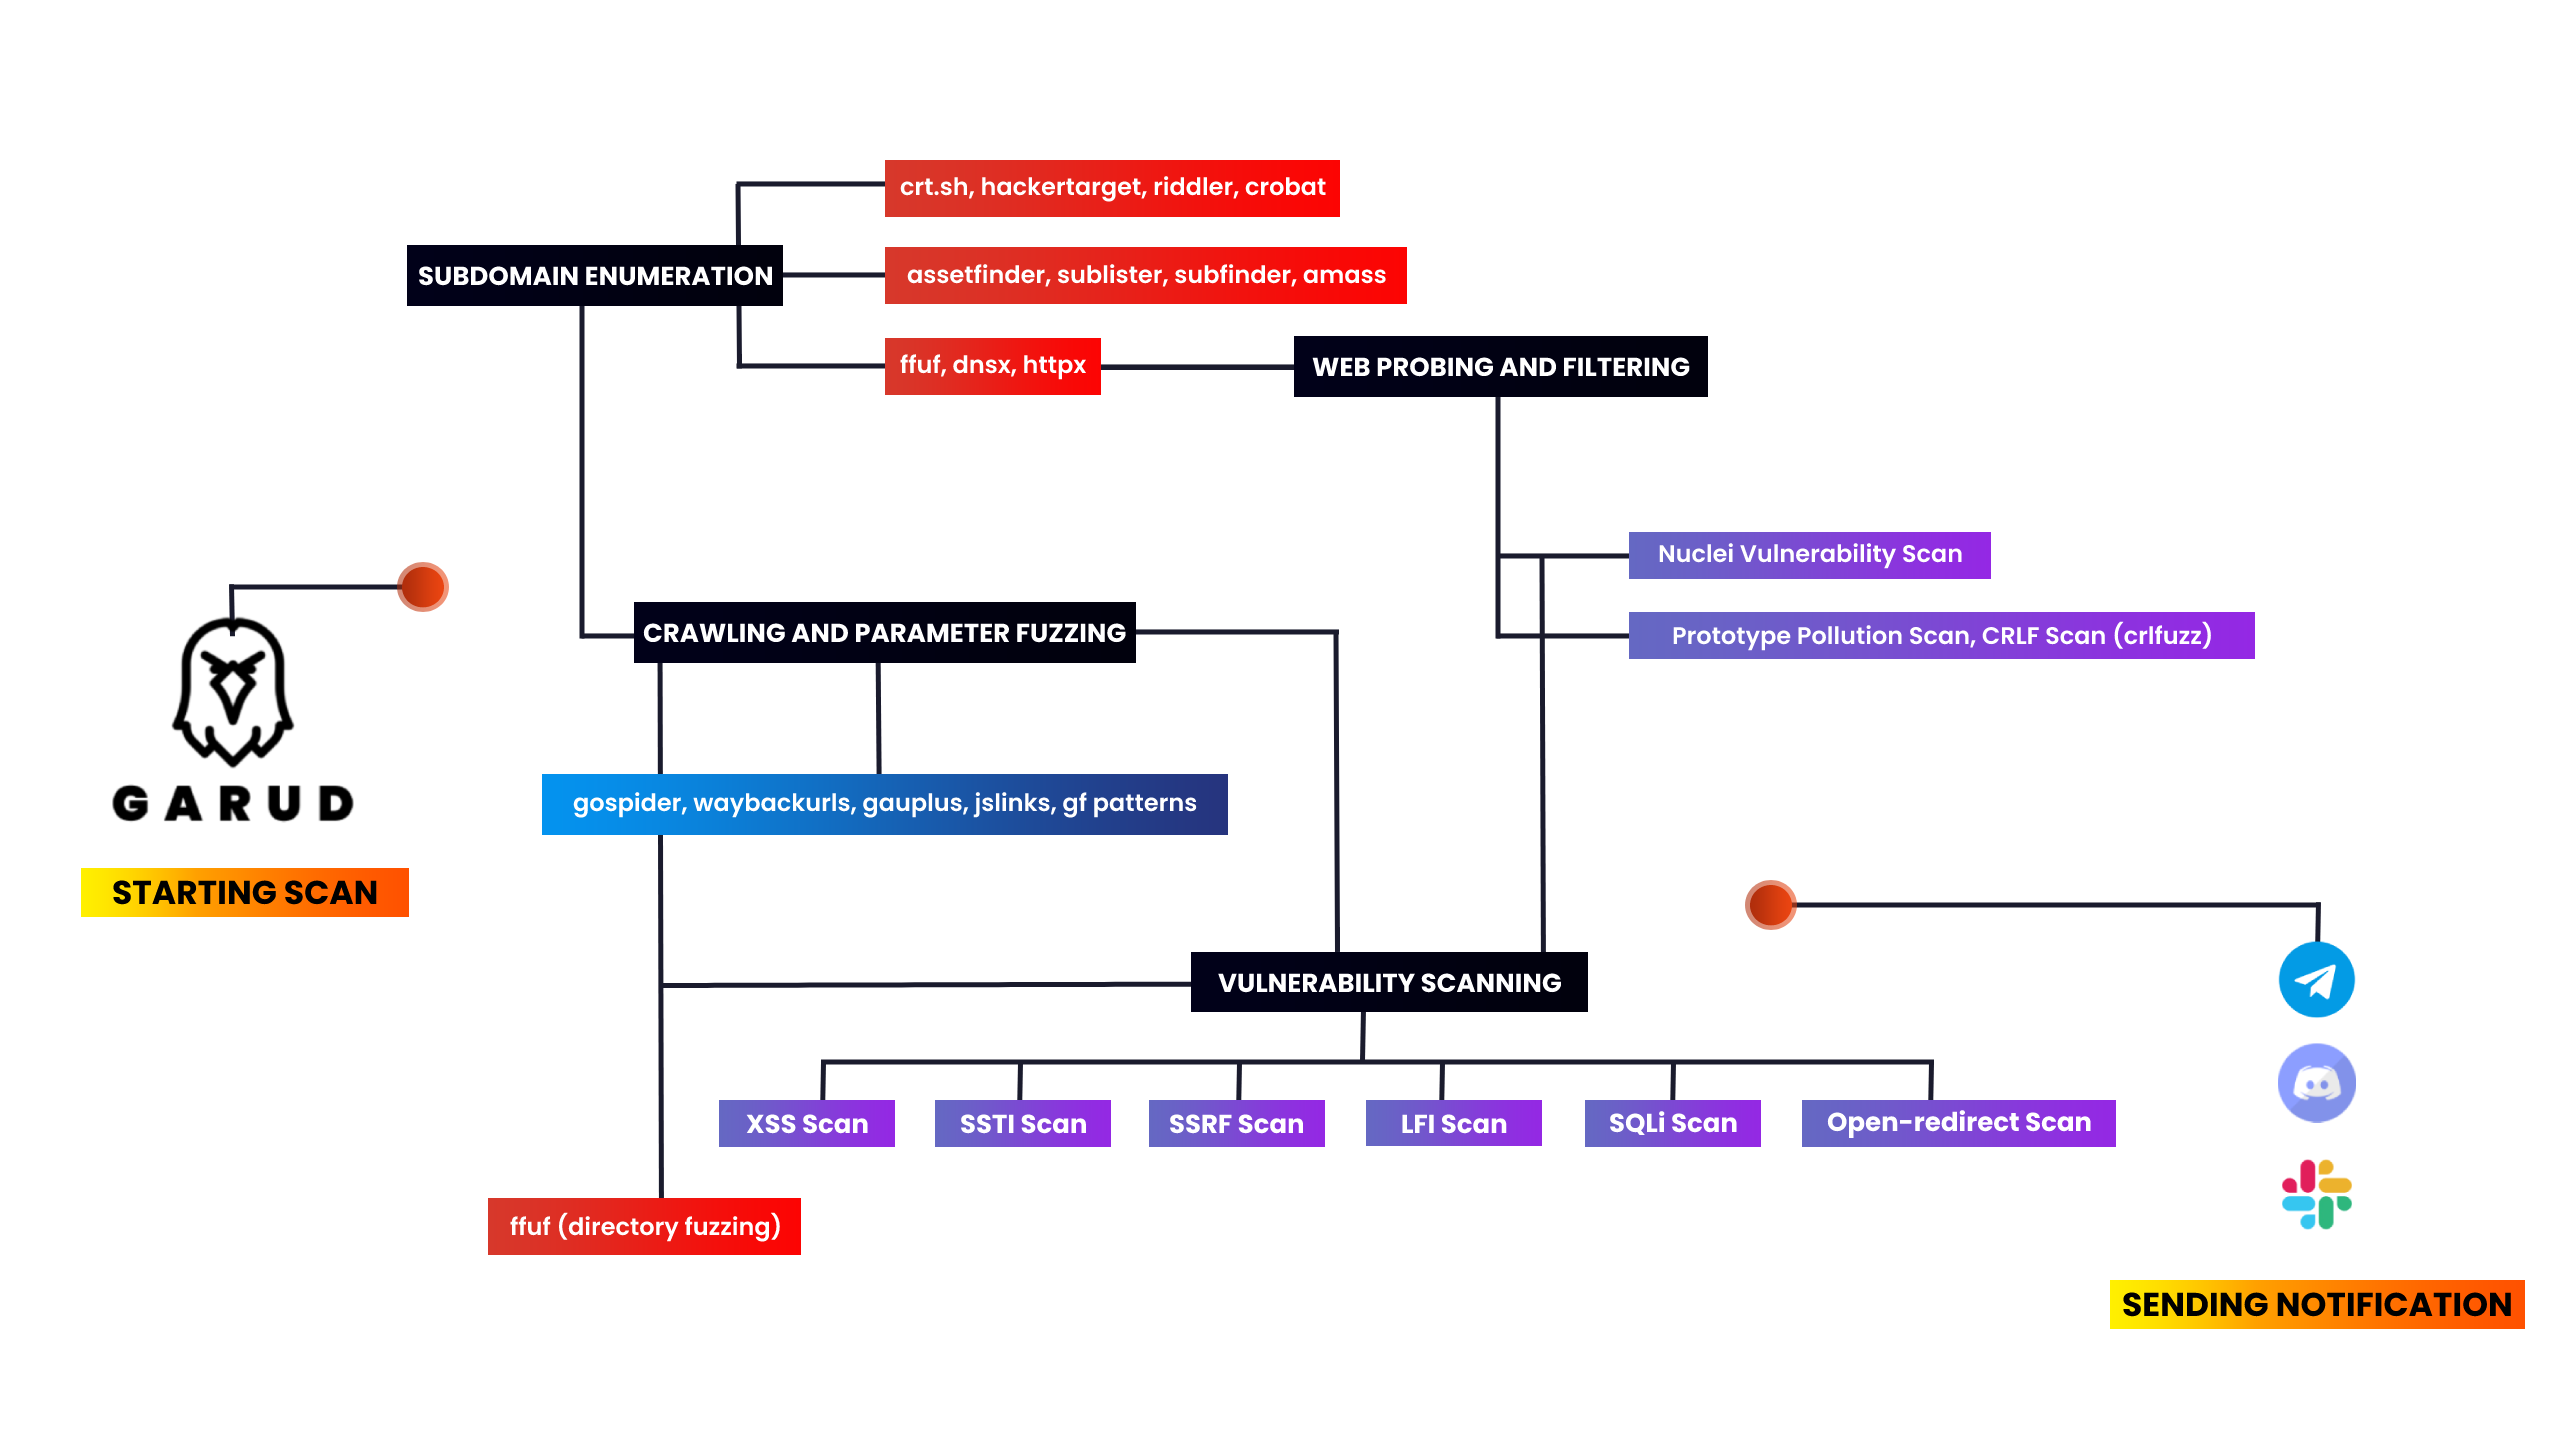
The script first enumerates all the subdomains of the gi domain using assetfinder, sublister, subfinder and amass then filters all li from the whole subdomain list then it extarct titles of the subdomains using httpx then it scans for subdomain takeo nuclei. Then it uses gauplus to extract paramters of the gi then it use gf patterns to filters xss, ssti, ssrf, sqli params from that gi and then it scans for low hanging fruits as well. Then it'll save all the output in a text file like target-xss.txt. Then it will send the notifications about the scan using notify. <br/>
<h3 align="left">How garud works</h3>
<p align="center"><br/>
<img src=".github/img/mindmap.png" alt="garud mindmap"><br/>
<!-- <img src="img/roadmap.png" alt="How garud works""> -->
</p><br/>
<h3>Installation</h3>
Requirements: `Go Language and Python 3.<br>
System requirements: Recommended to run on vps with 1VCPU and 2GB RAM.<br>
Tools used - You must need to install these tools to use this script<br>
<a href="subfinder</a> •sublist3r
<a href="</a> •gf patterns
<a href="</a> •dnsx
<a href="</a> •assetfinder
<a href="</a> •httpx
<a href="</a> •kxss
<a href="</a> •nuclei
<a href="</a> •dalfox
<a href="</a> •anew
<a href="</a> •notify
<a href="</a> •aquatone
<a href="</a> •amass
<a href="</a> •gau
<a href="</a> •crlfuzz
<a href="</a> •uro
<a href="</a> •ffuf
<a href="</a> •naabu
<a href="</a> •crobat
<a href="</a> •gobuster
<a href="</a> •gospider
<a href="</a> •waybackurls
<a href="</a><br>
> Note: If you encounter any-issue while running install.sh file or garud run sed -i -e 's/\r$//' install.sh
<h3>Usage</h3>
Fix errors while using or installing Garud
You can also copy the error and search on google this will make your debugging skills better ;)
Example Usage
Exclude out of scope domains
With all flags
Hide output in the terminal
Store output in a single json file
Docker
Contributed by
This image needs to be built with Buildkit
To run the container
Garud runs as root inside the container & so it is ad to configure Linux Namespaces
1. Isolate containers with a user namespace
2. Use Linux user namespaces to fix permissions in docker
<h3>Notifications</h3>
• •configure-notify
<p align="left">
<h3>Donate</h3>
|buymeacoffee.com/R0X4R|payU India|kofi.com/R0X4R|
|--------|--------|------|
Thanks to the authors of the tools used in this script.
@lc @de @1ndianl33t @w9w @OJ -project
Thanks to all the contributors contributors.md`
Warning: This code was originally created for personal use, it generates a substantial amount of traffic, please use with caution.
项目信息
开发语言:Shell
Star 数:809
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for some low hanging vulnerabilities automatically.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Garud - An automation tool that scans sub-domains, sub-dom |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:35:21 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 97 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |