 安全软件
点击放大
numasec - The AI Agent for Cyber Security.
项目说明
<h1 align="center">numasec</h1>
<p align="center">
<b>The open source AI security agent.</b>
</p>
<p align="center">
Give your terminal a security brain.
</p>
<p align="center">
Run security workflows with your local tools, agents, runbooks, findings, e, replay and reports.
</p>
<p align="center">
<code>npm install -g numasec</code>
</p>
<p align="center">
<a href=" src=" alt="CI"></a>
<a href=" src=" alt="release"></a>
<a href=" src=" alt="npm"></a>
<a href=" src=" alt="npm downloads"></a>
<a href=" src=" alt="GitHub stars"></a>
<a href="LICENSE"><img src=" alt="AGPL-3.0-or-later license"></a>
</p>
<p align="center">
<img src="assets/topreadme.png" alt="numasec AI security agent running in the terminal" width="920" />
</p>
<p align="center">
<a href="#demo">Demo</a> |
<a href="#why-numasec">Why</a> |
<a href="#what-it-feels-like">What it feels like</a> |
<a href="#try-it">Try it</a> |
<a href="#what-it-does">What it does</a> |
<a href="#commands">Commands</a> |
<a href="#architecture">Architecture</a> |
<a href="#roadmap">Roadmap</a>
</p>
---
What is numasec?
numasec is an AI security agent that runs in your terminal.
It uses the tools already installed on your machine, follows security runbooks, switches between cyber agents, keeps the operation context ali findings, stores e and helps turn the work into reports.
It is built for people who already li shell, browser, HTTP requests, scanners, ad, notes and reports.
A security agent for the workflow you already have.
Demo
<p align="center">
<a href="assets/demo.mp4">
<img src="assets/demo-preview.gif" alt="numasec running a scoped security operation from the terminal" width="940" />
</a>
<br />
<sub>Click the preview for the full terminal recording.</sub>
</p>
Why numasec
Security work does not happen in one clean place.
You mo terminal commands, browser work, HTTP requests, local tools, scanners, ad, notes, screenshots, findings and reports.
AI can help, but only if it li that workflow.
numasec gives the model a security workspace instead of just a chat box. It keeps the target, scope, tools, runbooks, findings, e, replay and report state together while the work is happening.
The goal is simple:
make security work feel faster, sharper and less scattered.
numasec is strongest today for authorized AppSec and Pentest workflows. Other cyber surfaces exist or are possible, but they are not marketed as equally mature yet.
Why now
Coding agents changed how de work.
They read code, run commands, edit files, execute tests and stay inside the de loop.
Security needs the same shift, but security work has different constraints.
A security agent needs to know the target, stay inside scope, use the local toolchain, remember what happened, separate noise from findings and keep enough context to produce useful output later.
That is what numasec is trying to become:
the open source AI security agent for the terminal.
What it feels like
Open numasec inside the workspace you are testing, pick the right security agent, check which local tools are a, then start a runbook and let the agent help you mo the workflow.
When the work changes, switch posture. When something matters, keep the finding, e, replay and report context close to the operation instead of scattering it across shell history, screenshots and notes.
Then come back later and resume without starting from zero.
Product tour
numasec starts like a terminal agent, then the security work begins, and it becomes a workspace.
<p align="center">
<img src="assets/dashboard.png" alt="numasec chat-first security console home screen" width="840" />
</p>
You get the model, the acti, the command palette, the working directory and the prompt. The point is not to leave your terminal; the point is to make the terminal smarter.
<p align="center">
<img src="assets/findings.png" alt="numasec findings lens with e, replay, reportability and operation sidebar" width="940" />
</p>
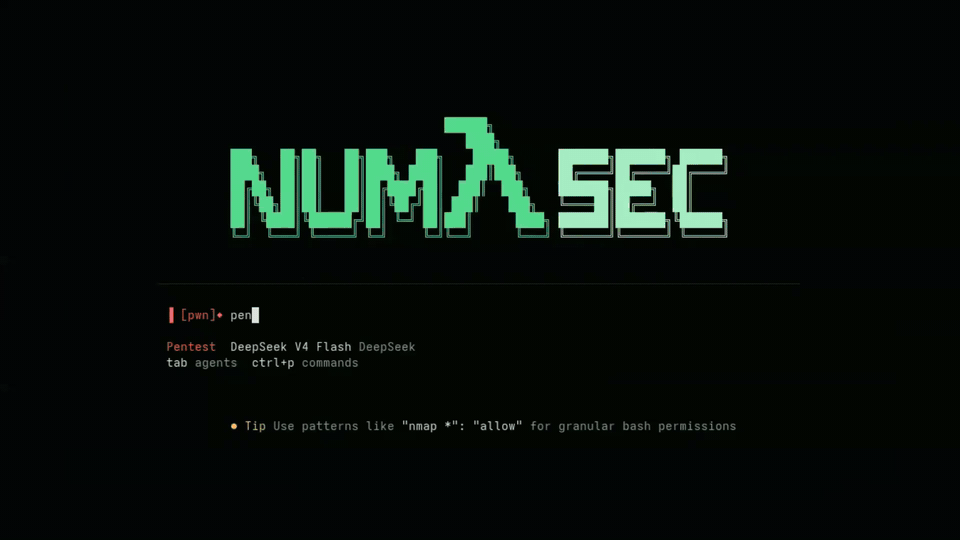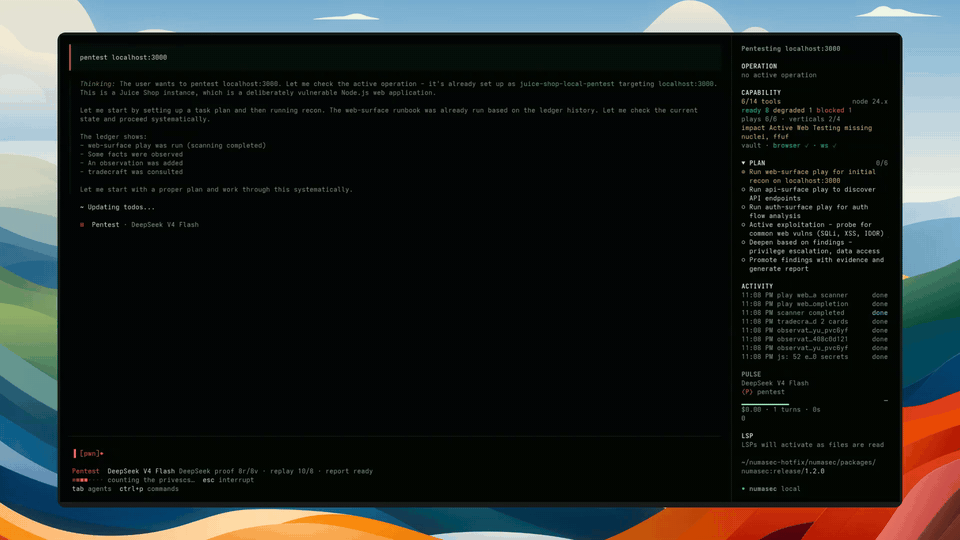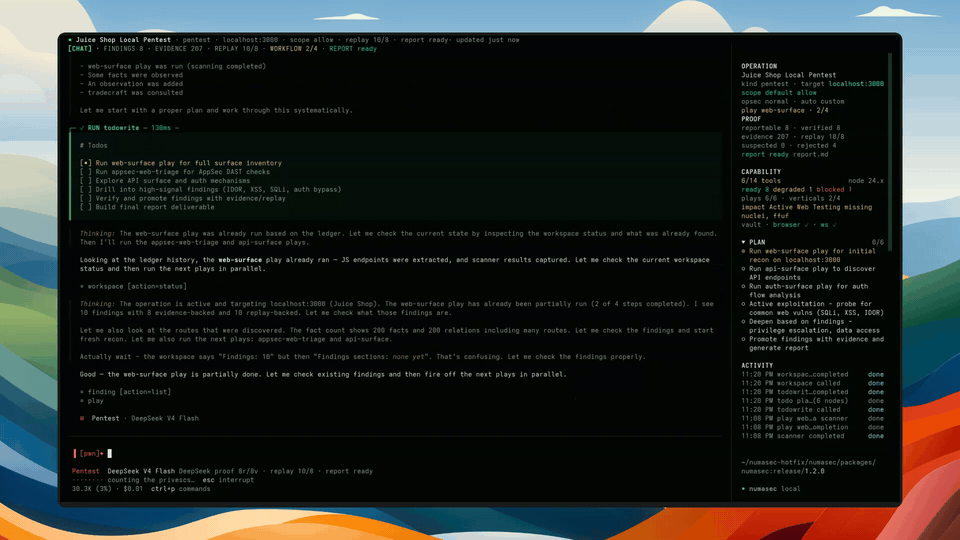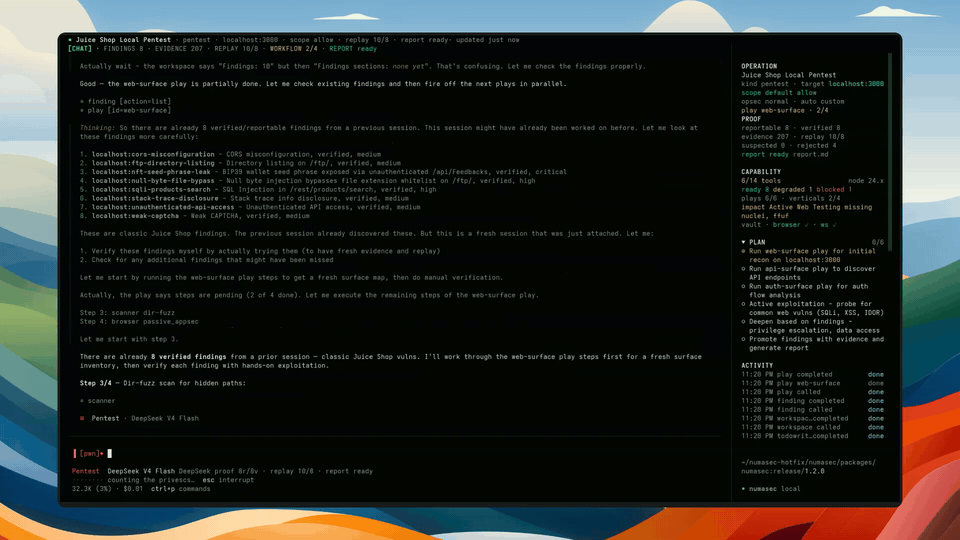
Findings are not dumped into chat: they live in the operation, where each one can carry state, se, e, replay status and next action, so the agent can keep working without losing the thread.
Weak signals can stay weak. Rejected claims remain . Reportable findings need proof.
<p align="center">
<img src="assets/switchagents.gif" alt="switching between numasec cyber specialist agents" width="760" />
</p>
Security work changes shape. AppSec, Pentest, OSINT, CTF/lab and research do not need the same posture, so you can switch the agent when the work changes instead of forcing one generic assistant to behave the same way e.
<p align="center">
<img src="assets/operations.png" alt="numasec operation selector with rename support" width="760" />
</p>
Operations are durable. Name them, rename them, resume them and export them. A security workflow should not disappear because the chat ended.
Try it
Then start with a local lab, CTF, owned app or authorized target:
Run numasec from the workspace you are testing and keep the target scope explicit.
What it does
| Capability | What it gives you |
| --- | --- |
| AI security agent | A model that works inside your terminal instead of sitting in a separate chat window. |
| Local tools | numasec uses the tools installed on your machine and shows what is a, missing or degraded. |
| Runbooks | Security workflows that keep the agent moving through a real task instead of random tool calls. |
| Agents | Switch posture with TAB for AppSec, Pentest, OSINT, CTF/lab and research-style work. |
| Operation memory | Keep target, scope, activity, findings, e, replay and report state together. |
| Findings workflow | Track security signals as they move from weak ideas to useful findings. |
| E and replay | Keep the material needed to understand, and reproduce important work. |
| Cyber knowledge | Bring intelligence, ad, methodology and tool docs into the workflow. |
| Reports | Generate deli from the operation instead of reconstructing e at the end. |
| Share bundles | Export the work so it can be re, resumed or handed off. |
Built for
numasec is for people who want an AI agent inside their security workflow, not beside it.
numasec is for authorized security work. Use it only on systems you own, labs, CTFs, or targets where you ha to test.
How the workflow fits together
numasec is not just a prompt with tools.
It keeps the security workflow connected: target, operation, posture, runbook, local tools, obser, findings, e, replay and report.
The important part: the operation does not live only in chat. numasec keeps a durable record of the work so the agent can continue, the operator can review, and the report can come from what actually happened.
How numasec is different
Most AI security tools fall into one of two traps: they only talk, or they only wrap tools. numasec tries to do something different: keep the workflow ali the agent works.
| Compared with | What usually happens | What numasec does |
| --- | --- | --- |
| Generic AI chats | Good advice, but detached from the actual work. | Runs inside the terminal workflow with tools, memory and operation state. |
| Generic coding agents | Great for repos and tests, but not shaped around security work. | Adds security agents, runbooks, scope, findings, e, replay and reports. |
| Scanner wrappers | Fast output, weak context. | Turns tool output into part of a larger operation. |
| Manual notes | Flexible, but e drifts apart. | Keeps findings, e, replay and reports connected. |
| Tool servers | Expose capabilities, but lea and memory to the user. | Adds the security workflow around the tools. |
Commands
numasec is designed to stay fast from the keyboard: start an operation, switch agents, run workflows, inspect tools, tighten opsec, export the work and come back later.
Install
npm
Bun
Docker
From source
Tool surface
numasec does not try to replace your tools.
It gives the agent a controlled way to use and reason around the en you already ha, files, browser, HTTP, scanners, e, reports, knowledge and workspace state.
The agent sees a small set of useful security surfaces:
bash, read, write, edit, apply_patch, grep, globhttp_request, browser, scanner, appsec_proberunbook, pwn_bootstrap, scope, opsec, autonomy, identitye, obser, finding, report, share, remediateknowledge, methodology, cvedoctor, workspace, vault, net, crypto, analyzeknowledge is the preferred cyber research surface. It routes intelligence, package ad, methodology, tradecraft, exploit signals and installed tool docs through one pro broker.
For obser like nginx 1.18.0, OpenSSH_8.2p1 or npm:react@18.2.0, it separates possibility from applicability, enriches with KEV/EPSS where a, and suggests safe next actions without turning intelligence into a finding.
cve remains as a compatibility alias for C lookup. New cyber research should use knowledge.
Local tools make numasec stronger. If these are installed, the agent can use or reason around them:
Use /doctor to see what is a, degraded, or missing on the current machine.
Models and pro
Bring the model you trust. numasec is model-agnostic and wraps the model you choose with a security workflow: terminal, tools, agents, runbooks, operation memory, findings, e and reports.
Supported provider families include OpenAI, Anthropic, Google, xAI, Bedrock, OpenRouter, Ollama, AI Gateway, OpenAI-compatible endpoints, and other pro supported through the local model stack.
The bet is not that one model magically sol. The bet is that good models become much more useful when they work inside the right security en.
Architecture
numasec wraps the model with a security workflow. The model can reason and act; numasec keeps the operation around it: tools, runbooks, events, facts, e, replay, findings and deli.
Operation memory
An operation is stored as events, facts, relations, e, replay artifacts, workflow state and deli.
numasec.md can exist as a deri pack. It helps orient the model, but it is not the source of truth.
Finding lifecycle
Security work has messy intermediate states. Something can look interesting without being true. Something can be obser being ready for a report. Something can be and later become stale.
numasec keeps those states instead of flattening e into chat output.
The model is allowed to explore. The workflow is not allowed to pretend every idea is a finding.
Runbooks instead of random tool spam
Security agents get noisy when they can call tools without a workflow. numasec uses runbooks to keep the agent moving through a recognizable task shape: surface mapping, AppSec triage, scoped pentest work and future domain-specific workflows.
Strongest today:
appsec-web-triageweb-surfacepwn / Pentest starter flowMaturity-labeled surfaces:
Built to avoid AI security slop
numasec is built around a simple rule: the agent can help you mo, but the workflow should not let it o.
That is why numasec tracks scope, operation state, findings, e, replay and report output.
Mature focus:
Other cyber surfaces exist or are planned, but they are not marketed as equally mature yet.
numasec does not claim to replace authorization, operator judgment, manual review or specialized tools.
That honesty is not marketing modesty. It is part of the product. Security tools lose trust when they confuse confidence with proof.
Roadmap
The long-term is simple:
an open source AI security agent that can grow with the community.
Short term, numasec is staying focused:
Longer term:
The rule stays the same: every mature domain needs real workflow support, not just a prompt.
Documentation
De
AppSec and Pentest benchmarks are local/manual release-confidence tools:
Do not run package tests from the repo root. numasec uses Bun-first package-local workflows.
Contributing
The most contributions make numasec a better operator:
If a change creates a confirmed security claim, it needs e. If a finding is reportable, it needs replay or a structured exemption.
Community
The best feedback is not "cool project".
The best feedback is:
Use GitHub issues and discussions for bugs, workflow feedback, runbook ideas, adapters and release questions.
Please keep examples authorized, lab-based or safely anonymized.
Help shape numasec
numasec is early, but the direction is clear:
make security work feel faster, sharper and less scattered with an AI agent that lives in the terminal.
If that feels useful, star the repo, try it on an authorized workflow and tell me where it breaks.
License
GNU Affero General Public License v3.0 or later. Use numasec for authorized security work, research, education, and defensi.
<p align="center">
Built by <a href=" Stabile</a>
| <a href="
<br/><sub>If numasec helps you, <a href=" a star</a> and share the workflow.</sub>
</p>
项目信息
开发语言:TypeScript
Star 数:803
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The AI Agent for Cyber Security.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | numasec - The AI Agent for Cyber Security. |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:35:26 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 168 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |