 安全软件
点击放大
cve-lite-cli - Fast, developer-friendly JS/TS dependency vulnerab
项目说明
*Most tools tell you what's wrong. CVE Lite CLI tells you what to run.*
![OWASP Lab Project]()
![npm ]()
![npm downloads]()
![npm total downloads]()
![CI]()
![GitHub Marketplace]()
![License]()
![Protected by CVE Lite CLI]()
![OpenSSF Best Practices]()
<di="center">
<a href="
<img src=" alt="CVE Lite CLI — An OWASP Foundation Project" width="500"/>
</a>
<h1>CVE Lite CLI</h1>
🏆 Officially recognized as an OWASP Lab Project
<p> scanning that starts in your terminal and fits cleanly into CI.<br/>Scan your lockfile, get copy-and-run fix commands, and ship clean code.</p>
<strong>Scan. Understand. Fix.</strong>
<br/>
<table>
<tr>
<td align="center" width="33%">🏆</td>
<td align="center" width="33%">🎯</td>
<td align="center" width="33%">🔒</td>
</tr>
<tr>
<td align="center" width="33%" ="top"><strong>OWASP Lab Project</strong><br/><sub>Peer-re by the org behind the OWASP Top 10 —<br/>the security standard followed by millions of de</sub></td>
<td align="center" width="33%" ="top"><strong>Remediation-first</strong><br/><sub> fix commands + parent-aware<br/>transiti — not just CVE IDs</sub></td>
<td align="center" width="33%" ="top"><strong>Runs locally</strong><br/><sub>Nothing leaves your machine — not your<br/>code, not your dependency tree</sub></td>
</tr>
</table>
<br/>
<p>
🏆 <strong>Featured on <a href=" Open Source Friday</a></strong> ·
<strong>Ranked #5</strong> in <a href=" Net Security's 20 open-source security tools</a> ·
<strong><a href=" Best Practices</a></strong>
</p>
<p>
Covered by
<a href=" Register</strong></a> ·
<a href=" Online</strong></a> ·
<a href=" ·
<a href=" Times</strong></a> ·
<a href=" ·
<a href="
</p>
<p>
<sub>Running in CI at
<a href="
<a href=" Go of British Columbia</strong></a> as a required merge gate,
<a href=" go digital services (<strong>DINUM</strong>)</a>, and
<a href="
In production use in France, Canada, Germany, Thailand and China.</sub>
</p>
<br/>
<p>
⚡ <strong>One command. No account, no API key, nothing leaves your machine.</strong>
<code>npx c .</code>
<a href="#quick-start"><strong>→ Quick Start</strong></a>
</p>
<br/>
<p>
<a href="#quick-start">Quick Start</a> •
<a href="#usage">Usage</a> •
<a href="#what-it-looks-like">Screenshots</a> •
<a href=" Report</a> •
<a href=" •
<a href=" •
<a href=" •
<a href=" Slack</a>
</p>
</div>
---
<di="center">
Package Managers
<table border="0" cellspacing="0" cellpadding="12">
<tr>
<td align="center"><img src=" width="48" height="48" alt="npm"/><br/><sub><b>npm</b></sub></td>
<td align="center"><img src=" width="48" height="48" alt="pnpm"/><br/><sub><b>pnpm</b></sub></td>
<td align="center"><img src=" width="48" height="48" alt="Yarn"/><br/><sub><b>Yarn</b></sub></td>
<td align="center"><img src=" width="48" height="48" alt="Bun"/><br/><sub><b>Bun</b></sub></td>
</tr>
</table>
</div>
---
Quick start
Or one-off with npx:
No account. No configuration. No source code leaves your machine.
> Note: CVE Lite CLI includes better-sqlite3, a nati binding used for the local ad database. During installation, npm may download a prebuilt binary or compile one from source. This can produce extra console output — it is expected and is not CVE Lite CLI itself running an install script. See Dependency footprint for details.
Usage
For the full flag reference and exit codes see the CLI Reference guide and Fix mode guide.
O hygiene (o)
o and resolutions are powerful, but they rot. CVE Lite CLI audits them across npm, pnpm, yarn, and bun, catching thirteen classes of problem:
| Rule | What it catches |
|---|---|
| OA001 | Orphaned target: o for a package no longer in the tree |
| OA002 | Floating tag: o pinned to a moving tag (latest, next) |
| OA003 | Wrong section: o placed in the wrong container |
| OA004 | Surpassed pin: the rest of the tree has moved past the pin |
| OA005 | Nested ineffecti that ne |
| OA006 | Coupled platform binary: o fights a parent's exact pin |
| OA007 | Frozen latest: registry has drifted past the pinned (needs --check-network) |
| OA008 | Materialized copy still on disk despite the o |
| OA009 | Stale floor: o range floor already met by all parent declarations |
| OA010 | floor: o range admits a known- (needs --check-network) |
| OA011 | Exceeds declared range: o floor can resolve into a major no parent permits |
| PD001 | O phantom: package imported in source but only present via an o pin |
| PD002 | Transiti phantom: package imported in source but only present as a transiti |
Use the o subcommand for a hygiene-only run (no CVE scan, faster, fully offline-capable) with auto-fix support. Use --check-o to append hygiene results to a regular CVE scan in one pass.
For the full guide with per-rule examples and CI patterns, see the O Hygiene Auditing guide.
Maintenance risk (--check-maintenance)
A C tells you a transiti is . It does not tell you *why you can't fix it* - often a direct dependency of yours pins it below the fix, and clearing it needs a breaking major upgrade the scanner ne. The DM001 rule surfaces exactly that, plus direct dependencies npm has marked deprecated.
| Signal | Se | What it means |
|---|---|---|
| Constraint drag | high | A direct dependency blocks a transitive CVE fix behind a major- upgrade |
| Deprecated on npm | medium | A direct dependency is deprecated - no fix is coming through a normal update |
Packages that have not published in years get a Last release context line; release age is informational, not a se signal on its own.
For the full guide, see the Maintenance Risk Detection guide.
Release cooldown awareness
Package managers added a release cooldown to skip the danger window right after a is published, when a hijacked release is live but not yet caught (the chalk/debug compromise sat live for about two hours). CVE Lite CLI reads the cooldown your project already configures and warns when a recommended fix is newer than that window, so it ne pushes you onto a your own package manager would refuse to install.
The warning is ad and on by default (no flag, no exit-code change). It reads min-release-age (npm), minimumReleaseAge (pnpm), or npmMinimalAgeGate (Yarn); it ne a window.
For the full guide, see the Release Cooldown Awareness guide.
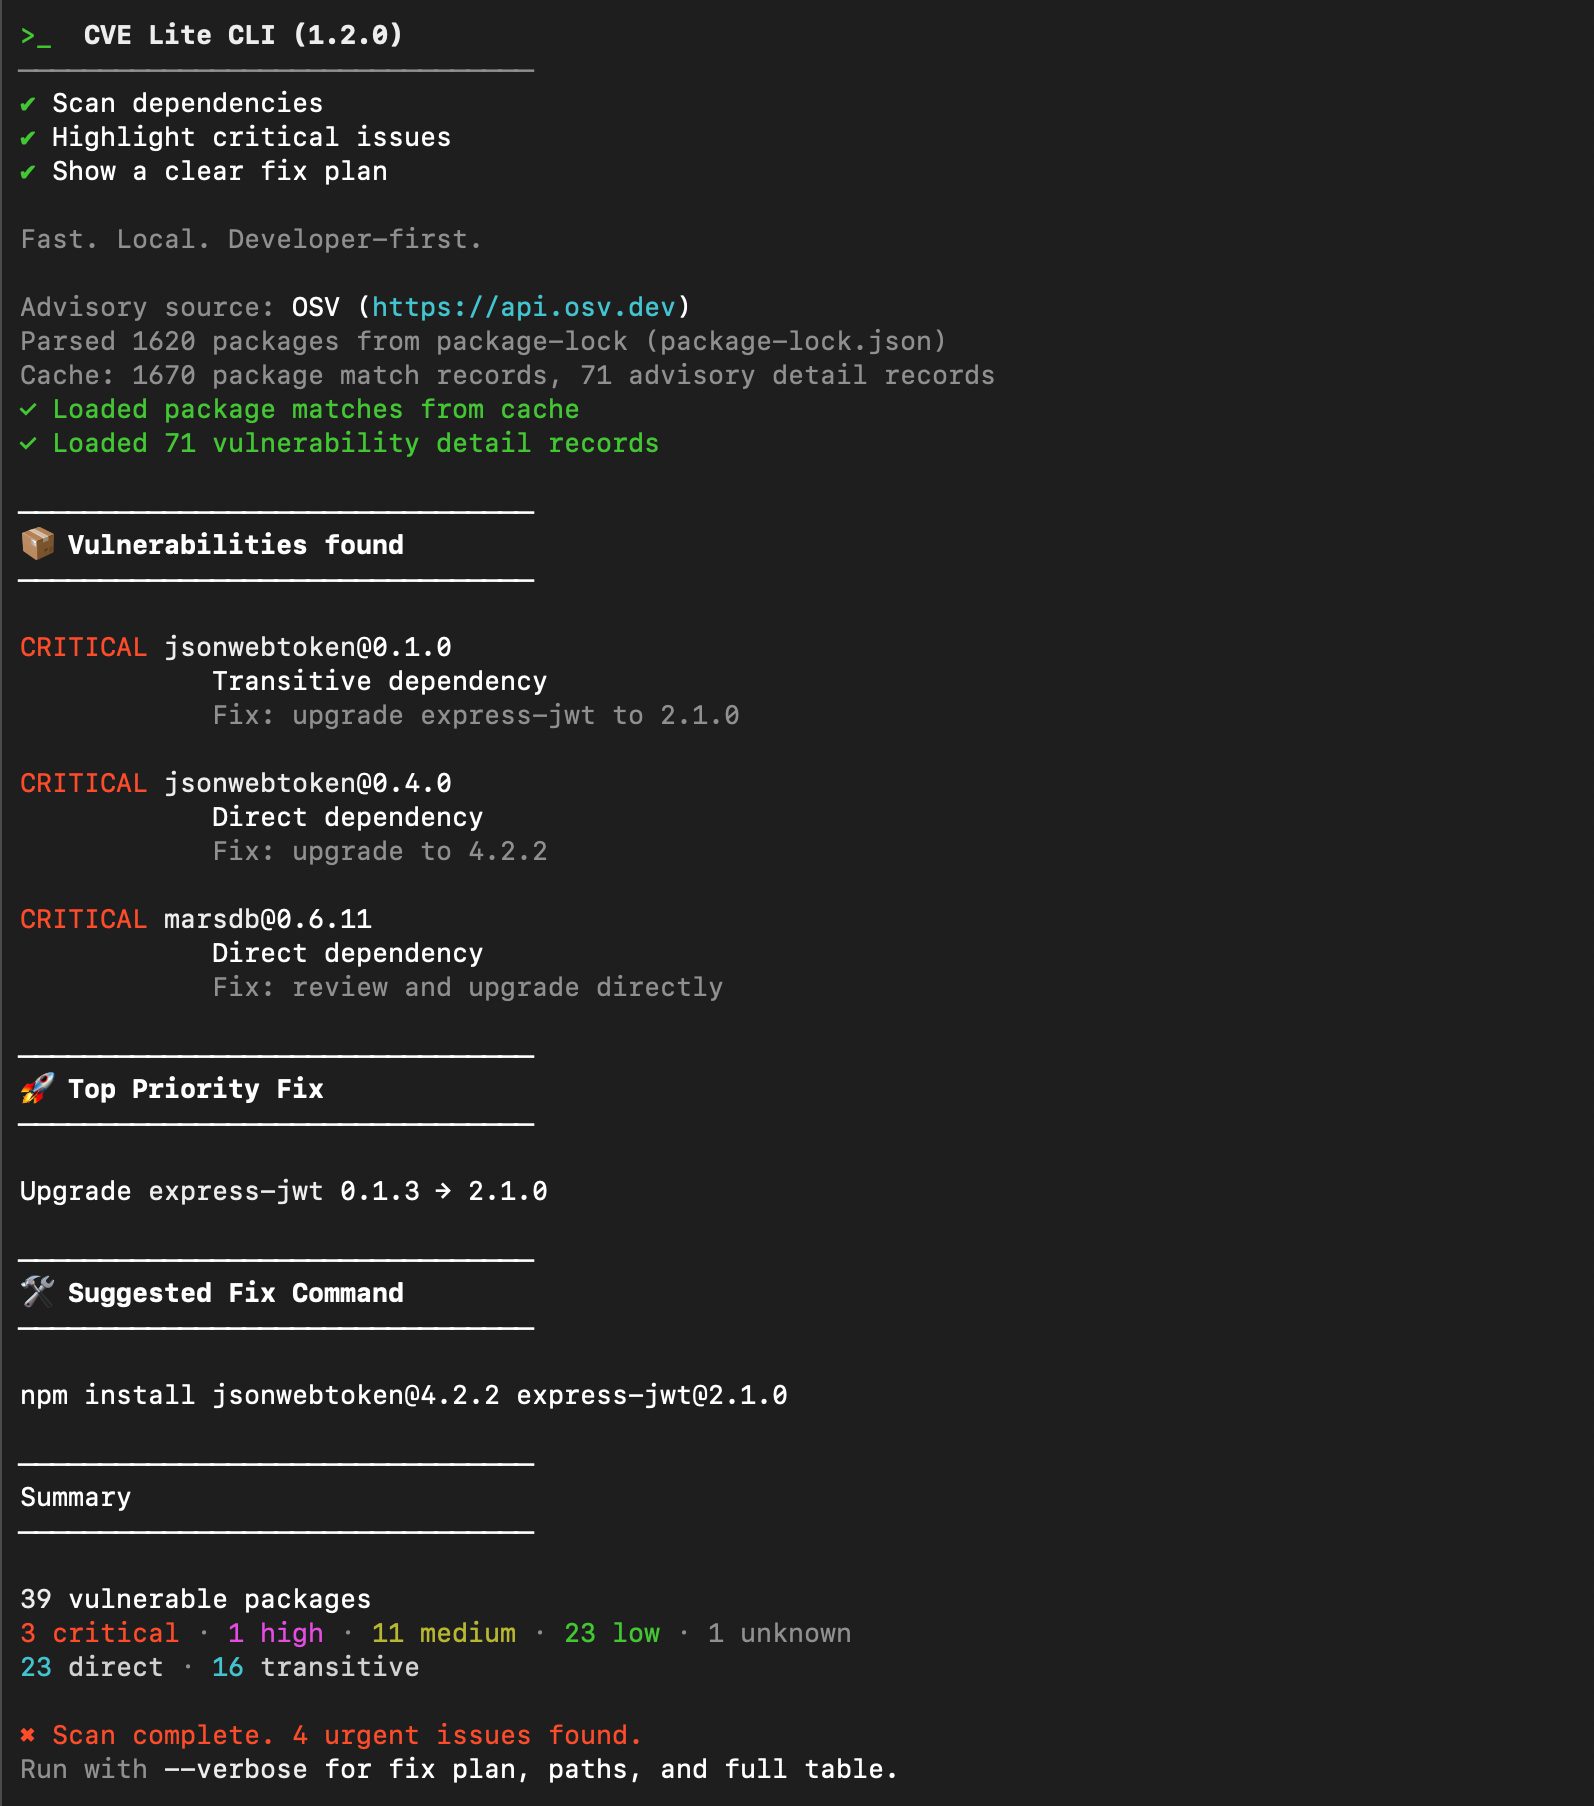
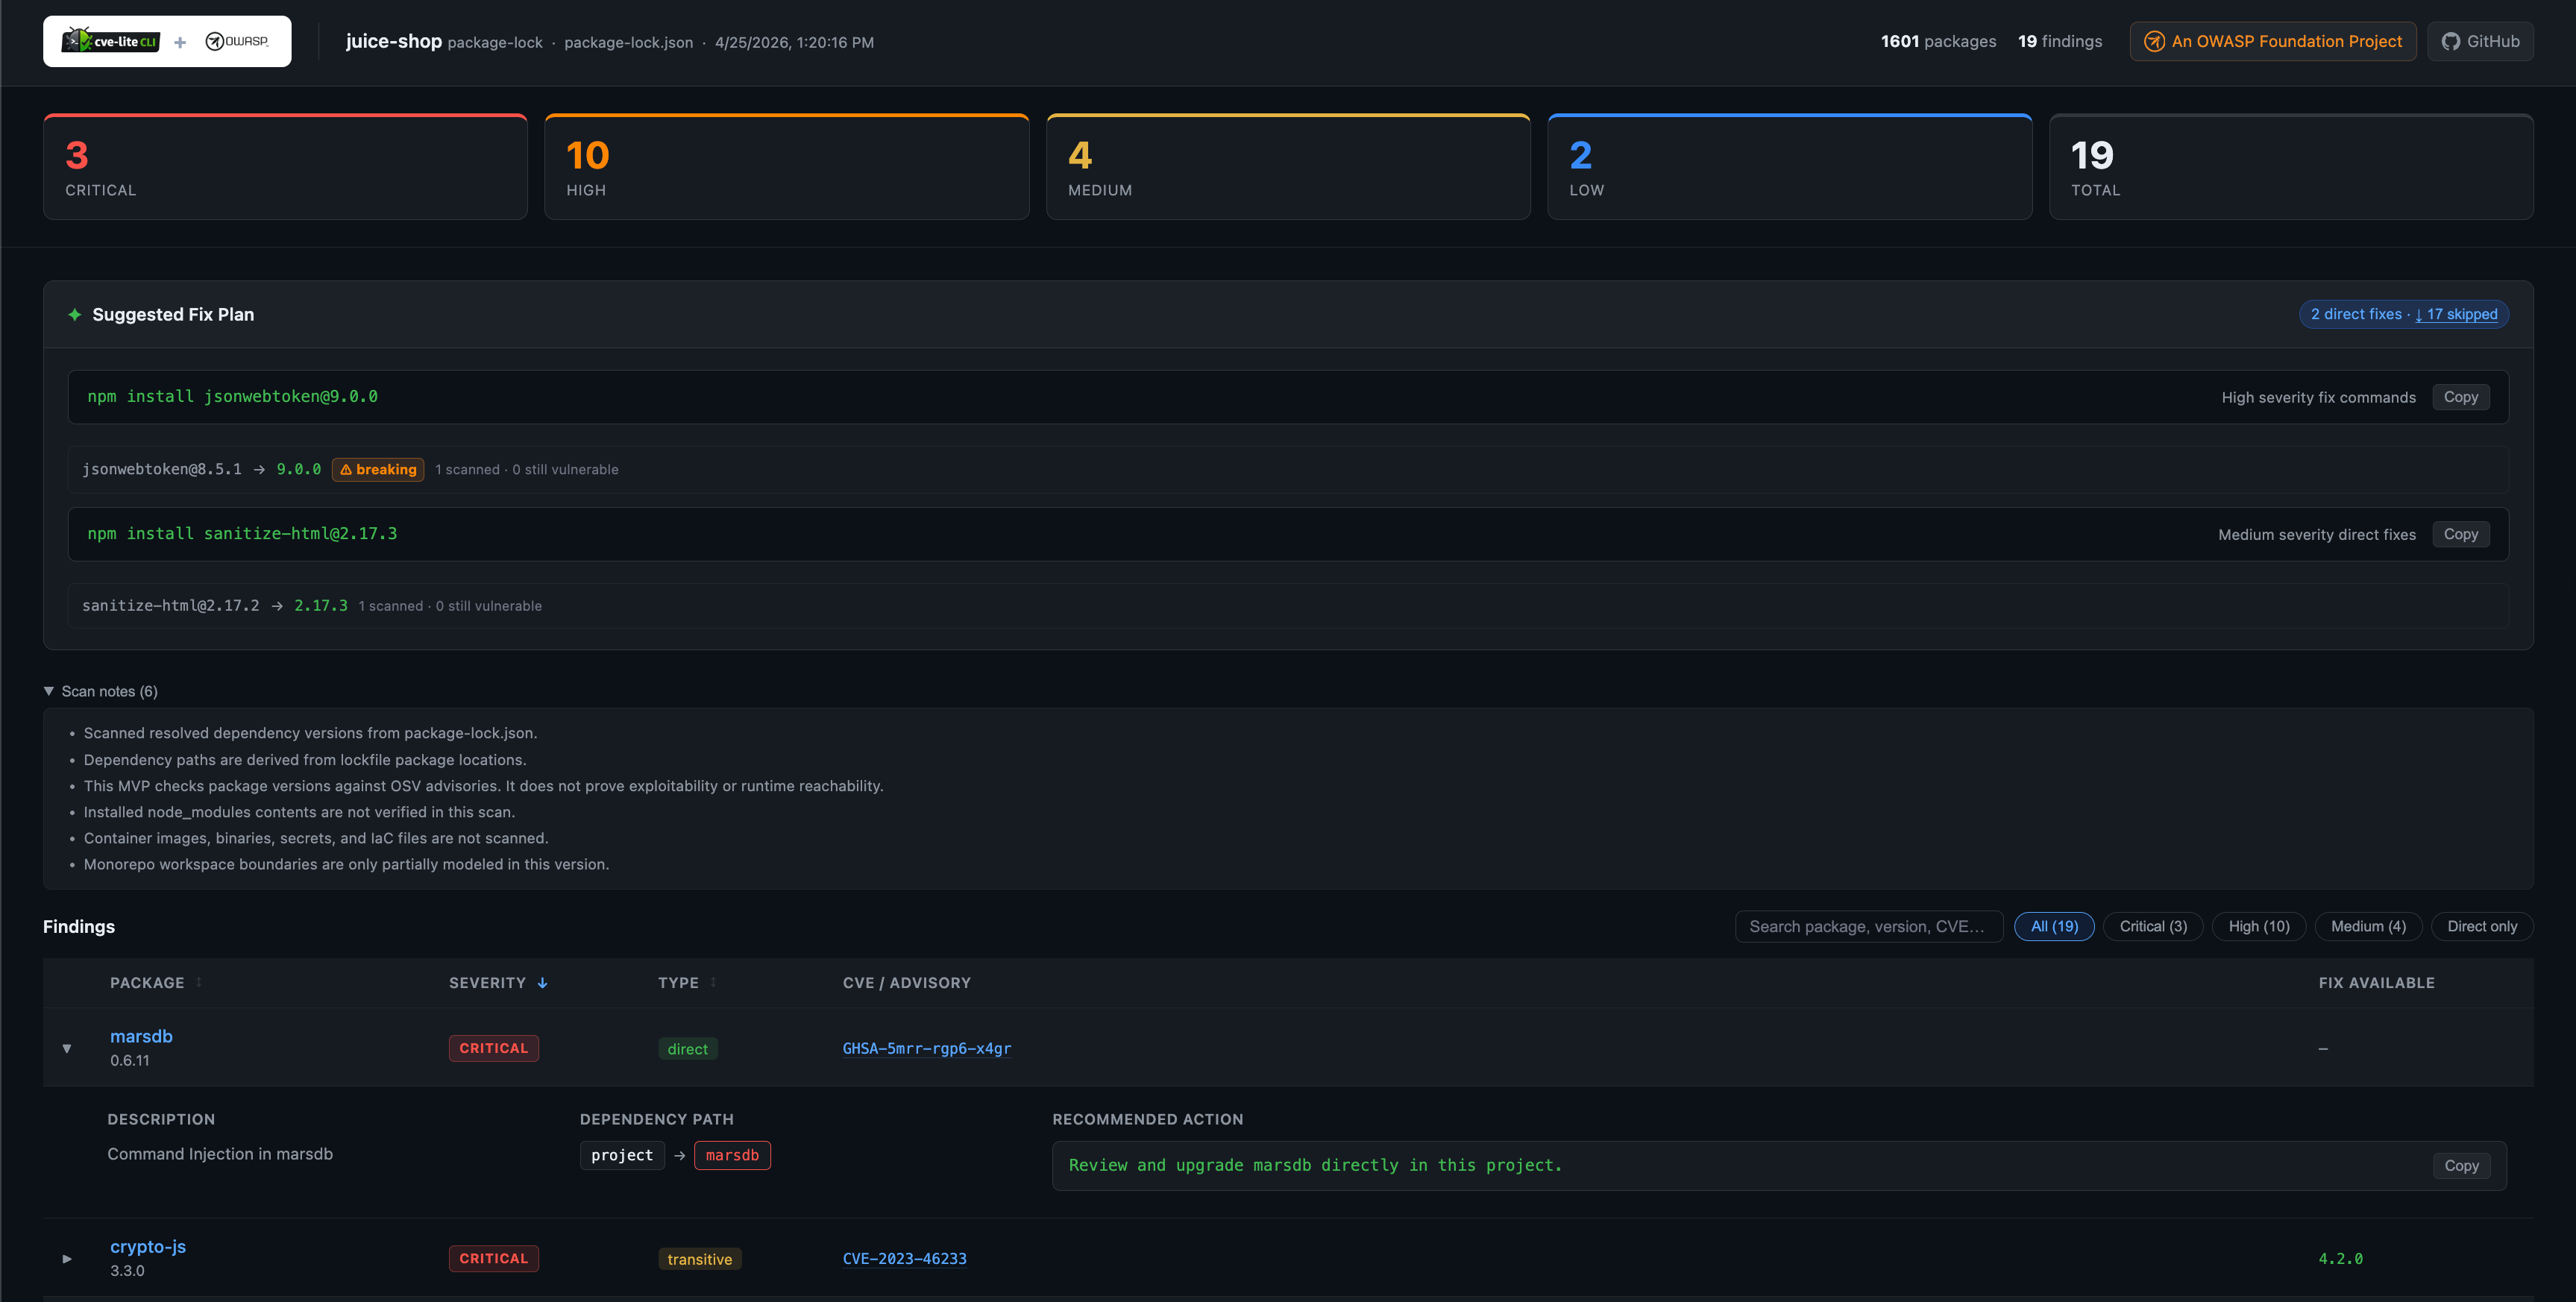
What it looks like
<table>
<tr>
<th align="center">Terminal output</th>
<th align="center">HTML dashboard (<code>--report</code>)</th>
</tr>
<tr>
<td align="center">
<a href="
<img src=" alt="CVE Lite CLI terminal output" width="440"/>
</a>
</td>
<td align="center">
<a href="
<img src=" alt="CVE Lite CLI HTML dashboard" width="440"/>
</a>
</td>
</tr>
<tr>
<td align="center"><sub>Default scan output · <a href=" guide</a></sub></td>
<td align="center"><sub>Generated with <code>--report</code> · <a href=" report guide</a></sub></td>
</tr>
</table>
<details>
<summary> terminal output — includes the full fix plan</summary>
<p align="center">
<a href=" src=" alt=" output part 1" width="280"/></a>
<a href=" src=" alt=" output part 2" width="280"/></a>
<a href=" src=" alt=" output part 3" width="280"/></a>
</p>
</details>
Why CVE Lite CLI
Most security tooling is built around pipelines, not de. Dependabot opens PRs you'll get to e. CI scanners block merges after the fact. Dashboards surface lists of CVE IDs with no clear path to fixing them. De learn to ignore it.
CVE Lite CLI is built for the moment before you push. It reads your lockfile locally, queries OSV and the npm registry ad API, and produces copy-and-run npm install, pnpm add, yarn add, or bun add commands — not a list of identifiers. You see which packages are direct transitive, get parent-aware upgrade guidance, and can scan offline in restricted en.
The closer a security tool is to a de's natural workflow, the more likely it is to be used.
How it compares
No other free tool combines all of the following: lockfile scanning across npm, pnpm, Yarn, and Bun; parent-aware transiti that tells you which package to upgrade (not just which one is ); fix before suggesting an upgrade; a fully offline ad DB for restricted en; CVE + license compliance scanning in a single pass; SBOM output in both CycloneDX and SPDX with the findings attached rather than as a separate in step; and an EPSS priority signal that combines C with exploitation likelihood into four actionable tiers.
| Capability | CVE Lite CLI | npm audit | OS | Snyk CLI | Socket CLI |
|---|:---:|:---:|:---:|:---:|:---:|
| JS/TS lockfile scanning | ✅ | ✅ | ✅ | ✅ | ✅ |
| npm + pnpm + Yarn + Bun support | ✅ | ❌ | ✅ | ✅ | ✅ |
| No account required | ✅ | ✅ | ✅ | ❌ | ❌ |
| Free to use | ✅ | ✅ | ✅ | ❌ | ❌ |
| Usage-aware reachability scanning | ✅ | ❌ | ❌ | ✅ | ⚠️ |
| Direct | ✅ | ⚠️ | ✅ | ✅ | ✅ |
| Dev dependency labelling | ✅ | ⚠️ | ❌ | ⚠️ | ❌ |
| Copy-and-run fix commands | ✅ | ❌ | ❌ | ✅ | ⚠️ |
| Transiti update guidance | ✅ | ❌ | ⚠️ | ⚠️ | ⚠️ |
| Suggested remediation plan | ✅ | ❌ | ⚠️ | ✅ | ⚠️ |
| Ratcheting mode (baseline suppression) | ✅ | ❌ | ❌ | ⚠️ | ❌ |
| Interactive HTML report | ✅ | ❌ | ❌ | ✅ | ❌ |
| SARIF / GitHub Code Scanning output | ✅ | ❌ | ✅ | ✅ | ❌ |
| JSON output | ✅ | ✅ | ✅ | ✅ | ✅ |
| SBOM output with findings attached (CycloneDX + SPDX) | ✅ | ❌ | ❌ | ⚠️ | ⚠️ |
| Offline/local ad DB | ✅ | ❌ | ⚠️ | ❌ | ❌ |
| O hygiene auditing | ✅ | ❌ | ❌ | ❌ | ❌ |
| Maintenance-risk detection (C drag) | ✅ | ❌ | ❌ | ❌ | ❌ |
| License compliance scanning (copyleft / unknown) | ✅ | ❌ | ❌ | ⚠️ | ⚠️ |
| Priority signal: C × EPSS exploitation likelihood | ✅ | ❌ | ❌ | ⚠️ | ❌ |
<sub>✅ = built-in strength · ⚠️ = partial or workflow-dependent · ❌ = not a core strength</sub>
The transiti guidance is a key difference: CVE Lite CLI avoids recommending direct installs for packages that are only present transitively. For npm lockfiles, it can identify when npm update <parent> is enough to re-resolve a known non- child within the current parent range, and when the parent package itself needs an upgrade.
For detailed per-tool analysis, see Comparison with other tools.
Replace Dependabot with one batched PR
CVE Lite CLI v1.26.0 ships a GitHub Action fix mode that runs on a schedule and opens a single batched pull request with all dependency upgrades - ad IDs, before/after finding counts, and OS fix included.
Add this file to your repo:
| | Dependabot | CVE Lite fix mode |
|---|---|---|
| PRs per run | One per package | One batched PR |
| Ad IDs in PR body | No | Yes (GHSA-xxxx, C) |
| Fix against OSV | No | Yes |
| Before/after finding counts | No | Yes |
| pnpm / Yarn Berry / Bun | Limited | Full nati |
| OWASP recognition | No | OWASP Lab Project |
Full Action documentation -> - for scan-only CI gating see the CI and Workflow Integration guide.
Real-world
CVE Lite CLI has been e against real open-source projects to that it surfaces meaningful issues - including non-obvious transiti and complex upgrade paths - not just low-signal ad matches.
yarn audit deduplication20+ case studies across npm, pnpm, Yarn, and Bun projects ->
In-repo lockfile fixtures for most projects li examples/ - clone and scan immediately without downloading full upstream checkouts.
These are not demos. They are documented scans against real codebases with real findings, recorded before and after applying fix commands.
If you maintain an open-source Ja or TypeScript project and want CVE Lite CLI e on it, open an issue and share the repository.
Press
Full press co ->
Recognized by OWASP
OWASP (Open Web Application Security Project) is the globally recognized nonprofit behind the security standards followed by millions of de worldwide - most notably the OWASP Top 10, the most widely cited web application security reference in the industry. Organizations from startups to Fortune 500 companies use OWASP guidelines as the foundation of their security programs.
CVE Lite CLI is an OWASP Lab Project - re and accepted by the OWASP community as a , open source security tool.
Where it fits in the OWASP ecosystem:
CVE Lite CLI fills a specific gap - fast, local-first JS/TS dependency scanning close to release time - that broader OWASP tools are not optimized for:
| Tool | Focus |
|---|---|
| CVE Lite CLI | Lockfile-first, local de CLI, remediation-focused, JS/TS |
| OWASP Dependency-Check | Multi-language, SAST-style, broader ecosystem |
| OWASP dep-scan | Multi-language and en, SBOM and cloud-native |
| OWASP Dependency-Track | Platform and SBOM management, not a local CLI |
CVE Lite CLI complements these tools. It is not a replacement for continuous monitoring or full SBOM management - it is the fast local check you run before pushing.
Community and adoption
CVE Lite CLI is used in production across organizations and independent de in multiple countries. Confirmed users span go digital services, enterprise engineering platforms, open-source libraries, and security education.
Notable adopters include:
Current limitations
Dependency footprint
Runtime: yaml · yarn-lockfile · better-sqlite3 · fflate · semver
Dev only: /node · tsx · typescript
This is intentional. Because CVE Lite CLI is a security-oriented tool, runtime dependencies are kept minimal and re.
Nati: better-sqlite3
better-sqlite3 is a native Node.js addon that provides the SQLite binding for CVE Lite CLI's local ad database. This database powers offline scanning (--offline, --offline-db), ad sync (c ad sync), and air-gapped workflows (c ad init).
Because it includes compiled C/C++ code, npm must run an install script when installing better-sqlite3. During installation:
prebuild-install downloads a prebuilt binary for your platform — fast, though npm may still print a deprecation warning for prebuild-install itself (#519).node-gyp, which requires a C/C++ toolchain and produces more console output.This install step belongs to better-sqlite3, not to CVE Lite CLI — the project itself does not define any preinstall, install, or postinstall hooks.
npm install-script permissions: Depending on your npm and configuration, npm may prompt you to approve the install script before it runs. This is an npm security feature. Online scanning works even when the install script is blocked — the nati is loaded lazily and only used by --offline, --offline-db, c ad sync, and c ad init. If you use any of those features, the better-sqlite3 install script must be allowed to complete.
npx behavior: When using npx c, a quiet run does not necessarily mean the install script was skipped. If npm's cache already contains the required prebuilt binary, installation is silent. On a cold cache, the same nati step runs.
More documentation
--fix skipping findings, CI failurespackage.json fallback, monorepos, private registriesSecurity and
Every release is signed - GPG-signed git tags for source, Sigstore Artifact Attestations for the release tarball, and ECDSA signatures via the npm registry. with:
For full details, fingerprints, and the project's threat model, see SECURITY.md and the Security Assurance Case.
For go details - roles, decision-making, and dispute resolution - see CONTRIBUTING.md.
Contributing
Feedback on output clarity, remediation guidance, ecosystem co, and CI usage is especially .
See CONTRIBUTING.md to get started.
Add a badge to your project
If you use CVE Lite CLI in your project, add this badge to your README:
![Protected by CVE Lite CLI]()
Community and support
For bug reports and feature requests: GitHub Issues
Helpful feedback includes reproducible bug reports, real-world lockfile edge cases, ideas for clearer output and remediation guidance, and CI or JSON workflow examples.
Using CVE Lite CLI at your company or in your projects? Share your use case in the community thread.
For security-related reporting: SECURITY.md
This project follows a Code of Conduct. Please review it before participating.
If CVE Lite CLI helps your release workflow, a GitHub star helps more de find it.
Contributors
Thanks to e who helps improve CVE Lite CLI - issues, pull requests, documentation, case studies, and real-world lockfile feedback all count.
<p align="center">
<a href="
<img src=" alt="Contributors to OWASP/c" />
</a>
</p>
<p align="center">
<sub>Avatar grid generated from the <a href=" contributors graph</a> via <a href="
</p>
New here? See CONTRIBUTING.md to get started, and review the Code of Conduct before participating.
Sponsors
Thank you to those who sponsor CVE Lite CLI and help keep it maintained:
---
Maintainer note: CVE Lite CLI is an OWASP Lab Project maintained by Sonu Kapoor. The goal is to build a tool the security and de community trusts and returns to - not a product that requires lock-in or a dashboard to be useful. If you find a real-world lockfile edge case, a remediation gap, or a workflow that doesn't fit, open an issue. Real-world feedback from real projects is the most input this project gets. See CONTRIBUTING.md for how to get in.
---
License
MIT - built in public and maintained as an OWASP Foundation Project by Sonu Kapoor.
项目信息
开发语言:TypeScript
Star 数:754
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix, JSON output, and practical remediation guidance.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | cve-lite-cli - Fast, developer-friendly JS/TS dependency vulnerab |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:35:39 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 291 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |