 安全软件
点击放大
DamnWebScanner - Another web vulnerabilities scanner, this extensio
项目说明
Damn Web Scanner
Another web scanner, this extension works on Chrome and Opera.
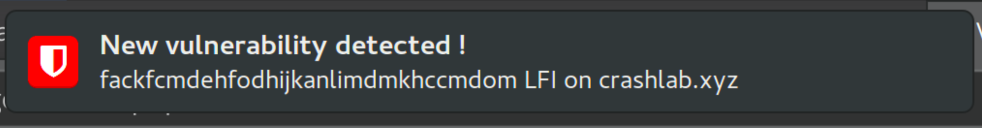
The extension is working on the background and will notify you if it finds any .
!Image of a noticiation
Currently it scans for:
All the features are:
Warning : Do not use this extension for illegal purpose, the main goal of it is to simplify the life of bug hunters. It's a BETA , many impro will come don't worry
Warning : A crash can happen ser, this issue isn't resolved yet. The docker-compose.yml is set to automatically restart the docker when this happen..
Install
You need to install and configure the server, it uses ghost and flask.
1. To get started you only need to start the docker and the dependencies will be installed.
2. Edit the ser
By default it's listening to the port 8000, it can be modified in the following files : popup.js, background.js, docker-compose.yml
3. The extension isn't packed, to use it go to chrome://extensions or opera://extensions then select "Load unpacked extension"
4. Browse the internet ! (Don't forget to start the extension by clicking the 'START' button)
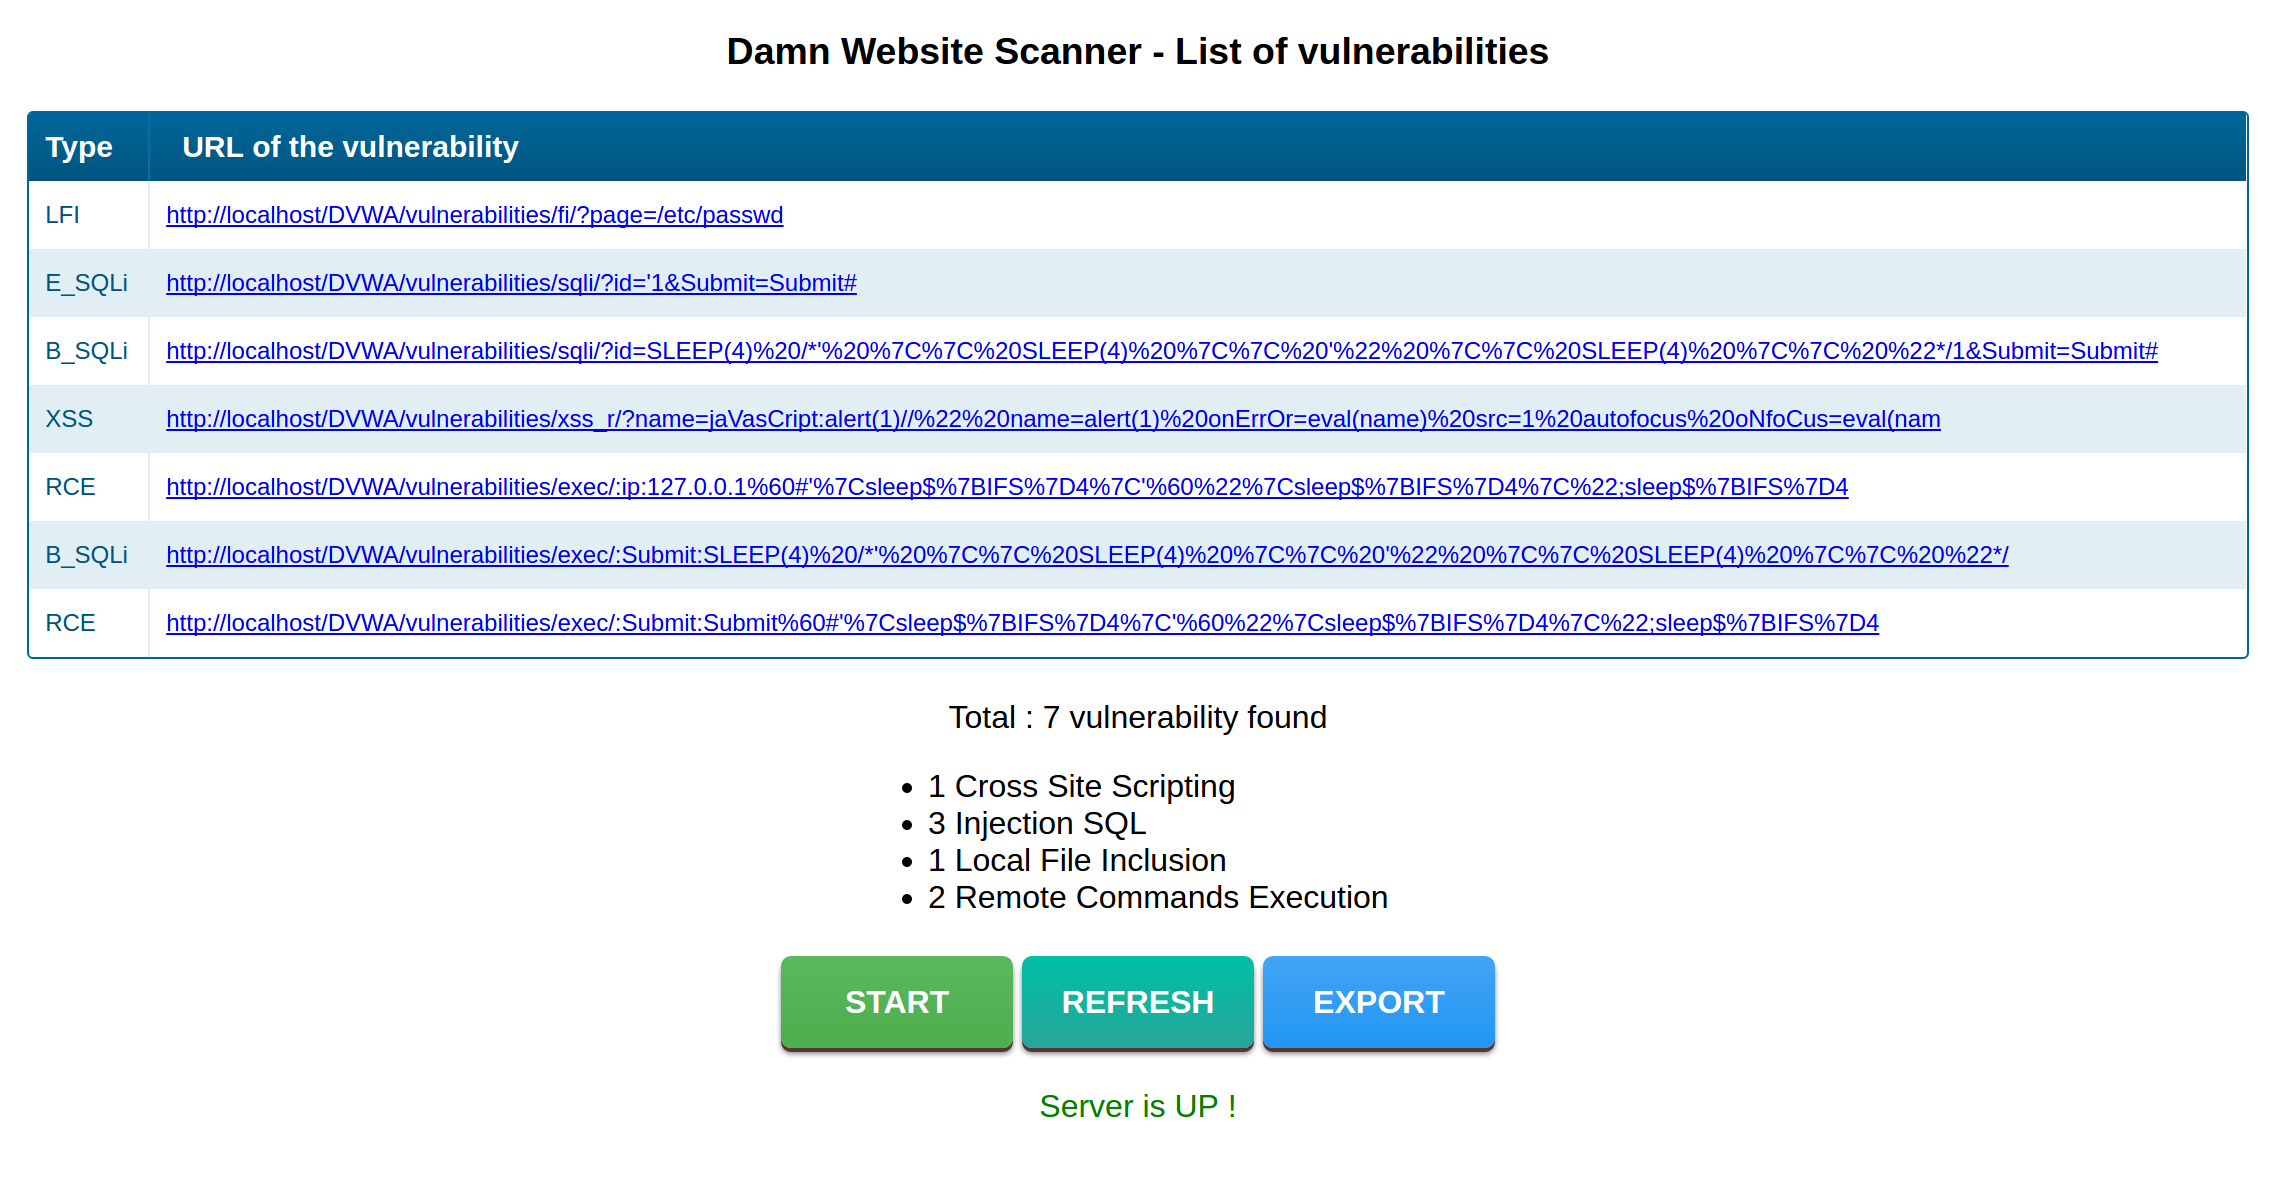
You can try the Error SQL, Blind SQL, LFI with Damn Web App.
The SQL Injection scanner was also tested on
!Image of D
Debugging
It's strongly recommended to debug any problem with Portainer using the logs table.
You will have an output like this :
A "/ping" request is done at every opening of the "Plugin Window" in your browser.
If you need the exact of the component used in the beta test, here they are.
Thanks, Contributors and Ideas
项目信息
开发语言:Python
Star 数:469
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Another web vulnerabilities scanner, this extension works on Chrome and Opera展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | DamnWebScanner - Another web vulnerabilities scanner, this extensio |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:36:31 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 368 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |