 安全软件
点击放大
ai-security-tool - 🛡️ Free open-source AI-powered security terminal &
项目说明
<article class="markdown-body entry-content container-lg" itemprop="text">
<h1>
<p align="center">
AI Security Tool<br>
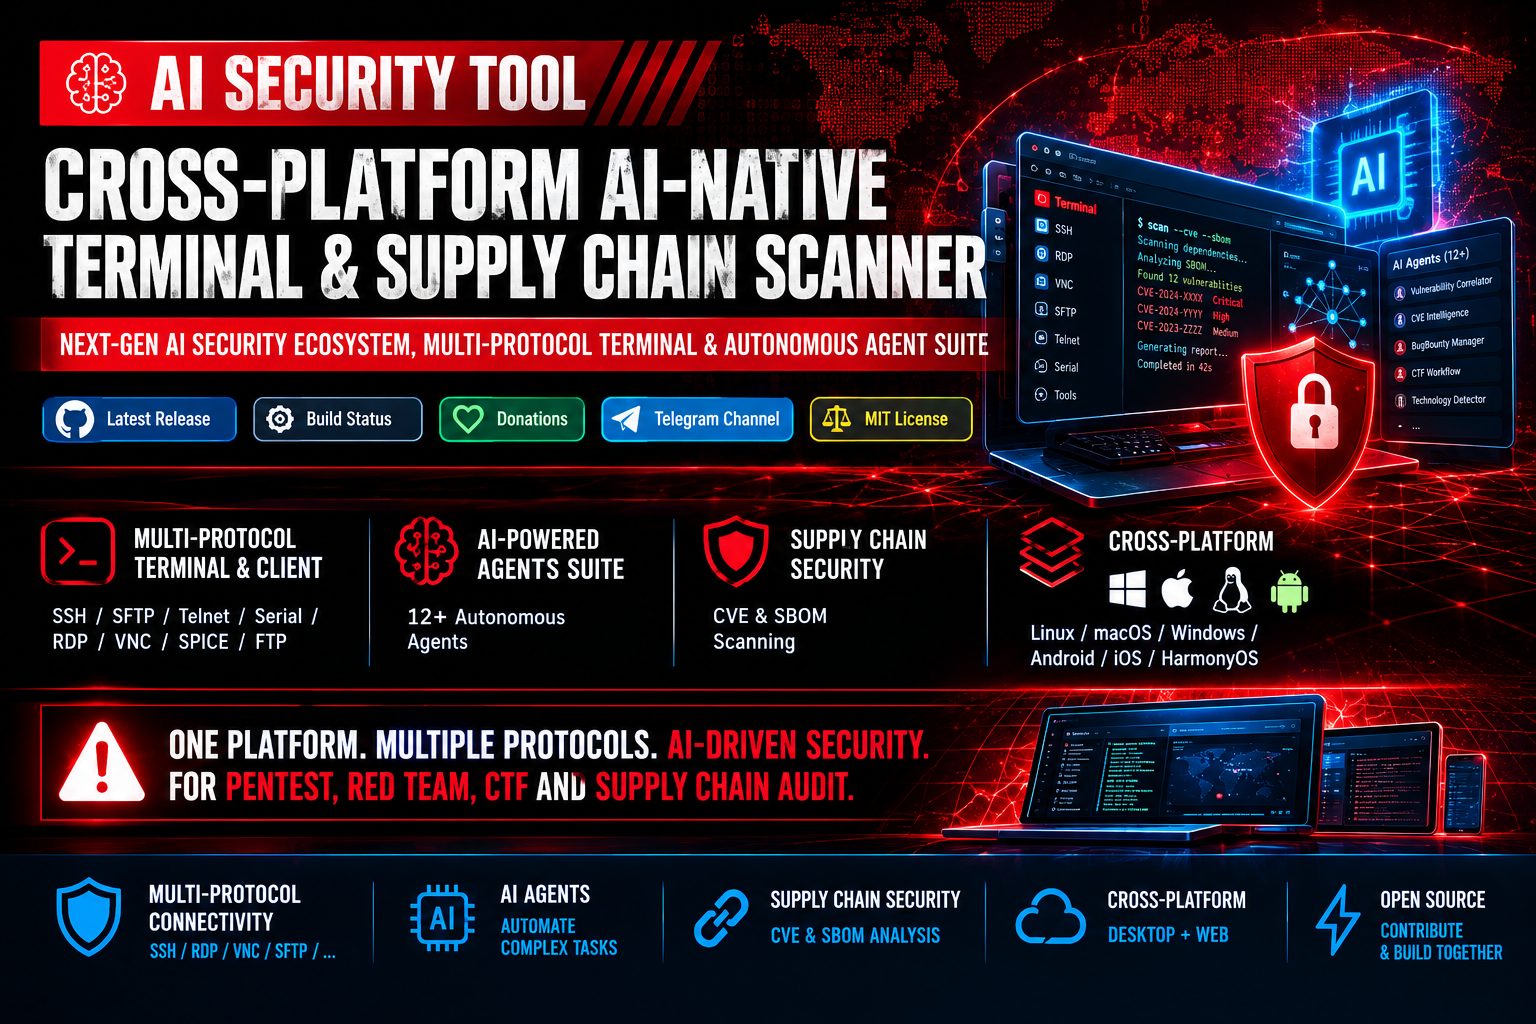
Cross-Platform AI-Nati & Supply Chain Scanner
</p>
</h1>
<p align="center"><strong>Next-Gen AI Security Ecosystem, Multi-Protocol Terminal & Autonomous Agent Suite</strong></p>
<hr>
<p align="center">
<a href=" rel="nofollow"><img src=" alt="Latest Release" style="max-width: 100%;"></a>
<a href=" rel="nofollow"><img src=" alt="Build Status" style="max-width: 100%;"></a>
<a href=" rel="nofollow"><img src=" alt="Donations" style="max-width: 100%;"></a>
<a href="" rel="nofollow"><img src=" alt="
<a href="LICENSE" rel="nofollow"><img src=" alt="License" style="max-width: 100%;"></a>
</p>
<p align="center">
<a href=" rel="nofollow"><b>🌐 Web Demo</b></a> •
<a href=" rel="nofollow"><b>📚 Project Website</b></a> •
<a href="" rel="nofollow"><b>💬 Community Chat</b></a>
</p>
<p align="center">
<b>Website Na:</b>
<a href=" •
<a href=" •
<a href=" •
<a href="
</p>
<p align="center">
<img width="100%" alt="AI Security Tool Banner" src="resources/banner.png" style="max-width: 100%; border-radius: 8px;">
</p>
<hr>
<h2>🧠 Conceptual O</h2>
<p>
<strong>AI Security Tool</strong> is an open-source, cross-platform ecosystem designed at the intersection of traditional system administration and modern cybersecurity. It combines a multi-protocol connectivity suite (SSH, RDP, VNC), deep Supply Chain Security analysis (CVE & SBOM auditing), and an autonomous ecosystem powered by <strong>12+ AI Agents</strong>.
<br><br>
The tool eliminates the need to switch between dozens of utilities during security audits, Red Team operations, penetration testing, or CTF challenges. A both as a desktop application (<strong>Linux, macOS, Windows, Android, iOS, HarmonyOS</strong>) and a fully featured <strong>Web Interface</strong>.
</p>
<h3>🎯 Core Philosophy</h3>
<p>
<em>"Bridge the gap between execution, intelligence, and supply chain audit."</em><br>
We built AI Security Tool to replace tedious manual workflows with a unified AI-Nati that automatically correlates contexts, tunes parameters, and automates auditing pipelines.
</p>
<hr>
<h2>🔍 Security Audit Modules & PoC Repositories</h2>
<p>A curated collection of scanners, PoC exploits, and technical research maintained by our community:</p>
<!-- Category 1: Remote Code Execution & Network Vulns -->
<details open>
<summary><b>🔥 Remote Code Execution (RCE) & Network Vulns</b> <code>5 modules</code></summary>
<br>
<ul>
<li>
<b><a href=" — <i>n8n Full Chain Unauthenticated RCE (Ni8mare)</i>
<a href="
</li>
<li>
<b><a href=" — <i>Netlogon Remote Code Execution Exploit</i>
<a href="
</li>
<li>
<b><a href=" — <i>Windows Remote Code Execution Proof-of-Concept</i>
<a href="
</li>
<li>
<b><a href=" — <i>Critical RCE Scanner Module</i>
<a href="
</li>
<li>
<b><a href=" — <i>Network Protocol Remote Code Execution</i>
<a href="
</li>
</ul>
</details>
<!-- Category 2: Pri Escalation -->
<details open>
<summary><b>🛡️ Pri Escalation (EoP) & Services</b> <code>3 modules</code></summary>
<br>
<ul>
<li>
<b><a href=" — <i>AD CS Certighost Domain Controller Impersonation</i>
<a href="
</li>
<li>
<b><a href=" — <i>CrossDevice Service Ele of Pri</i>
<a href="
</li>
<li>
<b><a href=" — <i>Local Pri Escalation Writeup & PoC</i>
<a href="
</li>
</ul>
</details>
<!-- Category 3: Research & Writeups -->
<details open>
<summary><b>📚 Research & Writeups</b> <code>2 modules</code></summary>
<br>
<ul>
<li>
<b><a href=" — <i>Deep Technical Analysis & PoC Research</i>
<a href="
</li>
<li>
<b><a href=" — <i>Full WriteUp & Exploitation Demonstration</i>
<a href="
</li>
</ul>
</details>
<br>
<h3>💻 Multi-Protocol Terminal & Client</h3>
<ul>
<li><strong>Supported Protocols:</strong> SSH, SFTP, Telnet, Serial Port, RDP, VNC, SPICE, FTP.</li>
<li><strong>UI & Customization:</strong> Window transparency (macOS, Windows), custom themes, and background images.</li>
<li><strong>Usability & Workflow:</strong>
<ul>
<li>Guake-style pop-up terminal triggered hotkey (default: <code>Ctrl + 2</code>).</li>
<li>Direct remote file editing via SFTP with a double-click.</li>
<li>Multi-input broadcast (transmit commands to multiple acti simultaneously).</li>
<li>SSH tunneling, SSH key/password authentication, global and session-specific proxy support.</li>
<li>Synchronization of bookmarks, themes, and quick commands Gist / Gitee Snippets.</li>
</ul>
</li>
</ul>
<h3>⚡ Ad Capabilities</h3>
<ul>
<li><strong>Intelligent Caching:</strong> Acceleration of repeated security analysis using LRU algorithms.</li>
<li><strong>Real-Time Process Manager:</strong> Li monitoring and execution control.</li>
<li><strong>API Security Testing:</strong> Built-in diagnostic modules for GraphQL, JWT, and REST APIs.</li>
<li><strong>LLM Integration:</strong> Built-in AI assistant supporting DeepSeek, OpenAI, and custom APIs for command suggestions, script generation, and terminal output analysis.</li>
</ul>
<hr>
<h2>🤖 Specialized AI-Agents Suite</h2>
<p>Dedicated autonomous agents integrated into the system for automating complex audit scenarios:</p>
<table>
<thead>
<tr>
<th>Agent</th>
<th>Purpose</th>
<th>Task Category</th>
</tr>
</thead>
<tbody>
<tr>
<td><code>IntelligentDecisionEngine</code></td>
<td>Automated tool selection and contextual parameter tuning</td>
<td>🧠 Core Logic</td>
</tr>
<tr>
<td><code>BugBountyWorkflowManager</code></td>
<td>Workflow management for reconnaissance and discovery</td>
<td>🎯 Pentest / Recon</td>
</tr>
<tr>
<td><code>CTFWorkflowManager</code></td>
<td>Automation and support for solving CTF challenges</td>
<td>🚩 CTF Automation</td>
</tr>
<tr>
<td><code>C</code></td>
<td>Deep research and Threat Intelligence gathering</td>
<td>🔍 Threat Intel</td>
</tr>
<tr>
<td><code></code></td>
<td>Identification and construction of complex multi-stage Attack Chains</td>
<td>🔗 Correlation</td>
</tr>
<tr>
<td><code>TechnologyDetector</code></td>
<td>Full tech stack identification and service fingerprinting</td>
<td>🌐 Fingerprinting</td>
</tr>
<tr>
<td><code>RateLimitDetector</code></td>
<td>Detection and automated e of rate-limiting mechanisms</td>
<td>⚡ Bypass & E</td>
</tr>
<tr>
<td><code>FailureReco</code></td>
<td>Automated error handling and tool recovery pipeline</td>
<td>🛡 System Resilience</td>
</tr>
<tr>
<td><code>PerformanceMonitor</code></td>
<td>Resource monitoring and system load optimization</td>
<td>📊 Resource Control</td>
</tr>
<tr>
<td><code>ParameterOptimizer</code></td>
<td>Context-aware parameter tuning for fuzzing and scanning tools</td>
<td>⚙️ Fuzzing Tuning</td>
</tr>
<tr>
<td><code>GracefulDegradation</code></td>
<td>Ensures fault tolerance during external service downtime</td>
<td>🔄 Fault Tolerance</td>
</tr>
</tbody>
</table>
<hr>
<h2>📊 Security Scanning & SBOM Workflow</h2>
<pre><code class="language-mermaid">graph TD
A[Target Project / Assets] --> B{Aggregated CVE DB Engine}
B -->|Daily Sync| C[NVD / OSV / GAD / RedHat]
A --> D[Binary & Dependency Analyzers]
D --> E[Generate / Parse SBOM Standard]
E --> F{ Correlator}
C --> F
F --> G[Enrich Context & Remediation Data]
G --> H[Export Reports: Console / JSON / CSV / HTML / PDF]
</code></pre>
<hr>
<h2>🚀 Quick Start & Installation</h2>
<h3>📦 Ready-to-Use Builds</h3>
<table>
<thead>
<tr>
<th>OS / Platform</th>
<th></th>
<th>Architecture / Format</th>
<th>Release Date</th>
<th>Status</th>
<th>Download Link</th>
</tr>
</thead>
<tbody>
<tr>
<td><strong>🪟 Windows</strong></td>
<td><code>v6.3.27</code></td>
<td>x64 Installer (.exe)</td>
<td>2026-09-08</td>
<td>🟢 Latest</td>
<td><a href=" .exe</strong></a></td>
</tr>
<tr>
<td><strong>🪟 Windows</strong></td>
<td><code>v6.3.20</code></td>
<td>x64 Portable (.tar.gz)</td>
<td>2026-09-08</td>
<td>🟢 Latest</td>
<td><a href=" .tar.gz</strong></a></td>
</tr>
<tr>
<td><strong>🍏 macOS</strong></td>
<td><code>v5.3.29</code></td>
<td>Apple Silicon M1/M2/M3 (.dmg)</td>
<td>2026-09-05</td>
<td>🟢 Stable</td>
<td><a href=" .dmg</strong></a></td>
</tr>
<tr>
<td><strong>🐧 Linux</strong></td>
<td><code>v5.3.27</code></td>
<td>Uni x64 (.tar.gz)</td>
<td>2026-09-01</td>
<td>🟢 Stable</td>
<td><a href=" .tar.gz</strong></a></td>
</tr>
<tr>
<td><strong>🤖 Android</strong></td>
<td><code>v8a 5.3.27</code></td>
<td>ARM64 APK (.apk)</td>
<td>2026-09-01</td>
<td>🟢 Stable</td>
<td><a href=" .apk</strong></a></td>
</tr>
</tbody>
</table>
<h3>🧪 One-Line Installation Scripts</h3>
<p>Fast deployment installation scripts:</p>
<p><strong>Linux / macOS:</strong></p>
<pre><code class="language-bash">curl -o- | bash
or using wget:
wget -qO- | bash</code></pre>
<p><strong>Windows PowerShell</strong> (Run as administrator):</p>
<pre><code class="language-powershell">iwr " -OutFile "$en\Desktop\one-line-web.bat"
cmd /c "%USERPROFILE%\Desktop\one-line-web.bat"</code></pre>
<p>The script installs Go, Python, and Node.js, extracts the archive. No extra commands are required.</p>
One-liner
or : ./build/bin/run-prod.sh</code></pre>
<p>Once started, open your browser at: <code>
<h3>🌐 Ser & Configuration</h3>
<p>When hosting on external or public networks, configure en in your <code>.env</code> file:</p>
<pre><code class="language-text">ENABLE_AUTH=1 # Enable password authentication
DISABLE_LOCAL_TERMINAL=1 # Disable direct access to local ser
SER=your_ser
SER=your_strong_password</code></pre>
<p>Start service:</p>
<pre><code class="language-bash">./run-ai-security-tool-web.sh</code></pre>
<p><em>Example configurations for Nginx and SSL are provided in <code>examples/nginx.conf</code>.</em></p>
<hr>
<h2>⚖️ License & Legal Disclaimer</h2>
<h3>🚨 Security & Compliance Notice</h3>
<blockquote>
<p>
<strong>IMPORTANT: This tool grants AI Agents capability to execute system commands.</strong><br>
• <strong>Action Control:</strong> Always monitor AI Agent acti via the real-time dashboard.<br>
• <strong>Least Pri:</strong> Execute the application strictly with the minimum necessary system permissions.<br>
• <strong>Network Security:</strong> Always enable authentication (<code>ENABLE_AUTH=1</code>) and disable local terminal access (<code>DISABLE_LOCAL_TERMINAL=1</code>) when exposing the Web interface externally.<br>
Running this tool against unauthorized systems is illegal. The de assume no liability for misuse or system damage.
</p>
</blockquote>
<hr>
<h2>🔄 Contribution & Community</h2>
<p>We welcome contributions from the cybersecurity community! Key contribution areas:</p>
<ol>
<li><strong>AI Integrations:</strong> Adding new LLM pro and de specialized security agents.</li>
<li><strong>Security Tools:</strong> Integrating third-party CLI scanners and custom parsers.</li>
<li><strong>Optimization:</strong> Improving parser speed, caching logic, and resource consumption.</li>
<li><strong>Documentation:</strong> Writing guides, research papers, and localized translations.</li>
</ol>
<hr>
<h2>🔗 Contact & Support</h2>
<ul>
<li><strong>Official Website:</strong> <a href="
<li><strong>gt;
<li><strong>Sponsor Project:</strong> <a href=" Donations</a></li>
<li><strong>Open Collective:</strong> <a href="
</ul>
<hr>
<p align="center"><em>AI Security Tool — Reimagining terminal workflow and automation for cybersecurity professionals.</em></p>
</article>
项目信息
开发语言:HTML
Star 数:409
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🛡️ Free open-source AI-powered security terminal & vulnerability scanner (CVE, SBOM). Supports SSH, SFTP, RDP, VNC, Serial, and 12+ autonomous AI agents (DeepSeek, OpenAI) for automated security workflows, CTF & DevSecOps. Cross-platform & Web UI.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ai-security-tool - 🛡️ Free open-source AI-powered security terminal & |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:37:04 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 192 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |