 安全软件
点击放大
SecObserve - SecObserve is an open source vulnerability and lic
项目说明
<di="center">
<img src=" width="80" alt="">
SecObserve
![OpenSSF Best Practices]() ![OpenSSF Scorecard]()
O · Integrations · Quickstart · Documentation · Code of Conduct · Contributing · License · Community projects · Funding
</div>
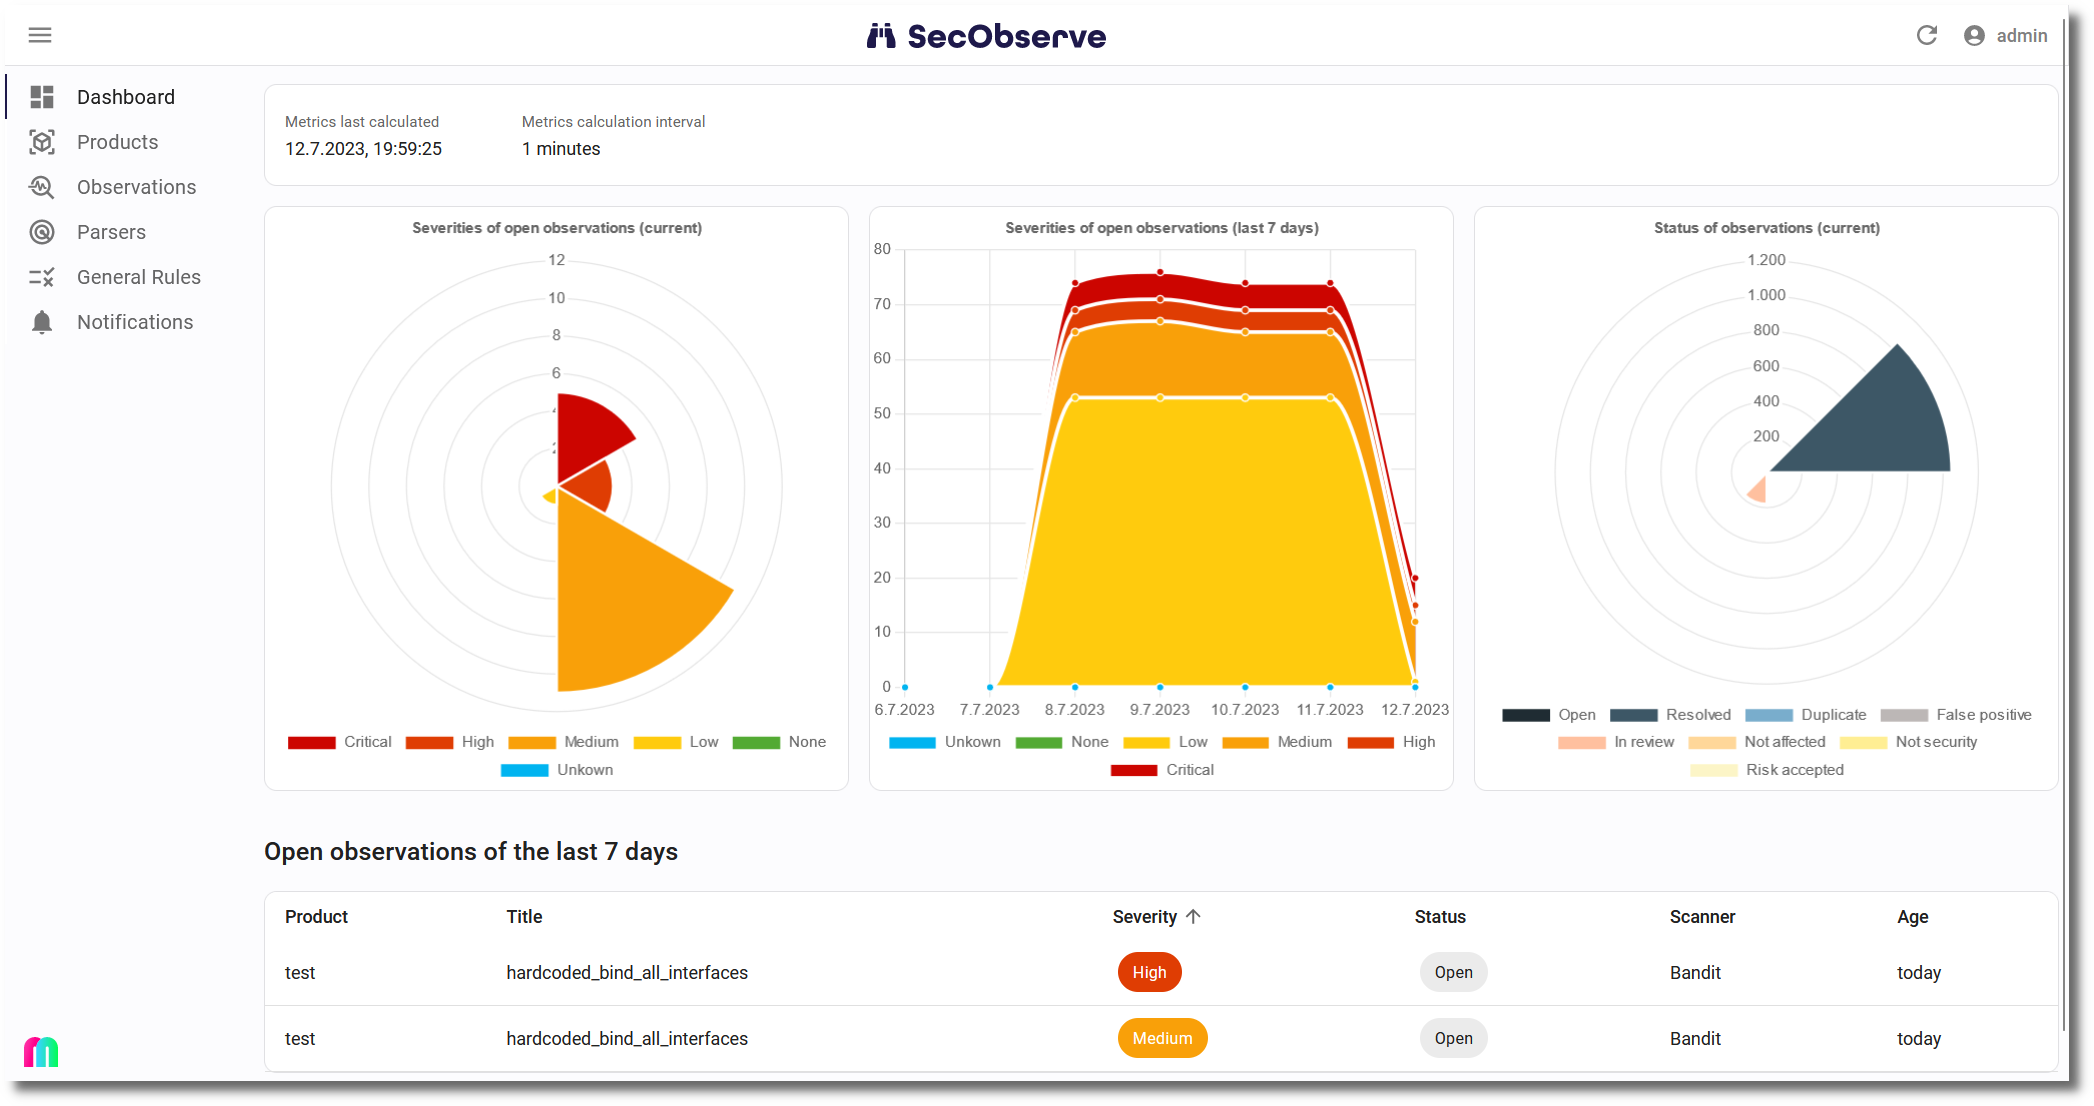
SecObserve is an open source and license management system for software de teams and cloud en. It supports a of open source scanners and integrates easily into CI/CD pipelines. Results about potential security flaws from scanning tools are made a for assessment and reporting.
!Dashboard
O
The aim of SecObserve is to make scanning and management as easy as possible for software de projects using open source tools. It consists of 2 major components:
* and license management system SecObserve: SecObser the de team with an o of the results of all and license scans for their project, which can be easily filtered and sorted. In the detailed view, the results are displayed uniformly with a wealth of information, regardless of which scanner generated them.
With the help of automatically executed rules and manual assessments, the results can be efficiently e to eliminate irrelevant results and accept risks. This allows the de team to concentrate on fixing the relevant .
* GitLab CI templates and GitHub actions: Integrating scanners into a CI/CD pipeline can be tedious. Each tool has to be installed differently and is called with different parameters. To avoid having to solve this task all o, there are repositories with GitLab CI Templates and GitHub Actions. These make the process of integrating scanners very simple by pro uniform methods for launching the tools and uniform parameters. The tools are regularly updated in the repositories so that the latest features and bug fixes are always a.
All templates run the scanner, upload the results into SecObserve and make the results of the scans a for download as artefacts in JSON format.
The sources of the GitHub actions and GitLab CI templates can be found in
!O
Integrations
!O
Quickstart
This starts SecObserve in de and testing mode with Docker Compose.
admin / adminTemplates for producti are documented in <
Documentation
The full documentation how to install and use SecObserve can be found here:
Code of Conduct
Please note that this project is released with a Code of Conduct. By participating in this project you agree to abide by its terms.
Contributing
Please see the Contributing Guidelines for more information on how to get in in the project.
License
SecObserve is licensed under the 3-Clause BSD License
Community projects
Funding
<img src=" width="20%" alt="NLNet"> <img src=" width="20%" alt="NLNet">
This project is funded through the NGI0 Commons Fund, a fund established by NLnet with financial support from the European Commission's Next Generation Internet programme, under the aegis of DG Communications Networks, Content and Technology under grant agreement No 101135429. Additional funding is made a by the Swiss State Secretariat for Education, Research and Inno (SERI).
项目信息
开发语言:Python
Star 数:317
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕SecObserve is an open source vulnerability and license management system for software development teams and cloud environments. It supports a variety of open source vulnerability scanners and integrates easily into CI/CD pipelines.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | SecObserve - SecObserve is an open source vulnerability and lic |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:38:00 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 520 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |