 安全软件
点击放大
OSTE-Meta-Scan - The OSTE meta scanner is a comprehensive web vulne
项目说明
OSTE-Meta-Scanner
This project is now maintained and supported by OSTE and is no longer a as an open-source project. For inquiries, commercial use, or support, please contact OSTE via LinkedIn, or official website, or sales team at +213.7.98.38.94.54 .
!Project Logo
This project aims to simplify the field of Dynamic Application Security Testing. The OSTE meta scanner is a comprehensive web scanner that combines multiple DAST scanners, including Nikto Scanner, ZAP, Nuclei, SkipFish, and Wapiti.
Table of Contents
Introduction
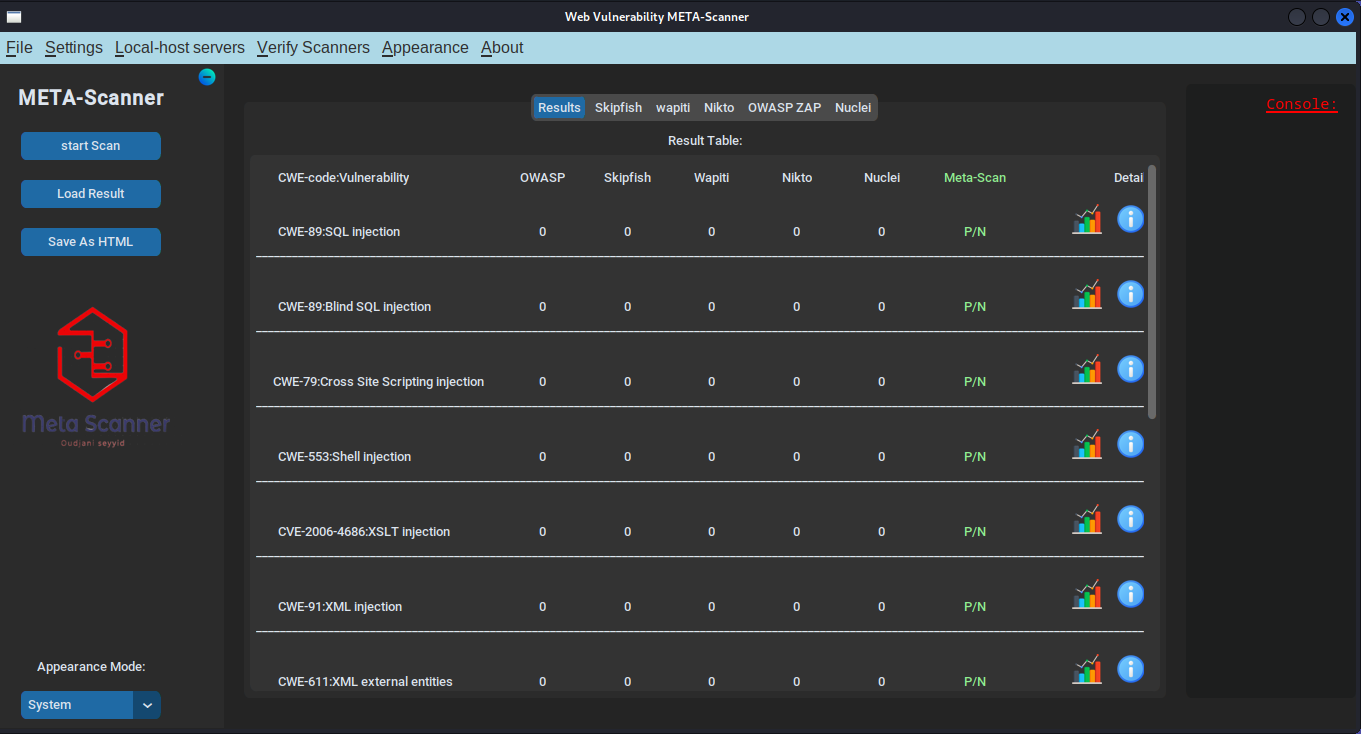
This software offers a user-friendly graphical interface which presents a comprehensi for each scan, making the scanning process effortless and straightforward.
The main focus of this scanner is on web injection such as SQL injection, XSS injection, OS command injection, XML injection, and many more. Additionally, it provides a list of supported by each scanner, apart from injection .
We offer two types of reports. The first is a consolidated report in JSON format, which includes important reports from each scanner. It contains details such as the , the corresponding URL, the parameter used, the Curl command, the attack , a description of the , and more.
The second report is an HTML file format that specifically highlights successful injection attacks. Our results and decisions are based on a no algorithm proposed during the ("A Meta-Scan based approach for the detection of injection in Web applications.", -Uni May 8, 1945 -Guelma -, Computer Science Department, Presented by: SEYYID TAQY EDINE OUDJANI, Supervised by: DR. ABDELHAKIM HANNOUSSE. 2023). [].
Features
List of Main supported:
1. Injection
- SQL injection
- Cross site scripting
- OS command injection
- XML injection
- XSLT injection
- XML External entites
- code injection
- host header injection
- html injection
- Template injection (ser)
- CRLF injection
- OGNL injection
2. Other (refer to the repository of each scanner for a complete list.)
- Skipfish support List.
- Wapiti support List.
- ZAP Acti list.
- Nikto support List (Specified: Tunning 9 & 4).
- Nuclei C.
Installation
The installation process requires a specific set of requirements. While this project is primarily supported on Kali Linux, it can also be compatible with other operating systems:
1. ZAP:
- kaliLinux: [ sudo apt install zaproxy ]
- Other OSs: [ ]
2. Wapiti:
- kaliLinux: [ sudo apt install wapiti ]
- Other OSs: [ ]
3. Skipfish:
- kaliLinux: [ sudo apt install skipfish ]
- Other OSs: [ ]
4. Nikto :
- kaliLinux: [ sudo apt install nikto ]
- Other OSs: [ ]
5. Nuclei:
- kaliLinux: [ sudo apt install nuclei ]
- Other OSs: [ ]
6. Python 3 * Libraries:
- customtkinter
- zapv2
- jinja2
- webbrowser
- PIL
- matplotlib
- BeautifulSoup
- pprint
7. optional requirments for more features:
- XAMP server
- NPM
(Note: Please note that I will be creating a bash script to automate the installation steps for Linux users as soon as possible.)
Usage
After cloning the repository to your local machine, you can initiate the application by executing the command python3 Metascan.py.
Then, you can na through the interface of the application.
Docker
A Docker image is a in OSTEscaner directory. It is based on kali linux and will need a xserver to display the python GUI.
On linux, you probably already have one runnig, on windows (including WSL) good oss servers are or xming.
first export your display:
Linux: export DISPLAY=:0.0
Windows (wsl): export DISPLAY="$(grep nameserver /etc/resolv.conf | sed 's/nameserver //'):0"
then build & run the docker image:
troubleshooting:
_tkinter.TclError: couldn't connect to display error. As it is based on network communication, yo may need to include your local ip address: e.g. export DISPLAY:192.168.100.5:0.0, on windows you may look for tutorial on xming and install additional fonts.Failed to fetch ) just retry the buildContributing
We welcome contributions to enhance and improve this project.
either by donation :
![BuyMeACoffee]()
or by your power of mind .contribute, please follow these guidelines:
1. Fork the repository and create a new branch for your contribution.
2. Ensure that your code adheres to the project's coding standards.
3. Make your changes, addressing the specific issue or adding the proposed enhancement.
4. Test your changes thoroughly.
5. Commit your changes and provide a clear and descripti message.
6. Push your changes to your forked repository.
7. Submit a pull request, detailing the changes you've made and pro any relevant information or context.
Please note that all contributions will be re by the project maintainers. We appreciate your effort and will do our best to provide timely feedback.
If you have any questions or need further clarification, feel free to reach out to us through the issue tracker or by contacting the project maintainers directly.
License
This project is under GNU GENERAL PUBLIC LICENSE 3, 29 June 2007.
This project is intended for educational purposes and aims to simplify the o assessment of cybersecurity. However, we want to emphasize that we are not liable for any malicious use of this application. It is crucial that users of this software exercise responsibility and ethical behavior. We strongly recommend notifying the targets or indi in before utilizing this software.
ScreenShots
!Main Interface
Contact
linkdin:()
项目信息
开发语言:Python
Star 数:305
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕The OSTE meta scanner is a comprehensive web vulnerability scanner that combines multiple DAST scanners, including Nikto Scanner, ZAP, Nuclei, SkipFish, and Wapiti.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OSTE-Meta-Scan - The OSTE meta scanner is a comprehensive web vulne |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:38:04 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 361 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |