 安全软件
点击放大
vbsec - Security scanning skill for Claude Code, Codex and
项目说明
<h1 align="center">vbsec — Security scanning for AI-written code</h1>
<p align="center">A security scanning skill for Claude Code, Codex and Antigravity: it reads your code, finds the 21 most common types, and shows you how to fix each one.<br>Free · Open source · Nothing extra to install</p>
<p align="center">
<a href="./LICENSE"><img src=" alt="MIT license"></a>
<a href=" src=" alt="GitHub stars"></a>
<img src=" alt="Claude Code">
<img src=" alt="OpenAI Codex">
<img src=" alt="Google Antigravity">
</p>
<p align="center">
<b><a href="#install">Install</a></b> ·
<b><a href="docs/examples/sample-report.md">Sample report</a></b> ·
<b><a href="#what-">21 types</a></b> ·
<b><a href="README.vi.md">🇻🇳 Tiếng Việt</a></b>
</p>
<p align="center">
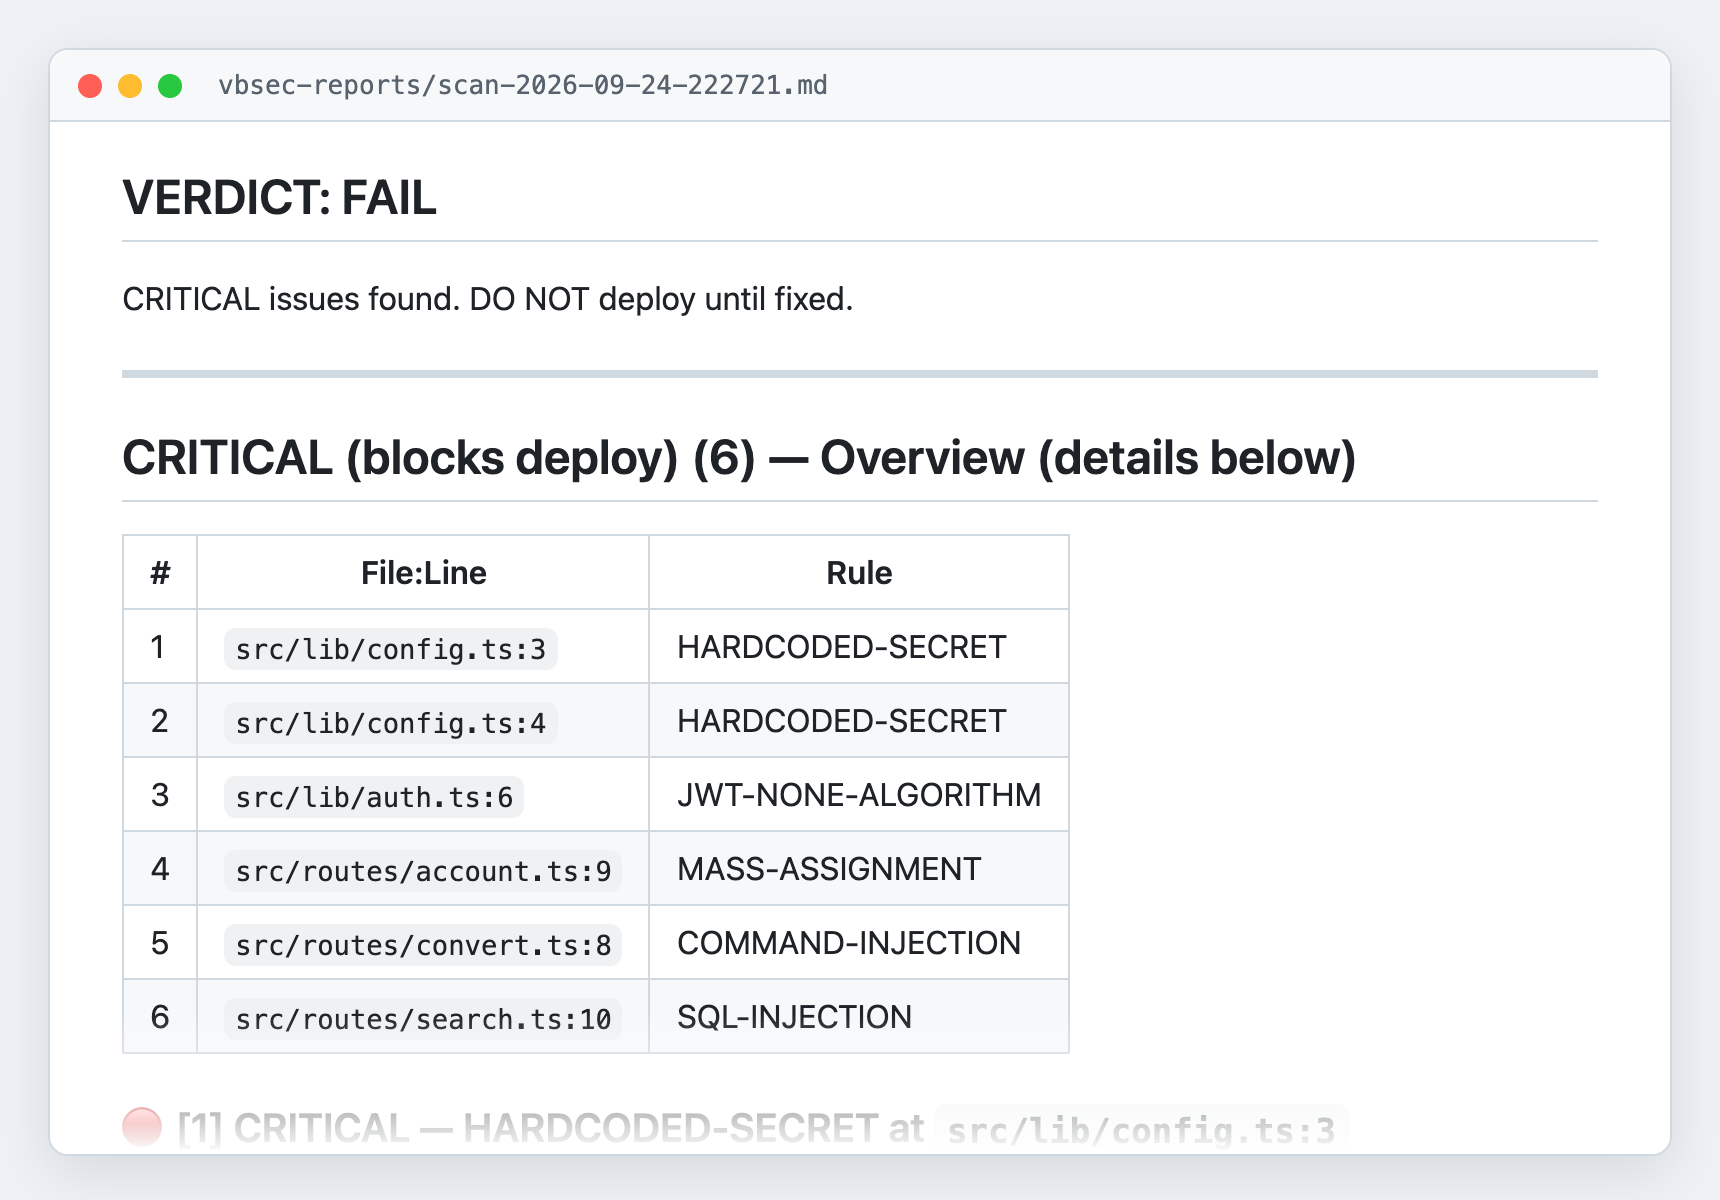
<a href="docs/examples/sample-report.md"><img src="docs/images/sample-report.png" alt="vbsec report: FAIL, table of 6 critical issues" width="760"></a><br>
<sub>A real report from scanning a sample Express + React app. Click the image to read the full report.</sub>
</p>
What vbsec does
/ you can hand to whoe it, with a JSON summary at the end for CI/CDExample: what vbsec catches
The code below works. Clicking through the app by hand, you'd ne a problem. AI assistants write code like this all the time.
vbsec reports 2 CRITICAL issues:
| Issue | Impact | Fix vbsec suggests |
|---|---|---|
| JWT-NONE-ALGORITHM | Anyone can mint their own role: "admin" token without the secret key | Use jwt.(token, secret, { algorithms: ["HS256"] }) |
| SQL-INJECTION | Typing ' UNION SELECT email, password_hash... into the search box dumps the whole user table | Pass parameters with ` replacements: { q: %${q}% } instead of building the string |
Read the full sample report to see how vbsec explains each issue.
Test results
The repo ships 8 sample apps with known, planted bugs (Go, PHP, TypeScript, Python, .NET), including hard cases: data flowing through several files, sanitizers written wrong, race conditions when deducting a balance. Each set also has traps that look like bugs but are safe, to measure false alarms.
| | Latest run |
|---|---|
| Bugs caught | 54/55 |
| False alarms on safe traps | 0 |
AI output can vary between runs. Re-run it yourself with ./scripts/run-fixtures.sh (see tests/README.md). vbsec has also been tried on OWASP Juice Shop and caught the classes matching its documented challenges.
How vbsec works
It reads code like a re, not like grep. Many scanners flag every query( as "possible SQL injection", so they cry wolf constantly and people stop reading. vbsec reads the surrounding code, works out where the data comes from, and only then decides.
Take the same line of code:
comes from a search box the user types into (req.query.q): flagged, because anyone can type malicious SQL there. is a constant in the code or a value from a config file: not flagged, because outsiders can't change it.To tell these apart, vbsec sorts data into 4 trust levels, from "sent by a stranger" (forms, URLs, headers, uploads) to "produced by the system" (constants, en ). Only stranger-supplied data that reaches a dangerous call without being cleaned gets reported.
It knows each language and framework. On top of the general rules, vbsec has dedicated rules for Go, PHP, TypeScript/Ja, Python and .NET, so it knows each library's traps. For example: Prisma.sql is safe but $queryRawUnsafe is not, bypassSecurityTrustHtml in Angular switches off XSS protection, and Gin's debug mode left on in production.
Small repos scan instantly, big ones get split up. Under about 20 code files, vbsec scans directly in roughly 30–60 seconds. Larger repos are split into parts for up to 3 agents working in parallel, then the results are merged and de-duplicated.
One issue per line item. A line of code with 2 problems (say, reading another user's data and a race condition) shows up as 2 separate issues. Counts stay honest, and each one can be ticked off as it's fixed.
Reports in English or . is the default; add lang=en for English. The report ends with a fixed-format JSON block in English, so CI/CD can read it and block merges while critical issues remain.
The same rules on all three tools. Claude Code, Codex and Antigravity share one rule set and produce the same findings. The only difference: Claude Code runs in parallel, so it's faster on large repos.
Install
You need one of: Claude Code, OpenAI Codex CLI, Google Antigravity.
The script detects which of these tools you have and installs the skill for each. To update later: cd ~/vbsec && git pull.
Manual install, installing for one specific tool, troubleshooting: docs/en/installation.md.
Usage
| Tool | How to run |
|---|---|
| Claude Code | / |$
| OpenAI Codex CLI | |
| Google Antigravity | say "scan security for this repo" |
Reports are saved to /scan-<timestamp>.md inside the scanned folder. Add / to .gitignore; vbsec reminds you if it's missing.
All options: docs/en/usage.md.
What vbsec catches
| Category | Issues |
|---|---|
| Leaked secrets, config | HARDCODED-SECRET · · CORS-MISCONFIG |SQL-INJECTION
| Injection | · COMMAND-INJECTION · XSS · INSECURE-DESERIALIZATION · SSRF · PATH-TRA |BROKEN-ACCESS-CONTROL
| Authentication, authorization | · IDOR · MASS-ASSIGNMENT · JWT-NONE-ALGORITHM · WEAK-PASSWORD-HASHING · CSRF |BRUTE-FORCE
| Abuse protection | · MISSING-RATE-LIMIT · RACE-CONDITION · UNRESTRICTED-FILE-UPLOAD |OUTDATED-DEPENDENCY
| Dependencies | · SLOPSQUATTING (package names the AI made up, registered first by attackers) |
Se, and safe code examples, and which languages ha rules: docs/en/rules.md.
Limitations
vbsec is a first line of defense, not proof that your system is secure.
, pip-audit, go, composer auditAdd a badge to your repo
Scanned with vbsec and fixed e? Add this badge to your README:
![vbsec: security scanned · passed]()
Sponsors
vbsec is free and open source thanks to:
<table>
<tr>
<td align="center" ="top" width="50%">
<a href=" src="docs/images/sponsor-sepay.svg" alt="SePay" height="42"></a><br>
<b><a href="
Open Banking platform: automatic bank transfer confirmation and API connections to banks
</td>
<td align="center" ="top" width="50%">
<a href=" src="docs/images/sponsor-123host.svg" alt="123HOST" height="42"></a><br>
<b><a href="
Hosting, VPS, servers and domains for businesses and de in
</td>
</tr>
</table>
Authors
vbsec distills security experience from running real payment and hosting systems, which get attacked every day, into a rule set that lets AI review the code AI writes.
Other open-source projects:
Contributing
Contributions are welcome: bug reports, rule fixes, new languages. See docs/en/contributing.md.
Three platforms, one rule set
| Platform | Skill folder | Large repos |
|---|---|---|
| Claude Code | skills// (canonical) | 3 parallel agents |skills/codex//
| OpenAI Codex CLI | | Scans parts one by one |skills/antigravity//
| Google Antigravity | | Scans parts one by one |
Edit rules in the canonical skills//, then run ./scripts/sync-skills.sh to copy them to the other two. SKILL.md and workflows/large-review*.md are maintained separately per platform.
Before opening a PR
Roadmap
, opt-in, needs network); automatic fixes by building (--auto-fix`, opt-in, needs git). See usageLicense
MIT · © 2026 Bui Tan Viet & Phan Quoc Hien
项目信息
开发语言:Python
Star 数:287
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Security scanning skill for Claude Code, Codex and Antigravity. Finds the 21 most common vulnerabilities in AI-written code and shows how to fix each one.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | vbsec - Security scanning skill for Claude Code, Codex and |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:38:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 206 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |