 安全软件
点击放大
pysentry - 🐍 Scan your Python dependencies for known security
项目说明
<di="center">
<img src="assets/logo.svg" alt="PySentry logo" width="96" height="96">
PySentry
Fast, reliable scanning for Python dependencies.
![CI]()
![PyPI]()
![crates.io]()
![Downloads]()
Documentation · Benchmarks · Help test & improve · Usage survey
</div>
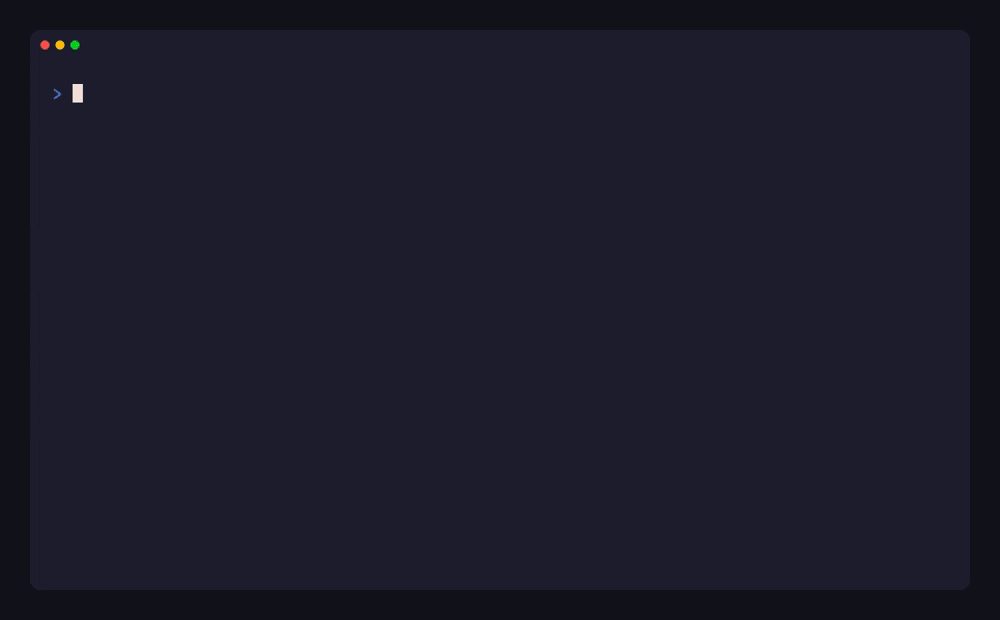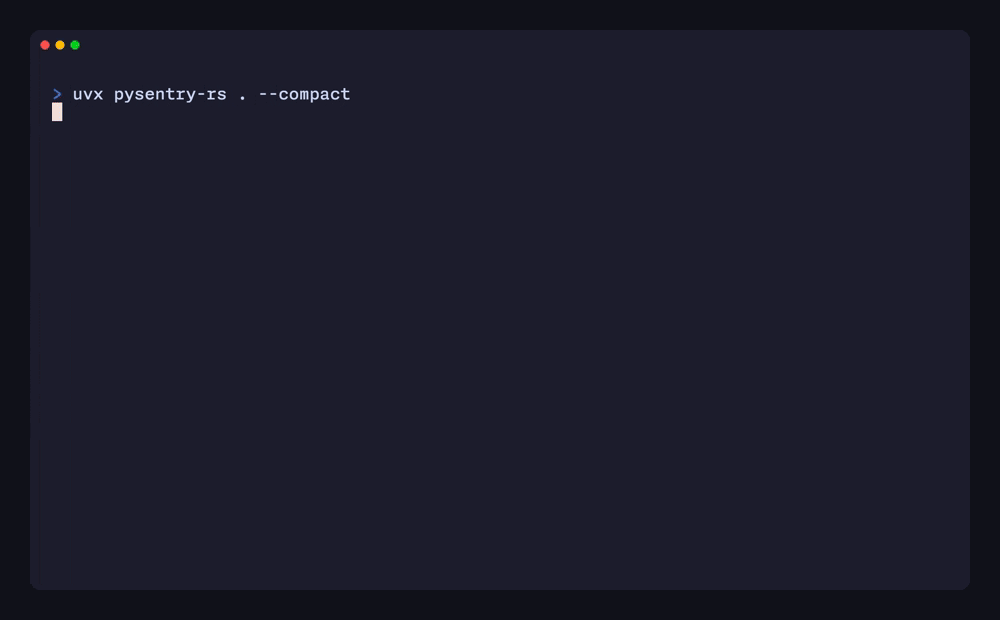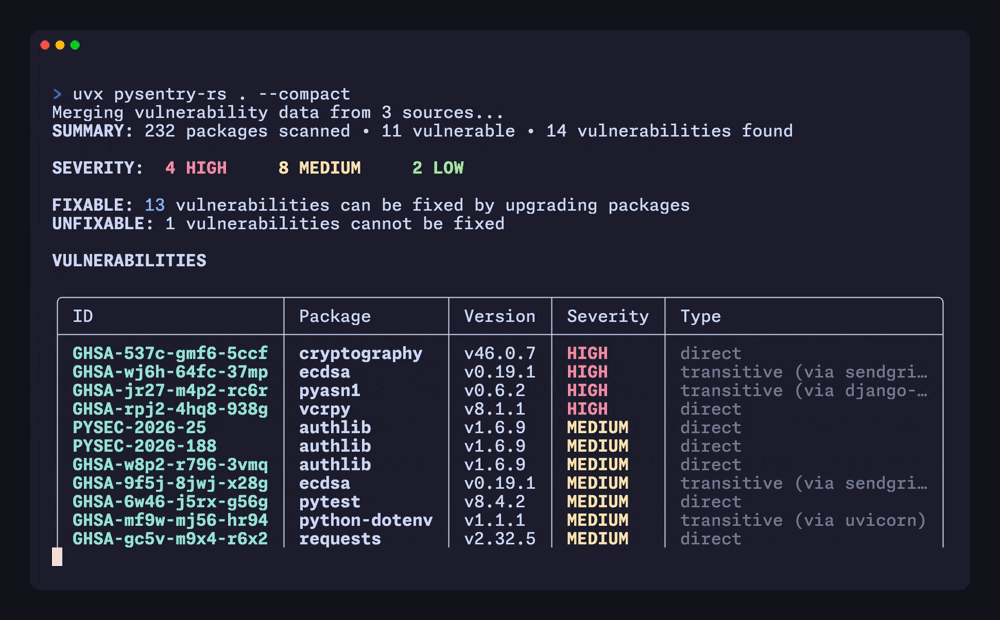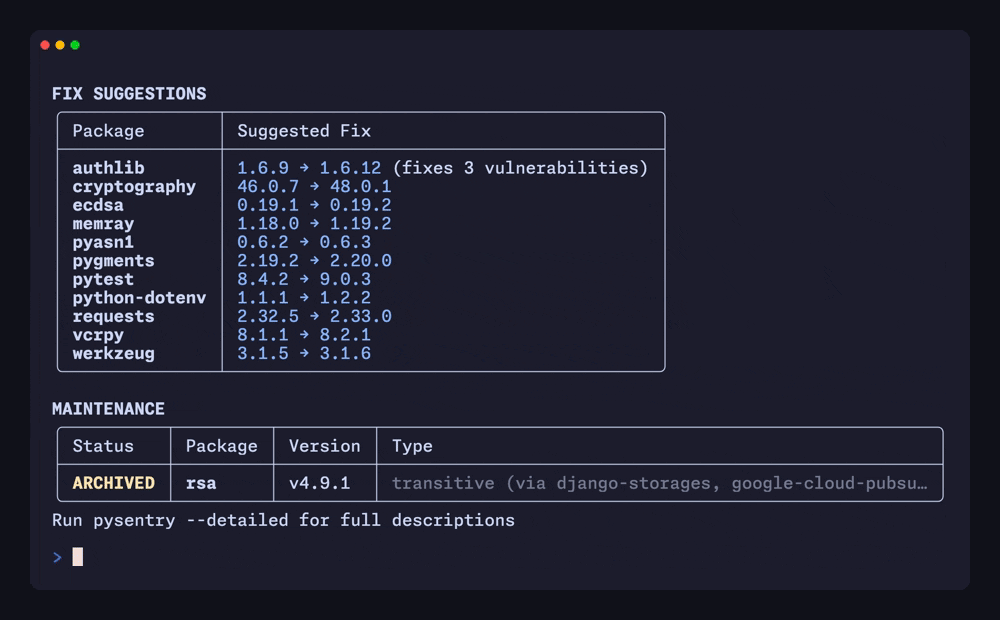
PySentry audits Python projects for known security . It reads your lock file or manifest, resolves the full dependency tree, and checks every package against three databases — then reports what is affected, how severe it is, and the upgrade that fixes it.
!PySentry scanning a project and reporting
Features
uv.lock, poetry.lock, Pipfile.lock, pylock.toml, pyproject.toml, Pipfile, requirements.txt, and PEP 723 inline script metadata. Lock files take precedence when both are present.--forbid-quarantined turns known malware into a failing build.--fail-on sets the exit threshold without hiding lower-se findings.Used by
PySentry runs in CI pipelines at Genkit (Google), O, activist.org, and To Be Precise, among others.
Installation
Pre-built binaries are attached to GitHub Releases. See the installation guide for all options.
> Naming: the Python package installs the binary as pysentry-rs; the Rust crate and release binaries are plain pysentry. Examples below use pysentry-rs — substitute accordingly.
Quick start
More examples in the quickstart guide.
Pre-commit
CI
The GitHub Action downloads a checksum- binary, audits the project, and uploads a SARIF report to GitHub Code Scanning:
On any other CI system, pysentry-rs --fail-on high exits non-zero when findings reach the threshold. Details in the CI guide.
Configuration
Project defaults live in .pysentry.toml or pyproject.toml; CLI flags always take precedence:
All options are covered in the configuration guide.
Documentation
Full documentation lives at
Installation ·
Quickstart ·
CLI options ·
Configuration files ·
En ·
Troubleshooting
Requirements
cargo install or building from sourceuv (recommended) or pip-tools for scanning manifests without a lock file (requirements.txt, pyproject.toml, Pipfile) — auditing lock files needs no external toolsFeedback
Bug reports and feature requests are welcome on the issue tracker; a couple of minutes on the usage survey helps shape the roadmap. For anything else, reach out at .
If PySentry saves you time, consider sponsoring on GitHub or buying me a coffee.
Acknowledgments
Inspired by pip-audit and uv #9189. data comes from PyPA, PyPI, and OSV.dev.
License
MIT
项目信息
开发语言:Rust
Star 数:250
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🐍 Scan your Python dependencies for known security vulnerabilities with Rust-powered scanner展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | pysentry - 🐍 Scan your Python dependencies for known security |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:39:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 218 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |