 安全软件
点击放大
Scanner-and-Patcher - A Web Vulnerability Scanner and Patcher
项目说明
Scanner and Patcher ![Build Status]()
***
<a href=" target="_blank">
<img alt="Maintenance" src=" />
</a>
<a href=" target="_blank">
<img alt="Documentation" src=" />
</a>
<a href=" target="_blank">
<img alt="License: MIT" src=" />
</a>
O:
The Scanner and Patcher project is built as part of the AlphaSecure framework, which has been presented and published at ACM IC3 2024 under the title AlphaSecure: A State-of-the-Art Framework for Web Application Detection and Patch Recommendation Using Automated Techniques. You can find the publication here AlphaSecure: A State-of-the-Art Framework for Web Application Detection and Patch Recommendation Using Automated Techniques.
This tools is very helpful for finding present in the Web _Applications_.
* A web application scanner explores a web application by crawling through its web pages and examines it for security , which in generation of malicious inputs and e of application's responses.
* These scanners are automated tools that scan web applications to look for security . They test web applications for common security problems such as cross-site scripting (XSS), SQL injection, and cross-site request forgery (CSRF).
* This scanner uses different tools like nmap, dnswalk, dnsrecon, dnsenum, dnsmap etc in order to scan ports, sites, hosts and network to find like OpenSSL CCS Injection, Slowloris, Denial of Service, etc.
***
Tools Used
***
|Serial No.|Tool Name| |Serial No.|Tool Name|
|:---------:|:--------|:--|:---------:|:--------:|
|1|whatweb| |2|nmap|
|3|golismero| |4|host|
|5|wget| |6|uniscan|
|7|wafw00f| |8|dirb|
|9|davtest| |10|thehar|
|11|xsser| |12|fierce|
|13|dnswalk| |14|dnsrecon|
|15|dnsenum| |16|dnsmap|
|17|dmitry| |18|nikto|
|19|whois| |20|lbd|
|21|wapiti| |22|devtest|
|23|sslyze|
***
Working
---
Phase 1
* User has to write:- "python3 web_scan.py (https or http) ://example.com"
* At first program will note initial time of running, then it will make url with "www.example.com".
* After this step system will check the internet connection using ping.
* Functionalities:-
* * To na to helper menu write this command:- --help for update --update
* * If user want to skip current scan/test:- CTRL+C
* * To quit the scanner use:- CTRL+Z
* * The program will tell scanning time taken by the tool for a specific test.
Phase 2
* From here the main function of scanner will start:
* The scanner will automatically select any tool to start scanning.
* Scanners that will be used and filename rotation (default: enabled (1)
* Command that is used to initiate the tool (with parameters and extra params) already given in code
* After founding in web application scanner will classify in specific format:-
* * [Responses + Se (c - critical | h - high | m - medium | l - low | i - informational) + Reference for Definition and Remediation]
* * Here c or critical defines most wheres l or low is for least system
#### Definitions:-
* > Critical:- * that score in the critical range usually have most of the following characteristics:
Exploitation of the likely results in root-le of servers or infrastructure devices.Exploitation is usually straightforward, in the sense that the attacker does not need any special authentication credentials or knowledge about indi , and does not need to persuade a target user, for example engineering, into performing any special functions.*
* > High:- *An attacker can fully compromise the confidentiality, integrity or a, of a target system without specialized access, user interaction or circumstances that are beyond the attacker’s control. Very likely to allow lateral mo and escalation of attack to other systems on the internal network of the application. The is difficult to exploit. Exploitation could result in elevated pri. Exploitation could result in a significant data loss or downtime.*
* > Medium:- *An attacker can partially compromise the confidentiality, integrity, or a of a target system. Specialized access, user interaction, or circumstances that are beyond the attacker’s control may be required for an attack to succeed. Very likely to be used in conjunction with other to escalate an attack. that require the attacker to manipulate indi engineering tactics. Denial of service that are difficult to set up. Exploits that require an attacker to reside on the same local network as the . where exploitation provides only very limited access. that require user pri for successful exploitation.*
* > Low:- *An attacker has limited scope to compromise the confidentiality, integrity, or a of a target system. Specialized access, user interaction, or circumstances that are beyond the attacker’s control is required for an attack to succeed. Needs to be used in conjunction with other to escalate an attack.*
* > Info:- *An attacker can obtain information about the web site. This is not necessarily a , but any information which an attacker obtains might be used to more accurately craft an attack at a later date. Recommended to restrict as far as possible any information disclosure.*
* > |CVSS V3 SCORE RANGE|SE IN AD|
> |:-------------------:|:--------------------:|
> |0.1 - 3.9|Low|
> |4.0 - 6.9|Medium|
> |7.0 - 8.9|High|
> |9.0 - 10.0|Critical|
####
* After this scanner will show results which inclues:
* * Response time
* * Total time for scanning
* * Class of
#### Remediation
* Now, Scanner will tell about *harmful effects* of that specific type .
* Scanner tell about sources to know more about the . (websites).
* After this step, scanner suggests some *remdies* to o the .
Phase 3
* Scanner will Generate a proper report including
* * Total number of scanned
* * Total number of skipped
* * Total number of detected
* * Time taken for total scan
* * Details about each and every .
* Writing all scan files output into SA-Debug-ScanLog for debugging purposes under the same directory
* For Debugging Purposes, You can view the complete output generated by all the tools named SA-Debug-ScanLog.
Use
|Serial No.| to Scan| |Serial No.| to Scan|
|:----------:|:---------------------:|---|:----------:|:---------------------:|
|1|IPv6||2|Wordpress|
|3|SiteMap/Robot.txt||4|Firewall|
|5|Slowloris Denial of Service||6|HEARTBLEED|
|7|POODLE||8|OpenSSL CCS Injection|
|9|FREAK||10|Firewall|
|11|LOGJAM||12|FTP Service|
|13|STUXNET||14|Telnet Service|
|15|LOG4j||16|Stress Tests|
|17|WebDAV||18|LFI, RFI or RCE.|
|19|XSS, SQLi, BSQL||20|XSS Header not present|
|21|Shellshock Bug||22|Leaks Internal IP|
|23|HTTP PUT DEL Methods||24|MS10-070|
|25|Outdated||26|CGI Directories|
|27|Interesting Files||28|Injectable Paths|
|29|Subdomains||30|MS-SQL DB Service|
|31|ORACLE DB Service||32|MySQL DB Service|
|33|RDP Server over UDP and TCP||34|SNMP Service|
|35|Elmah||36|SMB Ports over TCP and UDP|
|37|IIS WebDAV||38|X-XSS Protection|
Installation
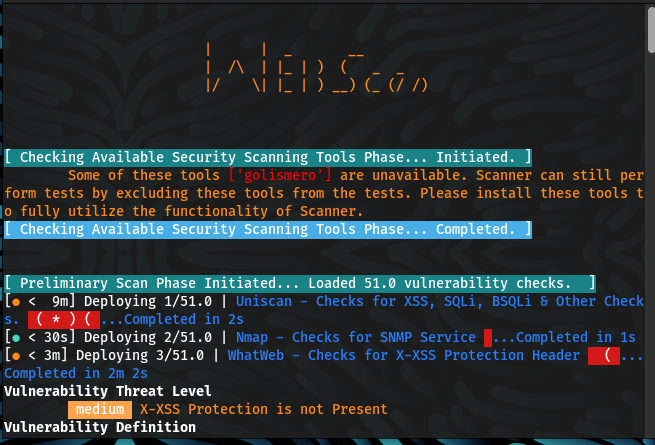
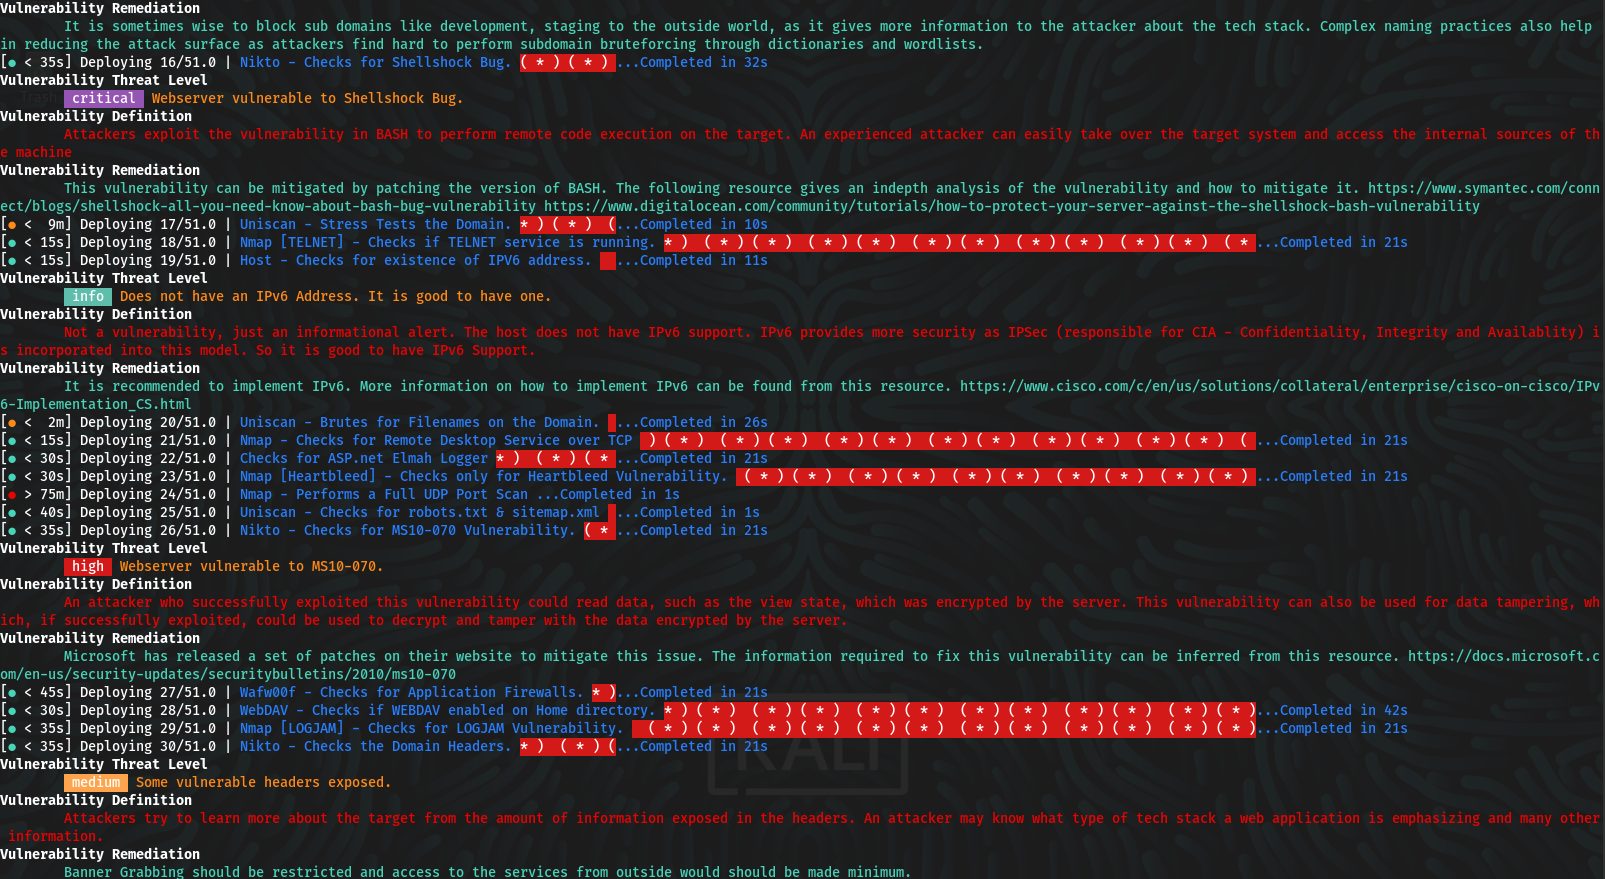
Screenshots of Scanner
!Screenshot from 2022-04-02 02-14-31
***
!Screenshot from 2022-04-02 02-26-22
***
💪 Contributions
-----
Template contributions ,
Feature Requests and
Bug Reports are more than welcome.
!Alt
👤 Authors
👤 GitHub: @Malwareman007<br>
👤 GitHub: @Riya73<br>
👤 GitHub:@nano-bot01<br>
🤝 Contributing
Contributions, issues and feature requests are welcome!<br />Feel free to check issues page.
❤ Show your support
Give a ⭐️ if this project helped you!
And by Buying me coffee.
***
项目信息
开发语言:HTML
Star 数:173
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A Web Vulnerability Scanner and Patcher 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Scanner-and-Patcher - A Web Vulnerability Scanner and Patcher |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:40:45 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 204 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |