 安全软件
点击放大
devguard - DevGuard Backend - Secure your Software Supply Cha
项目说明
<p align="center">
<a href="
<picture>
<source srcset="docs/logo_in.svg" media="(prefers-color-scheme: dark)">
<img src="docs/logo_horizontal.svg" alt="De by L3montree Logo" width="240" height="80">
</picture>
</a>
</p>
<h3 align="center">Open-source management for the full software supply chain</h3>
<p align="center">
An <a href=" Incubating Project</a> · Made in Germany 🇩🇪 for the world 🌍
</p>
<p align="center">
<a href="
·
<a href=" Demo</a>
·
<a href=" Bug</a>
·
<a href=" (Matrix)</a>
</p>
<p align="center">
<a href=" src=" alt="OpenSSF Best Practices"></a>
<a href=" src=" alt="Go Report Card"></a>
<a href="LICENSE.txt"><img src=" alt="License: AGPL-3.0"></a>
<a href=" src=" alt="Help Wanted"></a>
<a href=" src=" alt="Matrix"></a>
<a href=" src=" alt="CVSS"></a>
</p>
> [!NOTE]
> Join the monthly De Open Community Call — always at 17:00 (UTC+2) on the last thursday of the month. You can find the agenda in the Discussions. Help shape new features and discuss contributions. For support, join the community Matrix space.
---
What is De?
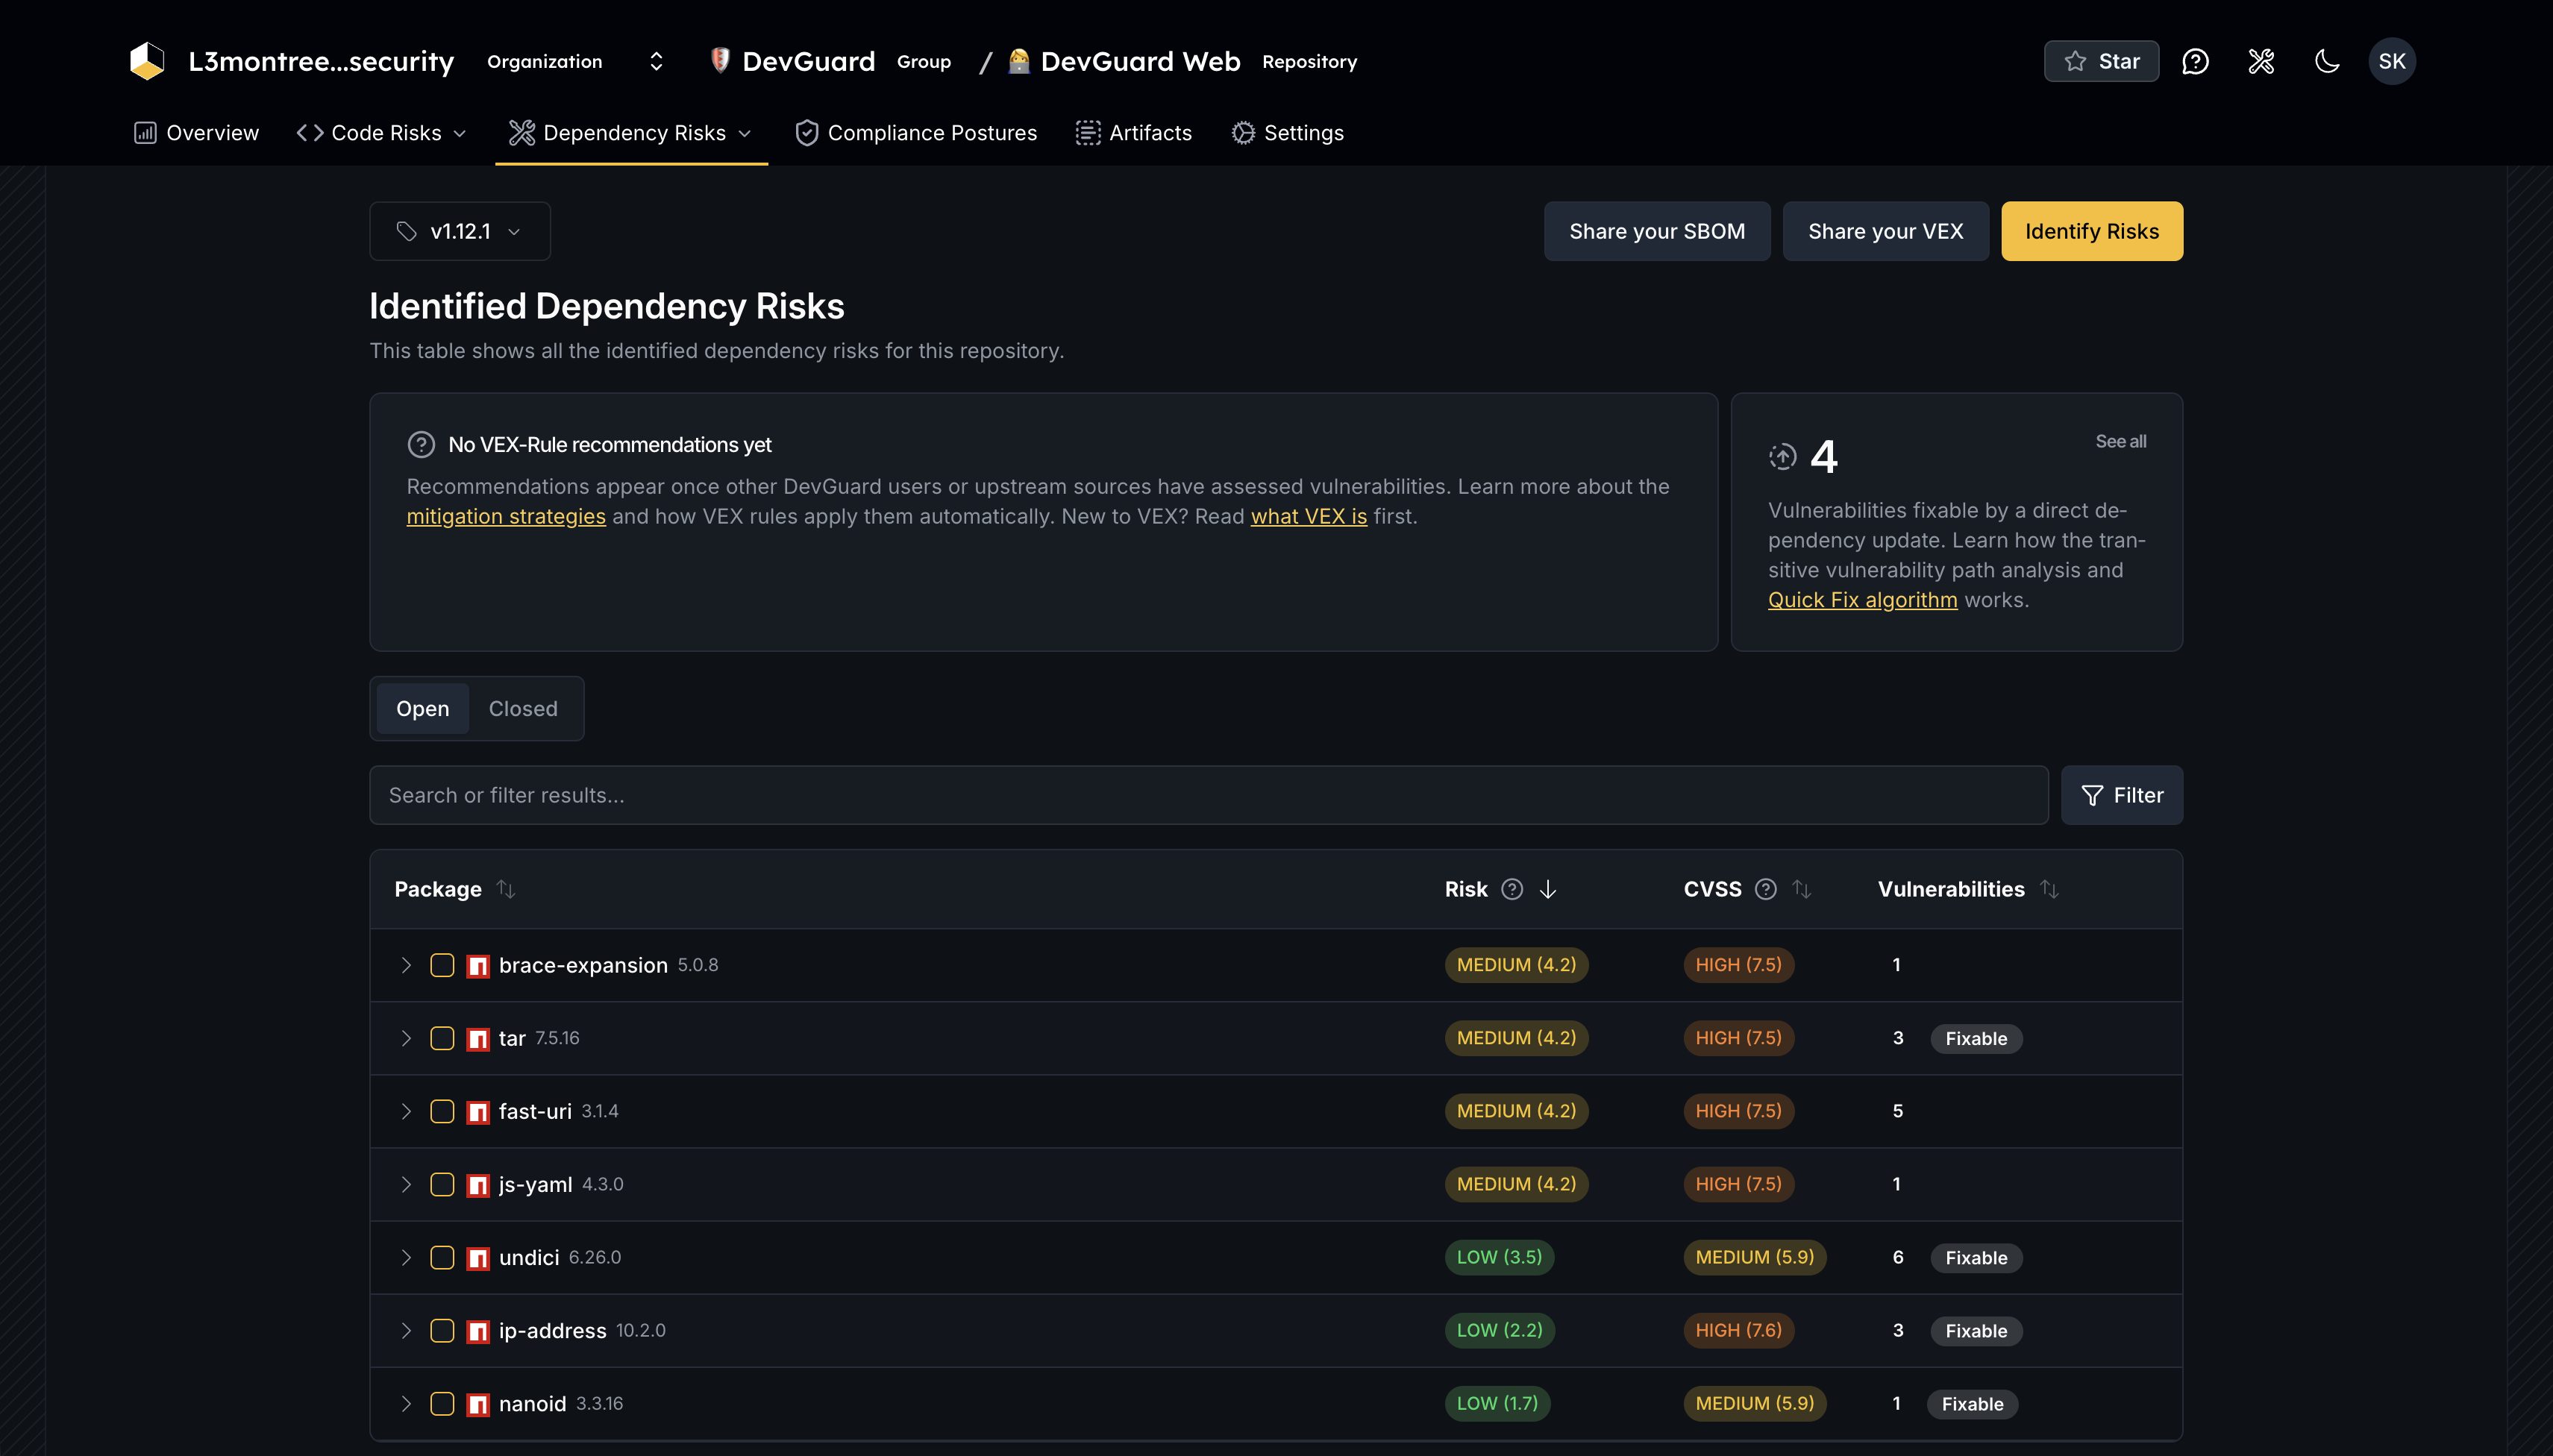
De is a single platform that finds, prioritizes, and tracks across your entire software supply chain — from source code and third-party dependencies to container images, infrastructure-as-code, and deployed artifacts.
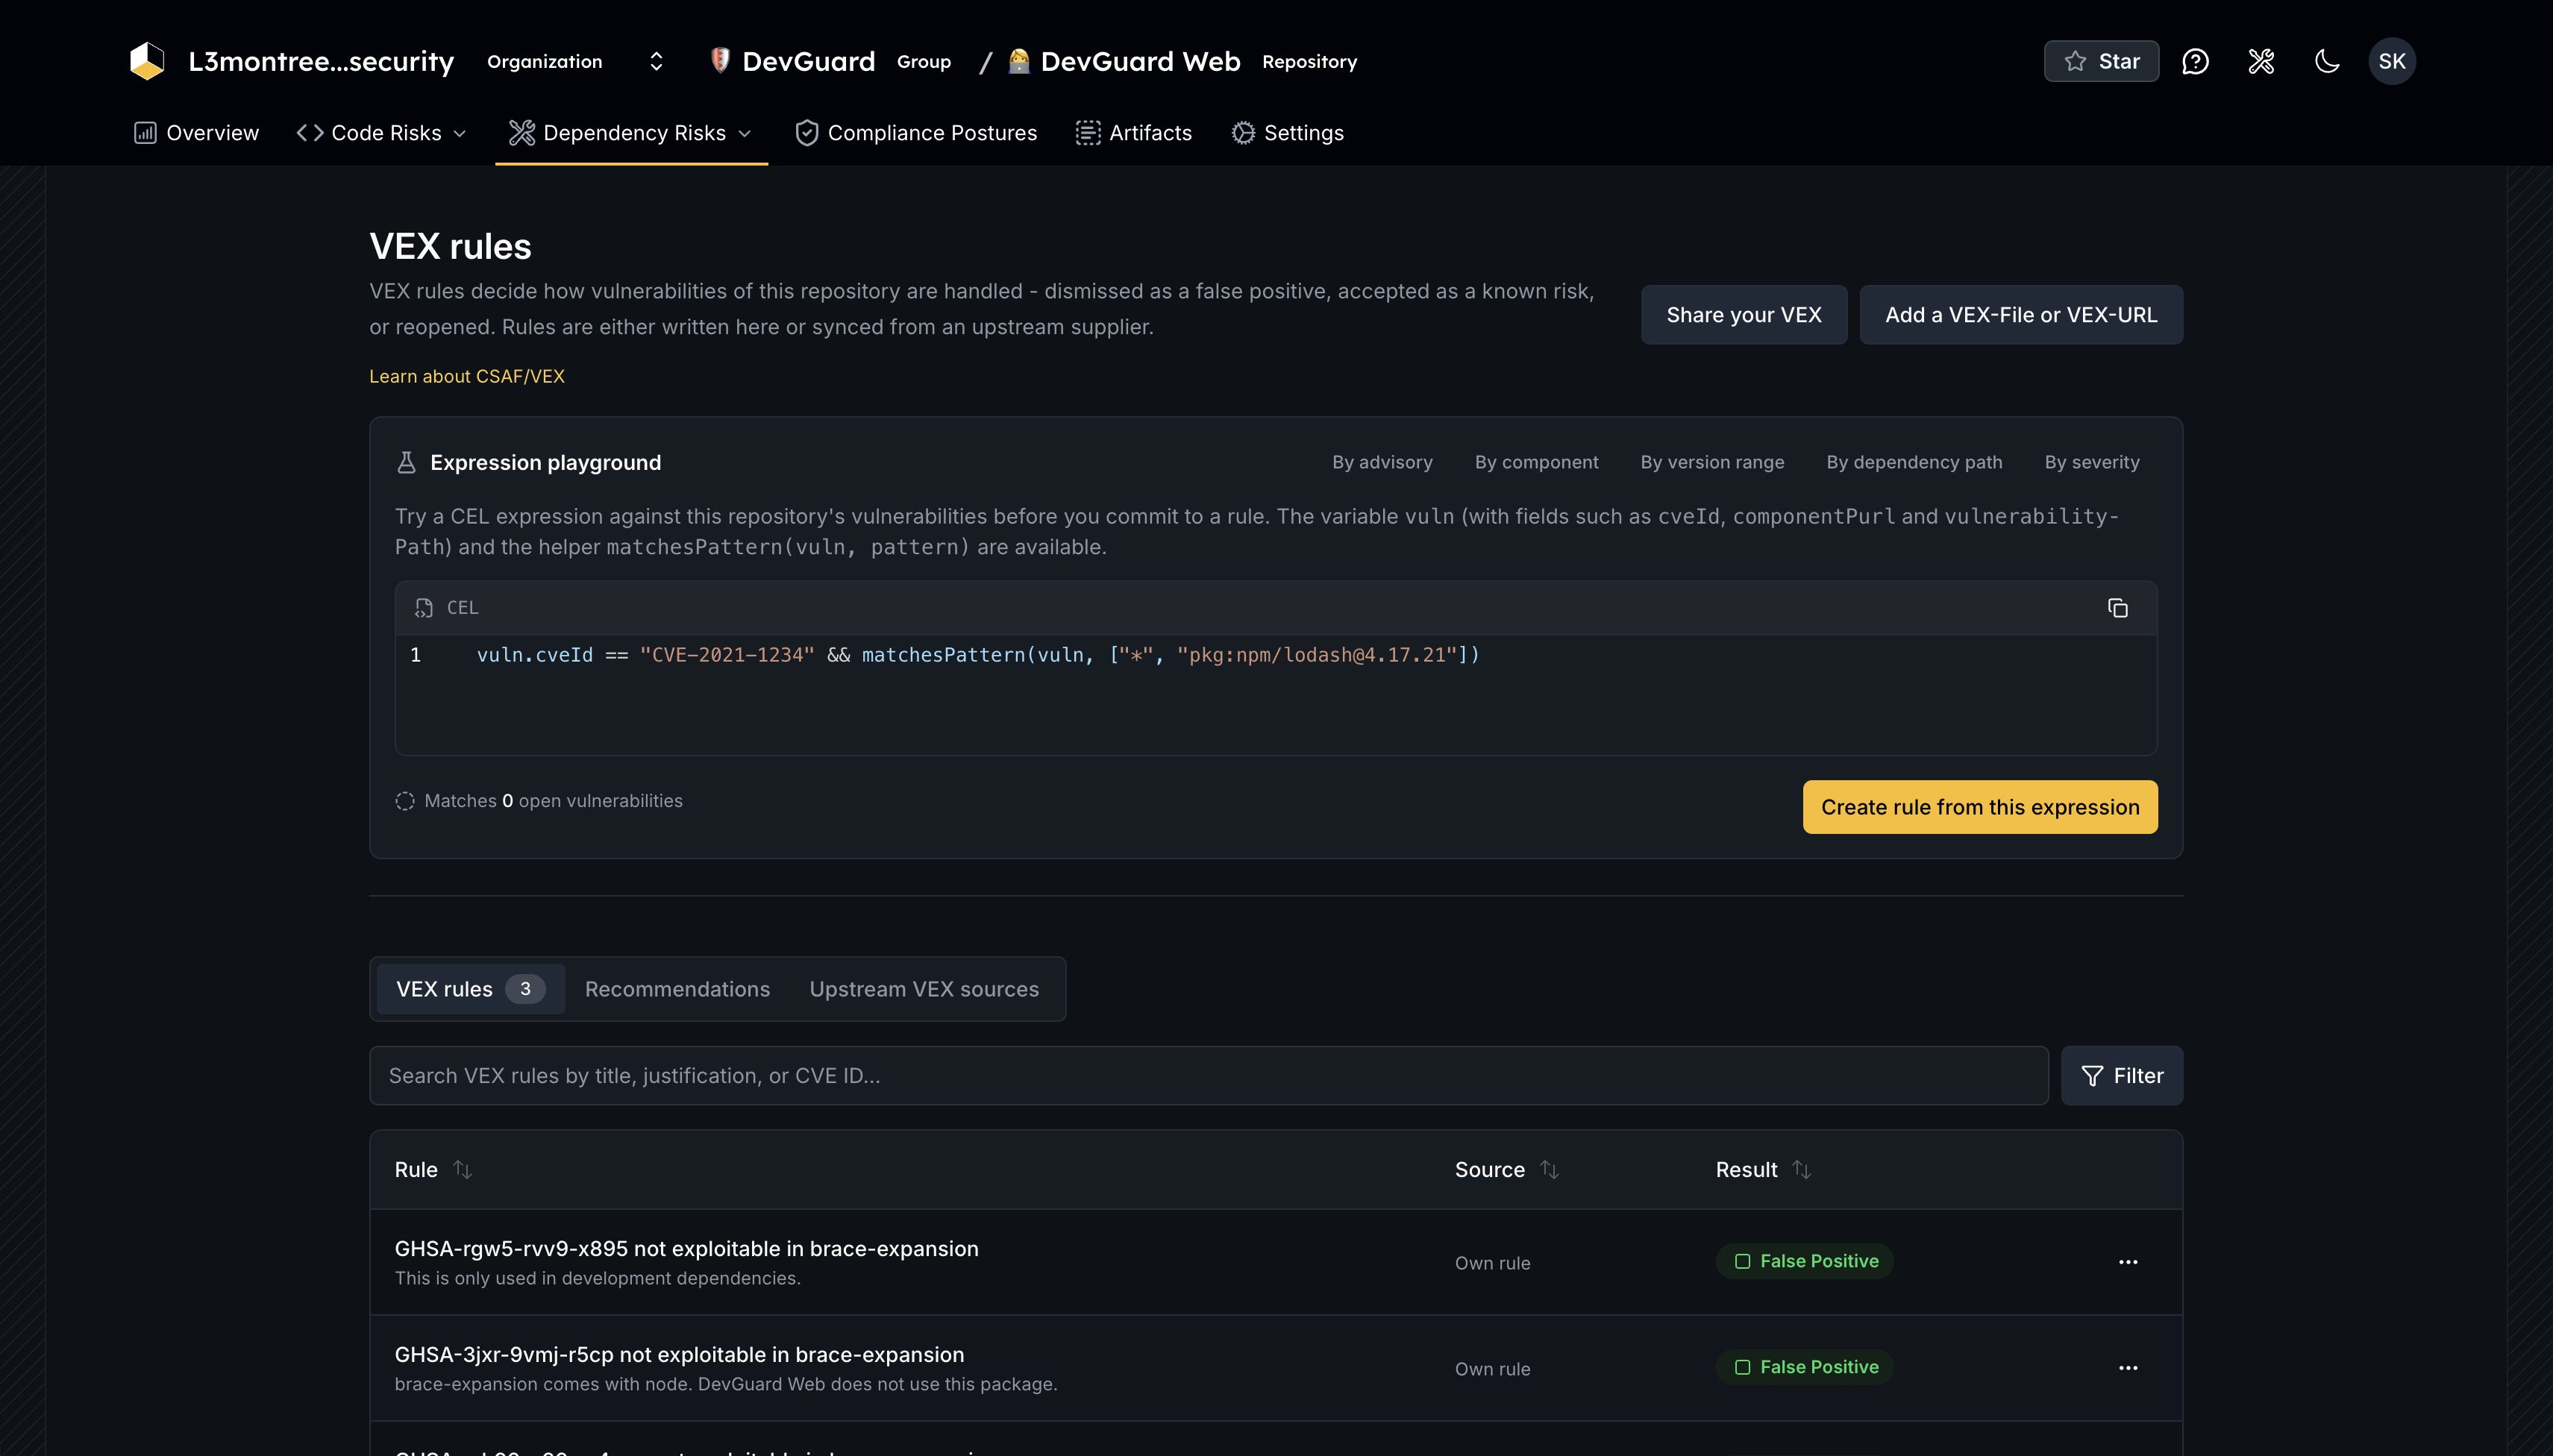
It replaces the patchwork of disconnected scanners, spreadsheets, and manual triage with one system that scans, prioritizes, tracks, and documents security findings across the whole SDLC. De is built exclusively on open standards — SBOM, VEX, SARIF, SLSA, in-toto — so there's no lock-in and no proprietary formats.
> This repository contains the De Backend (Go API + PostgreSQL). The web frontend lives at l3montree-de.

Why De?
Traditional security tools treat management as something separate from de — generating 50–80% false-positi, living in spreadsheets, and demanding context switches from engineers who just want to ship. De flips that: security intelligence is delivered where de already work (pull requests, CI, issue trackers), and real risks surface first thanks to multi-dimensional scoring.
Use De if you need to:
De is for de, DevOps engineers, and security teams. No specialized security knowledge required.

Key Capabilities
| Capability | What it does |
| --- | --- |
| Full De pipeline | Secret scanning, SAST, SCA, IaC scanning, container scanning, and license compliance — one CLI, one CI integration |
| Risk-based prioritization | Scores every finding as (C × (EPSS + 1)) / 2 / Component Depth so you fix what actually matters first |
| SBOM & | CycloneDX SBOMs, full , and live SBOM/ that always reflect current state |
| Dependency Firewall | Proxies npm, Go, and Python registries — blocks known-malicious and packages before download |
| Supply-chain integrity | in-toto attestations, SLSA pro, cosign signatures, reproducible builds with Nix |
| Policy enforcement | Organization-wide security policies written in OPA/Rego, enforced automatically |
| Bring your own scanner | Ingests SBOM (CycloneDX) and SARIF from Tri, Semgrep, and any standards-compliant tool |
| Issue tracker integration | GitHub Issues, GitLab Issues, and Jira — bidirectional sync with slash-command triage |


Getting started
The full documentation lives at docs.de.org. It covers installation, quickstart, CI/CD integration, scanner usage, and configuration.
For details on connecting to your CI, setting up the dependency firewall, or self-hosting in production, see the documentation.
Documentation
The full documentation lives at docs.de.org. Start here:
Live Demo
We scan De with De. Browse the public instance to see real data, SBOMs, and on a li:
main.de.org/l3montree-cybersecurity/projects/de
Li) SBOM and for this project:
| Component | SBOM | VEX |
| --- | --- | --- |
| Backend (this repo) | SBOM | VEX |
| Web Frontend | SBOM | VEX |
Talks & Presentations
Community & Contributing
Please follow the Code of Conduct when participating.
License
De is licensed under AGPL-3.0-or-later. See LICENSE.txt.
Sponsors & Supporters
<p align="center">
<a href=" src="docs/sponsors/sp-owasp.png" alt="OWASP" height="60"></a>
<a href=" src="docs/sponsors/sp-zendis.png" alt="ZenDiS" height="60"></a>
<a href=" src="docs/sponsors/sp-hbrs.png" alt="Bonn-Rhein-Sieg Uni of Applied Sciences" height="60"></a>
<a href=" src="docs/sponsors/sp-wg.png" alt="WhereGroup" height="60"></a>
<a href=" src="docs/sponsors/sp-wo.png" alt="WetterOnline" height="60"></a>
<a href=" src="docs/sponsors/sp-ikor.png" alt="Ikor" height="60"></a>
<a href=" src="docs/sponsors/sp-jlu.png" alt="JLU" height="60"></a>
<a href=" src="docs/sponsors/sp-saltrock.png" alt="Saltrock" height="60"></a>
<a href=" src="docs/sponsors/sp-readylabs.png" alt="Ready Labs" height="60"></a>
<a href=" src="docs/sponsors/sp-bc.png" alt="Business Code" height="60"></a>
<a href=" src="docs/sponsors/sp-cps.png" alt="CPS" height="60"></a>
<a href=" src="docs/sponsors/sp-cronn.png" alt="Cronn" height="60"></a>
<a href=" src="docs/sponsors/sp-heylogin.png" alt="HeyLogin" height="60"></a>
<a href=" src="docs/sponsors/sp-opencode.png" alt="OpenCode" height="60"></a>
<a href=" src="docs/sponsors/sp-opendesk.png" alt="OpenDesk" height="60"></a>
</p>
项目信息
开发语言:Go
Star 数:164
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕DevGuard Backend - Secure your Software Supply Chain - Attestation-based compliance as Code, manage your CVEs seamlessly, Integrate your Vulnerability Scanners, Security Framework Documentation made easy - OWASP Incubating Project展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | devguard - DevGuard Backend - Secure your Software Supply Cha |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:40:55 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 473 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |