 安全软件
点击放大
symfony-security-auditor - AI-powered multi-agent security auditor for Symfon
项目说明
Symfony Security Auditor
![CI]() ![codecov]() ![Mutation testing badge]() ![Total Downloads]() ![License: MIT]()
AI-powered, multi-agent security auditor for Symfony applications. An ad Attacker ⚔ Re loop catches the application-le SAST tools miss. Pro via symfony/ai.
!Symfony Security Auditor
> [!NOTE]
>
> main holds exactly the latest release, so e documented here is in the you install. De happens on branches.
Why this auditor?
Traditional PHP static analysis tools (PHPStan, Psalm) catch type errors. Static SAST tools (Psalm Security, Progpilot) follow taint flows but cannot reason about business logic, missing authorization, or multi-file attack chains. Dependency scanners (Dependabot, Renovate, Snyk) only flag known CVEs in third-party packages. This auditor runs alongside them, targeting the application-le flaws they cannot see.
Side-by-side comparison with PHPStan, Psalm, Progpilot, Dependabot, and Snyk: FAQ.
What it does
An ad Attacker agent hunts for ; a skeptical Re agent culls false positives over up to three iterations — then emits a report in console, JSON, SARIF, HTML, or Markdown.
🔀 Pipeline: Ingestion → Mapping → Audit (Attacker ⚔ Re) → Report.
See it in action
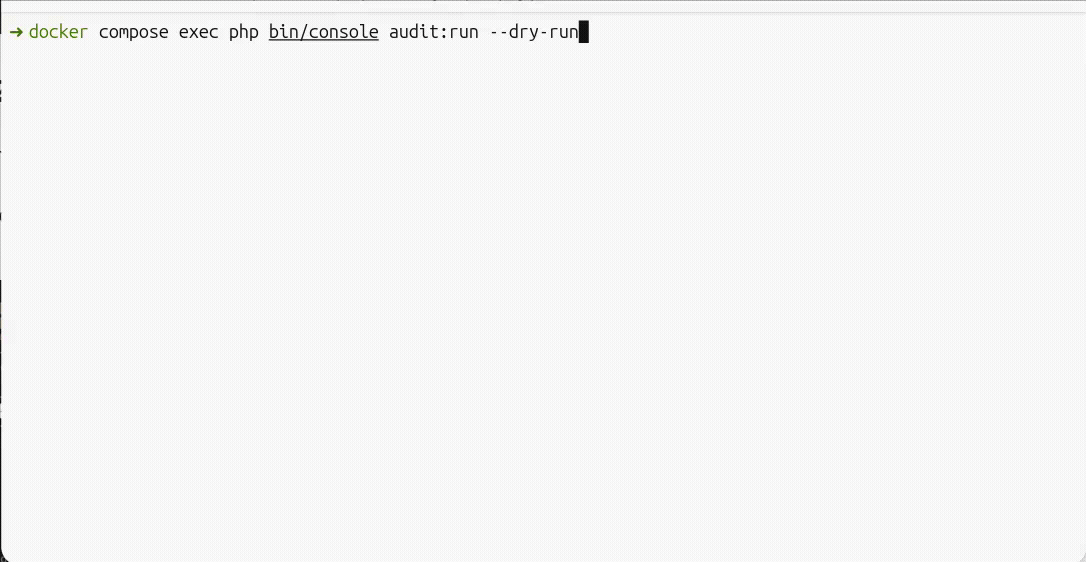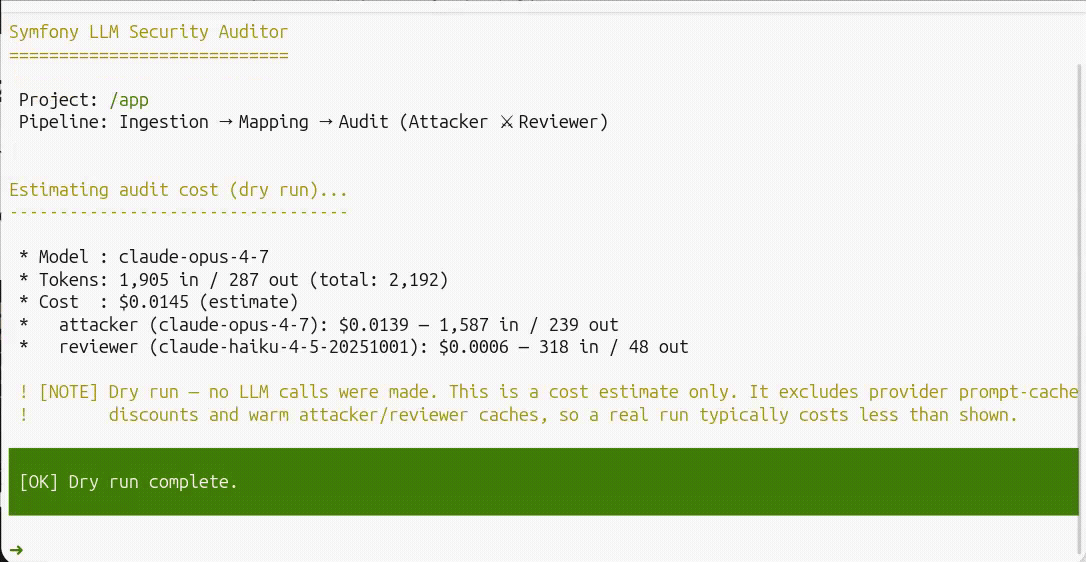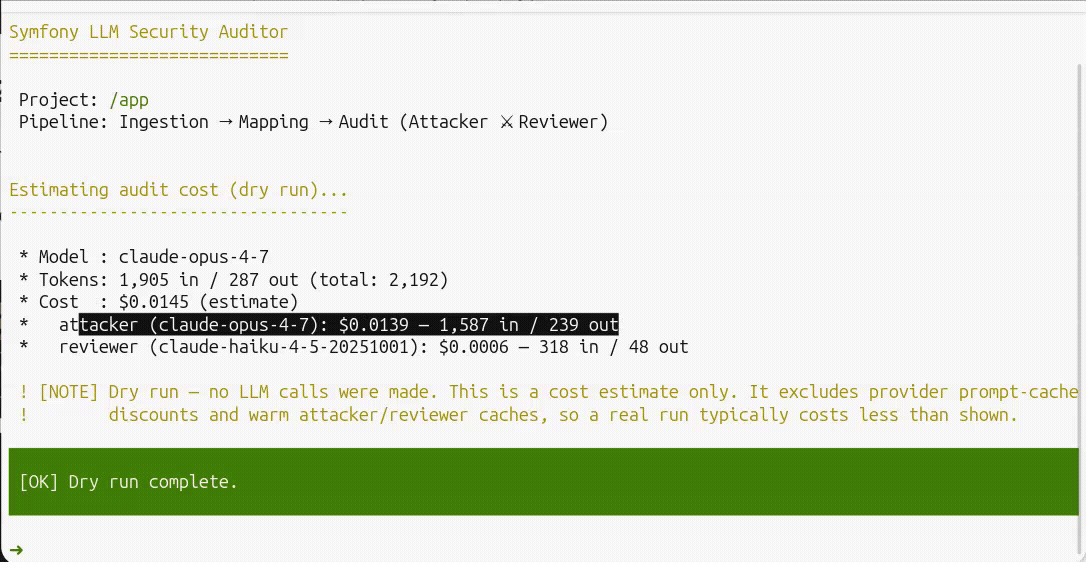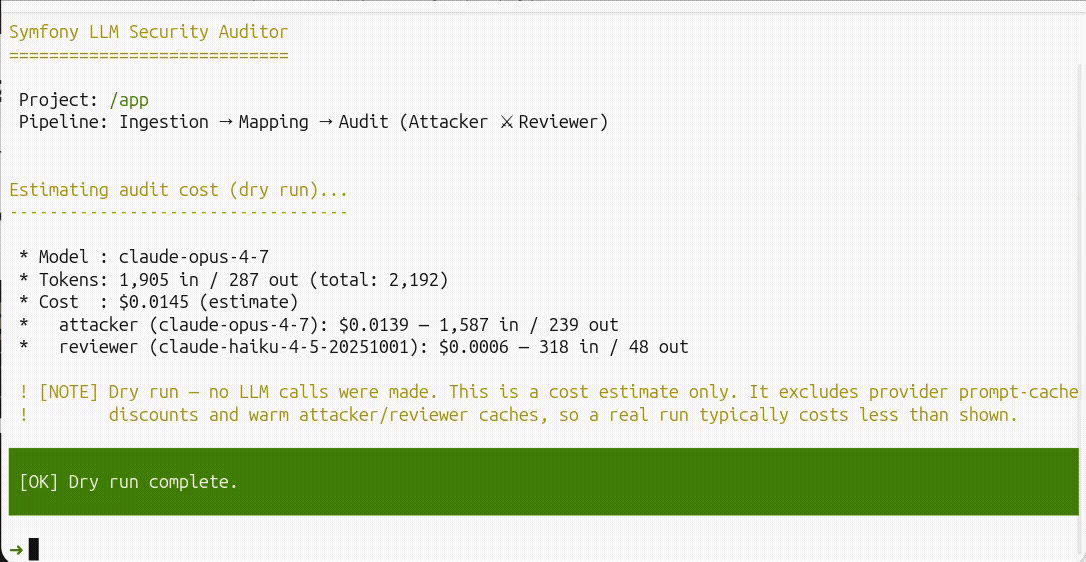
--dry-run mode
!Dry run — token and cost estimate with no LLM calls
Scans files and estimates token usage and cost without calling the LLM. Use this to gauge cost before committing to a full audit.
No LLM calls are made; exit code is always 0.
Console mode
!Li — the Attacker feed streaming to the report
While the pipeline runs, the audit narrates itself live — an attack-surface o, each finding streamed (color-coded by se in a terminal) the moment the Attacker flags it, per-chunk timing, and a re tally. In CI or any non-TTY output it degrades to clean, append-only lines (no bar, no ANSI codes). Progress is suppressed for any non-console --format to stdout and for --dry-run.
The full report renders the same way in console, JSON, SARIF, HTML, and Markdown — see CLI reference and output formats.
Getting Started
The auditor ships two maintained ways to run it — pick the one that fits:
dev dependencies.> [!TIP]
>
> Both expose the same audit command, options, and output formats — see the CLI reference — and both can serve the auditor to your AI assistant over MCP.
Standalone tool (binary)
Run the auditor like PHPStan or Psalm — one install, many projects, zero footprint in the audited app. Each release ships a self-contained nati that bundles its own PHP runtime (nothing to install on the host) for Linux, macOS, and Windows.
1. Install
One command — Linux, macOS, and Windows (under WSL):
install.sh detects your OS and CPU architecture, downloads the matching binary, and its SHA-256 checksum before installing — anywhere you have a POSIX shell.
Nati (PowerShell) — when you are not using WSL; Git Bash / MSYS / Cygwin users need this installer too (install.sh detects those shells and points here):
> [!TIP]
>
> One command, installed _and_ configured. Set SSA_INIT=1 and the installer runs the guided init for you right after downloading, so you skip step 2. With a terminal attached it prompts for your provider and offers to store your API key at the end, leaving you ready to audit; in a pipe or CI it takes the Anthropic defaults and stores no key, so export one or run auth:set before auditing. init fetches the provider bridge with composer, so composer must be a for this combined step.
>
>
Or download the binary for your platform straight from the latest release:
| Platform | Asset |
| ------------------- | --------------------------------------------- |
| Linux x86-64 | symfony-security-auditor-linux-x86_64 |
| Linux arm64 | symfony-security-auditor-linux-aarch64 |
| macOS Intel | symfony-security-auditor-macos-x86_64 |
| macOS Apple Silicon | symfony-security-auditor-macos-arm64 |
| Windows x86-64 | symfony-security-auditor-windows-x86_64.exe |
Every binary ships with a .sha256 checksum, and the install scripts abort rather than install a binary they cannot . To check a manual download yourself:
2. Configure — the guided init
Writes the config file (~/.config/symfony-security-auditor/config.yaml on Linux/macOS, %APPDATA%\symfony-security-auditor\config.yaml on Windows), downloads the provider bridge you pick, and finally asks for your API key — pasted in, ne, never in your shell history. init fetches that bridge with composer, so composer must be a for this one-time setup step; running audits afterward needs only the binary. The file is rootless (the same keys as the bundle, without the symfony_security_auditor: wrapper) plus a platform: block handed to symfony/ai. See configuration for the format and provider switching.
Press Enter at the key prompt to skip it — you can store the key any time with auth:set, or keep using an en and store nothing at all.
3. Run
audit is an alias for audit:run; every option documented in the CLI reference (--format, --output, --dry-run, --since, --fail-on, …) works identically.
Every run names the key it is about to spend, masked:
#### Managing the stored key
| Command | What it does |
| --- | --- |
| auth:set | Store or replace the key — prompts in, writes an owner-only file |
| auth:status | Show which key an audit would use, where it came from, and its SHA-256 fingerprint — never the key |
| auth:remove | Forget the stored key on this machine |
The key is kept in credentials.json next to your config, created 0600 on Linux/macOS (and inside the %APPDATA% profile directory, protected by its inherited ACL, on Windows). An audit refuses to read it if other users on the machine can, and tells you to rotate the key and chmod 600 the file.
An exported always wins, so nothing changes for Docker, Kubernetes, CI, or a per-run secret-manager prefix:
Rather not store the key at all, and no secret manager to read it from? Prompt for it per shell — read -rs keeps it off the screen, and a bare export keeps it out of ~/.bash_history:
> [!TIP]
>
> Storing nothing is a perfectly good choice. Pro the API key covers the en , a mounted secret file (%env(file:…)%), a password manager, and a CI secret store — and how they rank against the stored key.
4. Keep it up to date
self-update fetches the latest release for your platform, its checksum before replacing the binary, and swaps it in place — see the CLI reference.
Use it as a Symfony bundle
1. Install — Symfony Flex wires e
Installing the bundle requires PHP 8.3+ and Symfony 7.4+ in the host application (see composer.json) — the standalone binary has no such requirement, since it bundles its own runtime.
The official Flex recipe registers the bundle (dev/test) and drops a pre-configured config/packages/symfony_security_auditor.yaml.
Not using Flex? See Manual setup.
2. Install a platform bridge
Full list of supported pro: Configuration → Supported platforms.
3. Configure the platform
4. Adjust the auditor config
The Flex recipe already created this file — pick your model:
Optionally pick a one-knob preset — fast, balanced (default), or thorough:
A profile only fills the keys you lea — any explicitly configured key always wins. See Cost & Performance for exactly what each profile sets.
5. Run
Want JSON, SARIF, HTML, or Markdown instead? Add --format json --output report.json, --format sarif --output report.sarif, --format html --output report.html, or --format markdown --output report.md. See CLI reference.
Estimate cost before running:
> [!WARNING]
>
> Audit reports list your application's . On a public repository, CI artifacts are publicly downloadable — storing the report exposes your attack surface. Prefer GitHub Code Scanning (SARIF, restricted to collaborators), private storage (S3/GCS with IAM), or notification-only. See Report on Public Repositories.
<!-- -->
> [!TIP]
>
> Schedule the audit as a nightly CI job — the multi-agent LLM loop can take minutes, so blocking PRs on it hurts productivity. CI Integration has ready-to-copy GitHub Actions and GitLab CI schedules and a split-model config to control API costs. For dependency CVEs, pair it with Dependabot or Renovate — this auditor targets the application-le flaws those scanners cannot see.
Use it from your AI assistant (MCP)
mcp:serve starts a Model Context Protocol server, so any MCP client — Claude Code, Claude Desktop, Cursor, VS Code, Windsurf, Gemini CLI, Codex CLI, … — can audit a project on request and read back the JSON report. It works from the standalone binary and from the bundle alike:
The second snippet is the shape Claude Desktop, Cursor, Windsurf and Gemini CLI read; with the bundle, use "command": "php" and "args": ["/absolute/path/to/bin/console", "mcp:serve"].
> [!NOTE]
>
> The audit still runs on your configured provider and model, not on the assistant's, so it needs the same API key as a CLI run — with the binary, store it once with auth:set so a desktop client finds it. Point the auditor at a local Ollama and it needs no key at all. Setup for every client, including VS Code and Codex CLI: mcp:serve.
Features
#[IsGranted], denyAccessUnlessGranted, #[MapRequestPayload], Twig/Li, and surfaces controllers without proper access checks.|raw, hardcoded secrets, unsafe Doctrine, …) to focus the LLM; optional lean mode drops marker-free files to cut tokens. Results from other SAST tools can be imported as markers .audit:run --since=main audits only changed files for fast pull-request CI.read_file, grep, list_files, and lookup_ad (zero-config live C via composer audit, backed by Packagist + GitHub Security Ad).fast, balanced, and thorough preset the cost/speed/depth levers in a single line; any explicit key still wins.attacker_max_concurrent / re), Anthropic prompt caching on by default (~90% input-token discount), content-hash caching that skips identical chunks, cheap→expensi, and code slicing.privacy.offline_only refuses every network call the auditor owns (see Security by design).Retry-After-aware exponential backoff plus an optional proacti limiter keep you inside provider quotas (see Cost & Performance).console, executive (stakeholder summary: risk level, business impact, se/type/hotspot distributions, no per-finding detail), json, sarif (GitHub Code Scanning / GitLab Security Dashboard), html (self-contained, shareable), markdown (PR-friendly), junit (CI test-report panels), github (inline PR annotations, no SARIF upload step), and github-comment (PR comment headlined by the grade and score, self-updating on rerun). Baseline suppression: --generate-baseline accepts known findings, --baseline drops them from the report and exit code so only new findings fail CI; --min-score gates on the normalized score independently of --fail-on.mcp:serve exposes the audit as an MCP tool to Claude Code, Claude Desktop, Cursor, VS Code and any other MCP client, from the binary or the bundle (see Use it from your AI assistant).audit:diff compares two JSON reports by finding fingerprint, audit:trend tracks counts across a series of them.uses: /symfony-security-auditor@1.21.0) plus GitLab CI templates, with SARIF upload to Code Scanning and an optional shields.io badge tracking the report's letter grade. See CI Integration.LLMClientInterface seam let you plug in custom pro, agents, stages, ad feeds, or report formats; project-specific attacker skills need only configuration, no PHP.self-update and preflighted with doctor (see Standalone tool).Security by design
The auditor is conser about what leaves your machine:
scan.secret_scrubbing.enabled: true (the default), credential-shaped strings are redacted from file content _before_ it reaches the LLM: AWS / GitHub / Stripe / Slack / Google API keys, JWTs, PEM private keys, en credential assignments, and connection-string URIs with embedded credentials (postgres://user:pass). Add project-specific shapes with scan.secret_scrubbing.additional_patterns.cache.dir.ai.yaml. For zero third-party exposure, run fully offline with Ollama — nothing leaves your network. Set privacy.offline_only: true to have that enforced rather than assumed: the ad feed is dropped (no composer audit) and the standalone CLI refuses to boot against a platform endpoint that is not loopback or pri. docs/faq.md carries a tcpdump recipe for it yourself.Tuning & cost
Profiles (fast / balanced / thorough), split-model, concurrency, caching, budget caps, and 429 rate-limit handling are covered in Cost & Performance — start with a profile, then o indi keys as needed.
Supported Platforms
| Platform | Bridge package | Key env var(s) |
| --- | --- | --- |
| Anthropic (Claude) | symfony/ai-anthropic-platform | ANTHROPIC_API_KEY |
| OpenAI | symfony/ai-open-ai-platform | OPENAI_API_KEY |
| OpenAI Responses API | symfony/ai-open-responses-platform | OPENAI_API_KEY plus a base_url |
| Azure OpenAI | symfony/ai-azure-platform | AZURE_OPENAI_API_KEY, AZURE_OPENAI_BASEURL |
| Google Gemini | symfony/ai-gemini-platform | GEMINI_API_KEY |
| Google AI | symfony/ai- | GCP credentials |
| AWS Bedrock | symfony/ai-bedrock-platform | BEDROCK_API_KEY, or AWS credentials |
| DeepSeek | symfony/ai-deep-seek-platform | DEEPSEEK_API_KEY |
| Mistral | symfony/ai-mistral-platform | MISTRAL_API_KEY |
| MiniMax | symfony/ai-mini-max-platform | MINIMAX_API_KEY |
| Ollama (local) | symfony/ai-ollama-platform | _(none)_ |
| Albert (French gov) | symfony/ai-albert-platform | ALBERT_API_KEY plus a base_url |
| amazee.ai | symfony/ai-amazee-ai-platform | AMAZEEAI_API_KEY plus a base_url |
| Fireworks AI | symfony/ai-fireworks-platform | FIREWORKS_API_KEY |
| Together AI | symfony/ai-together-platform | TOGETHER_API_KEY |
| AI | symfony/ai- | |
| Eden AI | symfony/ai-eden-ai-platform | EDENAI_API_KEY |
| Generic (AI gateway) | symfony/ai-generic-platform | depends on the gateway |
Swapping pro requires only a config/packages/ai.yaml change — no PHP edits.
Any OpenAI-compatible endpoint behind a custom URL and token (an in-house AI gateway, LiteLLM, vLLM, LocalAI) goes through the generic platform. It is configured per instance, so the instance name is part of the platform block and, in standalone mode, part of provider: as well:
See Configuration → Instance-keyed platforms.
Documentation
FAQ
How much does an audit cost? Depends on project size and model. A medium Symfony app (~150 files) on Claude Opus + Haiku split-model with prompt caching enabled costs roughly $0.50 per nightly run. See CI → Managing LLM Costs.
Does it send my code to the cloud? Only to the LLM provider you configure, and credential-shaped strings are scrubbed first (see Security by design). For zero-cloud operation, use the Ollama local platform.
Full FAQ — privacy, false positives, model picks, comparisons: docs/faq.md.
Contributing
Contributions welcome, please refer to CONTRIBUTING.md.
Security
Found a in the auditor itself? Do not open a public issue. Report pri via GitHub Security Ad.
See SECURITY.md.
License
MIT — Copyright © Amstoutz
项目信息
开发语言:PHP
Star 数:95
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-powered multi-agent security auditor for Symfony applications — provider-agnostic via symfony/ai.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | symfony-security-auditor - AI-powered multi-agent security auditor for Symfon |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:42:53 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 161 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |