 安全软件
点击放大
cloud-audit - Fast, opinionated AWS security scanner. Curated ch
项目说明
<p align="center">
<img src="assets/logo-nobg.png" alt="cloud-audit logo" width="200">
</p>
<!-- mcp-name: io.github.gebalamariusz/cloud-audit -->
<h1 align="center">cloud-audit</h1>
<p align="center">
<a href="README.md">English</a> | <a href="README_zh-CN.md">简体中文</a>
</p>
<p align="center">
<strong>What can a hijacked AI agent reach in your AWS account, and can you prove it?</strong>
</p>
<p align="center">
Open-source, read-only AWS security scanner. 110 checks, 64 IAM pri methods, 31 attack-chain
rules, blast radius for any resource, and <code>agent-blast</code> for Bedrock Agents and AgentCore:
what a prompt-injected or credential-stolen agent can reach, with the IAM policy simulator as the witness.
Every finding ships an <strong>AWS CLI + Terraform fix</strong>. Nothing is written to your account.
</p>
<p align="center">
<a href=" src=" alt="PyPI "></a>
<a href=" src=" alt="Python "></a>
<a href=" src=" alt="CI"></a>
<a href=" src=" alt="License: MIT"></a>
<a href=" src=" alt="Docker"></a>
<a href=" src=" alt="Documentation"></a>
</p>
<p align="center">
<a href="#thirty-seconds-no-aws-account-needed">30-second demo</a> -
<a href="#agent-blast-what-a-hijacked-ai-agent-can-reach">agent-blast</a> -
<a href="#a-full-scan">Full scan</a> -
<a href="#whats-inside">What's inside</a> -
<a href="#proof-mode-simulated-not-guessed">Proof Mode</a> -
<a href="#installation">Installation</a> -
<a href="
</p>
Thirty seconds, no AWS account needed
The sample account is in. E derived from it (attack chains, root causes, breach cost,
security graph, agent reach) is produced by the same engines a real scan uses.
With credentials, the real thing is one command and read-only. The AWS-managed SecurityAudit
policy covers every check (permissions):
agent-blast: what a hijacked AI agent can reach
An AI agent in AWS is a bundle of IAM identities: the role the agent runs as, the execution roles of
the Lambda functions behind its tools, the roles of its knowledge bases, gateways and sandboxes.
When the agent is hijacked, the attacker acts with *those* identities. agent-blast answers what
that means, per agent, under two threat models:
| Threat model | What the attacker has | What is in reach |
|---|---|---|
| Identity takeover | the credentials of a role the agent runs as (sandbox escape, metadata-service read, leaked session) | the full role: pri methods, AssumeRole hops, data |
| Behaviour takeover | nothing but a prompt (indirect prompt injection through a document, a ticket, a web page) | what the agent's tools can do, bounded by the tools' own execution roles |
Real output for the sample agent (cloud-audit agent-blast --demo -a support-bot):
The story the output tells: the support bot itself is harmless, but a document that tricks it into
calling create-ticket runs code under a role that can pass an admin role to a new Lambda. Thesearch-docs tool, meant to read product docs, can also read the production database secret and
write into the backups bucket. Every line names the identity, the action and the resource, so the
fix is a policy statement, not a debate.
The same engine covers AgentCore. For the sample gateway (--demo -a tools-gw) the headline is a
cross-agent one:
What agent-blast reads (all list/get, no charge):
DRAFT resolved toits Lambda and the Lambda's execution role, knowledge bases resolved to their S3 data-source buckets.
target (Lambda, remote MCP server, API Gateway, OpenAPI, Smithy) with its credential provider,
code interpreter and browser execution roles.
effect, whether a
Condition is present. Conditions are flagged, ne. The simulatordecides.
Then, per identity: the 64 pri methods, AssumeRole hops through the trust graph,
and every data, secret, lateral, code-execution and model-in grant matched against concrete
resources. A knowledge-base bucket is always a concrete target, e s3:* on *, and
write access to it is reported as RAG poisoning. Anything the scanner could not read (a denied
region, a tool without an IAM identity) is a co note, never a silent pass.
-- asks iam:SimulatePrincipalPolicy about every concrete pair, with the context an attacker
really has (no MFA on the session, TLS transport), and marks each reach PROVEN, DENIED (with the
policy layer that denied: SCP, permissions boundary) or not asserted. Output formats: tree,json, markdown. The MCP ser the same report as get_agent_blast.
A full scan
cloud-audit scan runs 110 read-only checks across 25 AWS services, correlates the findings into
attack chains, ranks the fixes by how many chains they break and prices the exposure. This is the
sample account (cloud-audit demo), rendered by the same code as a real scan and trimmed for length:
Preview a fix before touching anything. simulate removes the findings a check would fix and
recomputes score, chains and exposure offline:
Walk outward from any resource to see what its compromise reaches:
--format json drops straight into the open browser at
blast-audit.haitmg.pl; --format mermaid gives a diagram for a
wiki page. exposure ranks every node of the security graph by internet reachability and escalation:
<p align="center">
<a href="
<img src="assets/blast-audit-boardroom.png" alt="blast-audit - executi view" width="760">
</a>
<br>
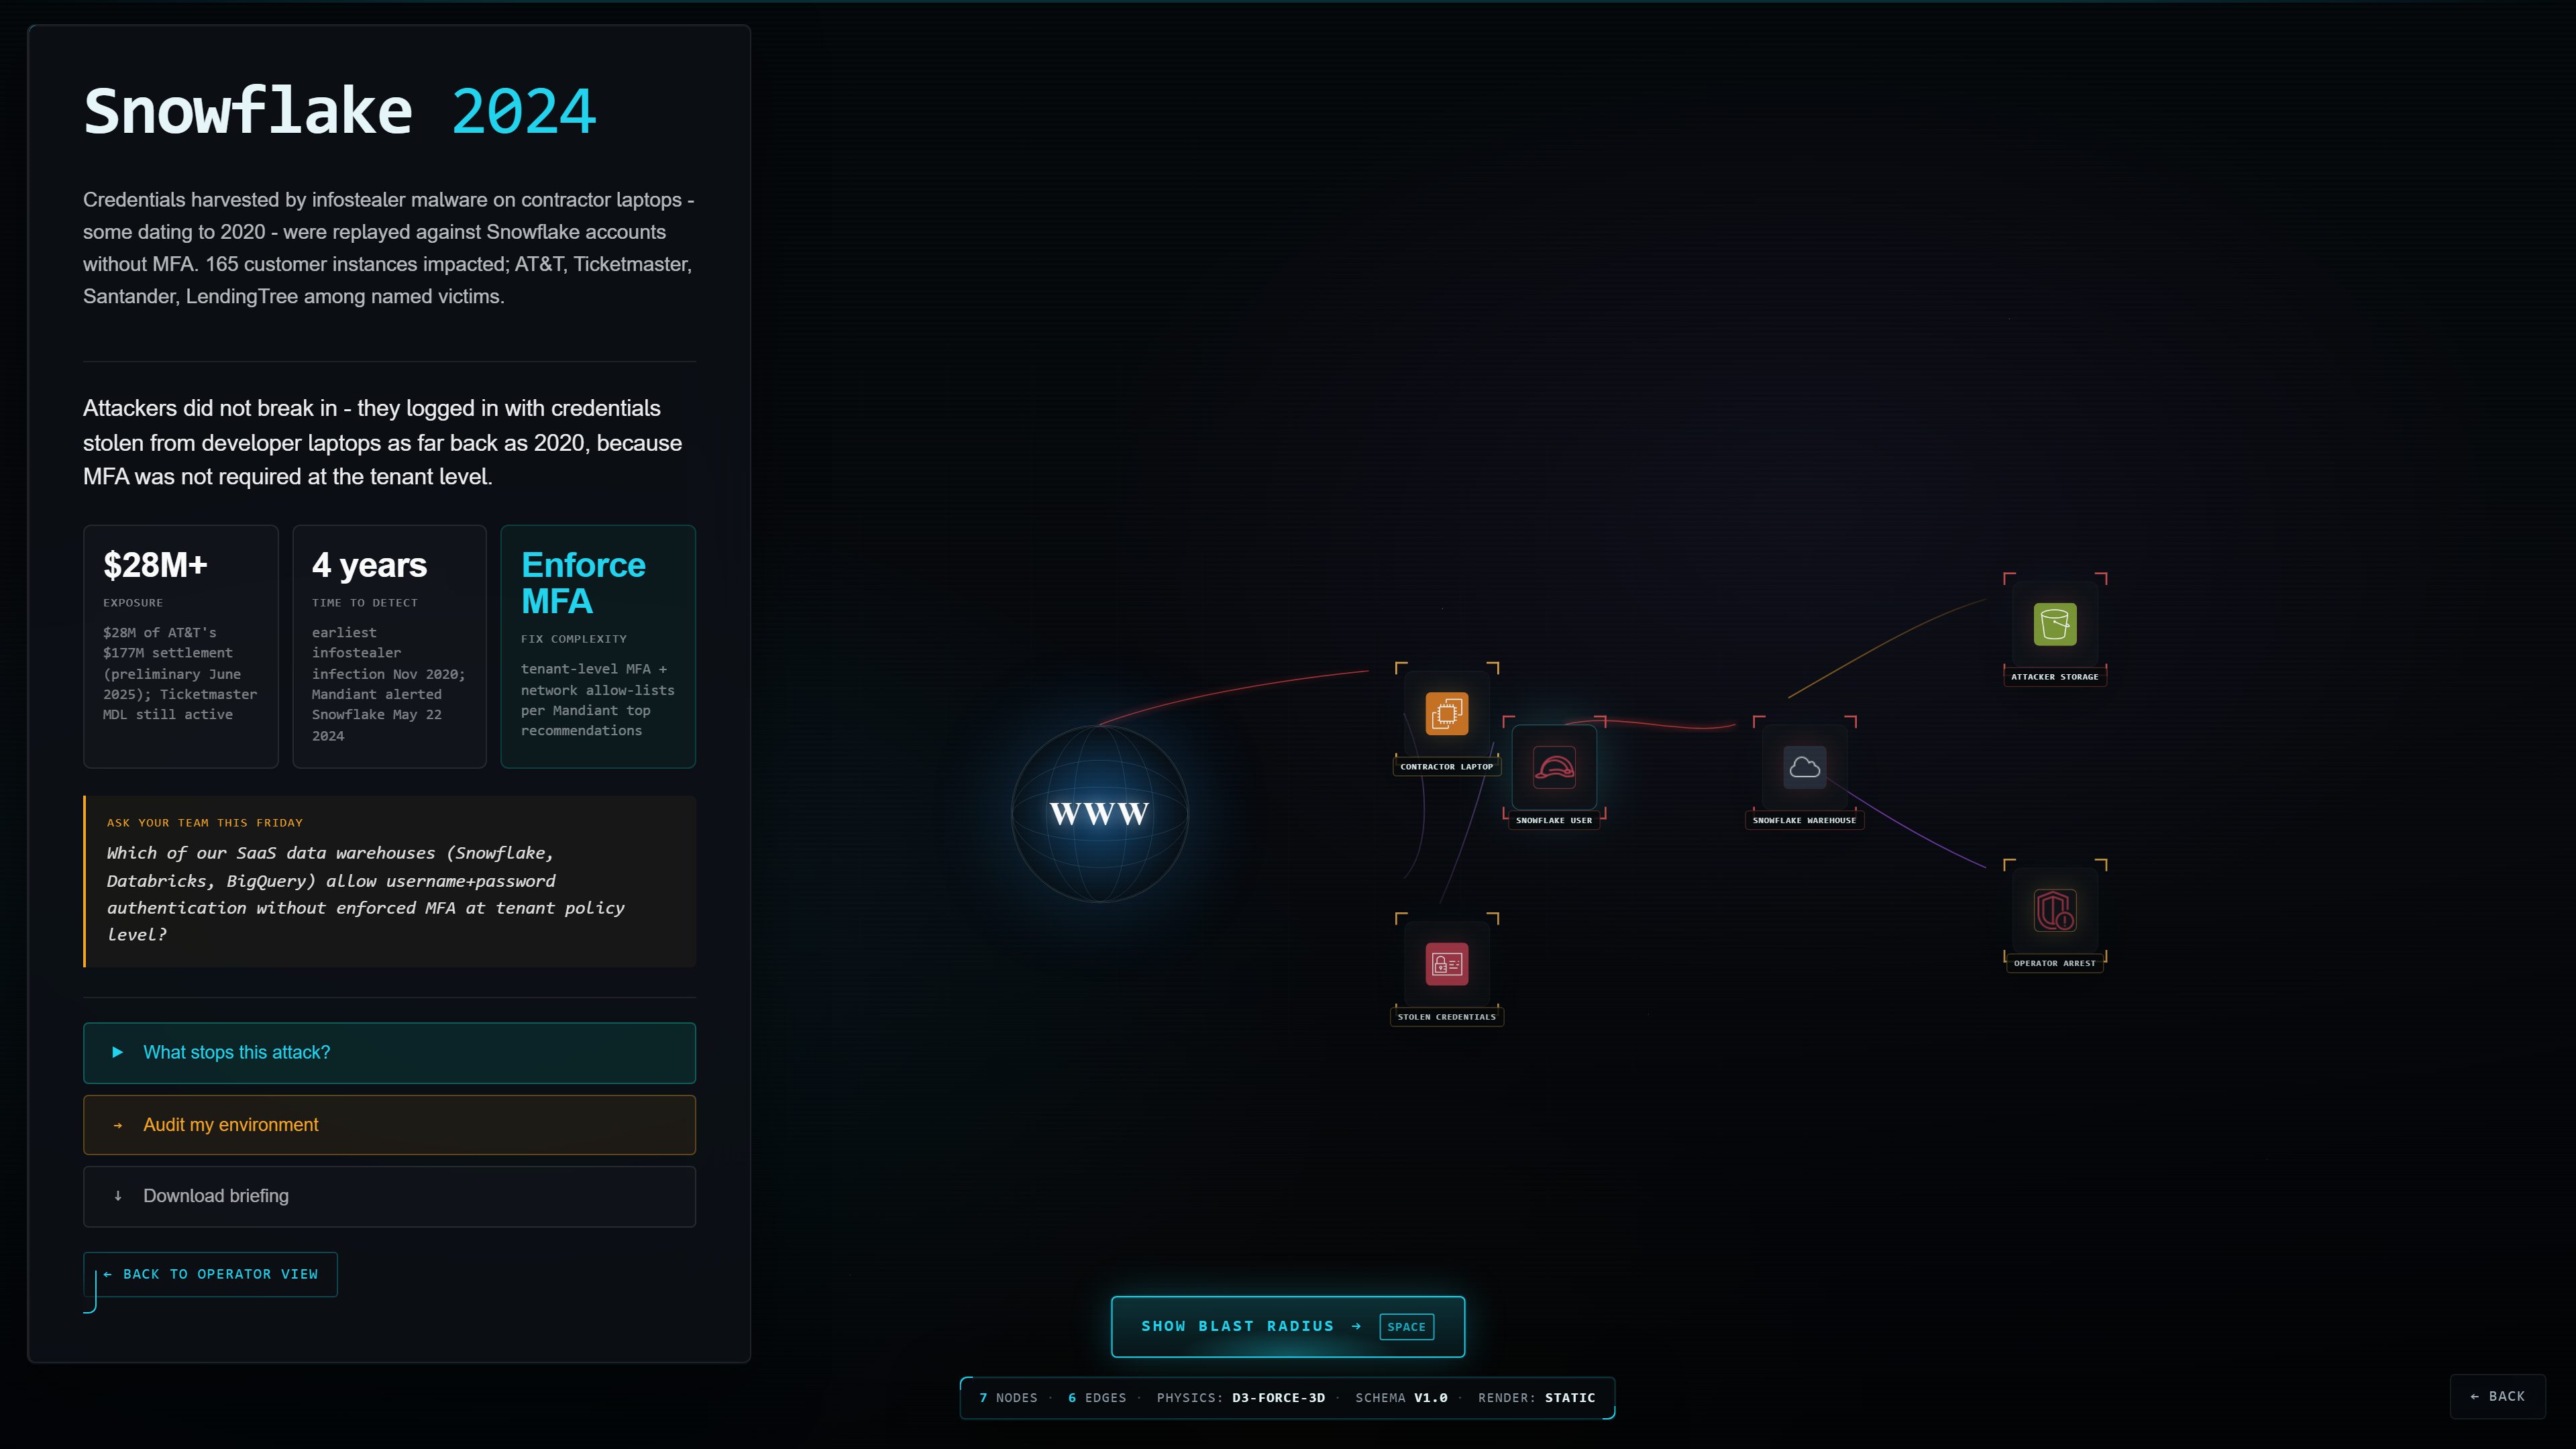
<sub>The runs entirely in your browser on a <code>blast-radius --format json</code> export.</sub>
</p>
What's inside
| Capability | Size | Command |
|---|---|---|
| Configuration checks, each with an AWS CLI and Terraform fix | 110 checks, 25 services: IAM, S3, EC2, VPC, RDS, KMS, CloudTrail, CloudWatch, GuardDuty, Config, Lambda, ECS, EFS, SSM, Secrets Manager, DynamoDB, Backup, Inspector, Security Hub, WAF, Bedrock, SageMaker, Bedrock AgentCore, Data Perimeter, account | scan, list-checks |
| IAM pri escalation | 64 methods in 9 categories: IAM self-mutation, credential access, PassRole to a service, Lambda code modification, trust-policy abuse, permission-boundary bypass, resource-policy abuse, compute hijack, lateral AssumeRole (BFS over the trust graph) | scan (aws-iam-018) |
| Attack chains | 31 rules correlating findings and li (EC2 to role, Lambda to role, OIDC to policy) into paths with MITRE ATT&CK references and a priority fix | scan |
| Root causes and quick wins | groups findings by the fix that removes them and ranks by chains broken | scan |
| What-If | before/after score, chains and exposure for any set of checks, offline | simulate --fix |
| Blast radius | forward BFS from an EC2 instance, IAM role or user, Lambda, S3 bucket or secret; JSON contract for the | blast-radius |
| Exposure ranking | every security-graph node scored by internet reachability and escalation | exposure |
| AI agents | in of Bedrock Agents and AgentCore runtimes, gateways, code interpreters, browsers with their IAM identities and tools; two-threat-model reach; OWASP Agentic and MITRE ATLAS tags; simulator proof | agent-blast |
| Proof Mode | iam:SimulatePrincipalPolicy on escalation paths (broad) and on concrete (principal, action, resource) triples (agent-blast) | scan --, agent-blast -- |
| Threat feed | 10 detectors of acti, each tied to a documented 2025-2026 incident pattern, as a rules pack | threat-feed |
| Data perimeter | 5 checks on resource policies: confused deputy and cross-organization exposure, e condition | scan (aws-dp-*) |
| AgentCore configuration | 6 checks: code interpreter and runtime network mode, MMDSv2, memory KMS, gateway authorizer, gateway policy engine | scan (aws-agc-*) |
| Breach cost | USD range per finding and per chain with the public source behind each number | scan |
| Compliance | 6 frameworks with per-control e: CIS AWS v3.0, SOC 2 Type II, ISO 27001:2022, HIPAA, NIS2, BSI C5:2020 | scan --compliance, list-frameworks |
| Drift and trend | diff two scans with exit codes; posture history with sparklines | diff, trend |
| Co gaps | a read the scanner was denied is reported as "not assessed", never as a pass | every command |
| Outputs | console, JSON, HTML report, SARIF (GitHub Code Scanning), Markdown | scan --format |
| MCP server | 7 read-only tools for Claude Code, Cursor and any MCP client, including get_agent_blast | cloud-audit-mcp |
The ten threat-feed detectors, as cloud-audit threat-feed --list prints them (rules pack 2026-Q2):
| Pattern | Se | What it catches |
|---|---|---|
| TF-001 | MEDIUM | SES recently identity (phishing setup precursor) |
| TF-002 | HIGH | Public Lambda Function URL (AuthType=NONE) |
| TF-003 | CRITICAL | AWS-attached credential quarantine policy |
| TF-004 | CRITICAL | Leaked-credentials scanner user-agent observed in CloudTrail |
| TF-005 | HIGH | Recently-created IAM role with cryptomining-style compute access |
| TF-006 | HIGH | EC2 or AgentCore using IMDSv1 / MMDSv1 (SSRF credential theft ) |
| TF-007 | MEDIUM | CI/CD role at risk of whoAMI confusion attack |
| TF-008 | HIGH | CloudTrail tampering precursor (logging stopped or delivery failing) |
| TF-009 | HIGH | IAM Roles Anywhere trust anchor with external CA |
| TF-010 | HIGH | AmazonDataZoneFullAccess attached to a non-admin principal |
Proof Mode: simulated, not guessed
Static analysis of IAM policies o. Proof Mode asks AWS's own authorization engine,iam:SimulatePrincipalPolicy, which is read-only and carries no per-call charge.
scan -- checks every detected escalation path. : true means the simulator allowedevery required action;
false means it denied one (the path is very likely a false positive);null means not asserted, with the reason in agent-blast -- checks every concrete (principal, action, resource) reach, supplies thecontext an attacker with stolen or assumed credentials has, and names the layer that denied.
What the simulator e as of 2026-07-30: identity policies, the attached permissions boundary,
the organization's SCPs including their condition keys, and the context keys you supply. What it does
not: resource control policies, policies, role chaining, and resource-based policies for
IAM roles. cloud-audit says so on every line. A true proves the permission exists. It does
not prove an end-to-end attack; nothing is executed.
Reports
CI/CD
--quiet exits with a code only: 0 clean, 1 findings, 2 error. Gate on se with--min-se high. cloud-audit diff old.json new.json --quiet exits 1 on new findings, so a
daily scan catches ClickOps drift. The repository is also a composite GitHub Action
(gebalamariusz/cloud-audit@v0). Ready-made workflows: basic scan,
daily diff, post-deploy.
Installation
Docker with credentials:
Python 3.10 to 3.13. Dependencies: boto3, typer, rich, pydantic, jinja2, pyyaml, mcp.
AWS permissions
Read-only. Attach the AWS-managed SecurityAudit policy; it covers every check, the IAM escalation
analysis, the agent in and Proof Mode:
cloud-audit ne your infrastructure. simulate, blast-radius, exposure, diff,trend and agent-blast run locally against a saved scan and make no AWS calls; -- adds
simulator calls only. Regions where a service does not exist are skipped; regions where the scanner
is denied a read are listed as co gaps.
MCP server
Se tools for AI assistants: scan_aws, get_findings, get_attack_chains,get_remediation, get_health_score, list_checks, get_agent_blast.
Then ask: *"scan my AWS account and tell me what my Bedrock agents could reach if hijacked"*.
<details>
<summary>Common flags and configuration</summary>
Defaults live in .cloud-audit.yml (regions, min_se, exclude_checks, time-boxedsuppressions). En (CLOUD_AUDIT_REGIONS, CLOUD_AUDIT_MIN_SE, ...)
o the file; CLI flags o e. See the
configuration guide.
</details>
Documentation
Full documentation at haitmg.pl/cloud-audit:
getting started,
agent-blast,
attack chains,
IAM escalation,
blast radius,
Proof Mode,
threat feed,
data perimeter,
AgentCore,
compliance, and the
full check reference.
Commercial support
cloud-audit is free and stays free. If you want a human on the findings, the author offers
professional services:
Details: haitmg.pl/cloud-audit-support
or email .
De
See CONTRIBUTING.md to add a check. Releases in CHANGELOG.md.
License
MIT - Mariusz Gebala / HAIT
项目信息
开发语言:Python
Star 数:72
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Fast, opinionated AWS security scanner. Curated checks. Zero noise. Copy-paste fixes.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | cloud-audit - Fast, opinionated AWS security scanner. Curated ch |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:43:47 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 397 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |