 安全软件
点击放大
goLoL - goLoL is a Windows host scanner with dual support
项目说明
goLoL
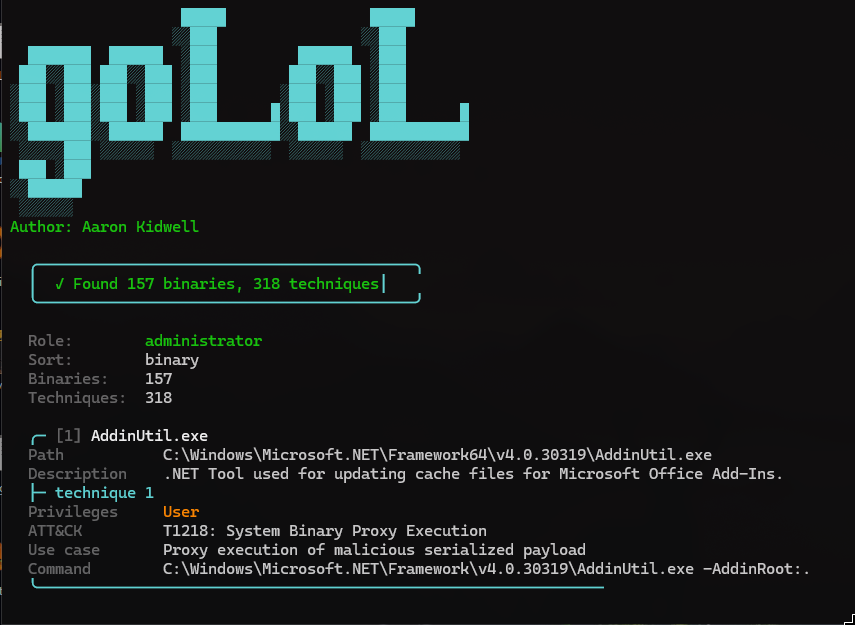
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current pri level (with MITRE ATT&CK mappings) and can scan local .sys files for /malicious LOLDrivers hash matches.
Note: This is not an OPSEC safe tool.
Author: Aaron Kidwell
!goLoL interacti output
Features
%WINDIR%, %ProgramFiles%, %USERPROFILE%, and WindowsApps locationsT1003.003: NTDS).sys files and matches against the live LOLDrivers JSON catalognet localgroup (one child process on Windows)Pri tiers
| Your context | What you see |
|---|---|
| Standard user | User-tier techniques |
| Member of local Administrators | User-tier + admin-tier techniques |
| NT AUTHORITY\\SYSTEM | User-tier + admin-tier + SYSTEM-tier techniques |
Admin-tier commands may still require an elevated shell even if your account is in the Administrators group. SYSTEM-tier entries are hidden unless the process token is SYSTEM (S-1-5-18).
Requirements
Install
Remote install (requires a tagged release on GitHub, e.g. v0.1.0):
The binary is placed in your GOPATH/bin (or ~/go/bin). On Windows, ensure that directory is on your PATH.
Clone and build:
Usage
goLoL supports two scan modes:
-driver for /malicious driver hash matchesRun from the module root (required for internal/ packages):
Build a binary (recommended.. strips debug info, ~30% smaller):
-s -w removes the symbol table and DWARF debug data. A default go build on this project is ~9.5 MB; with those flags it drops to ~6.4 MB.
Flags
| Flag | Description |
|---|---|
| -h, -help | Show help |
| -driver | Scan local drivers and list known /malicious matches from LOLDrivers |
| -plain | ASCII-only output (no colors, Unicode, or cursor control) |
| -s, -search | Show one binary by name (certutil or certutil.exe); reports if not on disk |
| -sort | Sort results: binary (default), pri, or attack |
Sort aliases: b, priv / p, mitre / a. Invalid print an error and show help.
Examples
Example output
Counts and binaries vary by host. The screenshot at the top of this README shows interactive mode (colored terminal, grouped by binary).
Plain mode (-plain):
How it works
1. Detects the current process pri context (standard user, local admin group member, or SYSTEM).
2. In default mode, downloads and parses the LOLBAS JSON catalog.
3. For each LOLBAS entry, remaps documented paths to the local filesystem and checks whether the binary exists.
4. Filters commands by pri tier and deduplicates by resol path.
5. In -driver mode, downloads the LOLDrivers JSON catalog, hashes local .sys files, and reports hash matches.
6. Prints results with paths, ATT&CK technique, use case, and example command (or dri metadata in -driver mode).
| Component | Location |
|---|---|
| LOLBAS catalog | |
| LOLDrivers catalog | |
| Pri detection | internal/pri |
| MITRE technique names | internal/mitre |
| Path resolution & output | main.go |
Project layout
Disclaimer
For authorized security testing, lab use, and education only. Only run against systems you own or ha permission to assess. LOLBAS entries describe techniques that may be abused by attackers, so use responsibly. The author is not responsible for misuse.
Technique and metadata are sourced from the LOLBAS Project and LOLDrivers. goLoL is not affiliated with or endorsed by either project.
License
MIT
项目信息
开发语言:Go
Star 数:70
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege level (with MITRE ATT&CK mappings) and can scan local .sys files for vulnerable/malicious LOLDrivers hash matches.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | goLoL - goLoL is a Windows host scanner with dual support |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:43:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 111 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |