 安全软件
点击放大
perseus - AI-powered security assessment SKILLS for your cod
项目说明
Perseus Security Skills for Claude Code
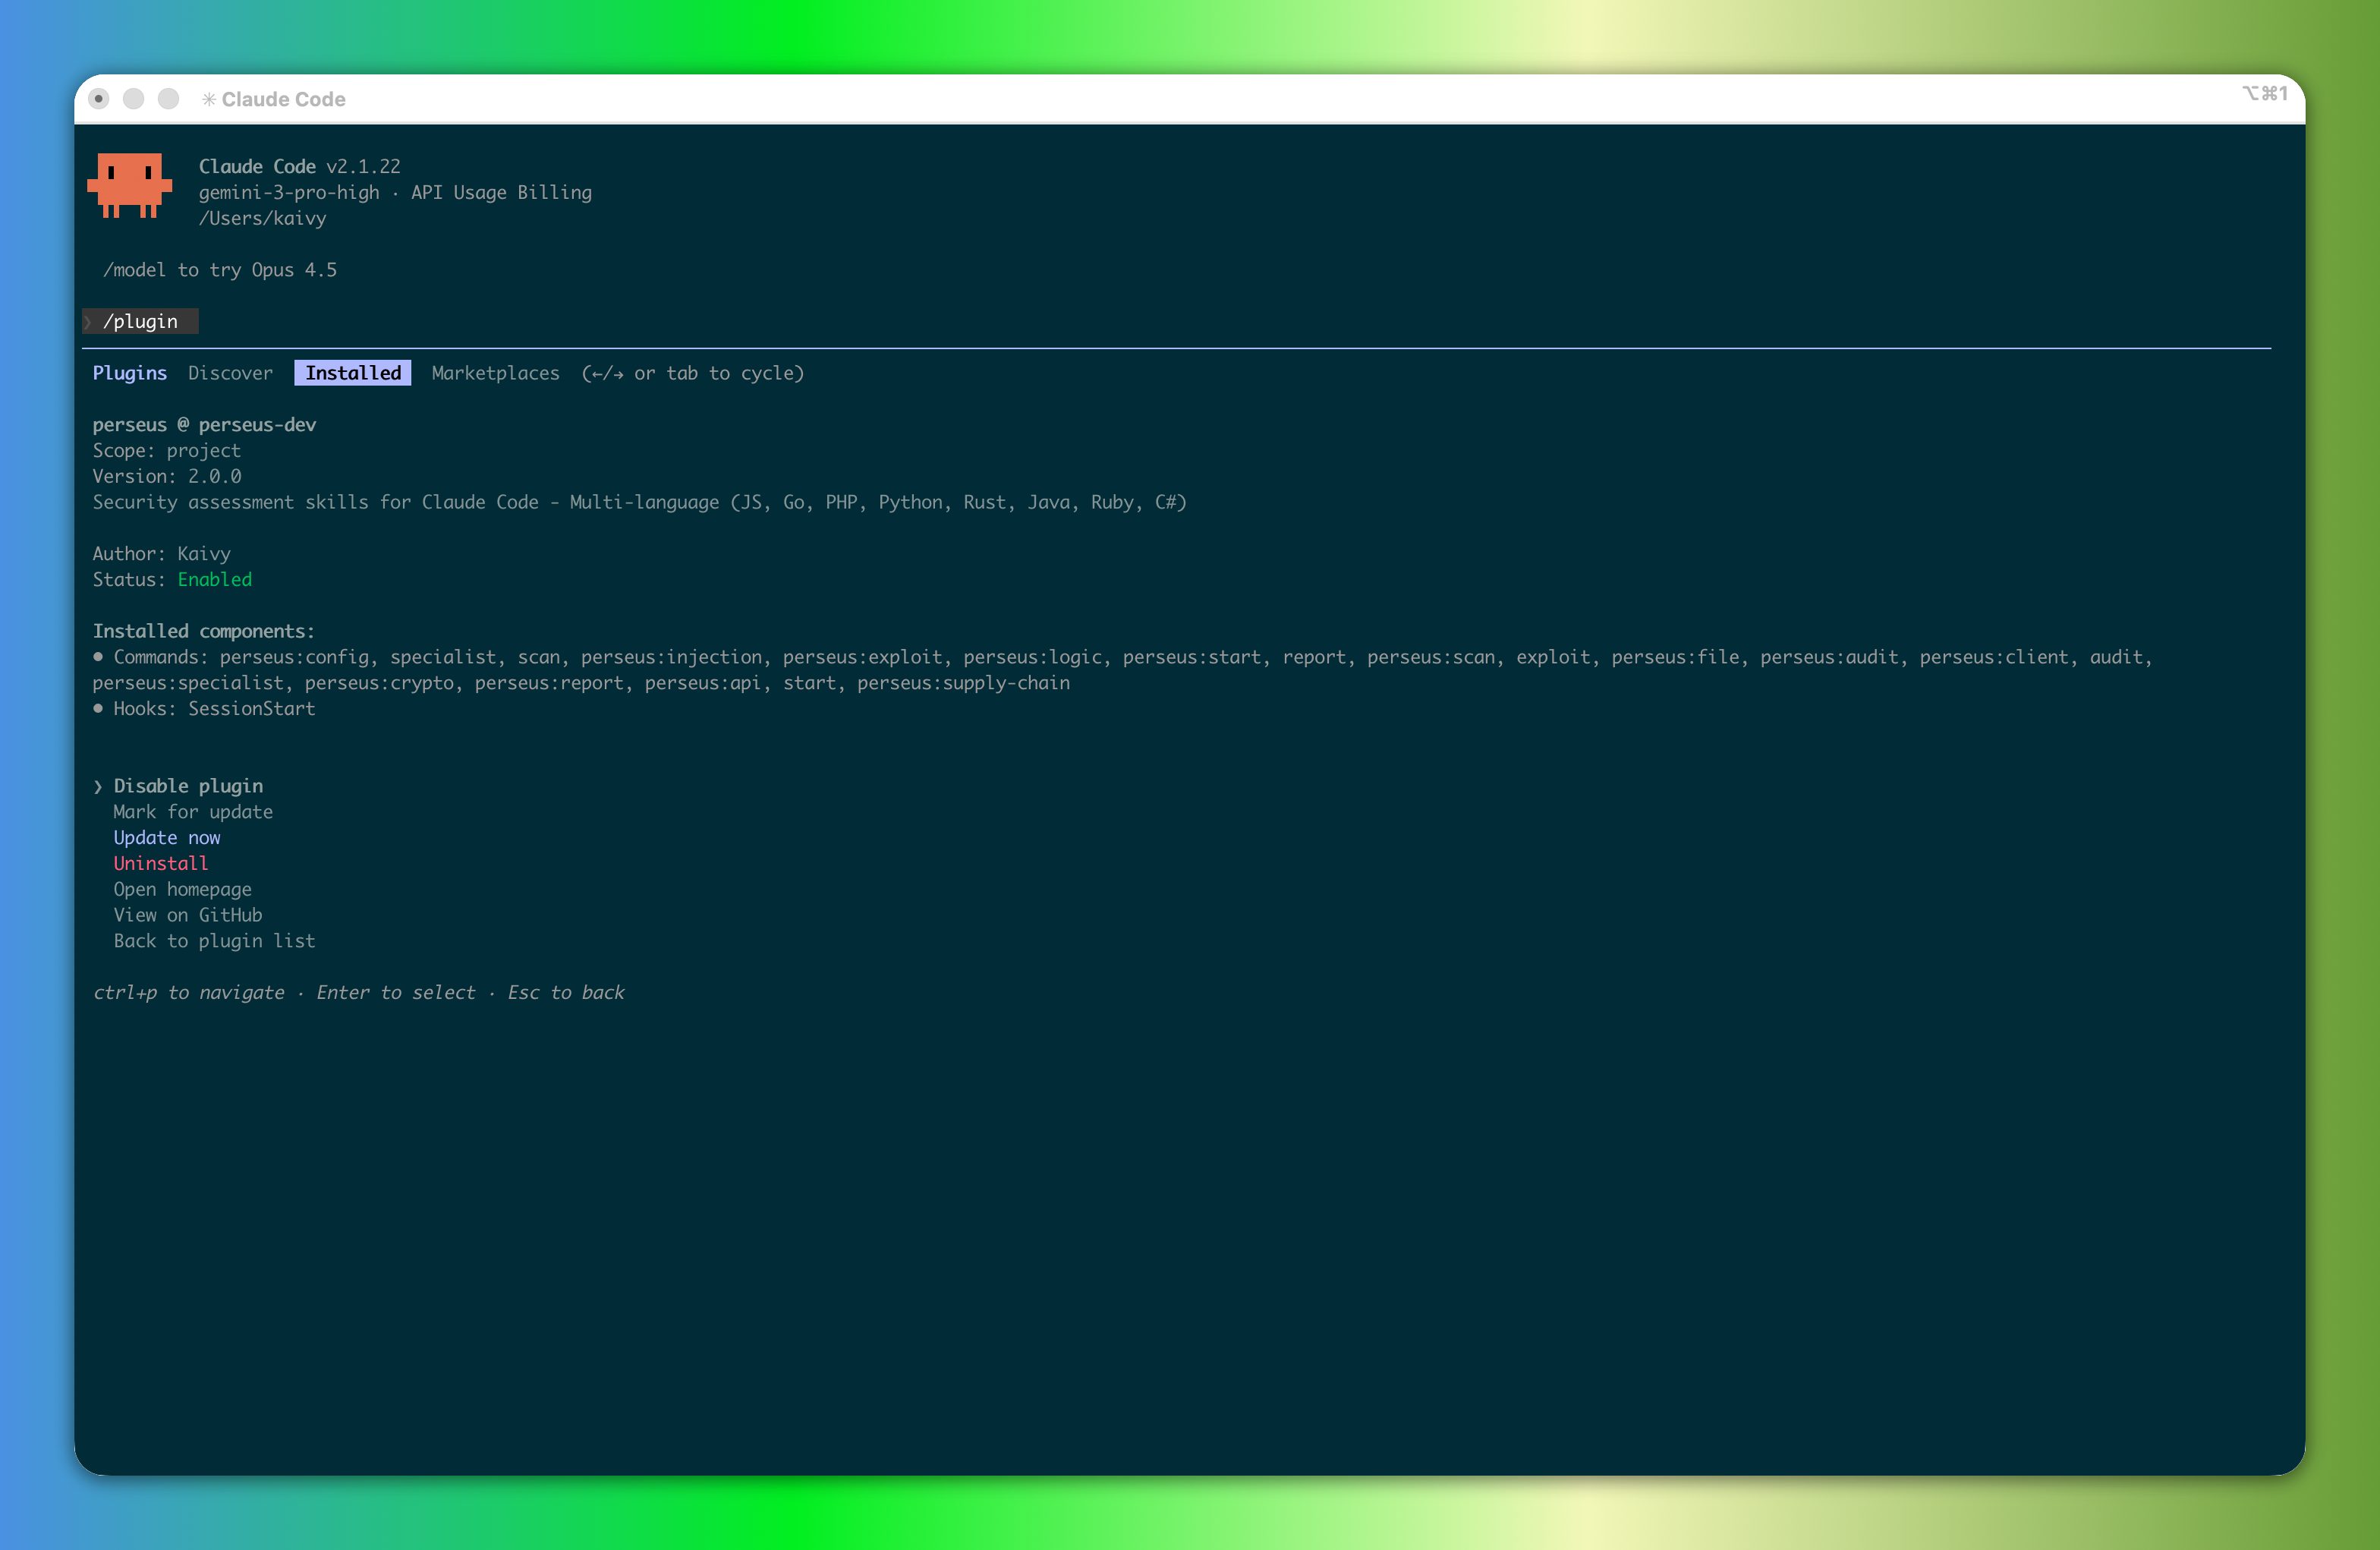
!Perseus Plugin
Perseus is a comprehensi of interacti assessment skills for Claude Code. It transforms Claude into an autonomous penetration testing partner for your own codebase, capable of performing e from initial reconnaissance to deep-di research and executi.
> Defensi Testing: Perseus analyzes your own code to find before attackers do. This is equi to running a security linter or static analyzer.
Features
Multi-Language Support (8 Languages)
| Language | Frameworks |
|----------|------------|
| Ja/TypeScript | Express, Fastify, Next.js, Nest.js, Hono, Bun |
| Go | Gin, Echo, Fiber, Chi |
| PHP | Laravel, Symfony, Slim, Lumen |
| Python | FastAPI, Django, Flask, Starlette |
| Rust | Actix-web, Axum, Rocket, Warp |
| Java | Spring Boot, Quarkus, Micronaut |
| Ruby | Rails, Sinatra, Grape |
| C# | ASP.NET Core, Minimal APIs |
Smart Auto-Detection
Perseus automatically detects your project's:
Extended Co
---
Installation
Claude Code
That's it! E is automatic:
Codex
OpenCode
Uninstall
---
Quick Start
---
Engagement Modes
Perseus uses explicit modes during assessment:
| Mode | En | Style |
|------|-------------|--------------------|
| PRODUCTION_SAFE | Li | Passi checks + minimal non-disrupti |
| STAGING_ACTIVE | Staging/pre-production | Acti with strict throttling |
| LAB_FULL | Isolated lab | Broad dynamic |
| LAB_RED_TEAM | Dedicated security lab | Controlled ad chain simulation with kill-switches |
Default mode is PRODUCTION_SAFE when en is unclear.
---
Core Assessment Phases
Perseus follows a structured 4-phase methodology:
Phase 1: Scan (Reconnaissance)
Maps architecture, entry points, dependencies, and attack surface.
| Command | Agents | Output |
|---------|--------|--------|
| /scan | 13 parallel agents | deli/code_analysis_deli.md |
Co:
Phase 2: Audit ( Analysis)
Deep white-box analysis using Negati Loop (Source → Flow → Sink → Defense → ).
Runs automatically after Scan during /start.
Wave 1: SQL Injection, Command Injection, XSS, Auth, Authz
Wave 2: SSRF, Template Injection, Deserialization, Path Tra, XXE
Wave 3: JWT, Crypto, Race Conditions, Business Logic
Phase 3: Exploit ()
findings with mode-aware safe Proof-of-Concept payloads.
Runs automatically after Audit during /start.
Safe Payloads Only:
SLEEP(5), AND 1=1sleep 5, whoamialert(1), alert(document.domain){{7*7}} → 49Phase 4: Report (Executi)
Synthesize all findings into professional security report.
| Command | Output |
|---------|--------|
| /report | deli/SECURITY_REPORT.md |
Report Includes:
---
Specialist Deep-Di
Perseus provides 8 enhanced specialist skills with multi-language support. These run automatically during /start when relevant signals are detected. Use /specialist to force-run all of them.
| Skill | Co |
|-------|----------|
| api | OWASP API Top 10, GraphQL, WebSocket, OAuth, Cache, gRPC |
| injection | NoSQL, LDAP, XPath, SSTI, Command, Log4j, Expression Language |
| crypto | JWT (8 languages), Hashing, Encryption, Key Management |
| supply-chain | CVEs (8 package managers), Typosquatting, Dependency Confusion |
| file | Path Tra, Upload Bypass, XXE, Zip Slip (8 languages) |
| logic | Business Logic, Race Conditions, AI/LLM Security, Price Manipulation |
| client | React, Next.js SSR, Ser, Vue, Angular, Svelte |
| config | Docker, CI/CD, Cloud (AWS/GCP/Azure), Kubernetes |
---
Command Reference
Short Commands (Aliases)
| Command | Description |
|---------|-------------|
|
/start | Full automated assessment with smart auto-detect ||
/scan | Phase 1: Reconnaissance ||
/report | Phase 4: Executi |Specialist Command
| Command | Description |
|---------|-------------|
|
/specialist | Run all specialist skills |Full Commands
| Command | Description |
|---------|-------------|
|
/perseus:start | Full automated assessment ||
/perseus:scan | Reconnaissance ||
/perseus:report | Executi |Full Specialist Command
| Command | Description |
|---------|-------------|
|
/perseus:specialist | Run all specialist skills |---
Output Structure
After a full assessment, the deli/ directory contains:
---
Project Structure
---
Running Tests
:
---
Safety & Ethics
Perseus is designed for defensi testing only:
PRODUCTION_SAFE is the default modeLAB_RED_TEAM requires isolated en and non-production dataABORTED-SAFETY---
Troubleshooting
Hook Blocking Issue
Problem: Perseus scan/start fails with error like:
Cause: The security-guidance plugin blocks files containing security-related keywords, even in documentation.
Solution 1: Automatic (Recommended)
Restart your Claude Code session. Perseus auto-patches the security hook on session start:
Solution 2: Manual Patch
If auto-patch doesn't work, run manually:
Solution 3: Patch All Hook Locations
The security hook may exist in multiple locations (cache + marketplaces). Patch all:
Solution 4: Disable Security Hook (Temporary)
Deli Not Created
Problem: deli/ folder is empty after scan.
Cause: Hook blocked file writing (see above).
Solution: Fix the hook issue, then run /scan again.
Skills Not Found
Problem: /scan or /start says skill not found.
Solution: Run the post-install script:
This creates all necessary symlinks automatically.
Session Start Hook Not Running
Problem: Auto-patch doesn't happen on session start.
Solution: hooks.json exists and is valid:
Should contain SessionStart configuration.
---
Changelog
v2.2.2 (2026-02)
/specialistv2.2.1 (2026-02)
PRODUCTION_SAFE, STAGING_ACTIVE, LAB_FULL, LAB_RED_TEAMABORTED-SAFETY outcomesengagement_profile.md, .mdv2.0.0 (2026-02)
/start now auto-detects language, framework, and infrastructurev1.0.0 (2026-01)
---
Documentation
| Platform | Guide |
|----------|-------|
| Claude Code | docs/README.claude.md |
| Codex | docs/README.codex.md |
| OpenCode | docs/README.opencode.md |
---
License
MIT
项目信息
开发语言:Shell
Star 数:68
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-powered security assessment SKILLS for your codebase. Multi-language (JS, Go, Python, Rust, Java, PHP, Ruby, C#). Works with Claude Code, Codex, OpenCode, etc.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | perseus - AI-powered security assessment SKILLS for your cod |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:44:05 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 288 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |