 安全软件
点击放大
subdosec - Subdosec is a fast, accurate subdomain takeover sc
项目说明
<p align="center">
<b>Subdosec</b>
</p>
<p align="center">
Subdomain takeo & reconnaissance tool.
</p>
---
!Demo
<p align="center">
<a href="#installation">Install</a> •
<a href="#running-subdosec">Usage</a> •
<a href="#web-based">Web Based</a> •
<a href="#contribution">Contribution</a> •
<a href="#online-scan">Online scan</a> •
<a href="#acknowledgments">Acknowledgments</a>
</p>
---
> Subdosec is a fast and accurate subdomain takeo with no false positives, featuring a public database of subdomains and detailed non- metadata (IP, CNAME, title, and status code) for reconnaissance.
Installation
Install or upgrade subdosec
Subdosec automatically detects its setup state, installs any missing dependencies, and boots the matching engine server on your first scan transparently.
---
Running subdosec
<b>[WARNING]
_Do not takeover all subdomains in test.txt,_
let e use that for demos.
</b>
<b>[INFO]
_Also check the Release section._
You can find interesting info.
</b>
<details>
<summary>Expand full help flags</summary>
</details>
Basic Commands
Prepare list
> Support without protocol
CMD 1
> Skip stored undetect to server & sa
> Read output
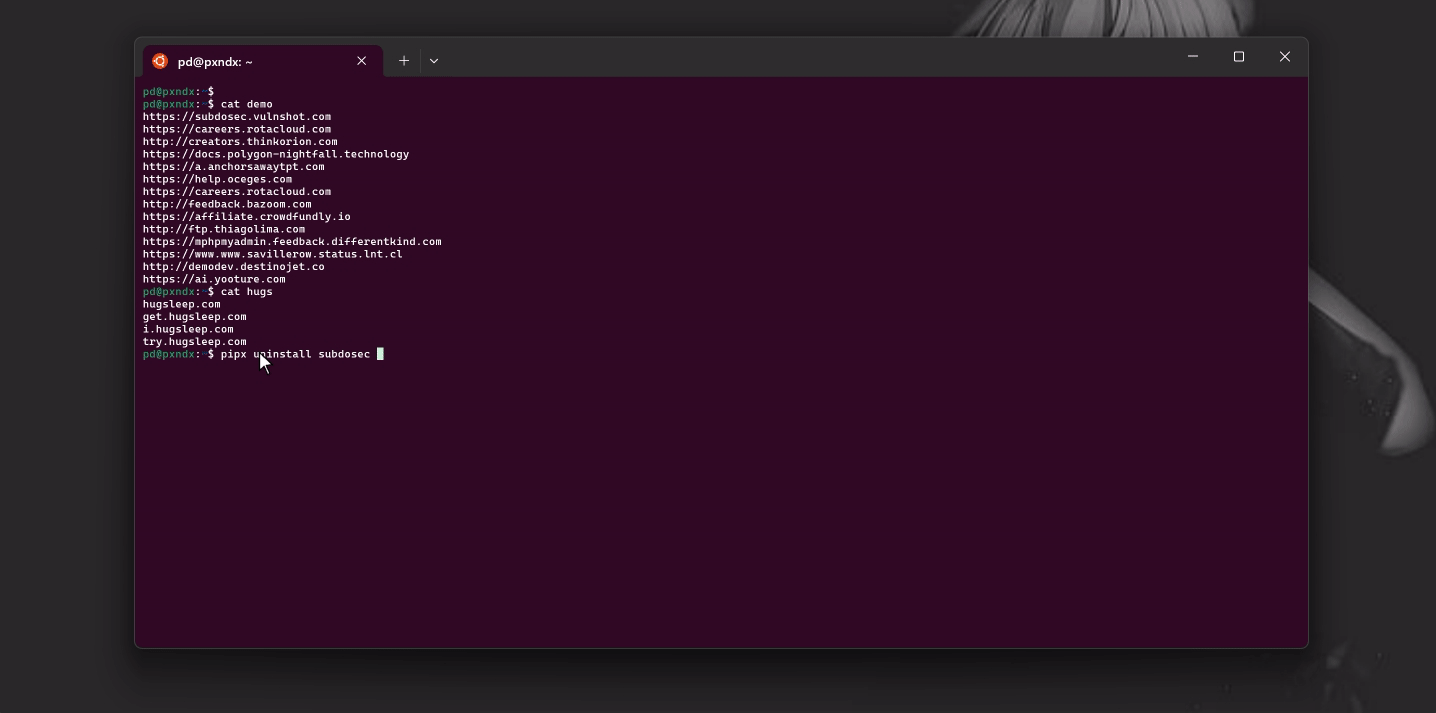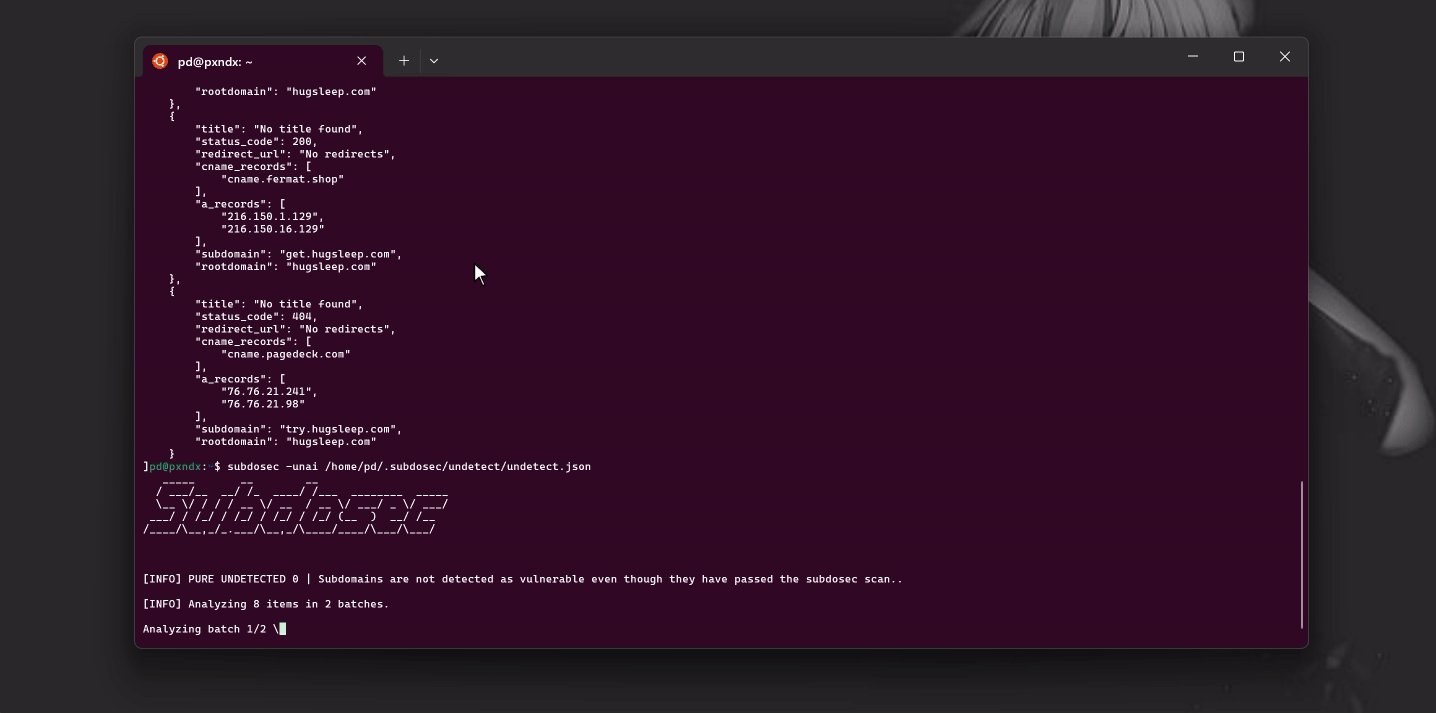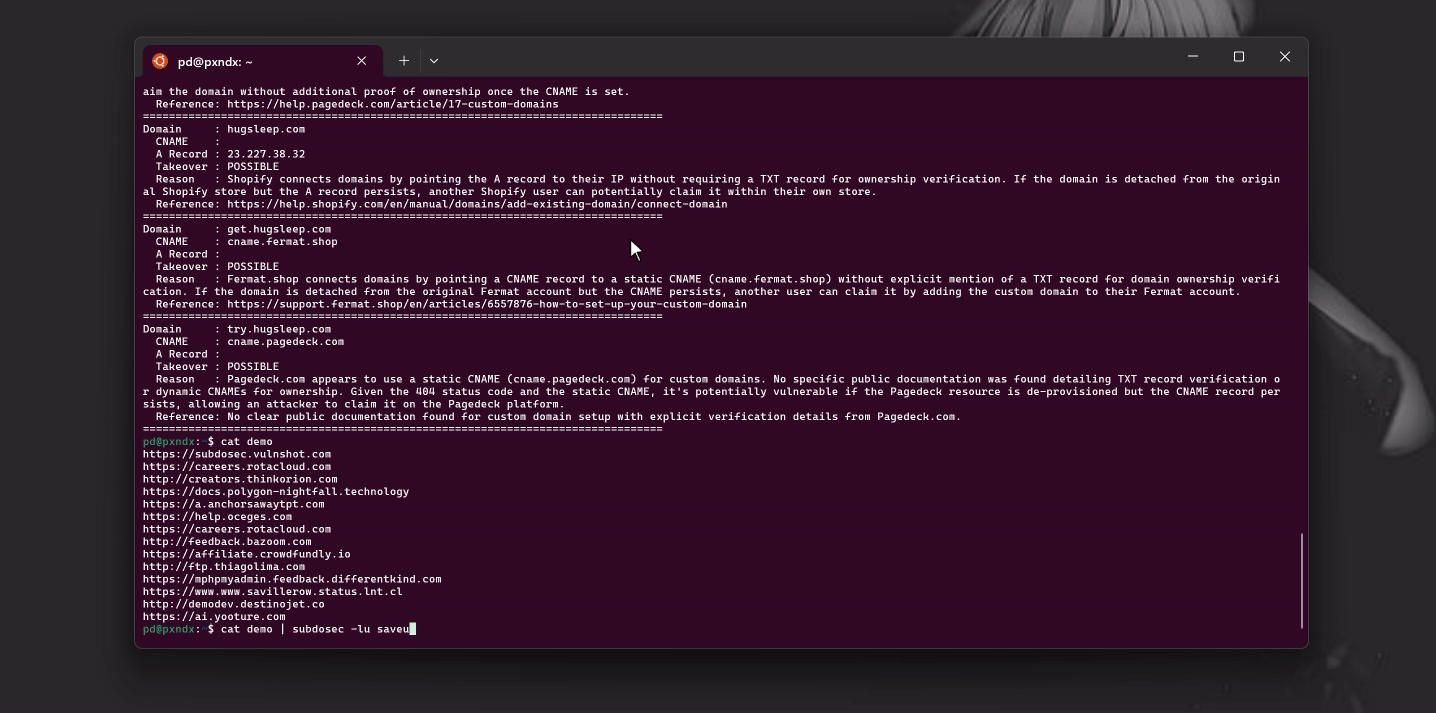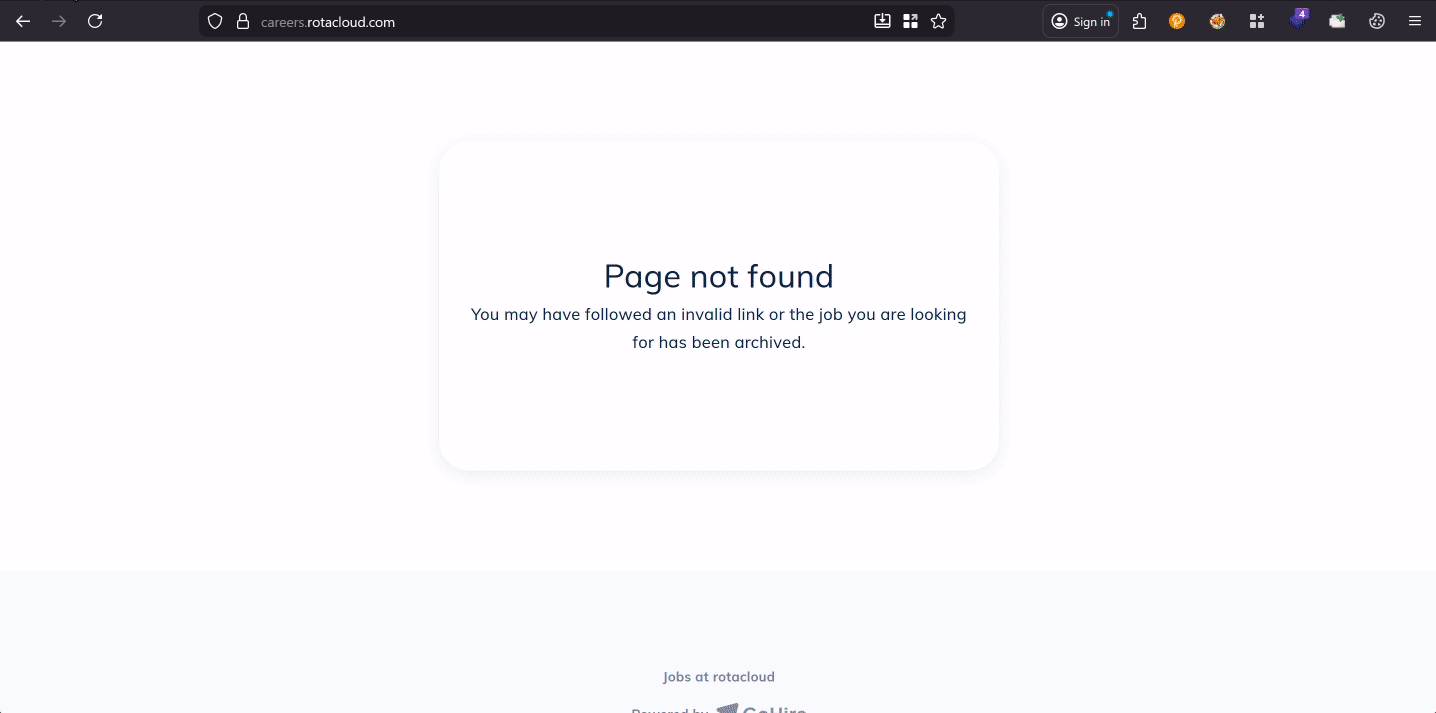
> Read undetect & auto analys new potential vuln with -unai
CMD 2
> Using root domain & pipeline subdomain finder tool like (subfinder, assetfinder, amass, etc)
CMD 3
> (Forward result to notify)
CMD 4
> Use private fingerprint, this flag will auto merge public + pri
<details>
<summary>Expand full help flags</summary>
</details>
CMD 5
> Launch the local web dashboard to inspect, search, filter, and export results
Web Based
Knowing the function of the subdosec web, here you can use the feature as a reconnaissance, to find out IP, CNAME, TITLE, STATUS CODE, etc. as further information or even to find new takeo
> It has the same function as undetect.json, the difference is that you and other people share it with each other.
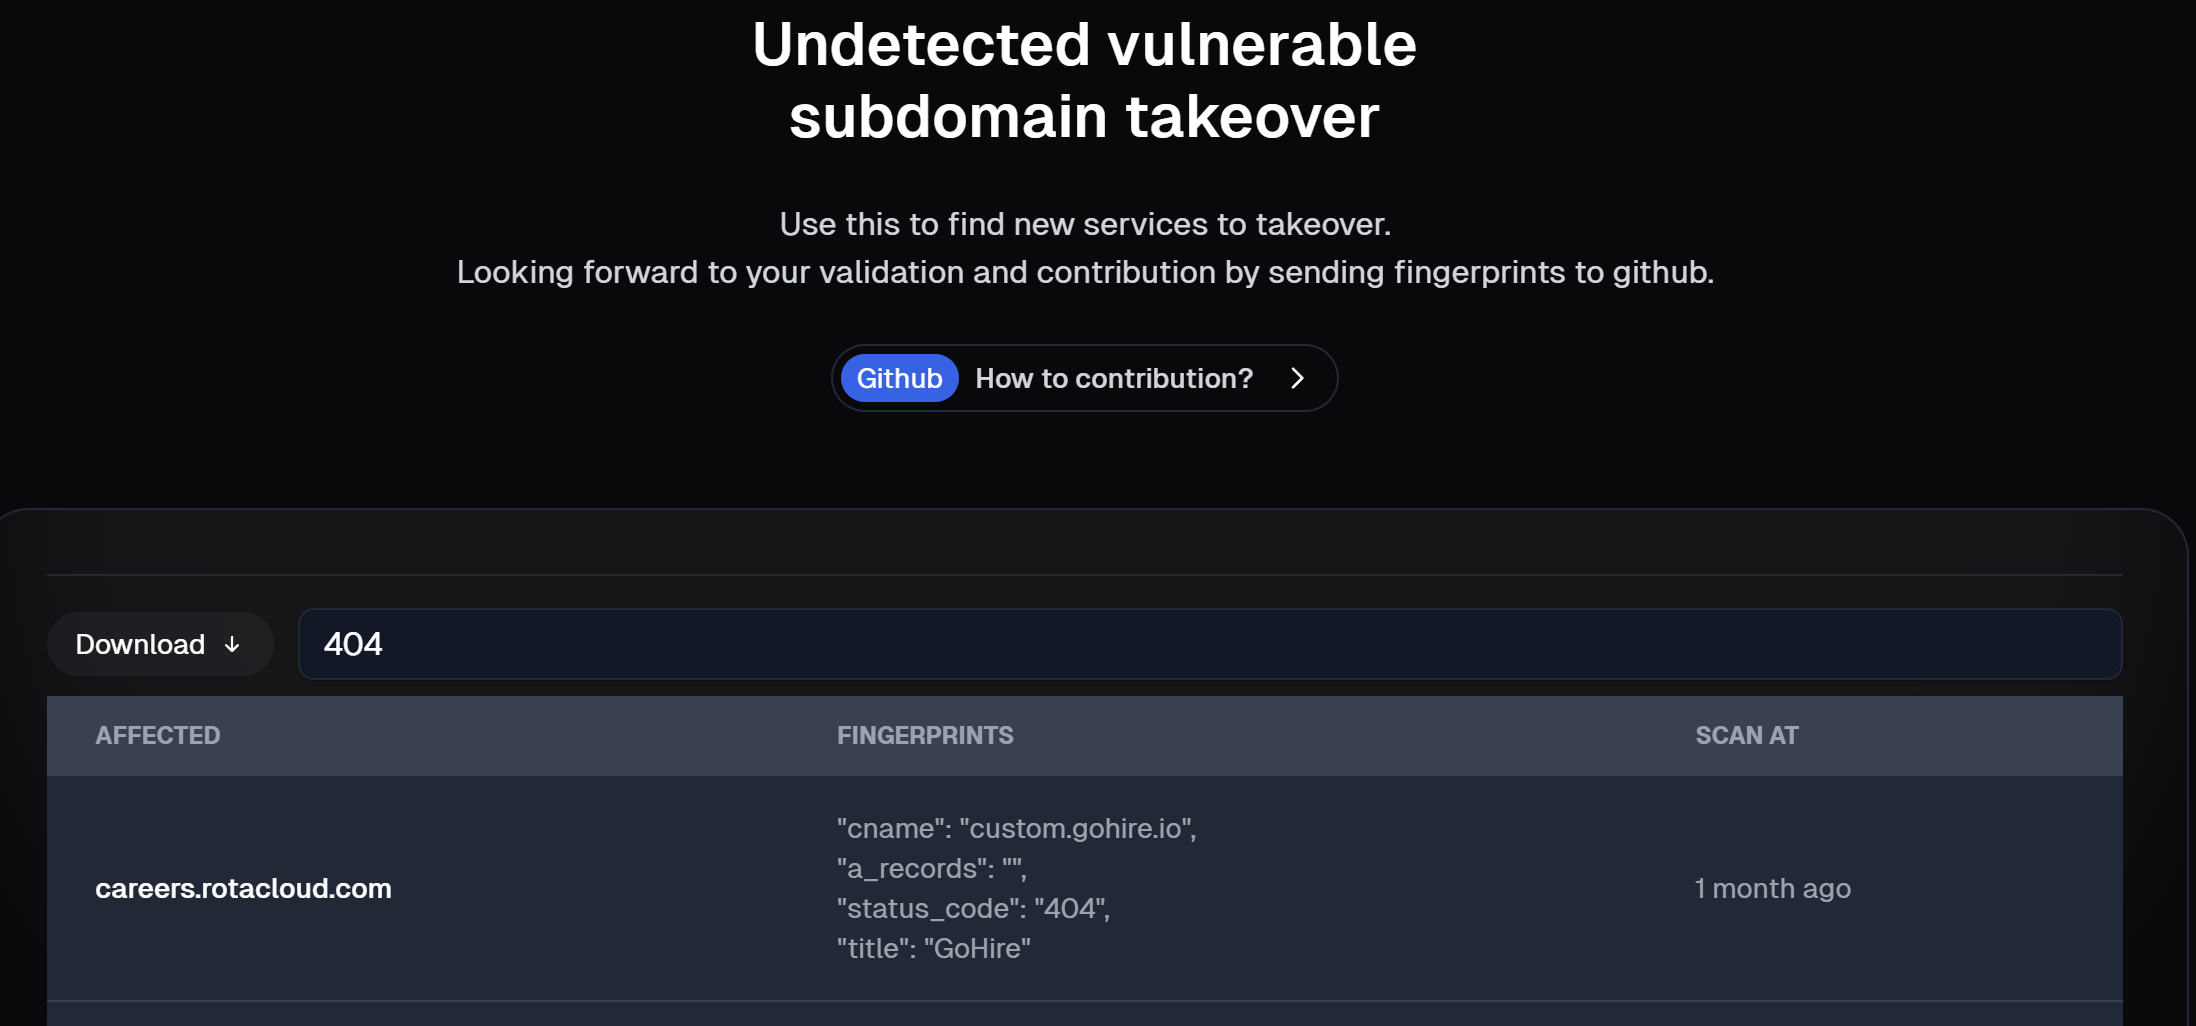
For example, you search for a site that is not detected as by subdosec with the keyword *404*, and there is information on cname.gohire.io and the title GoHire, which if you search on Google, there is no article information about subdomain takeover on the gohire service.
!Undetec
Contribution
After you find a new subdomain takeover, either manually or automatically (using -unai), you can submit the data to us using the subdosec -subfng command.
Dynamically you can use this element for rules :
>`title, cname, status_code, in_body, a_record, redirect
Online scan
If you are not a person with a security background, maybe a web-de and not familiar with cli tools. you can use the web to scan all your subdomains with a max of 10 subdomains per scan.
!Undetec
Acknowledgments
The predecessor tools that inspired the creation of subdosec tools.
---
<di="center">
<sub>subdosec` is distributed under MIT License</sub>
</div>
项目信息
开发语言:Python
Star 数:61
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Subdosec is a fast, accurate subdomain takeover scanner with no false positives. It also offers a database of sites vulnerable to subdomain takeover (public results), along with detailed metadata like IP, CNAME, TITLE, and STATUS CODE for reconnaissance to identify potential new vulnerabilities.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | subdosec - Subdosec is a fast, accurate subdomain takeover sc |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:44:45 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 142 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |