 安全软件
点击放大
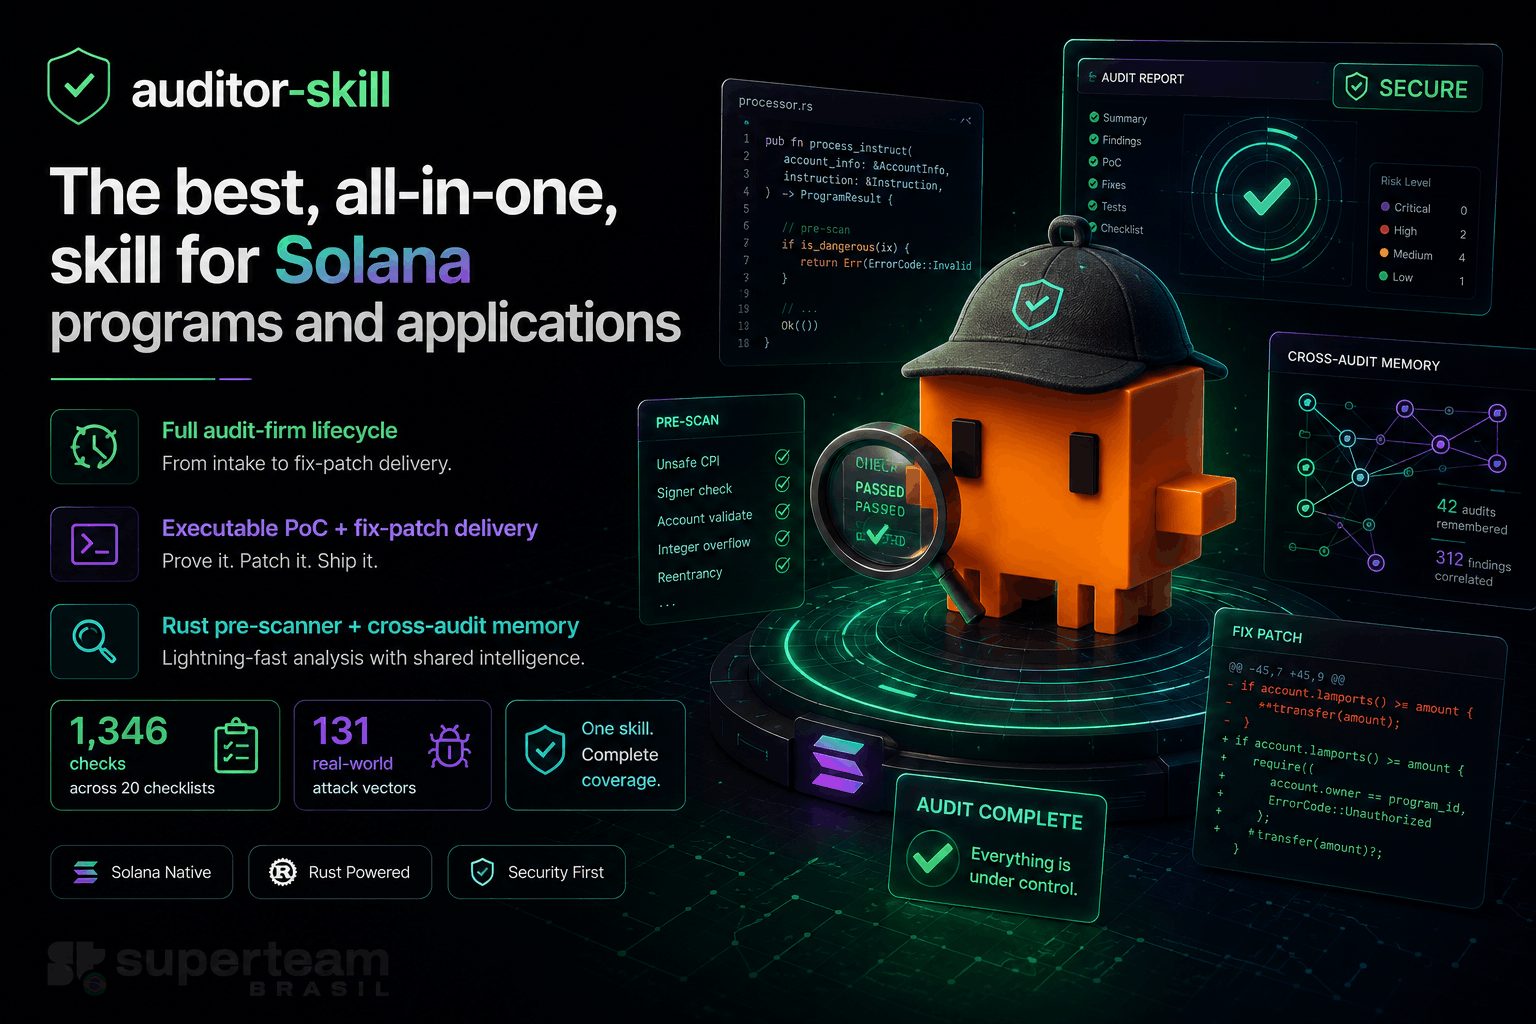
auditor-skill - Claude Code / agentic security skill for Solana pr
项目说明
<p align="center">
<img src="assets/banner.png" alt="auditor-skill — the best all-in-one security audit skill for Solana programs and applications" width="100%">
</p>
auditor-skill — Open-Source AI Security Audit Skill
> Production-grade security audit for any codebase, powered by AI agents.
> 20 checklists · 1,424 items · 137 known attack · executable PoCs + fix patches
> A full audit-firm lifecycle (automated + interactive) · Benchmarked against CertiK, SOC 2, OWASP Top 10:2025
> COSTS.md as a referecence - Running this audit can burn a lot of credits.
---
What Is This?
auditor-skill is a skill file (a structured prompt + checklists) that turns any LLM agent (Copilot, Cursor, Windsurf, Claude Code, Codex, etc.) into a professional-grade security auditor. It reads your code file by file, checks 1,424 items across 20 security domains, tests against 137 real-world attack , and produces a structured report with se scores.
It is not a SaaS product. It's a folder of markdown files you clone into your repo or give to an AI agent.
> Adaptation required before use. This skill was originally de for a specific Solana/Anchor DeFi project and then generalized. Before running it on your project you must update discovery/file-map.md with your actual folder structure, file names, and state names. The questionnaire in QUESTIONS.md is a blank template — fill it out (or run /auditor:intake) for your project before in the auditor. E else (checklists, known , output rules) is fully portable as-is.
---
What It Does (v7.4)
AddCollateralAdmin signature-bundle failure) and deployed-program pro checks (SC-053..058) — the layer cargo audit / npm audit can't see, because the artifact is your own deployed program./auditor:audit-cycle runs the whole engagement autonomously (intake → context → threat model → tool-assisted pass → domain-partitioned review → triage → independent peer review → synthesis) and hands back a professional client report. /auditor:audit-assist runs the same pipeline interactively, pausing at checkpoints for the calls only you can make./auditor:poc builds a runnable exploit (Mollusk / LiteSVM / Surfpool-fork / fuzz) that *asserts* the , and /auditor:patch drafts a minimal fix and proves it reverts the exploit. E is tiered ([PoC-REPRODUCED] … [PoC-PROSE]); prose is ne when a harness can't be built.audit-scan) enumerates the risky surface deterministically (~$0), cutting ~30-40% of input tokens on large programs. A cross-audit memory store (audit-mem) gi dedup, regression detection, and false-positi across runs.Documentation
| Guide | What's inside |
|-------|---------------|
| docs/getting-started.md | Install, submodule init, build the Rust tools, run your first audit |
| docs/audit-flows.md | The lifecycle and when to use each flow (/audit, /audit-cycle, /audit-assist, /re-audit) |
| docs/commands.md | Reference for all 15 commands |
| docs/agents.md | The 8-agent roster and how they chain |
| docs/power-tools.md | audit-scan, audit-mem, Trail of Bits, Surfpool, PoC/patch harnesses |
| docs/poc-and-patches.md | Executable exploit + fix-patch delivery |
| docs/output-and-rigor.md | Se, the Rule 5b gate, scope-gated loading, report format |
---
Supported Languages & Frameworks
| Language | Checklists | Items |
|----------|-----------|-------|
| Rust (Solana/Anchor) | 01-07 | 524 |
| Rust (off-chain services) | 20 | 21 |
| TypeScript / Node.js | 08-09 | 195 |
| React / Next.js | 08, 10 | 148 |
| Python | 14 | 82 |
| Go / Java / Ruby / PHP | 15 | 88 |
| AI / agent components | 19 | 33 |
| Always applied (any repo) | 11-13, 16-18 | 397 |
| Total | 20 | 1,424 |
---
Installation
Option 1: Claude Code plugin marketplace (recommended)
Registers the marketplace and installs the auditor plugin — all 15 /auditor:* commands and 8 agents. Then initialize the Trail of Bits execution tooling once (optional but recommended):
Option 2: Install script (any project)
Drops the skill into your project's .claude/skills/ and inits the tooling:
Option 3: Clone into your project manually
Claude Code auto-discovers skills under .claude/skills/; invoke by asking your agent to "audit this repo using the auditor-skill" (use Option 1 for the /auditor:* slash commands). For other agents (Cursor, Windsurf, Copilot, Codex), copy the folder anywhere the agent reads and point it at SKILL.md.
Option 4: Feed files to the API directly
If you're building a service, send SKILL.md + OUTPUT-RULES.md + FULL-AUDIT.md as system context and the target repo files as user content to any LLM API.
Tool execution (Trail of Bits) + optional Rust tools
auditor-skill Trail of Bits as a git submodule (/trailofbits) for real tool execution — SAST, fuzzing, co, mutation. Options 1 and 2 init it for you; to do it manually:
The nati works fully without it (it falls back to grep-based checks and notes where deeper tooling would run). With the submodule initialized, the auditor delegates to the tools per references/orchestration/boundary-map.md. For the optional token-efficiency tools (audit-scan pre-scanner + audit-mem memory), build the Rust CLIs:
---
Before Running an Audit
Scope-Gated Intake (v5.0)
auditor-skill does not bulk-read its whole corpus. It discovers the repo, declares an audit scope (OUTPUT-RULES.md Rule 0), and loads only the in-scope checklists and on demand:
OUTPUT-RULES.md (always),checklists/*.md the detected languages require (e.g. 14-python-safety.md only if .py is present),known-/*.md file only when its phase + language trigger reaches it,discovery/*.md and templates/*.md lazily, at the phase that uses them.The audit is complete when every in-scope item has an explicit ; out-of-scope items render [N/A — out of scope] from the gate.
1. Fill out the questionnaire: Copy QUESTIONS.md and answer all questions. This tells the auditor what checklists to apply, what se calibration to use, and what compliance frameworks matter.
2. Review estimated costs: Check COSTS.md for token/dollar estimates based on your repo size and chosen model.
3. Choose your scope:
| Scope | What It Covers | Estimated Time (50K lines) |
|-------|---------------|---------------------------|
| FULL | E — all 20 checklists + 137 | 60-90 min |
| PROGRAM | Smart contract only (checklists 01-07) | 20-35 min |
| BACKEND | Backend API (checklists 08-09) | 15-25 min |
| FRONTEND | Frontend (checklists 08, 10) | 15-25 min |
| DEVOPS | Infra + supply chain (checklists 11-13) | 10-15 min |
| QUICK | Known only (grep-based scan) | 5-10 min |
---
Folder Structure
---
Audit Flows
Beyond one-shot /audit, two flows run a full audit-company lifecycle end-to-end:
/auditor:audit-cycle — a fully automated audit-agent team (scope → context reconstruction → tool-assisted pass → parallel manual review with leaf-le gating → independent peer reconciliation → synthesis) that produces a professional client report at audit_<n>/REPORT.md. Optional PDF (needs pandoc):/auditor:audit-assist — an AI-assisted, human-in-the-loop flow: it pauses at checkpoints to surface findings and ask the questions only you can answer (business context, trust model, se calls), iterating until the audit document con./auditor:re-audit — fix-review: diffs against a prior report (FIXED / STILL-OPEN / REGRESSED) and sweeps for un-patched siblings of each fixed bug.Every intermediary step is also addressable on its own: /auditor:intake (persisted scoping), /auditor:threat-model (asset/actor/trust-boundary artifact), /auditor:triage (dedup + false-positi), and /auditor:poc / /auditor:patch (executable exploit + fix). Full command reference: docs/commands.md.
The client report follows professional firm con — executi, commit-pinned scope, findings with PoC/reachability, a code-maturity assessment, disclaimers. Like real firms, it does not issue a "safe to deploy" guarantee. Method + firm co: references/audit-lifecycle/.
---
Output Format
The audit produces a structured markdown report with:
1. Executi — risk score (1-10), deploy/no-deploy , se distribution
2. Instruction Matrix — every smart contract instruction mapped
3. State Model — account structs, PDA seeds, relationships
4. Per-Item — every in-scope checklist item (up to 1,424) with [PASS], [FAIL-N], [PARTIAL], or [N/A]
5. Known Results — each in-scope attack (up to 137) with explicit and e
6. Findings — deduplicated, se
7. Attack Scenarios — narrati paths
8. Aggregate Score — PASS/PARTIAL/FAIL percentages
9. Recommendations — prioritized fix list
For High/Critical findings, an optional audit_<n>/poc/ (runnable exploits that assert the bug) and audit_<n>/patches/ (minimal fixes proven to revert the exploit) accompany the report — see docs/poc-and-patches.md.
See OUTPUT-RULES.md for the complete specification.
---
How to Invoke
VS Code / GitHub Copilot
Cursor / Windsurf
Claude Code (CLI)
API (programmatic)
---
Contributing
Read CONTRIBUTING.md first — branch + PR flow (nothing lands on main directly), the corpus-count consistency rule enforced by scripts/check-corpus.sh in CI, and the no-AI-attribution commit policy (enable the hook with git config core.hooksPath scripts/hooks).
Adding a New Attack
1. Create known-/NNN-short-name.md with the next a number
2. Use this template:
grep command or check to perform
\
3. Add the entry to known-/INDEX.md
4. Submit a PR
Adding Checklist Items
1. Open the relevant checklist in checklists/
2. Add new items following the existing format (ID prefix + sequential number)
3. Update the item count in SKILL.md
Updating Cost Estimates
If model pricing changes, update COSTS.md with new rates.
---
Benchmarking
This auditor was designed by comparing methodology from:
| Standard | Domain | What We Took |
|----------|--------|-------------|
| CertiK | Crypto audit | On-chain taxonomy, formal approach |
| EY / SOC 2 | Enterprise IT audit | Control objectives, e requirements |
| OWASP Top 10:2025 | Web security | Attack categories, se calibration |
| NIST SP 800-53 | Go security | Control framework structure |
| COBIT 2019 | IT go | Process maturity model |
| GDPR / MiCA / DORA | EU regulation | Compliance checklist items |
---
License
MIT — use it, fork it, improve it, sell services built on it. Attribution appreciated but not required.
---
FAQ
Q: Does this replace a professional audit?
A: It covers more items than most paid audits (1,424 plus 137 known- checks 50-200), but an AI auditor cannot do e a human can (social engineering assessment, business logic review requiring domain expertise, legal compliance opinions). Use this as a first pass, then hire humans for what it flags.
Q: Which AI model should I use?
A: See COSTS.md. For maximum depth, use Opus 4 or o3. For best value, use Sonnet 4 or GPT-4.1. For CI/CD integration (fast, cheap), use Haiku or o4-mini.
Q: How long does an audit take?
A: Depends on repo size and model. A 50K-line repo takes 60-90 minutes with Opus 4. See COSTS.md for full estimates.
Q: Can I use this in CI/CD?
A: Yes — run the QUICK scope (known grep scan) on every PR, and FULL scope on release branches.
Q: Can I use this for non-Solana projects?
A: Yes — checklists 08-18 are language-agnostic or co/Go/Java/Ruby/PHP. Checklists 01-07 are Solana-specific.
---
Acknowledgments
auditor-skill stands on the shoulders of two open-source security projects — credited in full in ATTRIBUTION.md:
/trailofbits and orchestrated for real execution; methodology patterns re-implemented natively are credited by reference.All third-party methodology is used by *reference* — no third-party text is copied into this repository.
项目信息
开发语言:Rust
Star 数:58
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Claude Code / agentic security skill for Solana programs and software. Full audit-firm lifecycle, executable PoC + fix-patch delivery, a Rust pre-scanner + cross-audit memory, 1,346 checks across 20 checklists, and 131 real-world attack vectors.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | auditor-skill - Claude Code / agentic security skill for Solana pr |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:44:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 316 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |