 安全软件
点击放大
WonderSuite-Ai-Bug-Bounty - AI-Powered Offensive Security Research Engine - de
项目说明
<di="center">
<img src="public/wondersuite_logo.png" alt="WonderSuite" width="420" />
AI-Powered Offensi Research Engine
A desktop-nati testing platform built on Rust and Tauri with nati Context Protocol (MCP) integration for AI-dri research.
![Rust]()
![Tauri]()
![React]()
![MCP]()


![Latest Release]()
![Release Date]()
![Downloads (total)]()
![Downloads (latest)]()
![Stars]()
![Forks]()
![Last Commit]()
![CI]()
![CodeQL]()
Download ·
Features ·
Screenshots ·
Getting Started ·
MCP Tools ·
Contributing
</div>
---
O
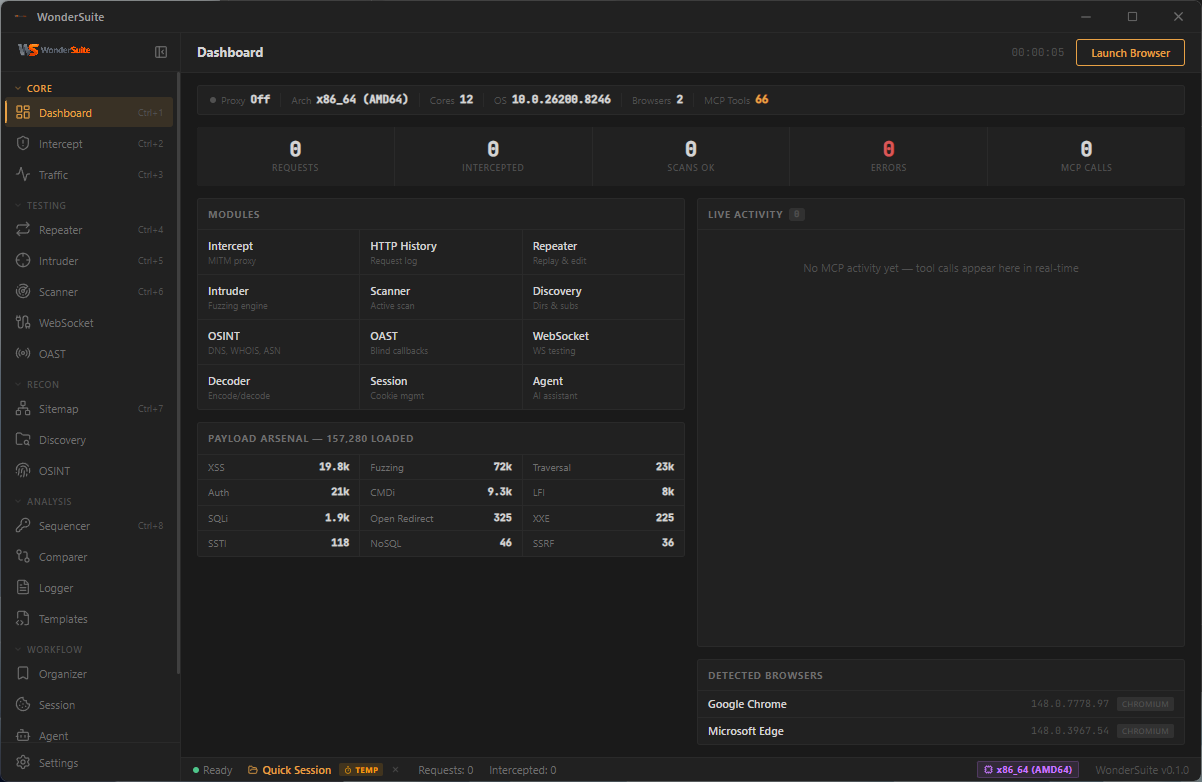
WonderSuite is a desktop nati security engine that combines Burp Suite-class tooling with autonomous AI agent capabilities. It provides a fully integrated en for web application security testing, network reconnaissance, and exploit de — all orchestrated through an MCP-compatible AI interface.
The platform ships with 91 purpose-built security tools accessible (trimmed from 100 in v0.3.11 — the standalone OAST tools were folded into acti(with_oast: true) to keep the AI's context budget lean), a full MITM proxy with Chrome 137 JA3/JA4 + HTTP/2 fingerprint impersonation (defeats Cloudflare, Akamai Bot Manager, DataDome, PerimeterX), a bundled Chrome-for-Testing 148 with stealth extension and per- isolation, a pentest-grade browser MCP surface with stable element refs and OAST-integrated blind-vuln detection, and automated scanning across SQLi, XSS, SSTI, LFI, CRLF, Open Redirect, plus blind cmdi / SSRF / Log4Shell via the bundled OAST listener.
<di="center">
<img src="docs/screenshots/dashboard.png" alt="WonderSuite Dashboard" width="900" />
</div>
See it in action
<di="center">
<img src="docs/preview.gif" alt="Claude Opus 4.7 driving WonderSuite end-to-end" width="900" />
*Claude Opus 4.7 driving WonderSuite end-to-end: opens WonderBrowser, walks through a registration form on its own (fills email + password fields, presses Sign up), and watches the resulting traffic stream through the proxy live — auth POST captured, JWT/CSRF surfaced, ready to fuzz. Zero scripted steps, the agent picks the tool sequence itself (browser_open → browser_snapshot → browser_fill_form → browser_click → proxy_get_traffic → analyze_jwt).*
▶ Full-quality MP4 (1.9 MB, with audio)
</div>
Core Capabilities
Intercepting Proxy
Full man-in-the-middle proxy with TLS interception and dynamic certificate authority generation. Supports real time request and response modification, match-and-replace rules with regex (5 targets: request_header/body/url, response_header/body), WebSocket message capture, upstream proxy chaining (HTTP/SOCKS5), traffic annotation with color highlighting, and proper HAR/JSON export (headers, queryString, statusText all populated). Upstream requests can be re-originated through a BoringSSL stack tuned to match Chrome 137's exact ClientHello, JA3/JA4 fingerprint and HTTP/2 SETTINGS frame ordering — bypasses Cloudflare, Akamai Bot Manager, DataDome, and PerimeterX.
WonderBrowser — Bundled Chrome-for-Testing 148
A pinned Chromium build (CfT 148.0.7778.97) shipped inside WonderSuite — , SHA-256-, ne, per- cached. Uses a separate .wondersuite/ profile so it doesn't touch the user's system Chrome. The bundled WonderSuite extension applies minimal stealth at document_start (deletes na.webdriver from the prototype, purges automation globals) — isBot: false on all 18 de.com checks. All outbound requests flow through the WonderSuite proxy for capture and TLS impersonation.
Cache behaviour (v0.3.28+): By default, WonderSuite wipes the browser's on-disk HTTP cache (Cache/, Code Cache/, Service Worker/, etc.) before every launch. This ensures every resource is fetched fresh through the proxy so it appears in the Sitemap and Code Audit — without this, Chrome would ser JS/CSS/images directly from disk, bypassing capture entirely. Toggle off in Settings → Browser → Clear HTTP cache on browser start if you need a warmed cache for a specific test.
Undetected — 17 / 17 Bot-Detection Signals Clean
Out of the box, no per-target tuning, no manual e: WonderBrowser plus the impersonating proxy passes every signal on third-party bot-detection fingerprinting suites. Live test against the public detector at de.com/are_you_a_bot:
<di="center">
<img src="docs/screenshots/wonderbrowser-bot-detection.png" alt="WonderBrowser passing de.com — : 'You are human!'" width="900" />
</div>
#### How — three independent stealth layers
WonderSuite stacks three orthogonal layers, each defeating a *different* class of fingerprinting:
1. TLS layer (proxy upstream). Every outbound TLS handshake is re-originated through a BoringSSL stack tuned to Chrome 137's exact ClientHello — cipher suite order, ALPN, GREASE bytes, extensions, key shares — plus HTTP/2 SETTINGS frame ordering. The resulting JA3/JA4 fingerprint is byte-identical to a real Chrome. Cloudflare, Akamai Bot Manager, DataDome and PerimeterX classify the request as a real browser at the TCP/TLS layer before any JS even runs.
2. Browser layer (binary + extension). WonderBrowser is Chrome-for-Testing 148 — not a fork, not CEF, not Electron. It runs an isolated .wondersuite/ profile separate from your system Chrome. A bundled MV3 extension hooks document_start (before any page JS) to delete na.webdriver directly off Na.prototype (no easy o) and purges automation globals (window.cdc_*, CDP-injection artifacts). The binary is SHA-256-, , ne.
3. Input layer (agent automation). When the AI agent drives the browser via MCP tools, every click / keystroke / scroll goes through Chrome's real input pipeline via CDP.Input.dispatchMouseEvent / dispatchKeyEvent / insertText — resulting DOM events carry event.isTrusted === true, indistinguishable from a physical keyboard and mouse. Mouse paths are humanlike Bezier trajectories with Gaussian jitter; typing cadence is drawn per-character from a normal distribution; pre-action dwell time and document.hasFocus() emulation are configurable per stealth profile (fast / human / paranoid). The AI cursor o lives in a closed Shadow DOM — to the operator, completely in to page JS. Fraud SDKs like FriendlyCaptcha, DataDome, Cloudflare Bot Management and Imperva — which silently drop programmatic form submissions when isTrusted: false — let WonderSuite traffic through.
#### How it flows — browser, proxy, optional impersonation
#### Optional impersonation toggle
TLS impersonation is on by default. It can be disabled in Settings → Browser → "Impersonate Chrome TLS (JA3/JA4 + HTTP/2)" — useful when you want to compare how a target reacts to a fingerprint-detectable ated client (the "what does Cloudflare actually block?" experiment). With the toggle off, upstream falls back to nati / stock reqwest, exposing a standard Rustls/OpenSSL JA3 fingerprint.
Browser MCP — Human-Nati Surface (v0.3.3+)
24 browser tools driving WonderBrowser via a single persistent CDP WebSocket. All input goes through Chrome's real input pipeline (CDP Input.dispatchMouseEvent / dispatchKeyEvent / insertText) so resulting DOM events have event.isTrusted === true — indistinguishable from a physical keyboard and mouse, defeats the class of fraud SDKs (FriendlyCaptcha, DataDome, Cloudflare Bot Management, Imperva) that silently drop programmatic form submissions. On top: humanlike Bezier mouse trajectories with Gaussian jitter, per-character typing cadence drawn from a normal distribution, configurable pre-action dwell, focus emulation so document.hasFocus() reports true. Three stealth profiles (fast / human / paranoid) trade speed against detection-resistance — pick one in Settings → Browser, or o per call. The AI cursor o lives in a closed Shadow DOM so it's to the user but completely in to page-JS. browser_stealth_check self-tests the stack and reports an isTrusted score with (indistinguishable / good / partially-detectable / detectable). Plus e from v0.3.2: ref-based snapshots, browser_fill_form accepting ref/selector/name, browser_storage_full one-shot auth dump, browser_replay_to_proxy, browser_dom_sinks, CSP- console, browser_resource_hints, CDP-nati wheel events.
Crawler
Multi-le with robots.txt + sitemap.xml + /.well-known/ + JS endpoint extraction discovery, soft-404 detection, SPA-aware rendering hooks, cookie + path canonicalization. Regex-based fast path for static apps; for SPAs the browser MCP surface is the better tool.
Code Audit (v0.3.24+)
Browse any target through the WonderSuite proxy — every JS file, stylesheet, API response, and image is captured automatically. Switch to the Code Audit tab inside the Sitemap module and all captured assets are instantly a for deep inspection: no separate crawl, no manual download, no de copy-paste.
<di="center">
<img src="docs/screenshots/code-audit.png" alt="Code Audit — source with findings and export menu" width="900" />
</div>
The workflow in three steps:
1. Capture — browse the target with the proxy running. JS bundles, CSS, API responses, and images stream into the asset tree as they're intercepted. E the browser loads passes through WonderSuite first.
2. Audit — the built-in finder engine scans every captured source file automatically. 60+ regex patterns surface secrets, tokens, API endpoints, links, and suspicious comments without any manual effort.
3. Export — right-click any domain, type-group, or indi file to export beautified source, a self-contained HTML security report, per-category CSV/TXT, or a full ZIP bundle (js/ · css/ · html/ · api/ · findings/) you can drop into a project folder or hand to an AI agent for a deeper code audit.
Three-panel layout: Asset tree (domain → type → file) · Shiki-highlighted source editor (minified code auto-formatted, line numbers, click-to-jump on findings) · Findings + Summary panel.
Finder engine — what it exposes automatically:
| Category | Examples |
|---|---|
| Secrets | AWS/GCP/Azure keys, OpenAI/Anthropic/HuggingFace tokens, Stripe live keys, GitHub tokens, Slack webhooks, Supabase service/anon keys, MongoDB/Postgres connection strings, private key blocks, NEXT_PUBLIC_ / VITE_ / REACT_APP_ en |
| Tokens | JWT, Bearer, Basic Auth, OAuth, refresh\_token, session cookies |
| API Endpoints | fetch(), axios, XHR, GraphQL operations, WebSocket URLs, gRPC/tRPC routes |
| Library | Combine with js_library_audit (MCP tool) to detect outdated jQuery, React, lodash, etc. and cross-reference known CVEs |
| Links | All absolute and relative URLs embedded in source |
| Comments | TODO/FIXME/HACK, comments mentioning passwords or credentials |
Sitemap multi-select (v0.3.26+):
Port Scanner — In-Process, Adapti (v0.3.7+)
Built-in port scanner with three real engines: TCP Connect (no admin, default), TCP SYN (raw sockets WinDivert on Windows / pnet on Linux+macOS), and UDP (no admin, response-based protocol detection). No nmap subprocess — service detection runs against the real nmap-ser file (187 probes, 12k+ regex match patterns) embedded at build time. Adapti 's Law (in_flight = target_pps × RTT_p50) — the permit pool floats with obser conditions every 2 seconds, where RustScan's batch_size is fixed at startup. Li results to a table; presets (Top-100, Top-1000, Web, Dev, DB, All); timing templates T0 paranoid → T6 ludicrous; export to JSONL, CSV, Nmap XML, gnmap, or ip:port. CIDR + range + hostname expansion. Idle-mode caps at ~100 pps for field-laptop use.
#### How it flows — three modes, one orchestrator
#### Pri model
| Platform | Connect | SYN | UDP |
|---|---|---|---|
| Linux | no admin | cap_net_raw via setcap | no admin (raw ICMP optional for closed-port detection) |
| macOS | no admin | root (signed launchd helper coming) | no admin |
| Windows | no admin | bundled WinDivert (LGPLv3, E by Reqrypt LLC) — one UAC consent for the SCM service install, no external download | no admin |
WonderSuite ships WinDivert 2.2.2 inside the installer (WinDivert.dll + WinDi.sys, 140 KB total). At first SYN scan the UI offers a one-click "Install network driver" button → ShellExecuteExW with verb runas → UAC consent → sc.exe create + sc.exe start register the kernel service. WinDivert.dll is dlopened from the resource_dir at scan time via libloading — no compile-time link, so the .exe launches cleanly on machines that don't have the driver yet (graceful fallback to TCP connect with a clear error message). HVCI / Memory Integrity detected ; on H machines the SYN engine surfaces a clear "disable Memory Integrity" message and falls back to connect.
Multi-Window Workspace (v0.3.7+)
Right-click any sidebar module → "Pop out to window" spawns a nati window with just that module. Cross-monitor workflow: Comparer on monitor 1, Repeater on monitor 2, Logger on monitor 3, main shell on monitor 4. Geometry persists per moduleId in localStorage — windows respawn at the same position on app restart (workspace save). Cross-window state bridge events: "Send to Repeater" from the Traffic tab in the main window still works when Repeater is detached. 240 ms pop-in animation, 240 ms scale-down re-dock. Each detached window is a separate WebView (~40-60 MB RAM) but shares one Rust backend — no IPC duplication.
MCP Server — 90 Tools + Operator Skill
Nati Context Protocol ser AI agents (Claude, Cursor, Windsurf, VS Code, Antigravity, Gemini CLI, …) to autonomously conduct security research against WonderSuite's tool surface. Ships with a project-le skill (.claude/skills/wondersuite.md) that teaches the AI workflows, error-recovery, and when-to-ask- — see Skill File below.
| Category | Tools |
|----------|-------|
| HTTP | send_request · send_to_repeater · send_to_intruder (auto-categorises payloads per param name) · h2_send_request · mtls_send_request |
| Proxy | proxy_start · proxy_stop · proxy_status · proxy_toggle_intercept · proxy_get_traffic · proxy_search_traffic · proxy_clear_traffic · proxy_export_traffic (JSON / HAR with full headers + queryString) · proxy_get_statistics · proxy_add_match_replace · proxy_add_interception_rule · proxy_add_tls_passthrough · proxy_set_upstream · proxy_annotate_traffic · proxy_get_websocket_messages · get_intercepted · forward_intercepted |
| Scanner | acti (SQLi · XSS · SSTI · LFI · Open Redirect · CRLF) with optional with_oast:true for blind cmdi, blind SSRF, Log4Shell via the bundled OAST listener · passi (headers, cookies, CORS, info disclosure) |
| Intruder | fuzz_request — Sniper · Battering Ram · Pitchfork · Cluster Bomb |
| Browser (24) | browser_open · browser_attach (reuse running WonderBrowser; auto_launch:true spawns) · browser_close · browser_na · browser_snapshot (a11y tree + ref=eN + forms-with-labels + honeypot detection + security block) · browser_screenshot (writes JPEG to disk, returns path) · browser_click (CDP-nati:true, humanlike trajectory) · browser_type (CDP insertText with Gaussian cadence) · browser_fill_form (ref/selector/name + auto-submit; ref path goes through humanlike CDP input) · browser_press_key (CDP dispatchKeyEvent) · browser_scroll (CDP mouseWheel event) · browser_select_option · browser_set_file_input · browser_get_outer_html · browser_e · browser_storage_full (cookies+LS+SS+IDB+SW+caches+cookie_header) · browser_console (incl. CSP ) · browser_dom_sinks (innerHTML/e enum) · browser_network_traffic (CDP ring buffer) · browser_replay_to_proxy (hand browser request to Repeater) · browser_resource_hints (robots/well-known/sourcemaps) · browser_wait_for · browser_tabs · browser_stealth_check (self-test the human-emulation stack) |
| Recon | crawl_target · disco · disco (concurrent DNS) · find_secrets · dns_resolve (with CDN detection) · js_link_finder |
| Port Scanner (5) | port_scan (host + presets + 15 in-process probes) · port_scan_range (CIDR/range/list, exclude_cdn) · ser (probe a known-open port) · banner_grab (raw bytes, custom payload) · port_scan_results (paginated drill-down) |
| OSINT | whois_lookup · asn_lookup · crtsh_search · wayback_lookup · hackertarget_lookup · ip_geolocation · tech_detect · fa · re · graphql_introspect |
| Codec | encode · decode · hash · smart_decode · analyze_jwt (alg=none, kid SQLi/tra, jku/x5u SSRF, HS/RS confusion) |
| OAST | Embedded in-process listeners (HTTP / DNS / SMTP) with path-correlated callbacks; drive from acti(with_oast: true) (recommended for AI agents) or the OAST UI panel. Standalone oast_* MCP tools are not in the agent surface as of v0.3.11 — un-comment in src-tauri/src/mcp/handlers/mod.rs if you need raw payload control. |
| Exploit | race_request · raw_tcp_send · websocket_connect · analyze_cdn_waf (with CDN bypass strategies) |
| Reporting | generate_report (markdown / JSON / summary) · bambda_filter · payload_manager · get_traffic_log |
Autonomous Security Research
The AI agent operates independently through the MCP interface. It can launch WonderBrowser, walk the app with browser_snapshot's stable refs, dri with browser_fill_form (by ref OR selector OR name), capture the authenticated session via browser_storage_full (cookies + LS + SS + IDB + SW + Cache in one call, ready-to-replay Cookie: header), and hand any browser-discovered request to the proxy's Repeater via browser_replay_to_proxy. From there: acti with_oast:true fires error+time-based SQLi, reflected XSS, SSTI, LFI, Open Redirect, AND blind-injection probes (curl/wget/JNDI-LDAP/Log4Shell-style) that callback to the bundled OAST listener — every callback becomes a critical-se, certain-confidence finding. analyze_jwt flags alg=none, kid-as-SQLi-sink, jku/x5u SSRF, and HS/RS key-confusion classes. analyze_cdn_waf returns actionable bypass strategies cross-referenced to other tools (origin discovery via dns_history/crtsh_search/fa, header-manipulation e, payload obfuscation, protocol-le).
Screenshots
<table>
<tr>
<td align="center" width="50%">
<strong>Project Launcher</strong><br/>
<img src="docs/screenshots/project-launcher.png" alt="Project Launcher" width="100%" />
</td>
<td align="center" width="50%">
<strong>Dashboard</strong><br/>
<img src="docs/screenshots/dashboard.png" alt="Dashboard" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Intercepting Proxy</strong><br/>
<img src="docs/screenshots/intercept-proxy.png" alt="Intercept Proxy" width="100%" />
</td>
<td align="center">
<strong>Traffic History · Context Menu</strong><br/>
<img src="docs/screenshots/traffic-context-menu.png" alt="Traffic Context Menu" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Repeater</strong><br/>
<img src="docs/screenshots/repeater.png" alt="Repeater" width="100%" />
</td>
<td align="center">
<strong>Intruder · Sniper Mode</strong><br/>
<img src="docs/screenshots/intruder.png" alt="Intruder" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Scanner</strong><br/>
<img src="docs/screenshots/scanner.png" alt="Scanner" width="100%" />
</td>
<td align="center">
<strong> Templates</strong><br/>
<img src="docs/screenshots/templates.png" alt="Templates" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Sitemap · Tree View</strong><br/>
<img src="docs/screenshots/sitemap-tree.png" alt="Sitemap Tree" width="100%" />
</td>
<td align="center">
<strong>Sitemap · Diagram View</strong><br/>
<img src="docs/screenshots/sitemap-diagram.png" alt="Sitemap Diagram" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>OSINT · DNS Records</strong><br/>
<img src="docs/screenshots/osint-dns.png" alt="OSINT DNS" width="100%" />
</td>
<td align="center">
<strong>Token Sequencer</strong><br/>
<img src="docs/screenshots/sequencer.png" alt="Sequencer" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Decoder / Codec Tools</strong><br/>
<img src="docs/screenshots/tools-decoder.png" alt="Tools Decoder" width="100%" />
</td>
<td align="center">
<strong>Sitemap · Mixed Explore View</strong><br/>
<img src="docs/screenshots/sitemap-mixed.png" alt="Sitemap Mixed" width="100%" />
</td>
</tr>
</table>
<details>
<summary><strong>Settings Panels</strong> (click to expand)</summary>
<table>
<tr>
<td align="center" width="50%">
<strong>General · System Info</strong><br/>
<img src="docs/screenshots/settings-general.png" alt="Settings General" width="100%" />
</td>
<td align="center" width="50%">
<strong>MCP Server · IDE Integration</strong><br/>
<img src="docs/screenshots/settings-mcp.png" alt="Settings MCP" width="100%" />
</td>
</tr>
<tr>
<td align="center">
<strong>Proxy Configuration</strong><br/>
<img src="docs/screenshots/settings-proxy.png" alt="Settings Proxy" width="100%" />
</td>
<td align="center">
<strong>Appearance · Themes</strong><br/>
<img src="docs/screenshots/settings-appearance.png" alt="Settings Appearance" width="100%" />
</td>
</tr>
</table>
</details>
Architecture
How it flows. The pentester drives the React UI; every action travels through Tauri IPC into the Rust engine. The MITM proxy MITM-decrypts the browser's TLS, then re-originates each upstream request through a BoringSSL stack tuned to Chrome 137's exact ClientHello + JA3/JA4 + HTTP/2 SETTINGS fingerprint — so Cloudflare/Akamai/DataDome/PerimeterX see real Chrome. WonderBrowser is the bundled Chrome-for-Testing 148 with a stealth extension shipped in the install (no system Chrome dependency). Scanner and intruder probe the target, posting blind-vuln callbacks to the integrated OAST listener callback_urls. In parallel, any MCP-compatible AI client speaks JSON-RPC to the same 85-tool surface — including 24 pentest-grade browser tools that share state with the proxy via a stable request-ID space — so a human and an AI agent can in the same target with the exact same primitives.
Tech Stack
| Component | Technology |
|-----------|------------|
| Backend | Rust 1.78+ |
| Framework | Tauri 2.x |
| Frontend | React 19, TypeScript, Vite, Zustand |
| Proxy | tokio, nati, rsa/x509-cert (dynamic CA) |
| TLS impersonation | wreq + boring-sys2 (BoringSSL), webpki-root-certs (Mozilla CA bundle) — win+mac only, Linux fallback to nati |
| Browser | Bundled Chrome-for-Testing 148.0.7778.97 (SHA-256- lazy download) + WonderSuite extension (MV3) |
| Browser MCP | Persistent CDP WebSocket (tokio-tungstenite) with multiplexed request correlation + a11y-tree snapshot engine |
| MCP | Axum HTTP server (JSON-RPC 2.0), dedicated thread/runtime |
| HTTP Client | reqwest with TLS 1.3 |
| OAST | Embedded axum HTTP listener + tokio UDP DNS server + raw-TCP SMTP listener, shared INTERACTIONS log |
Download
Pre-built, code-signed installers for all major platforms are published on every release. The Tauri updater also ser binaries — running WonderSuite checks latest.json on startup and offers an in-app update when a new is a.
<di="center">
| Platform | Installer | Notes |
|---|---|---|
| Windows 10/11 (x64) | .msi · .exe (NSIS) | Bundles WinDivert 2.2.2 — one UAC consent on first SYN scan, none afterward |
| macOS (Apple Silicon) | WonderSuite_*_aarch64.dmg | M1 / M2 / M3 / M4 native |
| macOS (Intel) | WonderSuite_*_x64.dmg | x86_64 native |
| Linux (x86_64) | .AppImage · .deb · .rpm | Raw-socket SYN scan needs CAP_NET_RAW |
📥 Latest release → · All releases → · Changelog →
!Total downloads
!Latest release downloads
!Stars
</div>
Every artifact is reproducibly built in GitHub Actions and ships with a Tauri-updater signature (.sig next to each installer). a download against the published Ed25519 public key in src-tauri/tauri.conf.json (plugins.updater.pubkey).
Getting Started
> Skip this section if you just want to run WonderSuite — grab a pre-built installer above. The instructions below are for building from source.
Prerequisites
webkit2gtk-4.1, libayatana-appindicator3-dev, librs, build-essentialInstallation (from source)
De
Production Build
Output is written to src-tauri/target/release/bundle/ (.msi, .exe, .dmg, .AppImage, .deb, depending on platform).
A helper build-release.cmd is provided for Windows de (opens a console window, prints the artifact paths when done).
Connecting an AI Client to MCP
The MCP ser on . The Settings → MCP Server tab auto-detects supported IDEs (Cursor, Windsurf, VS Code, Antigravity, Gemini CLI, Void) and offers one-click install. Manual config snippet:
Skill File — Teach Your AI How to Use WonderSuite
WonderSuite ships a project-le skill that turns your AI client into a senior pentester instead of a tool-calling chatbot. The skill is at .claude/skills/wondersuite.md and contains:
browser_open vs browser_attach vs browser_attach({auto_launch, use_real_profile})PROXY_DOWN, STALE_REF, CDP_LOST, PROFILE_LOCKED …)Install into your own project (one-time):
Or clone the repo and copy the file:
Use: open a Claude Code / compatible session in that directory. The skill auto-loads — its frontmatter tells Claude to apply it whenever the user says things like "test this target", "scan", "pentest", "find ", "attach to my browser". You can also force-invoke it with /wondersuite.
Keep it current: the skill is with the rest of the repo. After a release, re-run the install command above to pick up new tools / workflow impro.
Project Structure
Responsible Use
WonderSuite is intended for authorized security testing, defensi, and educational use. Only test systems you own or ha written permission to assess. The authors and contributors are not responsible for misuse.
Contributing
Contributions are welcome and very much appreciated. WonderSuite is open source under the MIT License and we'd love your help to make it better.
Whether you want to:
src-tauri/src/mcp/handlers/ for examples, and register the tool in src-tauri/src/mcp/mod.rs::tool_definitions()There's no CLA. By contributing, you agree that your contributions will be licensed under the project's MIT License.
Please run npm run tauri build locally before submitting a PR to make sure it still builds across the full pipeline. If you touch the Rust side, cargo check --manifest-path src-tauri/Cargo.toml is a quick sanity check.
Copyright
The WonderSuite name and the original codebase are © SFR De (<). The project is licensed under the MIT License — you may use, modify, fork, and redistribute it under those terms. Contributions remain copyrighted by their respecti but are licensed to the project (and downstream users) under the same MIT terms.
Star History.
![Star History Chart]()
License
Released under the MIT License © 2026 SFR De.
---
<di="center">
<sub>Built with Rust, Tauri, and React · Made by <a href=" De</a></sub>
</div>
项目信息
开发语言:Rust
Star 数:50
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕AI-Powered Offensive Security Research Engine - desktop-native security testing platform with native MCP integration. 90 tools, MITM proxy, stealth browser, autonomous AI agent. Built on Tauri + Rust + React.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | WonderSuite-Ai-Bug-Bounty - AI-Powered Offensive Security Research Engine - de |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:45:57 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 398 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |