 安全软件
点击放大
EmbedXPL-Forge - Embedded Device Security Assessment Framework — 70
项目说明
<p align="center">
<img src="docs/img/embedxpl-forge-banner_16x9.png" alt="EmbedXPL-Forge" width="100%">
</p>
!Python


![XPL Suite]()
![Issues]()
![Last Commit]()
---
> Platform Note: This framework is designed and tested primarily on Linux (Debian/Ubuntu/Kali). Most hardware-dependent modules (wireless adapters, USB devices, raw socket access, firmware tools) require Linux. Running on Windows or macOS may cause errors or limited functionality in many modules. Linux is strongly recommended for maximum compatibility.
---
EmbedXPL-Forge
Embedded & Perimeter Security Assessment Framework
EmbedXPL-Forge is an open-source exploitation and scanning framework for security professionals auditing routers, switches, IP cameras, NVR/DVR, GPON ONTs, ISP CPEs, printers, IoT, OT/ICS, and embedded edge devices. It provides 2800+ acti co credential testing, exploitation, network scanning, payload generation, RTSP camera attacks, firmware manipulation, multi-language PolyExploit orchestration, and a full printer arsenal — with 700+ CVEs mapped across 114+ and an APT Group Attack Engine that reproduces real-world nation-state attack chains.
> : 3.2.0
Features
pip install embedxpl[nse])tools/phase_gate.py ensures every module passes import, anti-FP, reference, and code quality checks before mergeSupported Device Types
| Type | Co | Description |
|------|----------|-------------|
| Routers / GPON ONT / CPE | 580+ modules | SOHO routers, enterprise gateways, GPON CPE/ONT (primary focus) |
| IP Cameras / NVR / DVR | 60+ modules | Hik, Dahua, Axis, Reolink, Amcrest, Uniview, Tapo, Swann, ANNKE, Edimax, Intelbras, Grandstream, Foscam, Xiongmai OEM, M, and 20+ more |
| Printers / MFP | 185+ modules | HP, Canon, Lexmark, Xerox, Ricoh, Brother, Epson, Kyocera, Samsung; IPP/PJL/LPD/WSD/CUPS chains |
| NAS (Network Storage) | 20+ modules | QNAP, Synology, D-Link NAS, Zyxel NAS |
| VPN / Firewall Appliances / NGFW | 202 modules | Palo Alto, Fortinet, Cisco ASA/FTD/FMC, Check Point, Juniper, SonicWall, Sophos, WatchGuard, Zyxel, F5 BIG-IP, Citrix/NetScaler, Ivanti, Pulse Secure, pfSense, OPNsense, Barracuda, Imper, Huawei USG, Stormshield, Hillstone, Sangfor, H3C, Radware, Symantec ProxySG, Trend Micro TippingPoint, Trellix, Arista EOS, OpenVPN AS, Phoenix Contact mGuard, Siemens SCALANCE, Moxa EDR, VyOS, IPFire, Kerio, Cisco Meraki, Array Networks + OT/ICS protocol bypass modules |
| Switches L2/L3 | 3 modules | Managed switches (Cisco, D-Link, NETGEAR) |
| SOHO Edge | 9 modules | Tra, NAS, wireless APs |
| ICS / OT / Industrial | 35+ modules | PLCs, SCADA, Modbus, S7comm, EtherNet/IP, Uni Robots PolyScope 5 |
| Smart Home / Maritime | 10+ modules | eNet SMART HOME, OpenRemote IoT, Metis maritime WIC/DFS |
| Embedded OS | 25+ modules | RIOT OS, OpenWrt, , QNX, wolfSSL devices, Tuya Arduino SDK |
Supported
Network / Router / CPE: 2Wire · 3Com · ActionTec · Alcatel-Lucent · Alpha Networks · Arris · Aruba · Asmax · Astoria · ASUS · Belkin · BHU · Billion · Binatone · Calix · CERIO · Cisco · Cobham · Comtrend · D-Link · DD-WRT · Draytek · EasyBox (Arcadyan) · Edimax · EE BrightBox · EnGenius · FiberHome · Fortinet · Freebox · GL.iNet · GPON · HooToo · Huawei · Intelbras · IPFire · Juniper · LG · Linksys · Mercury · MiFi (Novatel) · MikroTik · MitraStar · Motorola · Mo · Netcore · NETGEAR · Netsys · Obser · OpenWrt · RuggedCom · Ruijie · Seagate · SerComm · Shuttle · Sitecom · SMC · SonicWall · Starbridge · Technicolor · Tenda · Thomson · TOTOLINK · TP-Link · TRENDnet · Ubee · Ubiquiti · Unicorn · UTStarcom · Wavlink · Xiaomi · Zhone · Zoom · ZTE · ZyXEL
Cameras / NVR / DVR: Hik · Dahua · Axis · Reolink · Amcrest · Uniview (UNV) · Tapo (TP-Link) · Swann · ANNKE · Edimax · Intelbras · Grandstream · Foscam · Acti · A · Beward · Brickcom · Cisco cameras · Geuterbruck · Honeywell cameras · Jo · Siemens cameras · Xiongmai (OEM) · Zivif · M DVR · Generic P2P WiFi cameras · Generic DVR/NVR OEM
Printers / MFP: HP LaserJet/PageWide · Canon imageRUNNER/imageClass · Lexmark CX/CS/MS/MX · Xerox WorkCentre/AltaLink/ · Ricoh MP/Aficio/SP · Brother MFC/DCP · Epson WorkForce · Kyocera ECOSYS · Samsung SyncThru · Generic IPP/PJL/LPD/CUPS/WSD
NAS / VPN / Firewall / Security: QNAP · Synology · D-Link NAS · Zyxel NAS · Ivanti · SonicWall · Fortinet (FortiOS/FortiGate/FortiWeb/FortiClient EMS) · Palo Alto (PAN-OS) · Cisco ASA/FTD · CheckPoint · Sophos XG · WatchGuard Firebox · A
ICS / OT / Robotics: Uni Robots (UR3/UR5/UR10/UR16) · OpenPLC · Modbus TCP · Siemens S7 · EtherNet/IP CIP · BACnet · DNP3 · PROFINET DCP
Smart Home / Maritime / Embedded OS: eNet SMART HOME · OpenRemote IoT · Metis WIC/DFS (maritime) · RIOT OS · OpenWrt · · QNX · Zephyr · wolfSSL · Tuya arduino-tuyaopen
Installation
Option 1 — PyPI (recommended)
Option 2 — With Nmap NSE scripts
> Note: On Linux/macOS the install step may require sudo to write to /usr/share/nmap/scripts/.
> Run: sudo python -m embedxpl.nse install
Option 3 — From source
Option 4 — Python module
Quick Start
Usage
Interacti
Common Commands
| Command | Description |
|---------|-------------|
| use <module> | Select a module |
| show options | Display configurable options |
| show info | Display module metadata and references |
| show devices | List supported device types |
| set <option> <value> | Configure an option |
| check | if target is |
| run | Execute the module |
| search <term> | Search modules by keyword |
| discover [subnet] [--timing T0-T5] [--fresh] | Scan subnet, fingerprint targets, suggest modules |
| sessions list\|show\|delete\|export\|purge | Manage persistent scan history per host |
| apt | List APT groups with reproducible attack chains |
| apt show <group> | View attack chain details (MITRE ATT&CK, CVEs, modules) |
| apt search <device\|CVE> | Find APT groups targeting a device or CVE |
| apt run <group> [#] | Execute APT attack chain (all or specific attack) |
APT Group Attack Engine
Network Discovery
Discovery uses a multi-phase pipeline: ARP sweep → Nmap (multi-method host probes) → Scapy → TCP connect fallback. Results are matched against the module catalog and filtered by /model. The IEEE OUI database (embedxpl/data/oui.txt) resolves MAC addresses to with online-first lookup and local fallback. When a host exposes WiFi capabilities, the tool recommends WirelessXPL-Forge for wireless-specific attacks.
Timing profiles (T0–T5) mirror Nmap con:
| Profile | Delay | Use case |
|---------|-------|----------|
| T0 | paranoid — 300s | IDS e |
| T1 | sneaky — 15s | Quiet audits |
| T2 | polite — 2s | Minimal impact |
| T3 | normal — 0.5s | Default |
| T4 | aggressive — 0.1s | Fast LAN scans |
| T5 | insane — 0s | CTF / lab only |
Session Management
Sessions are stored in ~/.exf_sessions/ as JSON, keyed by SHA-256 of IP+MAC. On re-discovery of a known host, already-tested modules are shown as [Tested] and skipped by default.
AutoPwn Scanner
RTSP Camera Engine
Full-featured RTSP attack pipeline with Python-nati co all standard RTSP transport modes.
Transport Modes
| Mode | Port | Class / Method |
|------|------|---------------|
| rtsp | 554 | RTSPClient(host, port) |
| rtsps | 443/8443 | RTSPClient(host, port, use_tls=True) |
| http | 80/8080 | RTSPClient(host, port, tunnel_http=True) |
| https | 443/8443 | RTSPClient(host, port, use_tls=True, tunnel_http=True) |
| auto | any | RTSPClient.from_scheme(host, port, "http") |
Attack Pipeline
Expected output:
Skip-Scan Mode (Known Hosts)
Expected input/output:
RTSP-o Tunnel
Used when cameras are behind HTTP proxies or corporate firewalls that block TCP/554.
Expected input/output:
RTSP Module (Interactive)
Nmap NSE Scripts
EmbedXPL-Forge includes 7 custom Nmap NSE scripts for IoT/camera scanning and C.
Installation
Expected output:
List / Info
NSE Script Reference
#### embedxpl-rtsp-discover — RTSP Service Discovery
Detects RTSP services, grabs the Server: banner, identifies , lists supported methods, and cross-references known CVEs.
Expected output:
#### embedxpl-camera-identify — Deep Camera Fingerprinting
Multi-protocol identification: probes HTTP/HTTPS web UI, RTSP banner, and ONVIF. Extracts , model, firmware, serial, and MAC.
Expected output (Hik):
#### embedxpl-hik — Hik C
Acti of C (RCE via /SDK/webLanguage, CVSS 9.8) and C (auth bypass snapshot).
Expected output:
#### embedxpl-dahua-vuln — Dahua C
Tests C (auth bypass, CVSS 9.8), C (user disclosure), C (legacy DVR). Also covers Dahua OEMs: Amcrest, Intelbras, T, ANNKE.
Expected output:
#### embedxpl-rtsp-creds — RTSP Default Credential Tester
Tests 18 default credential pairs across 9+ common RTSP routes using Basic auth. Reports the first match.
Expected output:
#### embedxpl-iot-c — Multi- C
Detects and 10 active C Hik, Dahua, D-Link NAS, Reolink, Uniview, QNAP, SonicWall, and GPON.
Expected output:
#### embedxpl-camera-snapshot — Unauthenticated Snapshot Access
Probes 16 snapshot endpoints. Reports any URL returning image/* without credentials. Optionally saves JPEG files locally.
Expected output:
Run All NSE Scripts
Uninstall:
Firmware Exploitation
What it does:
1. Detects firmware format (TRX, DLOB, SEAMA, WRGG, raw binary)
2. Injects reverse shell backdoor at a suitable offset
3. Recalculates CRC32/MD5 checksum
4. Uploads flash endpoint (bypassing auth where applicable)
5. Waits for device reboot and backdoor execution
PolyExploit Orchestrator
Enables runtime C/C++ compilation and multi-language script execution for exploits not portable to pure Python.
C/C++ Runtime Compilation
Multi-Language Script Execution
New in v3.1.0 — CVE 2026/2025/2024 + Printer Domain + Quality Gates
54 new modules across printers, embedded OS, ICS/OT, smart home, maritime IoT, and 2026 Pwn2Own chains. Key highlights:
2026 Pwn2Own Chains
Critical 2026 CVEs
Printer Arsenal Examples
Backdoor / Factory Password Co
27+ exploit modules targeting factory passwords, hardcoded backdoors, default WPA key generation algorithms, and DNS hijack CSRF across legacy and modern SOHO routers. Key examples:
All 27 new /modules:alcatel_lucent · alpha_networks · astoria · binatone · ddwrt · easybox · ee · freebox · mifi · motorola · observa · ruggedcom · seagate · sitecom · starbridge · ubee · unicorn · utstarcom · zoom · plus belkin, netgear, trendnet gap-fills.
Module Structure
Extended Module Co
This section documents the ISP device modules, backdoor/factory password exploits, RTSP client framework, OSINT tools, and specialized security modules.
---
ISP Device Security Modules
Exploits and scanners targeting ISP-issued CPEs and IP cameras commonly deployed by internet pro (Sercomm-based ONTs, GPON CPEs, and ISP-branded devices).
| Device | CVE | Module Path | Attack Type |
|--------|-----|-------------|-------------|
| TP-Link TL-SC3171 / SC4171 / SC4171G | C | exploits/cameras/tplink/tl_sc_series_cmd_inject_c | Command Injection (unauth) |
| TP-Link TL-SC3171 / SC3130 | C | exploits/cameras/tplink/tl_sc_series_unauth_firmware_upload_c | Unauthenticated Firmware Upload |
| D-Link DCS-932L | C | exploits/cameras/dlink/dcs_932l_light_sensor_rce_c | Light Sensor RCE |
| D-Link DCS-932L | C | exploits/cameras/dlink/dcs_932l_admin_cmd_inject_c | Admin Panel Command Injection |
| D-Link DCS-933L | C | exploits/cameras/dlink/dcs_933l_admin_cmd_inject_c | Admin Panel Command Injection |
| ZTE ZXHN H267N / H268N | C | exploits/routers/zte/zxhn_h267n_h268n_dos_c | Denial of Service |
| ZTE ZXHN H298A / H108N | C | exploits/routers/zte/zxhn_h298a_cred_dump_c | Credential Dump (ETHCheat) |
| Intelbras IWR routers | - | exploits/routers/intelbras/iwr_luci_rpc_rce | LuCI RPC Unauthenticated RCE |
| Multi- BR ISP scanner | - | scanners/specialized/br_isp_scanner | Acti + vuln check |
Usage examples:
Notes: C affects ZTE ZXHN H298A 1.1 and H108N 2.6. No authentication required.
Legal: Use only on devices you own or ha authorization to test.
---
Legacy Router Backdoor and Factory Password Modules
Classic router backdoor and factory password exploits implemented in the EmbedXPL-Forge module format.
| Device | CVE / Reference | Module Path | Attack Type |
|--------|----------------|-------------|-------------|
| Cobham A 700 SATCOM | C | exploits/specialized/vsat/cobham_a014_2943 | Admin Password Reset (unauth) |
| Huawei HG8245H | - | osint/keygen/huawei_hg8245_wpa_keygen | WPA Default Key Generator |
| Alcatel-Lucent OmniPCX Enterprise | - | exploits/voip/alcatel_lucent/omnipcx_enterprise_mastercgi_rce | masterCGI Unauthenticated RCE |
| Linksys E-Series (The Moon) | EDB-31683 | exploits/routers/linksys/eseries_themoon_rce_tmunblock | tmUnblock.cgi RCE |
| NETGEAR DGN2200 | EDB-24665 | exploits/routers/netgear/dgn2200_open_telnetd_rce | open-telnetd Unauthenticated RCE |
| Siemens FlexiISN | - | exploits/routers/siemens/flexiisn_auth_bypass | Authentication Bypass |
| Thomson BTHomeHub | - | exploits/routers/thomson/bthomehub_ | VoIP Configuration Hijack |
| AT&T 2Wire Gateway | - | exploits/routers/two_wire/atandt_gateway_crlf_dos | CRLF Injection / DoS |
Usage examples:
Notes: The Moon worm (Linksys E-Series C tmUnblock.cgi without authentication on firmware < 2.0.08.
Legal: Use only on devices you own or ha authorization to test.
---
RTSP Client Framework
A pure Python RFC 2326 RTSP/1.0 client library used as the foundation for all RTSP camera attack modules.
Module: network/rtsp/rtsp_client.py - RTSPClient class
Features:
with RTSPClient(...) as client)Usage example:
Requirements: Python 3.8+, no external dependencies.
---
FCC-ID Lookup Module
OSINT module that queries the FCC Equipment Authorization database to retrie details from FCC ID codes found on hardware labels.
Module: osint/fcc_id_lookup.py
Usage example:
Tips:
GRANTEE_CODE-PRODUCT_CODE)osint/github_recon to find public firmware repos for the deviceRequirements: Internet access, requests library.
---
Camera URL Generator
Generates known camera stream URLs based on , model, and firmware , using the iSpy camera database format.
Module: osint/camera_url_generator.py
Usage example:
Tips:
network/rtsp/rtsp_route_brute to enumerate liset all_ true to dump all known URLs---
Traffic Enforcement Security Modules
Modules targeting traffic enforcement infrastructure (toll RSUs, radar systems, ANPR cameras).
#### Kapsch TrafficCom RSU EFI Shell (C)
Module: exploits/specialized/traffic_enforcement/kapsch_rsu_efi_shell_c
: Kapsch Road-Side Units (RSUs) used in electronic tolling lack UEFI Secure Boot enforcement and BIOS password protection, allowing physical attackers to drop into an EFI interacti and access the full filesystem.
Impact: Configuration extraction, TLS private key theft, implant installation, toll enforcement bypass.
Usage example:
Physical exploitation steps:
1. Open RSU enclosure (tamper-e screws)
2. Connect USB keyboard and monitor to RSU mainboard
3. Power cycle - press ESC/DEL/F2 during POST
4. Na: Boot Manager -> EFI Internal Shell
5. Access filesystem: fs0:\efi\config\ for configuration extraction
Requirements: Physical access to RSU hardware (monitor + USB keyboard), or network access to management interface for banner detection.
Legal: Unauthorized access to toll enforcement infrastructure is a criminal offense. Use only on units you own or ha written authorization to assess.
---
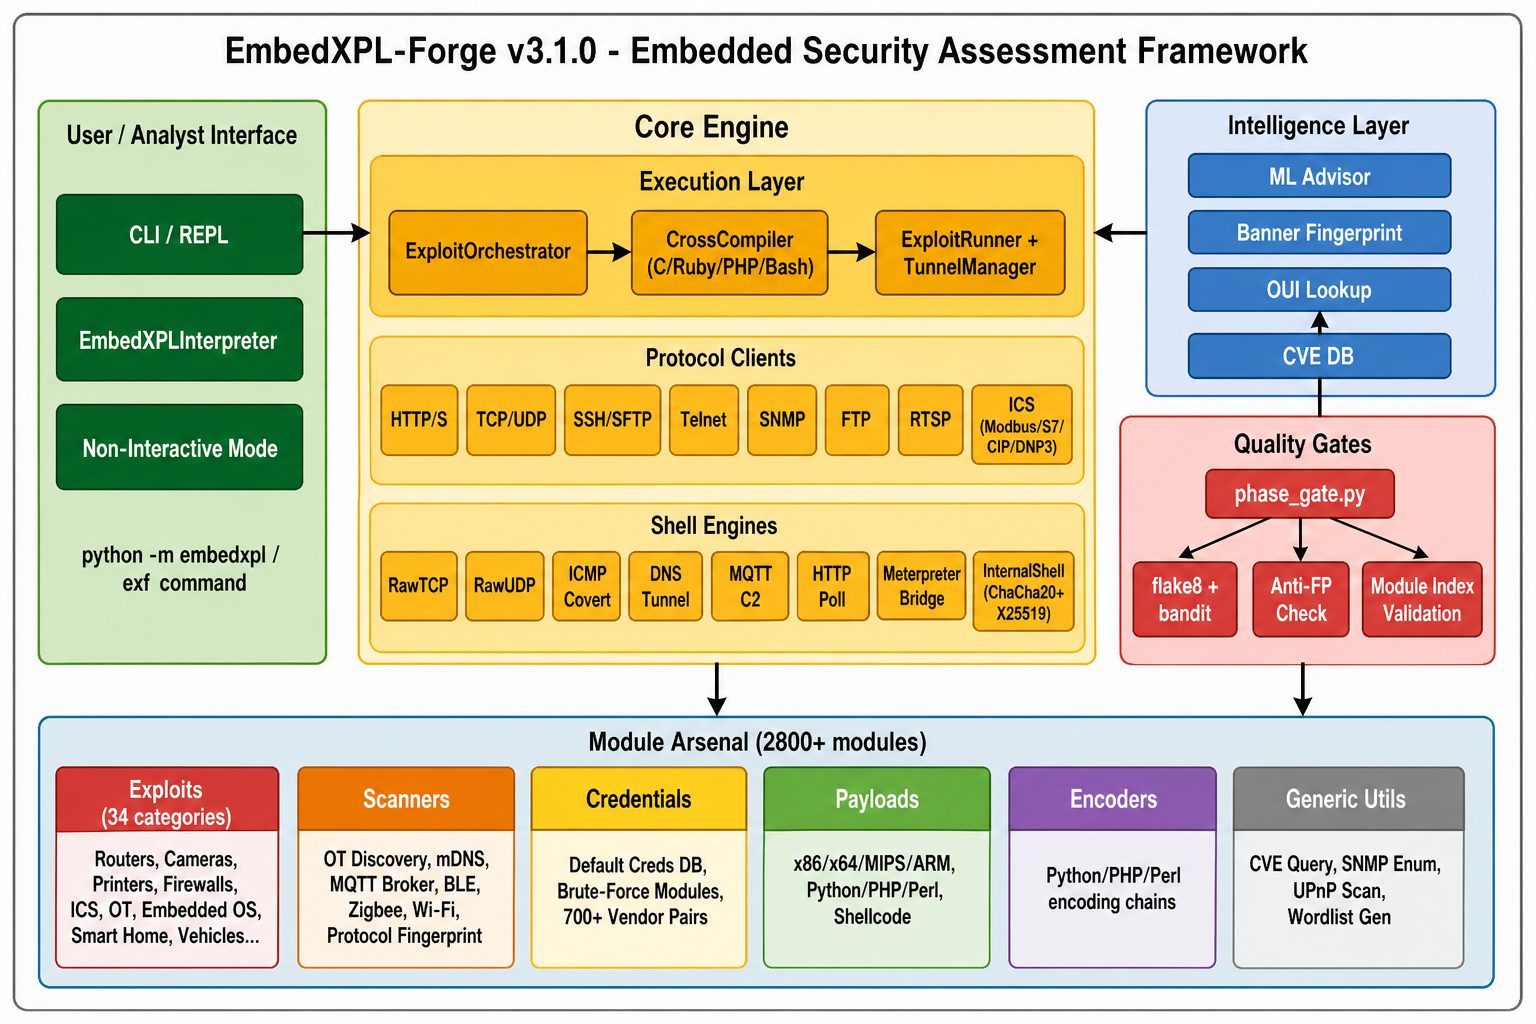
Framework Architecture (v3.1.0)
Component Architecture
Full layered view of the framework: CLI layer, Core Engine (orchestrator, protocol clients, shell engines), Intelligence Layer (ML, OUI, CVE DB), Quality Gates, and the 2800+ module arsenal organized by category.
<p align="center">
<img src="docs/assets/embedxpl_architecture.png" width="960" alt="EmbedXPL-Forge Component Architecture v3.1.0"/>
</p>
Audit & Exploitation Flow
End-to-end data flow from target input through discovery, fingerprinting, module selection, exploitation, and reporting.
<p align="center">
<img src="docs/assets/embedxpl_flow.png" width="960" alt="EmbedXPL-Forge Exploitation Flow v3.1.0"/>
</p>
Architecture & Attack Surface Maps
Attack surface maps showing module co per access , in the style of operational security diagrams.
Source files in docs/diagrams/architecture/.
Module Architecture O
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_o.png" width="900" alt="EmbedXPL-Forge Architecture O"/>
</p>
APT Group Attack Chains
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_apt_chains.png" width="900" alt="APT Group Attack Chains"/>
</p>
SOHO Router Attack Surface
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_soho_router.png" width="900" alt="SOHO Router Attack Surface"/>
</p>
TP-Link Attack Surface (APT28/GRU Campaign)
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_tplink_apt28.png" width="900" alt="TP-Link APT28 Attack Surface"/>
</p>
MikroTik RouterOS Attack Surface
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_mikrotik.png" width="900" alt="MikroTik Attack Surface"/>
</p>
GPON ONT Attack Surface (Huawei EG8145)
<p align="center">
<img src="docs/diagrams/architecture/exf_arch_gpon_ont.png" width="900" alt="GPON ONT Attack Surface"/>
</p>
Requirements
nmap (binary) for enhanced network discovery and NSE scriptsmasscan for high-speed RTSP discoverygcc/clang for PolyExploit C/C++ runtime compilationmsfconsole for Metasploit integration Python dependencies (auto-installed):requests, paramiko, pysnmp, pycryptodome, scapy, colorama, rich, python-nmap, aiohttp
NSE extras (pip install "embedxpl[nse]"):python-nmap (already included in core)
Full list: requirements.txt
Legal Disclaimer
EmbedXPL-Forge is intended for authorized security testing and research only. Use this tool exclusively on systems you own or ha written permission to test. Unauthorized access to computer systems is illegal. The authors assume no liability for misuse.
License
BSD License — see LICENSE for details.
---
Contact
Support / general inquiries:
Security issues: SECURITY.md
---
André Henrique
| | |
|---|---|
| GitHub | |
| X / Twitter | |
| LinkedIn | mrhenrike |
União Geek
| | |
|---|---|
| Website | uniaogeek.com.br |
| Blog | uniaogeek.com.br/blog |
| GitHub | Uniao-Geek |
| Instagram | |
---
License: BSD-3-Clause License - Copyright (c) 2026 União Geek
Created by: André Henrique () | União Geek
Leia em Português - Command co - Wiki
项目信息
开发语言:Python
Star 数:50
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs, IoT/embedded edge.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | EmbedXPL-Forge - Embedded Device Security Assessment Framework — 70 |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:46:01 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 431 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |