 安全软件
点击放大
log4shell-finder - Fastest filesystem scanner for log4shell (CVE-2021
项目说明
log4shell-finder - Fastest file system scanner for log4j instances

Python port of log4j-detector is copyright (C) Copyright 2021 Mergebase Software Inc. Licensed .
> *Moti for porting to Python was to impro, reduce memory consumption and increase code readability. See below section about performance comparism.*
>
> And it seems this is the fastest scanning tool with lowest memory requirement
Identifies log4j (1.x), reload4j (1.2.18+) and log4j-core (2.x) on your file-system to
C,
C and many others - see table below.
It is able to find instances embedded in larger applications
several layers deep. Works on Linux, Windows, Mac or anywhere else Python 3.8+ runs.
Can correctly detect log4j inside executable spring-boot jars/wars, dependencies blended
into uber jars, shaded jars, and even
exploded jar files just sitting uncompressed on the file-system (aka *.class).
It can also handle shaded class files - extensions .esclazz (elastic) and .classdata (Azure).
Ja extensions searched: .zip, .jar, .war, .ear, .aar, .jpi,.hpi, .rar, .nar, .wab, .eba, .ejb, .sar, .apk, .par, .kar
Detected
| Detects | CVE | CVSSv3 | Se | Java | Vuln from | to | Fixed in | library |
| :----- | :------------- | :----- | :------- | :---- | :--------- | :----------------------------- | :------------------ | :-- |
| YES | C | 10.0 | Critical | 8 | 2.0-beta9 | 2.14.1 | 2.15.0 | log4jv2 |
| YES | C | 9.8 | Critical | 7 | 2.0-alpha1 | 2.8.1 | 2.8.2 | log4jv2 |
| YES | C | 9.8 | Critical | | 1.2.0 | 1.2.17 | nofix | log4jv1 |
| YES | C | 9.0 | Critical | 7/8 | 2.0-beta9 | 2.15.0 excluding 2.12.2 | 2.12.2/2.16.0 | log4jv2 |
| YES | C | 9.8 | Critical | | 1.2.0 | 1.2.17 | nofix / 1.2.18.1 | log4jv1, reload4j |
| YES | C | 9.8 | Critical | | 1.2.0 | 1.2.17 | nofix / 1.2.18.1 | log4jv1, reload4j |
| YES | C | 8.8 | High | | 1.0 | 1.2.17 | nofix / 1.2.18.1 | log4jv1, reload4j |
| YES | C | 7.5 | High | - | 1.0 | 1.2.17 | nofix | log4jv1 |
| YES | C | 6.6 | Medium | 6/7/8 | 2.0-alpha7 | 2.17.0, excluding 2.3.2/2.12.4 | 2.3.2/2.12.4/2.17.1 | log4jv2 |
| - | C | 6.6 | Medium | - | 1.0 | 1.2.7 | 1.2.8 | logback |
| YES | C | 5.9 | Medium | 6/7/8 | 2.0-beta9 | 2.16.0, excluding 2.12.3 | 2.3.1/2.12.3/2.17.0 | log4jv2 |
| - | C | 3.7 | Low | 7/8 | 2.0-alpha1 | 2.13.1 | 2.12.3/2.13.2 | log4jv2 |
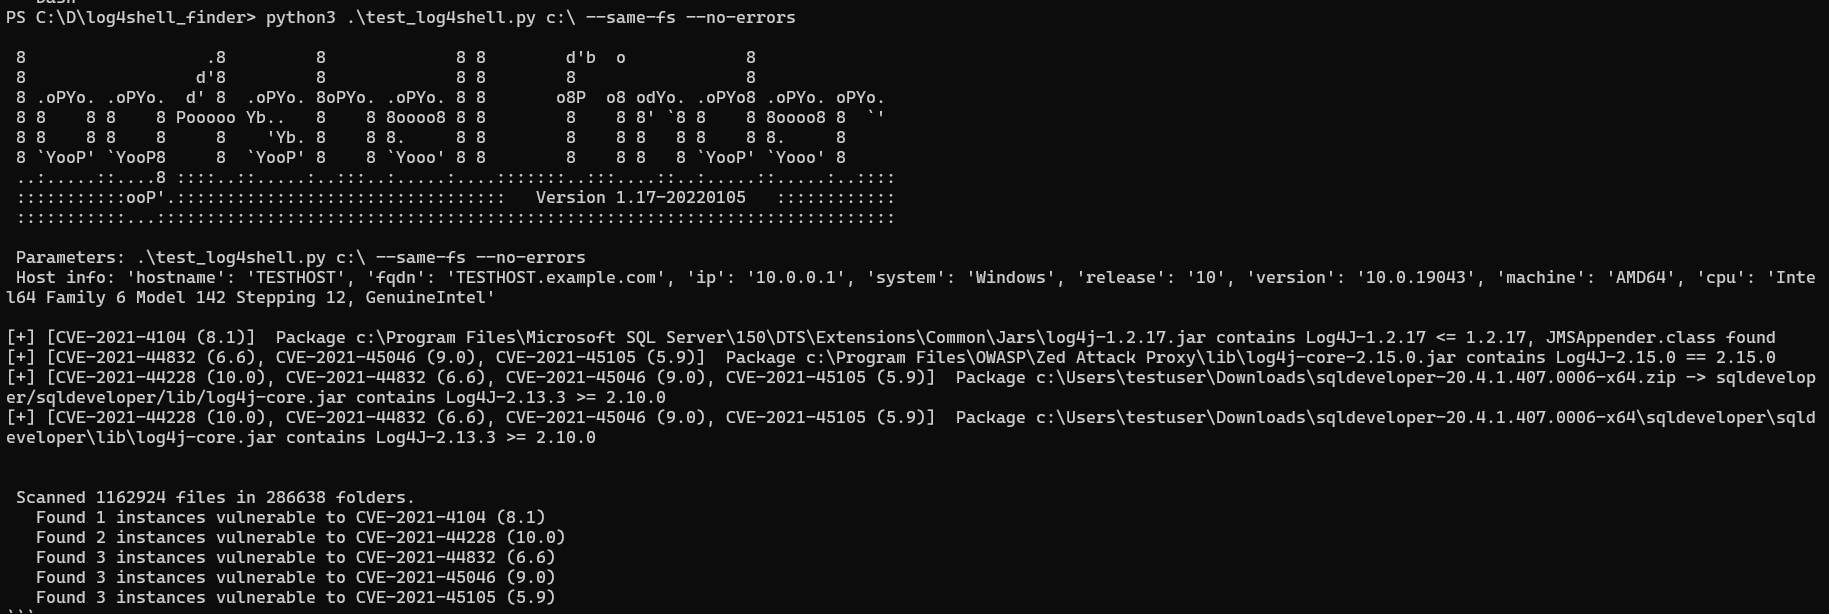
Each instance is reported with apropriate list of CVEs. For each C library file is being analyzed whether the recommended
workarounds (e.g. JndiLookup.class or JMSAppender.class removed) has been applied and in that case is considered as non-.
Status STRANGE is reported for archives with log4j-core pom.properties file, but without actual bytecode
classes, ususally those are source packages and can be ignored.
> Warning --fix feature is experimental, use it on your own risk, make sure you backup your jar files prior using it.
Argument --fix attempts to rename instances of JndiLookup.class into JndiLookup.vulne, thus pre the class
from loading. Within Ja it's done via in place rename, does not require re-zipping of the archive and is
instant fast.
> Binaries are a for Linux 64bit, MS Windows 64bit and 32bit - see Releases
>
> Minimum supported Python is 3.8. According to my testing Python 3.6 zip implementation cannot open many .jar files from my test data.
Performance
log4shell finder is optimized for performance and low memory footprint.
Updated on 23.1.2022, performance measured on a directory with 26237 files in 2005 folders.
> Runtime reduced by half, memory consumtion by 2/3, file system reads byt at least 90%
log4shell-finder (this tool)
log4j-finder ()
log4j-detector ()
log4j2-scan ()
Changelog
1.22-20220222
all parameter--no-cs to omit cs to allow easier merging of results from multiple hosts--threads parameter to manually tune number of scanning threads--c parameter in order to write "CLEAN" line to cs in case no log4j library detected--c parameter in order to write "STATS" line to cs with runtime in seconds and number of files and folders scanned1.21-20220109
--fix command in 1.19 and 1.20 could corrupt .jar archives. For previous changes see Release Notes
Usage
Either run from a python interpreter or use the Windows/Linux binaries from the dist folder.
> Beware to run it as a user with access (at least read-only) to the whole filesystem. log4shell-finder tra
> just folders it can access to, not reporting permission denied errors.
Does not require any extra python libraries.
Compile binaries
The binaries were produced with:
If you want to build a 32bit , install a 32bit Python interpreter, install pyinstaller with:
and then:
Sample execution
On Linux you may run like:
for MS Windows:
On MS Windows:
Make sure you' pywin32, e.g. via pip install pywin32
Scanning Kali, with progress reported every second and excluded zip-bomb folder:
JSON output
Output to json contains all found items as well as host information:
CS
has following columns:
项目信息
开发语言:Python
Star 数:39
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305, CVE-2022-23307 ... ) instances of log4j library. Excellent performance and low memory footprint.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | log4shell-finder - Fastest filesystem scanner for log4shell (CVE-2021 |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:48:10 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 352 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |