 安全软件
点击放大
OpenVulnScan - A simple vulnerability scanning application built
项目说明
Open
A simple scanning application built with FastAPI.
Setup
1. Install dependencies:
2. Run the application:
OR
if running :
Windows:
Linux:
3. Access the web interface:
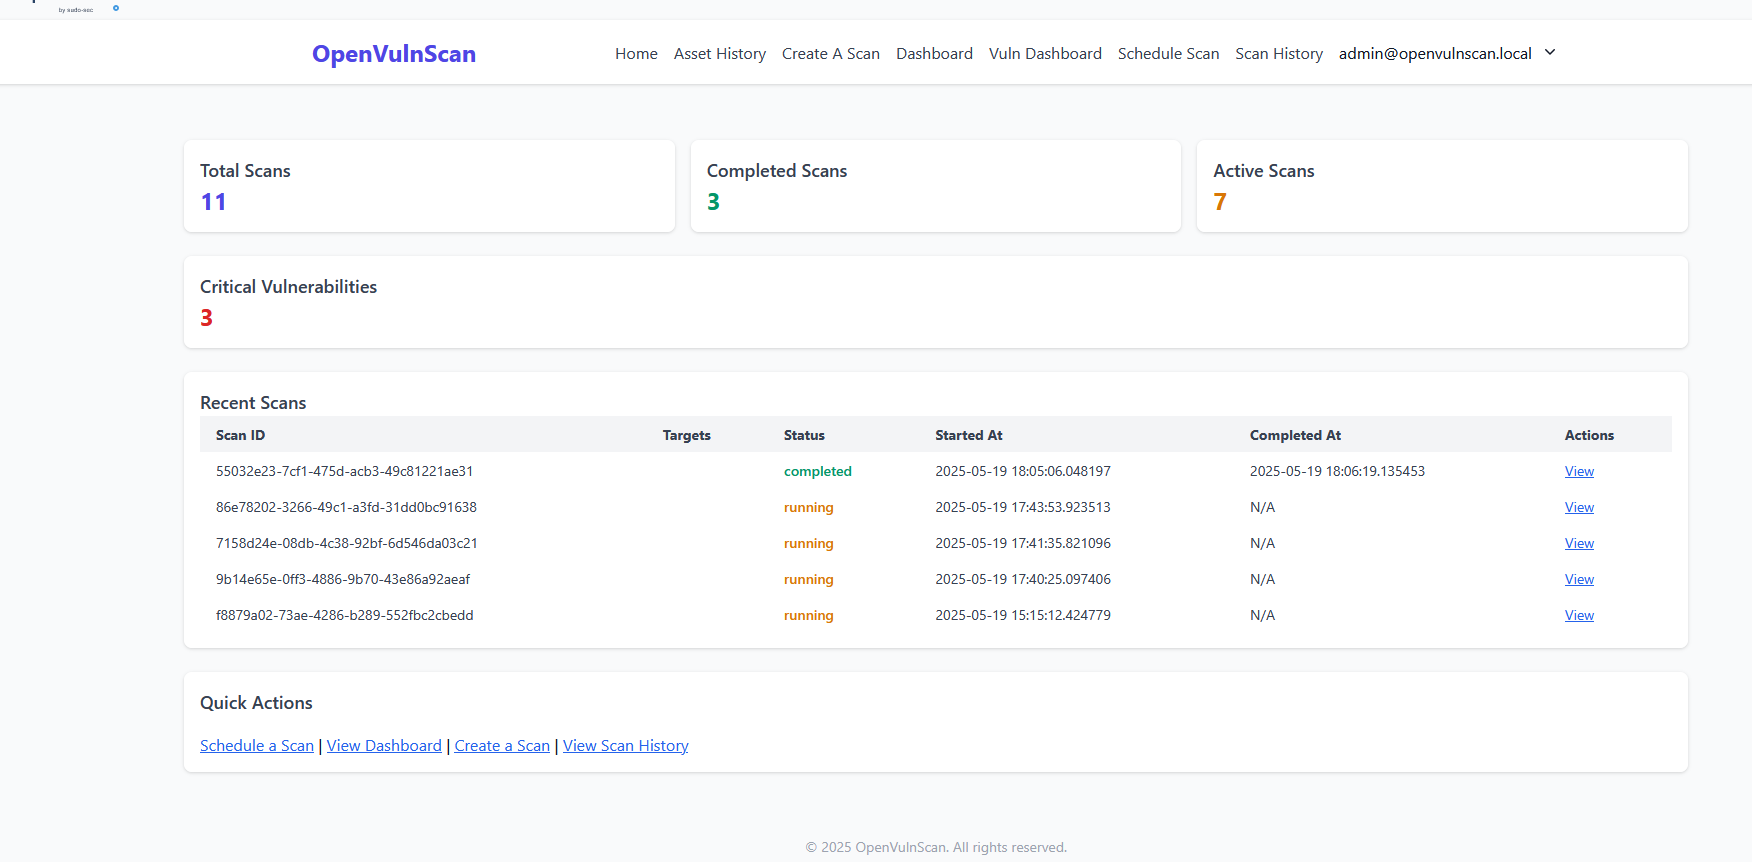
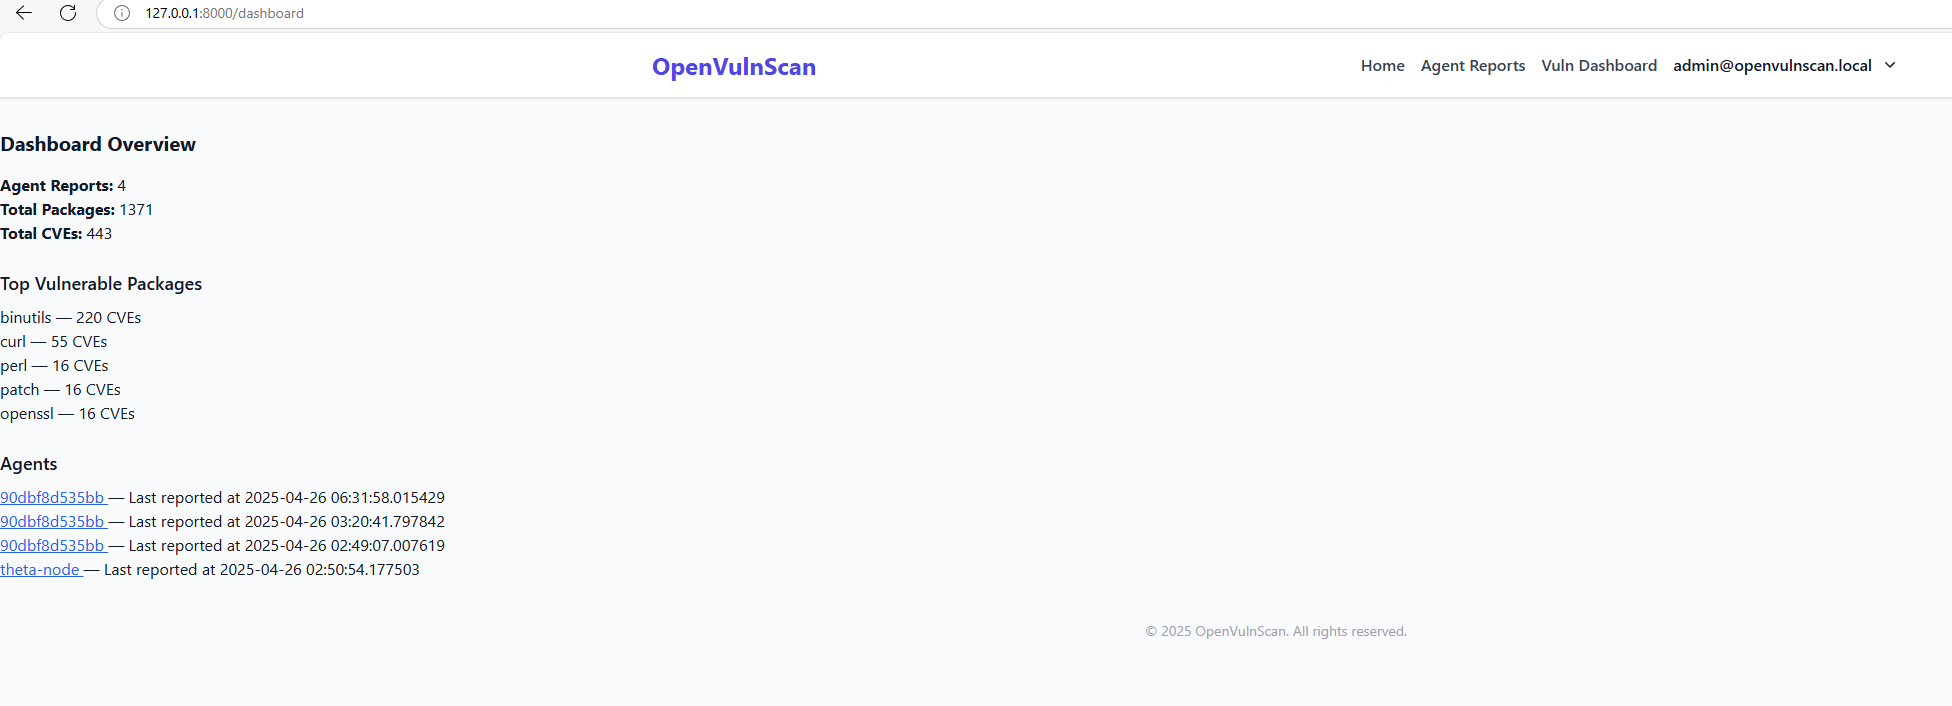
!alt text
!alt text
!alt text
!alt text
!alt text
!alt text
API Docs
!alt text
Features
---
Default Login
the default account is:
:warning: change after standing up. :warning:
Web Interface Links
| Feature | URL |
|--------|-----|
| 🏠 Dashboard | |
| 📋 View Scan Results | /scan/{scan_id} |
| 🧾 Download PDF Report | /scan/{scan_id}/pdf |
| 📥 Download Agent Script | /agent/download?open= |
| 🗂 Agent Reports View | |
| Blog information | []|
| User Guide| [] |
| Admin Guide | [] |
|KB for Open| [] |
| Demo Video |[]|
---
API Usage (with curl)
🧪 Start a Scan
📥 Download Agent Script
open=change to the ip address of scanner if not localhost
📤 Submit Agent Package Report
---
Project Structure
app.py: Main application entry point
config.py: Configuration settings
database/: Database operations
models/: Pydantic models
scanners/: Scanner implementations
services/: Business logic services
utils/: Utility functions
templates/: HTML templates
static/: Static files
data/: Data storage
---
License
MIT
项目信息
开发语言:Python
Star 数:35
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕A simple vulnerability scanning application built with FastAPI. vulnerability-scanner open-source-security nmap-cve SIEM展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | OpenVulnScan - A simple vulnerability scanning application built |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:48:56 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 274 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |