 安全软件
点击放大
ShieldEye_ComplianceScan - Web security and compliance scanner. SSL/TLS, head
项目说明
<di="center">
🛡️ ShieldEye ComplianceScan
Web compliance and scanner
*GDPR • PCI-DSS • ISO 27001, with a GTK4 desktop UI, a REST API, and JSON/SARIF reporting*
![License: MIT]()
![Python]()
![GTK4]()
![FastAPI]()
Features • Quick Start • Screenshots • Architecture • API • Contributing
---
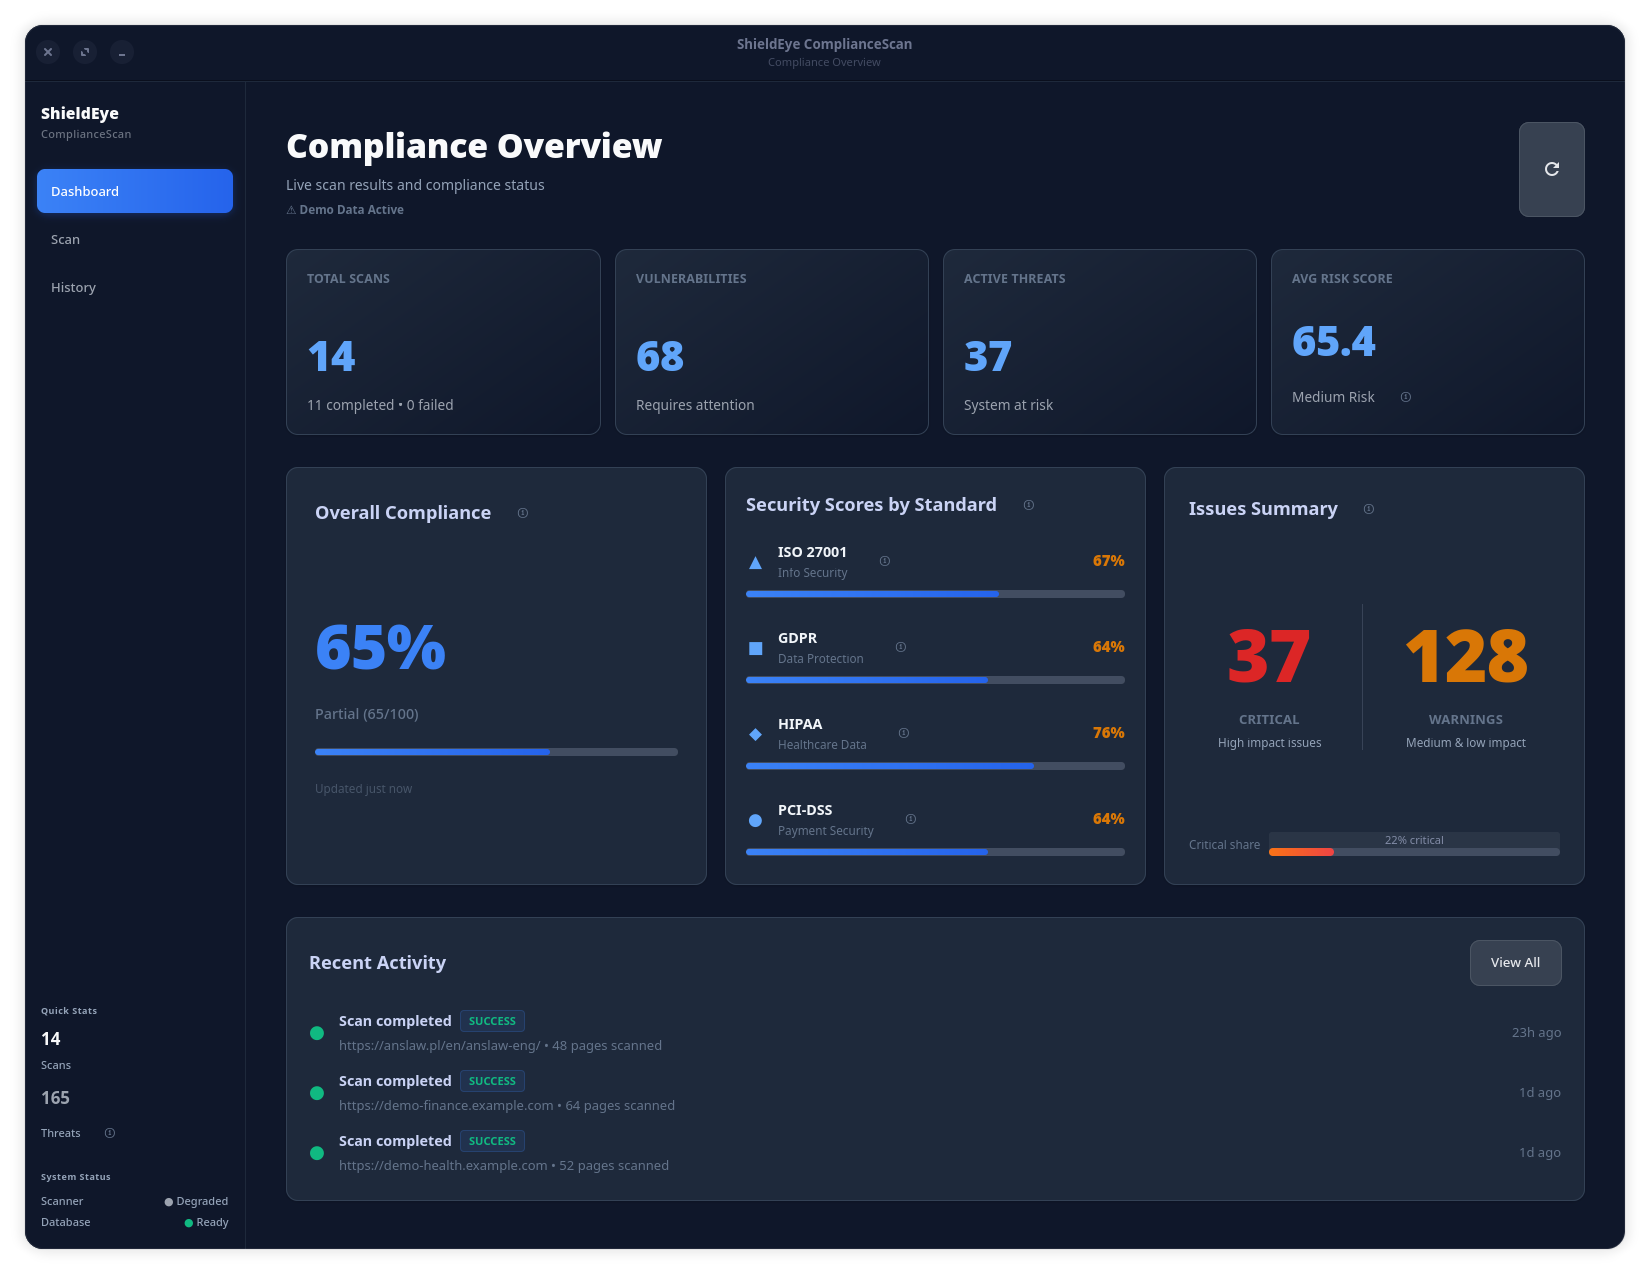
!ShieldEye ComplianceScan Dashboard
</div>
---
What is ShieldEye ComplianceScan?
ComplianceScan checks a web target against common security baselines and maps
the findings onto compliance standards. It inspects TLS configuration, security
headers, and cookie flags, then e the result against GDPR, PCI-DSS, and
ISO 27001 control sets and produces a report with CVSS v3.1-scored findings.
You can drive it three ways: a GTK4 desktop app for interactive use, a CLI for
local and scripted runs, and a FastAPI REST service for integration. Results are
persisted to SQLite and can be exported as JSON, SARIF, CSV, XML, Markdown, or
PDF.
It's meant for the recurring "is this site configured sanely, and where does it
sit against the standards we care about" check, not a substitute for a full
audit or a manual pentest. HIPAA mapping exists but is partial.
> ⚠️ Authorized use only. Only scan systems you own or ha written
> permission to test.
---
Features
<table>
<tr>
<td width="50%">
Security scanning
Secure, HttpOnly, SameSite</td>
<td width="50%">
Compliance mapping
security.txt, incident-response signals</td>
</tr>
<tr>
<td width="50%">
Interfaces
</td>
<td width="50%">
Scoring & reporting
</td>
</tr>
</table>
---
Screenshots
<di="center">
| Dashboard | New Scan | History |
|:---------:|:--------:|:-------:|
| !Dashboard | !New Scan | !History |
| *Compliance o and metrics* | *Configure and launch a scan* | *Scan audit trail with filtering* |
</div>
---
Architecture
A modular Python backend shared by three frontends (GTK, CLI, REST):
Tech Stack
| Layer | Technology |
|-------|------------|
| GUI | GTK4 + libadwaita, PyGObject |
| API | FastAPI, U |
| Scanning | requests, BeautifulSoup4 |
| Reporting | wkhtmltopdf (PDF), SARIF/CSV/XML/Markdown exporters |
| Storage | SQLite |
---
Quick Start
Prerequisites
| Requirement | | Notes |
|-------------|---------|-------|
| Python | 3.10–3.13 | |
| GTK4 + libadwaita | 4.0+ | system package, with PyGObject |
| wkhtmltopdf | recent | only for PDF reports |
| Linux | - | tested on Arch, Fedora/RHEL |
1. Install system dependencies
GTK and PyGObject come from your distro, not pip:
2. Get the code and install Python deps
Or use the interacti, which handles dependency install for you:
3. Launch
---
CLI
---
Configuration
Paths are o :
A few capabilities are gated behind flags (defaults are safe):
| Flag | Default | Description |
|------|---------|-------------|
| COMPLIANCE_BENCHMARKS_ENABLED | true | CIS/PCI-DSS/SOC2 benchmark execution |
| SHIELDEYE_ALLOW_INSECURE_TARGETS | false | Permit scanning targets with invalid TLS (internal use) |
| ENABLE_REMEDIATION_SNIPPETS | true | Include copy-paste fix commands in reports |
Production toggles (Redis-backed rate limiting, Prometheus export, ML
correlation) live in .en and are documented indocs/MIGRATION_GUIDE.md. history is inCHANGELOG.md.
---
API
The REST API ships with OpenAPI/Swagger docs. Scan and config routes require a
Bearer token; health and template lookups are open.
| Method | Endpoint | Description |
|--------|----------|-------------|
| POST | /scans | Create and queue a compliance scan |
| GET | /scans | List recent scans (with filtering) |
| GET | /scans/{id} | Scan details and findings |
| DELETE | /scans/{id} | Remove a scan and its findings |
| GET | /scans/{id}/export?format=sarif | Export results (json, csv, xml, sarif, markdown) |
| GET | /templates · /templates/{name} | Scan templates |
| POST | /schedules · GET /schedules | Recurring scan schedules |
| POST | /webhooks/subscribe · GET /webhooks | Scan-completion webhooks |
| GET | /stats | Aggregated scan statistics |
| GET | /health | Service health and dependency checks |
See docs/INTEGRATION_GUIDE.md for the Core /
SurfaceScan data flow.
---
De
Beyond the basics, the backend also carries a policy-as-code engine
(policy/.py), control-mapping benchmarks (benchmark/engine.py),
typed Core/SurfaceScan integration clients (integrations/), and optional
resilience/obser hooks (backend/utils/). See CHANGELOG.md
for what landed when.
---
Contributing
1. Fork and branch off main.
2. Keep changes scoped and add tests for new scanner or compliance logic.
3. Make sure pytest passes before opening a PR.
---
License
MIT - see LICENSE.
---
Related Projects
Part of the ShieldEye toolkit:
项目信息
开发语言:Python
Star 数:33
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Web security and compliance scanner. SSL/TLS, headers and cookie analysis mapped to GDPR, PCI-DSS, ISO 27001 and HIPAA. CVSS v3.1 scoring, PDF reports, SARIF export. GTK4 desktop GUI. Part of the ShieldEye toolkit.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ShieldEye_ComplianceScan - Web security and compliance scanner. SSL/TLS, head |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:49:33 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 400 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |