 安全软件
点击放大
Cascavel - 🐍 Cascavel — The zero-friction offensive security
项目说明
<p align="center">
<img src="docs/casca.png" alt="Cascavel" width="800" />
</p>
<h1 align="center">
<code>CASCAVEL CTEM ENGINE</code>
</h1>
<h3 align="center">Autonomous Ad Exposure (AEV) and Red Team Orchestration Platform.</h3>
<p align="center">
<strong>Cascavel is a zero-friction Continuous Threat Exposure Management (CTEM) engine. It orchestrates complex attack chains, enriches findings with Threat Intel (EPSS/CISA KE AI-dri, and exports nati (OCSF) in a single command.</strong>
</p>
<p align="center">
<a href=" casca.dev</strong></a> ·
🇺🇸 <strong>English</strong> ·
<a href="README.pt-BR.md">🇧🇷 Português (Brasil)</a>
</p>
<p align="center">
<a href="LICENSE"><img src=" /></a>
<a href=" src=" /></a>
<img src=" />
<img src=" />
<a href="CHANGELOG.md"><img src=" /></a>
<img src=" />
<img src=" />
<a href=" src=" /></a>
<a href=" src=" /></a>
</p>
---
🦅 Executi & Philosophy
Standard management causes critical alert fatigue. Security Operations Centers (SOC) analysts waste hours triaging non-exploitable findings from dozens of non-integrated tools that output incompatible proprietary formats.
Cascavel v3.0 shifts organizations from reacti management to a proacti Continuous Threat Exposure Management (CTEM) program. By bridging the gap between business strategy and technical execution, Casca that security teams only focus on exposures that pose a credible, reachable risk to the business.
---
⚙️ The 5-Stage CTEM Lifecycle (How Casca)
Casca automates Gartner’s fi CTEM framework into a single executable pipeline:
1. Scoping & Discovery
Unlike traditional tools that rely on hardcoded parameters, Cascavel's Dynamic Spidering Engine automatically crawls the target infrastructure (APIs, SaaS integrations, Cloud workloads), mapping forms, headers, and query strings dynamically to construct an accurate attack surface.
2. Prioritization
Generic C are obsolete. Casca every discovered exposure with real-world threat intelligence:
* FIRST.org EPSS (Exploit Prediction Scoring System): Calculates the actual probability of exploitation in the wild within 30 days.
* CISA KE Exploited ): Cross-references exposures against active APT/Ransomware campaigns.
3. (AEV)
The Ad Exposure (AEV) engine drops False Positives to near-zero. Casca *Global Baselines* for network latency and WAF behaviors *before* scanning. Using Multi-Stage (like
Content-Type boundary checking), it only reports that are mathematically and contextually exploitable. 4. Mobilization & Remediation
Instead of dumping JSON files, Casca AI-dri payloads. Using the
--ai-fix flag, it synthesizes contextual Bash scripts, Python mitigations, or Kubernetes manifests to patch the exact exposure discovered.5. Telemetry & Go
Casca native OCSF (Open Cybersecurity Schema Framework) v1.1.0 telemetry, ensuring immediate compatibility with modern SIEMs (Splunk, Elastic, AWS Security Lake) without custom parsers.
---
🎬 See it in Action
<p align="center">
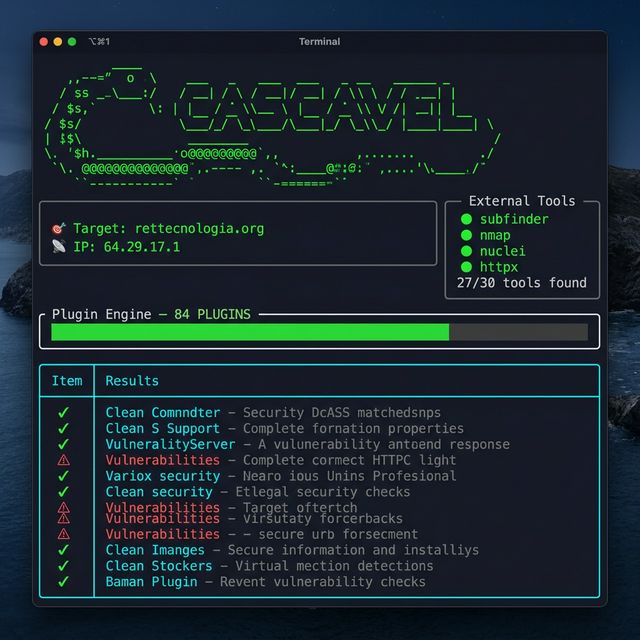
<img src="docs/casca.png" width="700" />
</p>
<p align="center">
<sub><strong>Cinematic AEV Boot Sequence</strong> · Real-time Threat Preloader · Stealth Simulation</sub>
</p>
<p align="center">
<img src="docs/casca.png" width="700" />
</p>
<p align="center">
<sub><strong>Interactive CTEM Dashboard</strong> · EPSS Tracking · CISA KE</sub>
</p>
---
🚀 Deterministic Omni-Distribution Installation
Cascavel v3.0 uses an Omni-Distribution Pipeline. It is built, signed, and published across multiple ecosystems simultaneously with SLSA Level 3 Pro and Cosign cryptographic signatures.
The installer is engineered under a strict 2026 Threat Model, guaranteeing total dependency isolation and pre supply chain RCE.
Does not require git. Compatible with macOS, Linux, Windows, WSL2, and Docker.
1. Nati (Zero Dependencies)
2. Docker / GHCR
3. NPM (Node Ecosystem)
4. PyPI (Python Ecosystem)
Installer Protections (Hardening v2.0)
| Defense Mechanism | Security Outcome |
|:--|:---|
| Hermetic En | Isolates (mktemp -d) pre OS-le. |
| Zero Supply Chain | Enforces integrity SHA-256 hashes in requirements.txt. |
| TOCTOU Pre | Uses anti-symlink locks and strict umask 077 permissions. |
| Clean Exit Hooks | POSIX trap handlers ensure secure deletion of /tmp artifacts on exit. |
| $PATH Isolation | Prevents Binary Hijacking by stripping relative . entries from PATH. |
---
🛠️ CLI Reference: Red Team Workflows
The terminal API is designed to be highly tactical and straightforward.
CI/CD Orchestration (GitHub Actions)
Add this as a blocking security gate in your
.github/workflows/ctem.yml:---
🧩 Plugin Arsenal (108) and Architecture
Our architecture prioritizes the absolute elimination of false positives via AST parsing and deep semantic detection.
Core Engine
Infiltration Categories
1. Injection & Code Exec (7): xss_scanner, sqli_scanner, ssti_scanner, rce_scanner, nosql_scanner...
2. Cloud & K8s Infra (8): cloud_metadata (SSRF via 169.254.x), docker_exposure, s3_bucket_enum...
3. Authentication (6): jwt_analyzer (Alg Bypass, Null Signature), oauth_scanner, idor_scanner...
4. Defense Bypass (7): cors_checker, csp_bypass, waf_e, cache_poisoning...
5. API Logic Attacks (6): graphql_probe, mass_assignment, api_...
6. OSINT and Recon (11): shodan_recon, dns_rebinding, subdomain_takeover...
For the complete matrix of and pre-calculated C, consult our Plugin Documentation.
---
🛡️ Defensive & Supply-Chain Hardening (2026 Standard)
An offensi must be immune to retaliation. Casca its host from traps laid by Blue Teams in HoneyPots, while enforcing rigorous CI/CD supply-chain security.
| Retaliation | Core Defensi |
|:---|:---|
| Terminal Injection (ANSI) | Strict Regex filters remo Escape payloads (CSI/OSC/DCS), pre terminal clipboard hijacking. |
| Command Injection (OS) | Mandates -- binary delimiters and blocks nati in subprocess.run(shell=False). |
| Ser Request Forgery | Internal IP lock (169.254.x) prevents malicious instances from rebounding attacks. redirects=False strictly enforced. |
| Path Tra Sandboxing | Utlizes pathlib.resolve().is_relative_to() ensuring total containment of OCSF logs and Reports. |
| Arbitrary Deserialization | Rejects pickle functions and globally enforces yaml.safe_load(). |
Cascavel's own CI/CD pipeline is a fortress:
* Unmasked SAST: 100% of the codebase is audited by Semgrep, Bandit, and TruffleHog without exclusion filters (--exclude-rule granular approach).
* Zizmor Hardened: GitHub Actions workflows are mathematically against cache-poisoning, unpinned actions, and pri escalation .
* Cryptographic Signatures: All Omni-Distribution releases are signed /Cosign.
---
🤝 Contributing
Rigid rules ensure Framework integrity:
*Cascavel is classified as "Dual-Use". The author repudiates its usage against unauthorized assets.*
---
<p align="center">
<strong>CASCA</strong><br />
<sub>
Engineered and maintained by <strong>De</strong><br />
<a href=" Profile</a>
</sub>
</p>
项目信息
开发语言:Python
Star 数:29
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🐍 Cascavel — The zero-friction offensive security engine. Automate Red Team scans, validate exposures (CTEM), and generate compliance reports in one command.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Cascavel - 🐍 Cascavel — The zero-friction offensive security |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:50:45 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 504 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |