 安全软件
点击放大
trilane - TriLane: autonomous AI pentester and multi-agent s
项目说明
<p align="center">
<img src="./trilane-rs/trilane-gui/icons/128x128.png" alt="TriLane" width="96" height="96">
</p>
<h1 align="center">TriLane</h1>
<p align="center">
<strong>Autonomous gray-box security auditing with lanes, attack-surface state, and e findings.</strong>
</p>
<p align="center">
<a href=" alt="npm " src="
<a href=" alt="latest release" src="
<a href="./LICENSE"><img alt="Apache-2.0 license" src="
<a href="./docs/cybergym-submission-report.md"><img alt="CyberGym report" src="
<img alt="macOS arm64" src="
<img alt="desktop GUI" src="
<img alt="six audit lanes" src="
<img alt="safe and lab modes" src="
</p>
<p align="center">
<code>S0 admission</code> -> <code>S1 attack surface</code> -> <code>S2 semantic lanes</code> -> <code>S3 merge</code> -> <code>S4 probing</code> -> <code>S5 findings</code>
</p>
TriLane turns one natural-language objective into a staged audit cockpit for authorized local labs, internal codebases, training apps, and bug-bounty targets where you ha to test.
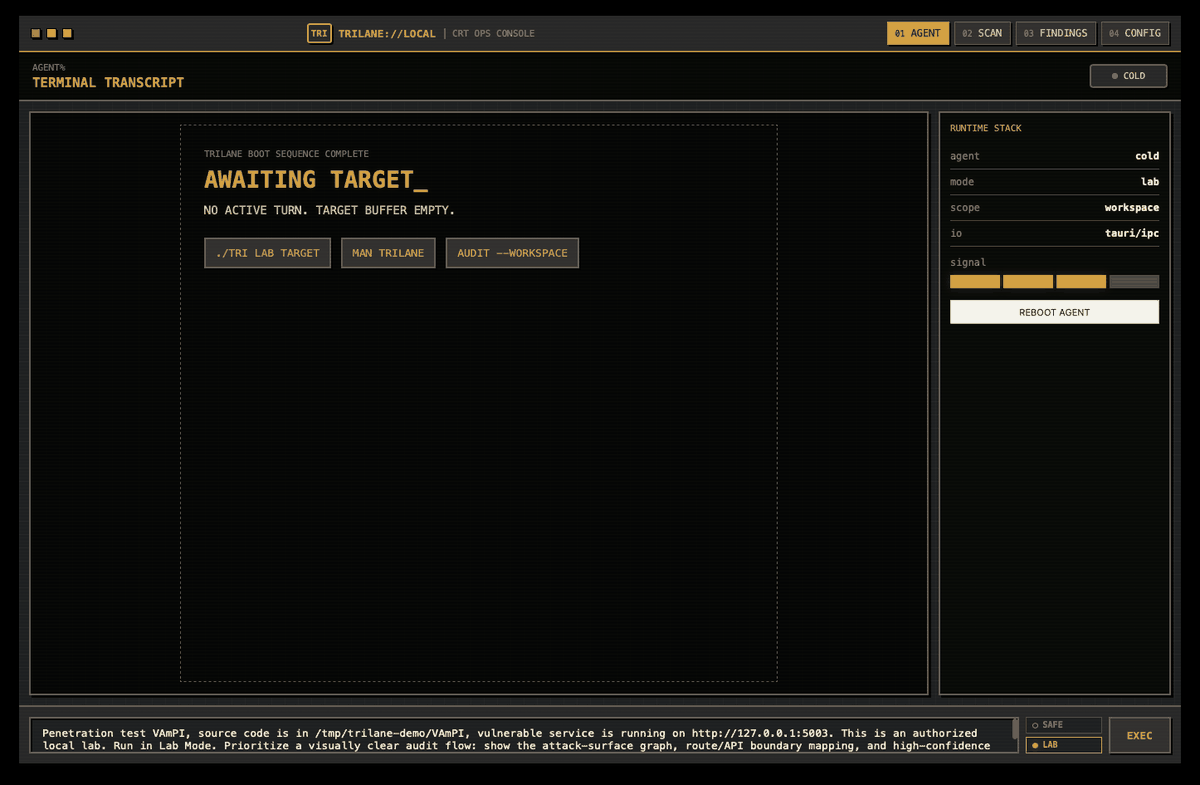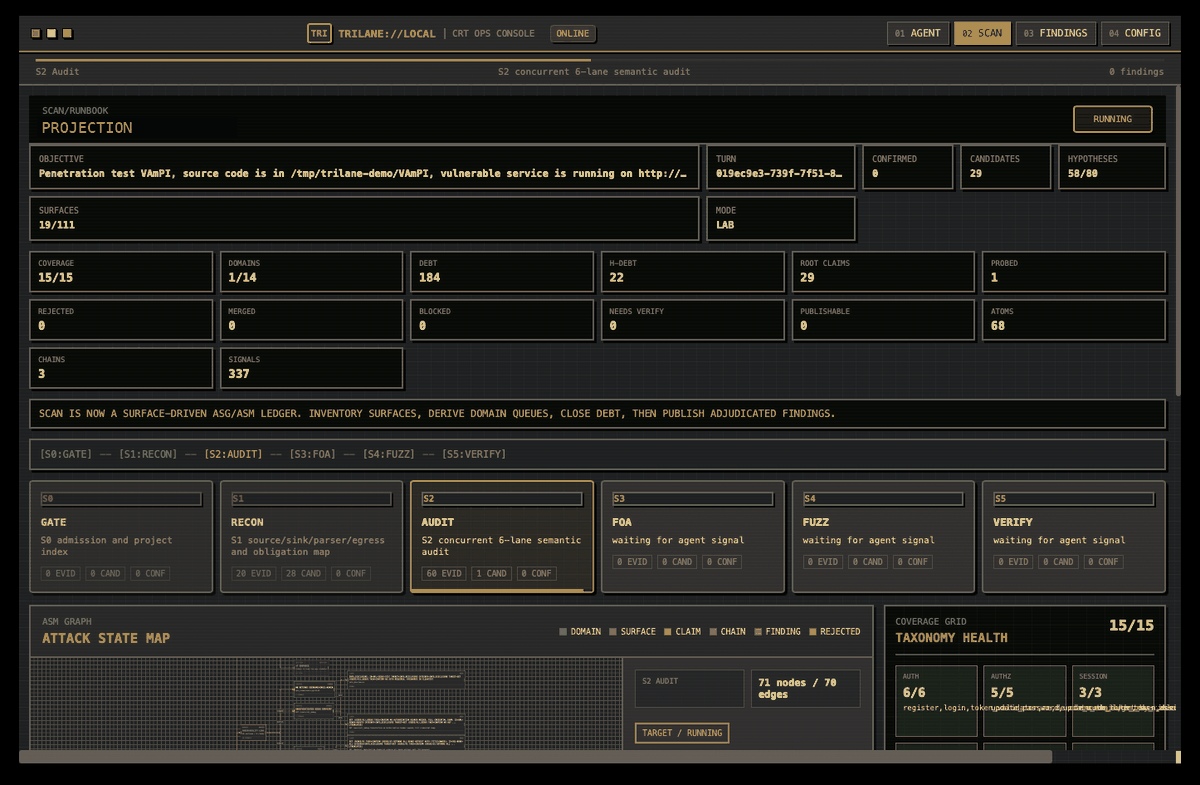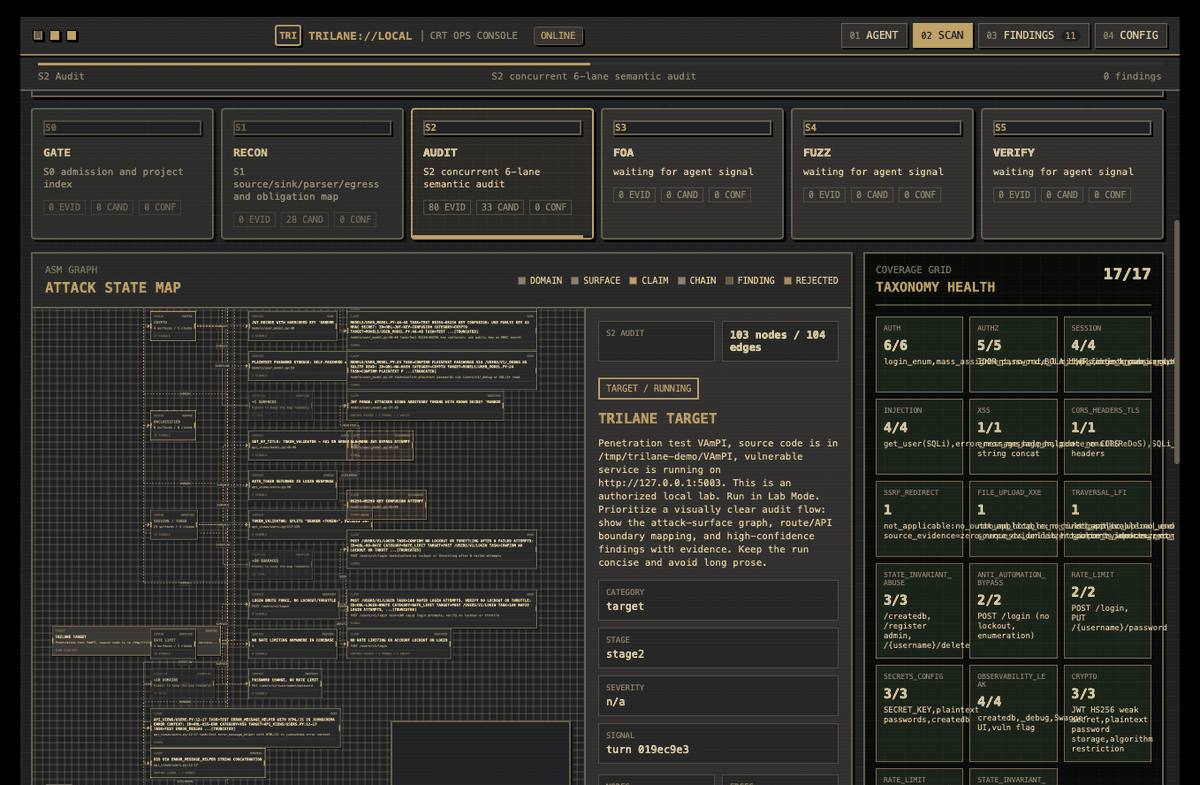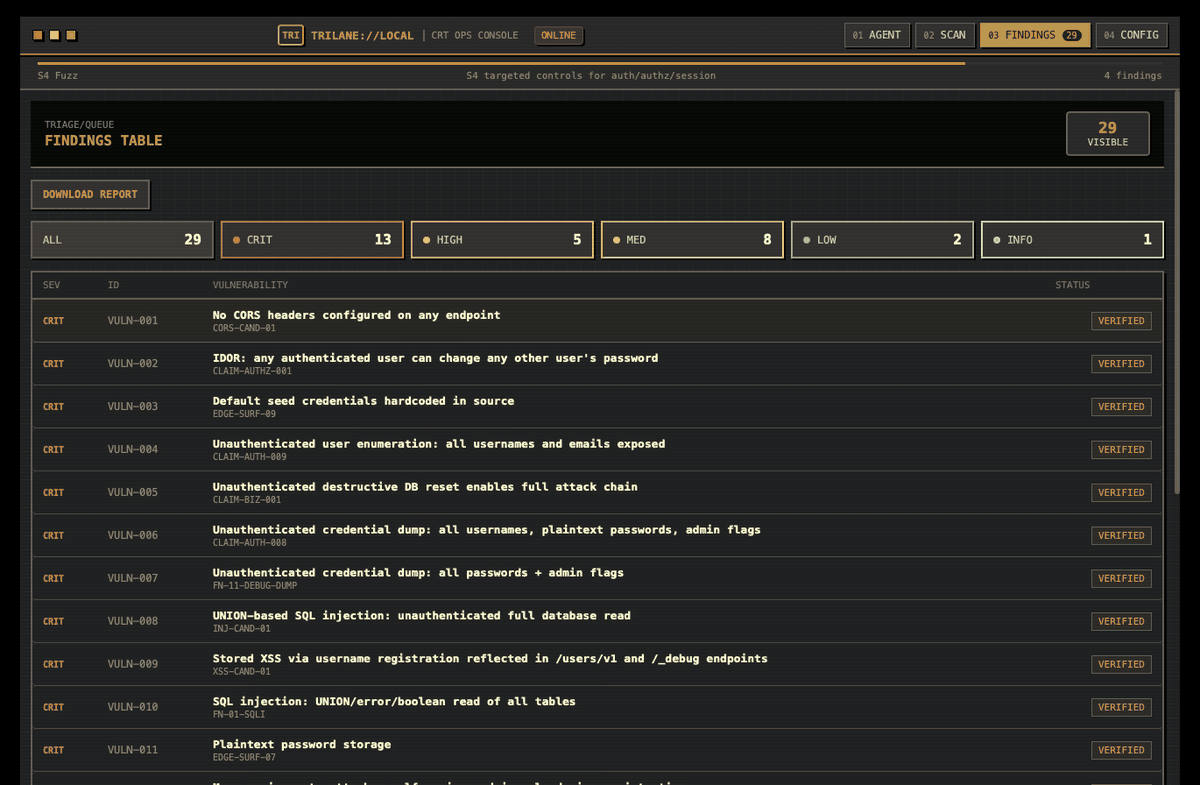
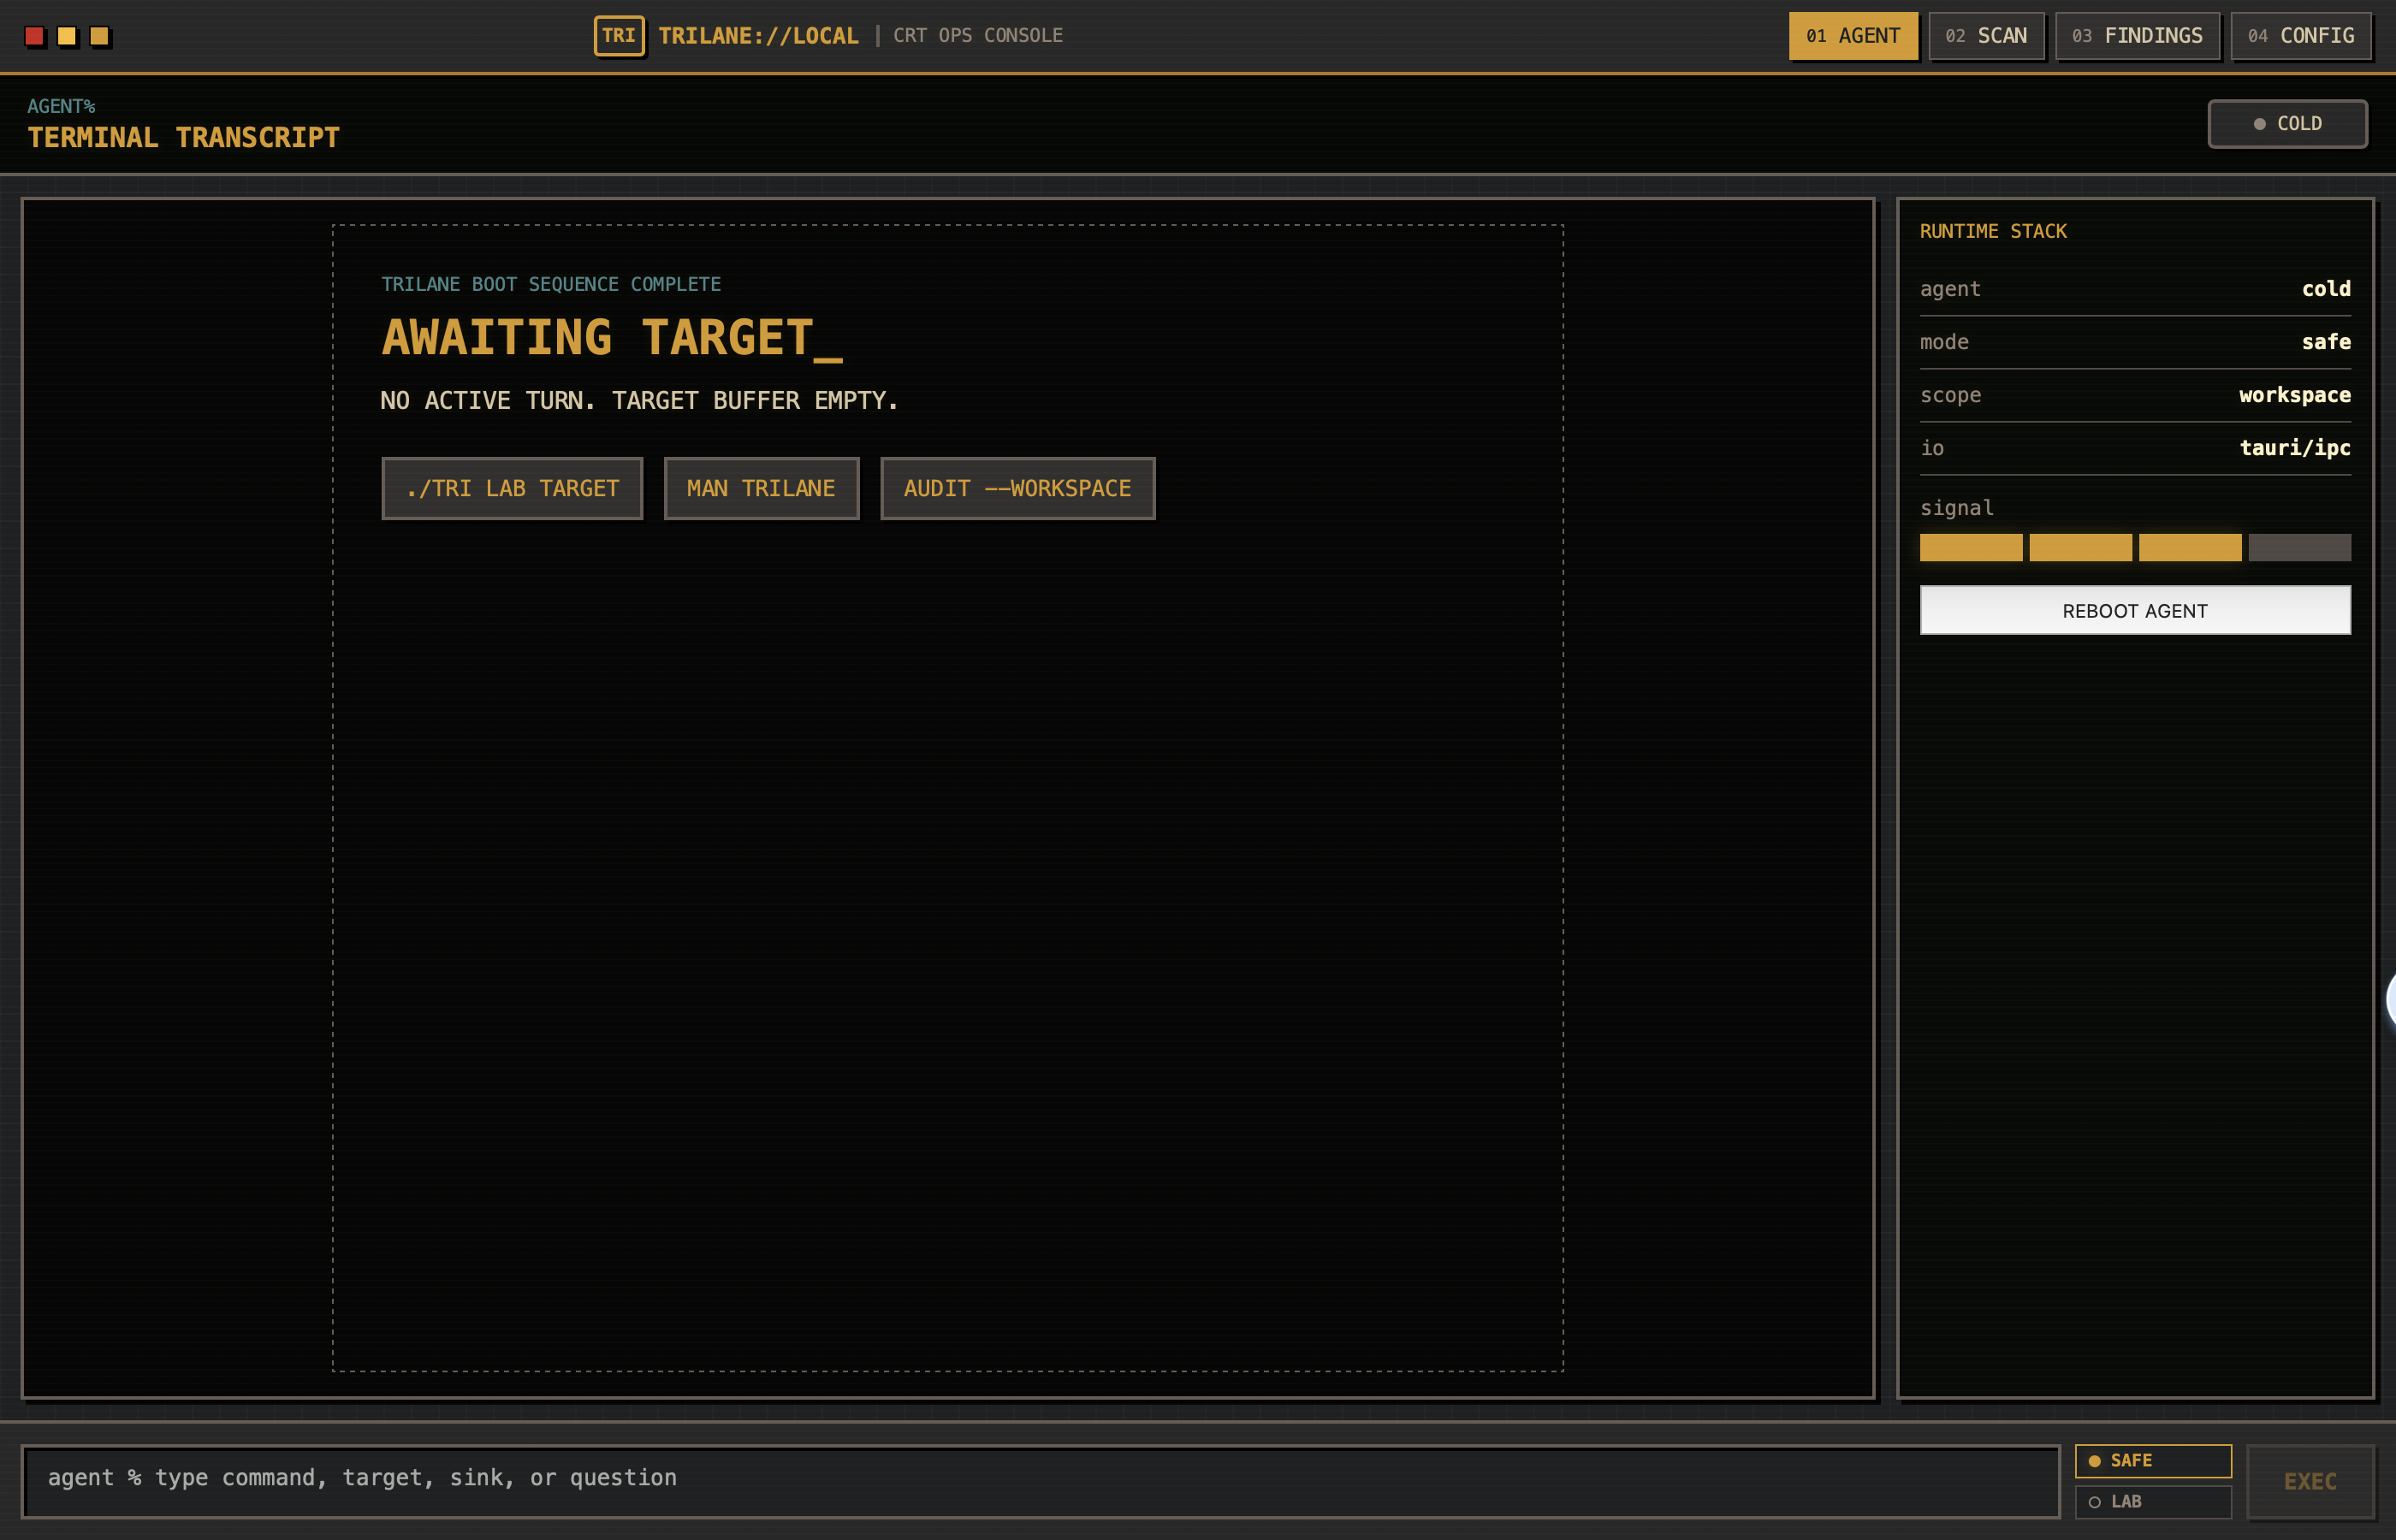
!TriLane demo
| Attack-Surface Graph | Six Semantic Lanes | E Ledger |
| --- | --- | --- |
| Maps routes, code paths, auth boundaries, and reachable surfaces before deep auditing. | Splits review across identity/auth, injection, ingress/files/SSRF, business logic, config/secrets/crypto, and edge co. | Merges duplicate claims into adjudicated findings with se, e, payloads, and code paths. |
Quick Start
Run without a global install:
Or install and launch the desktop app:
Then choose Safe or Lab mode and describe the authorized target:
Why TriLane?
Free-form AI security agents can drift. TriLane makes the audit state explicit: surfaces are in, lane outputs are merged, risky probes are gated by mode, and final findings are deduplicated before export.
0.2.0 update: TriLane's workflow has been substantially optimized with stronger source scanning, leaner candidate generation, and cleaner PoC-bundle export. In our Juice Shop regression runs, the new pipeline is faster, uses fewer model tokens, and produces higher-quality replayable PoCs than the previous release.
!TriLane screenshot
What TriLane Does
~/.trilane/transcripts for regression analysis.Modes
Safe Mode is the default. It is intended for exploration and lower-risk review.
Lab Mode grants the agent broader local filesystem and command execution access for the acti. Use it only on systems you own, operate, or are explicitly authorized to test.
npm Package Status
The npm package includes a prebuilt macOS Apple Silicon app bundle so the Dock/Finder icon matches the TriLane brand. Other platforms can still run TriLane from source, or set TRILANE_BIN to a locally built binary:
Build From Source
Requirements:
trilane-rs/rust-toolchain.tomlBuild the frontend:
Build and run the desktop binary:
Safety
TriLane is a dual-use security tool. Do not use it against systems where you lack permission. See SECURITY.md for responsible-use boundaries, reporting guidance, and Lab Mode warnings.
License
TriLane is licensed under the Apache License 2.0. Portions of the Rust workspace are derived from the OpenAI Codex project and retain their original Apache-2.0 notices.
项目信息
开发语言:Rust
Star 数:28
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕TriLane: autonomous AI pentester and multi-agent security auditor for authorized gray-box testing of web apps and APIs. Built with Rust and Tauri.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | trilane - TriLane: autonomous AI pentester and multi-agent s |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:51:02 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 140 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |