 安全软件
点击放大
ZeroHuntAI - ZeroHuntAI is an advanced source code vulnerabilit
项目说明
📖ZeroHuntAI - AI-Powered Scanner
ZeroHuntAI is an ad, modular, and extensible source code scanner designed to detect exploits and security weaknesses in local directories or GitHub repositories. Le static code analysis, pattern matching, and AI-driven risk scoring, ZeroHuntAI empowers de and security researchers to identify and mitigate threats like RCE, SQL Injection, XSS, and more.
!ZeroHuntAI Logo
✨ Key Features
* Multi-Mode Scanning:
* Local Scanner: Recursively analyzes .py, .php, .js, .java, .c, .cpp, .go, and more.
* GitHub Scanner: Clones and scans repositories directly from URLs.
* Buffer O, SQL Injection, Command Injection, Path Tra, XSS, Authentication Flaws, Logic Bugs, and more.
* Extracts secrets from .env and configuration files.
* AST-based parsing for deep code insights.
* Regex pattern matching for risky functions (e.g., eval(), system(), mysqli_query()).
* Contextual detection and data flow analysis.
* AI Risk Scoring:
* Mock LLM e (placeholder) to classify risks as High, Medium, or Low.
* Future-ready for integration with models like GPT-4 or LLaMA.
* Exploitation Simulation:
* Runs simulated exploits (e.g., SQLi, XSS) in an isolated Docker en.
* User Experience:
* CLI with colored output (via rich or colorama).
* Web dashboard for interacti browsing.
* Exploitation Simulation Engine:
* Simulates exploits in a Docker sandbox and reports success (✅) or failure (❌).
* Data Flow & Taint Analysis:
* Tracks from input to execution using tools like Bandit or Semgrep.
* Auto PoC Generator:
* Generates Python/Bash exploit scripts and PDF reports for each .
* API Endpoint Analysis:
* Extracts and tests endpoints for IDOR, SSRF, and Auth Bypass.
* Interactive Call Graph:
* function relationships and data flow in an HTML graph.
* Highlights exploitable paths in red.
* Call Graph
* Finds API keys, tokens, and sensitive data in code or configs.
* Integrates with C to cross-check findings.
* Generates random payloads to test for Buffer O and Logic Bugs.
* Auto Patch Generator:
* Suggests secure code fixes for detected issues.
Reporting:
* JSON and HTML reports with detailed findings.
* Interactive Call Graph & Taint Flow .
🚀 Getting Started
Prerequisites
Python
Required libraries: gitpython, ast, colorama, requests, tqdm, etc. (see requirements.txt).
Installation
Clone the repository:
Install Requirements:
Usage Examples
Scan a local directory:
Scan a GitHub repository:
Enable Call Graph :
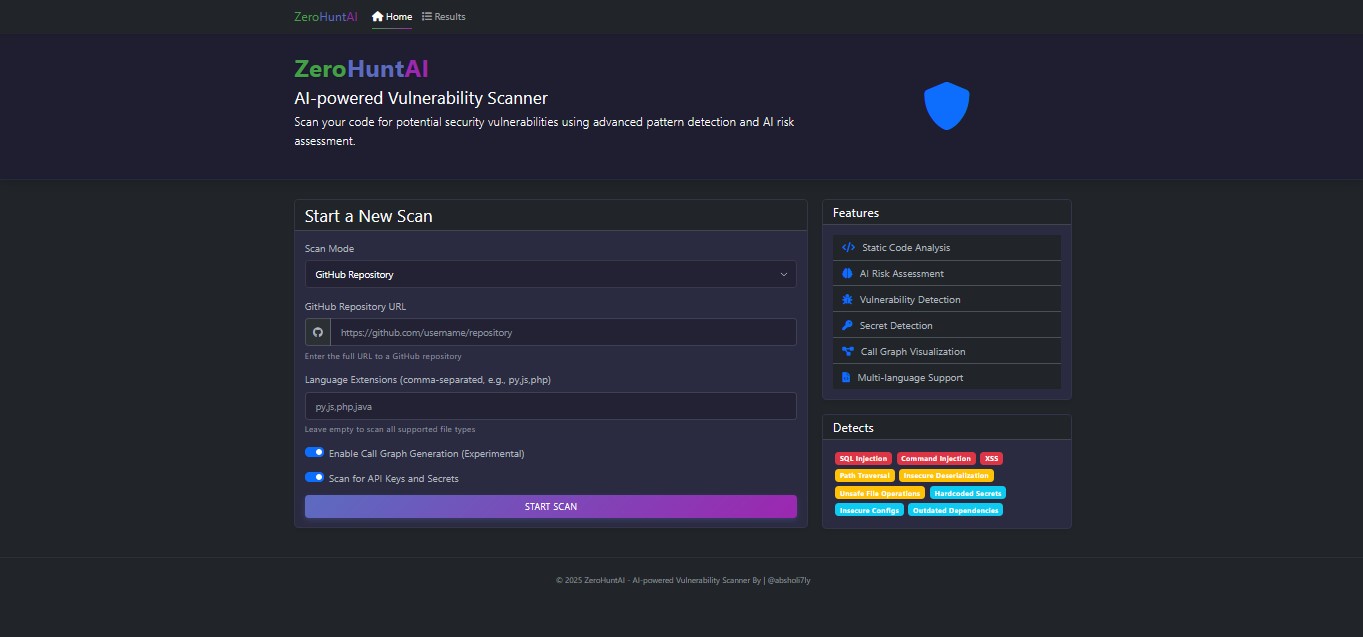
!ZeroHuntAI
--------------------------------------------------------------------------------
!ZeroHuntAI
--------------------------------------------------------------------------------
!ZeroHuntAI
--------------------------------------------------------------------------------
📜 License
This project is licensed under the MIT License - see the LICENSE file for details.
🙌 Credits
Built with ❤️ by [absholi7ly].
Inspired by open-source SAST tools and the security research community.
Report Sample
Note
This project is in its early stages and is still under de, and we are continually working to improve it and enhance its features to provide the best performance and reliability. We welcome any suggestions or contributions from interested parties to support and improve the project.
💻 Contribution and de
Hello to all security researchers and de to contribute to the de of ZeroHuntAI
To contribute:
* Fork Warehouse
* Add your feature
* Open Pull Request
⚠️ Legal Disclaimer
For educational use only. Unauthorized use is your responsibility.
⭐ Support the project by giving it a Star!
项目信息
开发语言:Python
Star 数:25
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕ZeroHuntAI is an advanced source code vulnerability scanner designed to detect potential vulnerabilities in your codebase. It combines static code analysis with pattern matching and AI evaluation to identify security issues before they can be exploited.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ZeroHuntAI - ZeroHuntAI is an advanced source code vulnerabilit |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:52:19 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 171 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |