 安全软件
点击放大
ApiHunter - Async API security scanner in Rust for CORS, CSP,
项目说明
<!-- donation:eth:start -->
<di="center">
Support De
If this project helps your work, support ongoing maintenance and new features.
ETH Donation Wallet 0x11282eE5726B3370c8B480e321b3B2aA13686582
<a href="
<img src="publiceth.svg" alt="Ethereum donation QR code" width="220" />
</a>
_Scan the QR code or copy the wallet address above._
</div>
<!-- donation:eth:end -->
<di="center">
🎯 ApiHunter
<img src=" alt="Typing SVG" />
!Rust
!Security
!API
!Async
!CI
!License
</div>
---
📺 Video Demo
<di="center">
<a href="
<img src="apihunter_repo_thumbnail.png" alt="ApiHunter Demo Video" width="600" />
</a>
<br>
<em>Click to watch the full demo on YouTube</em>
</div>
---
🖥️ Desktop App Snapshots
<p align="center">
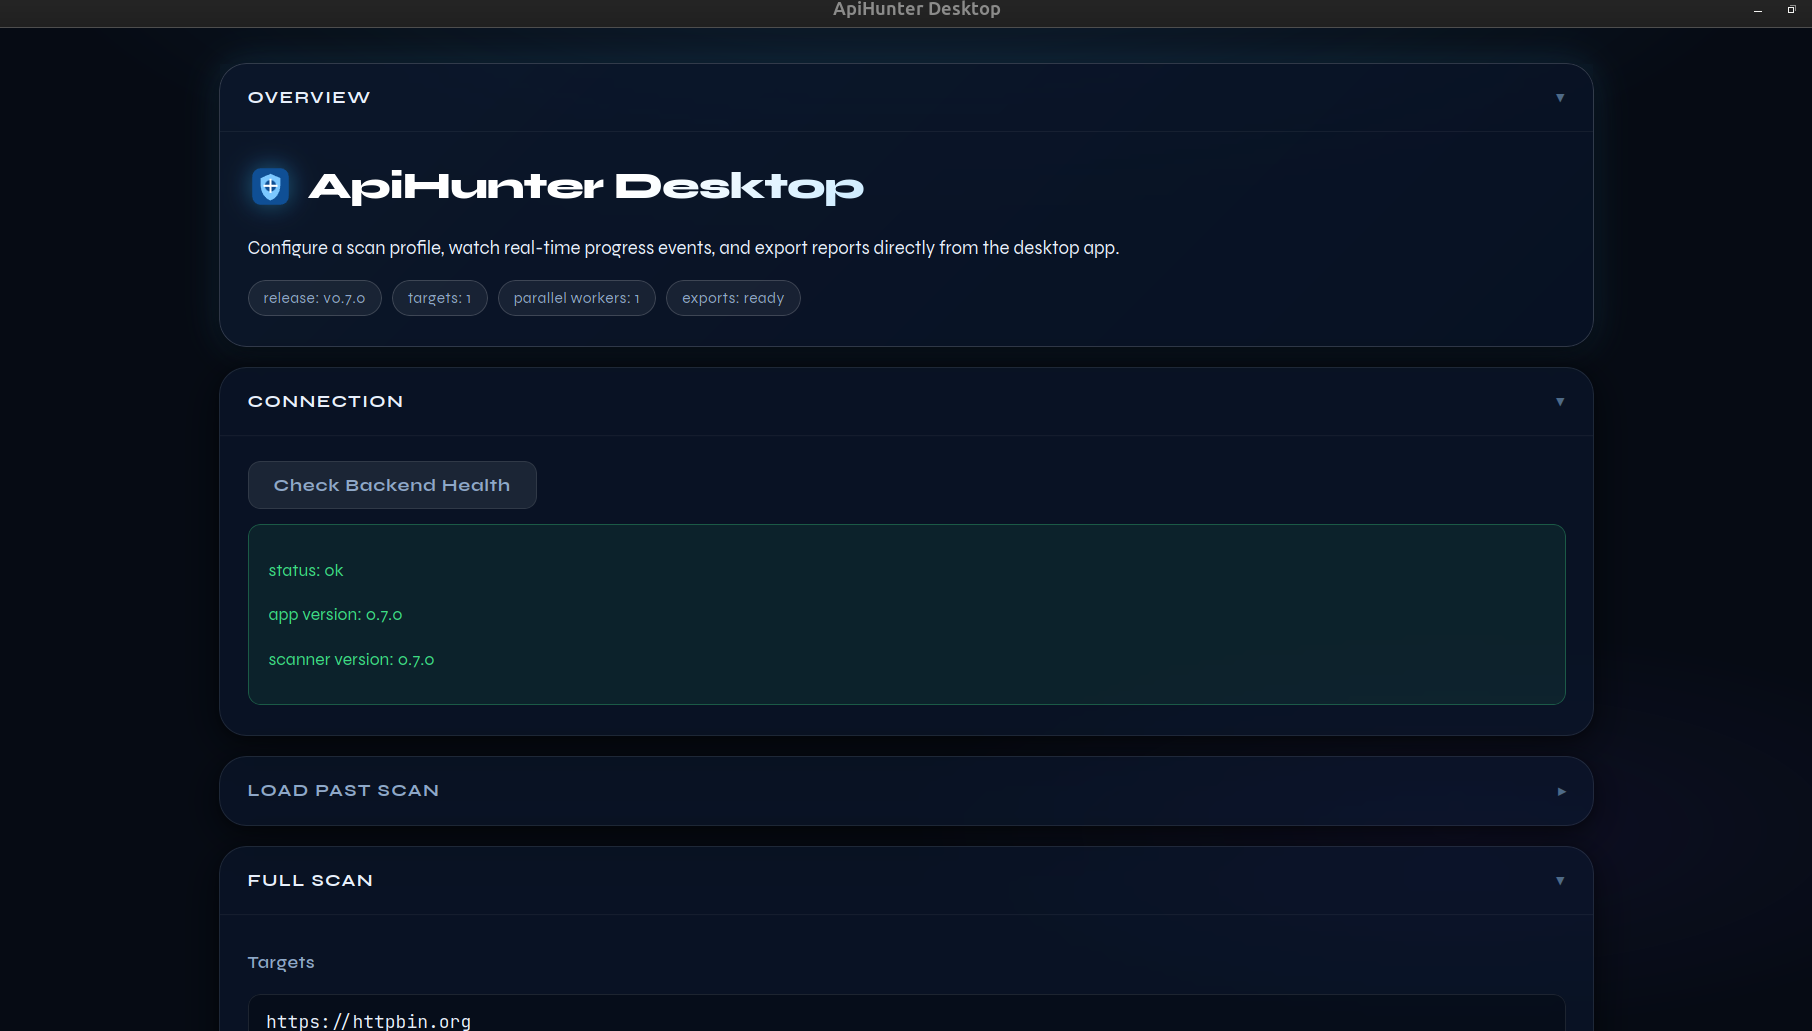
<img src="docs/images/desktop/o.png" alt="ApiHunter Desktop — O panel with chip, health check, and Full Scan target input" width="900" />
</p>
<p align="center">
<img src="docs/images/desktop/full-scan-controls.png" alt="ApiHunter Desktop — Full Scan controls: Quick Passive / Deep Acti, collapsible Safety, Runtime Limits, and Scanner Toggles sections" width="900" />
</p>
<p align="center">
<img src="docs/images/desktop/results-analytics.png" alt="ApiHunter Desktop — Results analytics dashboard: se heatmap, worst-target card, scan efficiency, summary, findings breakdown, and top checks" width="900" />
</p>
<p align="center">
<img src="docs/images/desktop/results-exports.png" alt="ApiHunter Desktop — Results lower panel: target ranking, scanner co, check se breakdown, per-target summary, and one-click export buttons" width="900" />
</p>
---
📑 Table of Contents
---
Async, modular API security scanner for API baseline testing and regression detection.
Combines discovery with targeted checks (CORS/CSP/GraphQL/OpenAPI/JWT/API Security) using adapti and CI-ready outputs (NDJSON/SARIF).
Use cases: offense for red-team/API pentest discovery and exploit , and defense for CI/CD regression gating, continuous API hardening, and early misconfiguration detection.
> Scanning at scale? See Triage Mode — scan 5000 targets in 20 minutes with core security checks, then use Enrich Mode to add threat intelligence context (ports, CVEs, ASN, domain age) to findings.
Naming
ApiHunterapihunterapi_scannerapihunter (default for cargo run)GitHub Metadata (Recommended)
Set these in the GitHub repository settings for disco:
Async API security scanner for CORS/CSP/GraphQL/JWT/OpenAPI and active API posture checks.rust, security, api-security, scanner, graphql, cors, csp, jwt, openapi, sarif, ndjsonRepository Flow
Why ApiHunter?
Core Ad
- SPA catch-all detection with canary probing
- Context-aware secret (frontend )
- Body content and referer checking
- Response fingerprinting to skip duplicate findings
- Adapti (AIMD) that backs off on errors
- Per-host rate limiting with configurable delays
- Politeness controls (retries, timeouts, WAF e)
- Dry-run mode for acti
- Runtime User-Agent rotation from curated pool (assets/user_agents.txt)
- Randomized request delays with jitter
- Per-host delay enforcement (avoids burst patterns)
- Retry logic with exponential backoff
- Custom header injection for blending with legitimate traffic
- Adapti based on ser
- No hardcoded scanner fingerprints in default mode
Stealth Techniques Deep Dive
ApiHunter uses several stealth techniques to avoid detection by WAF (Web Application Firewall) and bot protection systems:
#### 1. User-Agent Rotation
What it does: Randomly cycles through 100+ real browser User-Agent strings from a file (assets/user_agents.txt)
Why it works: Bots typically use the same User-Agent (like curl/7.68.0). By pretending to be Chrome, Firefox, Safari, etc., you blend in with legitimate traffic
Simple analogy: Like wearing different disguises instead of always wearing the same uniform
#### 2. Random Timing & Jitter
What it does: Adds random delays between requests (controlled by --delay-ms) with jitter (small random )
Why it works: Bots send requests at perfect intervals (exactly 100ms apart). Humans are unpredictable. Random timing makes traffic look organic
Simple analogy: Walking with irregular steps instead of marching like a robot
#### 3. Per-Host Delay Enforcement
What it does: Tracks delay separately for each domain, not globally
Why it works: Prevents burst patterns where you hit one host 50 times instantly. Each host sees polite, spaced-out requests
Simple analogy: Taking turns in different con instead of shouting at one person repeatedly
#### 4. Adapti (AIMD)
What it does: Automatically slows down when getting 429 (rate limit) or 503 (server busy) errors, speeds up when successful
Why it works: Backs off when caught, mimics how browsers retry. WAFs see "this client respects our limits"
Simple analogy: Slowing down when traffic is congested, speeding up on open roads
#### 5. Retry with Exponential Backoff
What it does: When a request fails, waits 1s, then 2s, then 4s before retrying
Why it works: Legitimate clients retry gracefully. Bots often hammer immediately or give up
Simple analogy: Knocking on a door, waiting longer each time instead of banging continuously
#### 6. No Scanner Fingerprints
What it does: Doesn't send headers like X-Scanner: ApiHunter or predictable patterns
Why it works: Many tools lea (Nuclei templates, sqlmap patterns). ApiHunter avoids obvious markers
Simple analogy: Not wearing a name tag that says "Security Tester"
#### 7. Connection Reuse & Pooling
What it does: Uses per-host HTTP client pools, keeps connections alive
Why it works: Browsers reuse connections. Opening/closing for every request looks suspicious
Simple analogy: Keeping the door open instead of slamming it shut and ringing the bell again
#### 8. Custom Header Injection
What it does: Can add headers like Referer, X-Forwarded-For, custom cookies
Why it works: Makes requests look like they came from a legitimate application flow (clicked a link, ha cookies)
Simple analogy: Showing a ticket stub when entering a venue instead of jumping the fence
#### Detection Comparison
| Technique | Without E | With E |
|-----------|----------------|-------------|
| User-Agent | python-requests/2.28.0 (obvious bot) | Mozilla/5.0 (Windows NT 10.0; Win64; x64)... (looks like Chrome) |
| Timing | Perfect 100ms intervals → WAF blocks | 120ms, 95ms, 180ms → looks human |
| Retries | Instant retry → ban | Wait 1s→2s→4s → "patient client" |
| Concurrency | 100 parallel hits → alarm | Adaptive 5→10→3 based on response → "polite browser" |
#### When to use --waf-e
- Baseline diffing (only report new findings)
- Streaming NDJSON output for real-time monitoring
- SARIF 2.1.0 for GitHub/GitLab Code Scanning
- Exit code bitmask for pipeline control
- Se filtering and failure thresholds
- Rust async runtime (tokio) with zero-cost abstractions
- Concurrent scanning with semaphore-bounded parallelism
- Per-host HTTP client pools to avoid connection bottlenecks
- Efficient memory usage (no GC pauses)
- JSON-based auth flows with cookie/header extraction
- Dual-identity IDOR/BOLA testing
- Session file import (Excalibur integration)
- Bearer, Basic, and custom header auth
- Automatic unauth client for pri escalation checks
Scanner Modules
ApiHunter includes 13 built-in scanner modules. See docs/scanners.md for detailed detection logic.
| Scanner | Type | What It Detects |
|---------|------|----------------|
| CORS | Passive | Wildcard origins, reflected origins with credentials, null origin acceptance, regex bypass (suffix/prefix attacks), missing Vary: Origin, unsafe preflight methods |
| CSP | Passive | Missing Content-Security-Policy, unsafe-inline/unsafe-e, wildcard sources, bypassable CDN hosts (JSONP gadgets), missing frame-ancestors |
| GraphQL | Passive | Introspection enabled, sensiti fields (user/password/token types), field suggestions (schema leakage), query batching, alias amplification (DoS), GraphiQL/Playground exposure |
| JWT | Passive | alg=none tokens, weak HS256 secrets (wordlist-based), missing/excessi, sensiti in payload, algorithm confusion |
| OpenAPI | Passive | Missing security schemes, operations without auth requirements, file upload endpoints, deprecated operations still present, unsecured sensiti |
| API | Passive | header disclosure, concurrent legacy/new API , deprecation headers, and response drift across benign query/ (plus deep mode via --response-diff-deep) |
| gRPC/Protobuf | Passive + Active | gRPC transport/content-type signals, protobuf surface hints, and optional reflection/health probe signals |
| API Security | Passive + Active | Missing security headers (X-Content-Type-Options, X-Frame-Options), ser disclosure, unauthenticated access to sensiti, HTTP method enumeration, debug endpoints, secret exposure patterns, active IDOR/BOLA checks (body + selected header comparison), blind SSRF callback probes, and gateway/bypass probe signals |
| Mass Assignment | Active | Reflected sensiti (is_admin, role, permissions), persisted state changes, pri escalation injection |
| OAuth/OIDC | Active | Redirect URI bypass, missing state parameter, PKCE support issues (missing S256, plain allowed), implicit flow enabled, password grant enabled |
| Rate Limit | Active | Missing rate limiting (burst probes), missing Retry-After headers, IP header spoofing bypass (X-Forwarded-For) |
| WebSocket | Active | WebSocket upgrade acceptance on common paths, missing origin , unauthenticated WebSocket connections |
| C | Active | Template-driven C from assets/c/*.toml (168 templates currently), baseline differential matching |
Passi run by default and analyze responses without sending crafted requests.
Acti/checks require --acti and send potentially in probes (IDOR/BOLA, mutation, bypass tests).
IDOR/BOLA li the API Security scanner (there is no dedicated --no-idor flag; use --no-api-security to disable it).
Module Output & Signal Notes
These notes summarize how findings are emitted and what typically causes noise:
| Module | Finding Prefix / Shape | Common False Positives | Common False Negatives |
|---------|-------------------------|-------------------------|-------------------------|
| CORS | cors/* with origin/e fields | Reflection on non-sensiti | Origin checks applied only on authenticated routes |
| CSP | csp/* with directi | Legacy CSP applied intentionally during migration | CSP delivered only on production CDN edge path |
| GraphQL | graphql/* with endpoint + capability signal | Public playground intended for internal/testing tenants | Schema controls enabled only after auth |
| JWT | jwt/* with token claim/header e | Test/demo tokens in synthetic responses | Token ne in scanned responses |
| OpenAPI | openapi/* with operation/security context | Spec intentionally includes deprecated but blocked endpoints | Spec una or split across private docs |
| API | api_/* + response_diff/* | Multiple supported during controlled migrations | paths not disco from current seed set |
| gRPC/Protobuf | grpc_protobuf/* with transport/reflection e | gRPC-like metadata on edge proxies without exposed RPC surface | gRPC endpoints behind separate host/path not reached from seed set |
| API Security | api_security/* with header/path/method e | Debug/test endpoints intentionally exposed in non-prod | Controls enforced behind auth/session context |
| Mass Assignment | mass_assignment/* with reflected/persisted deltas | Echo behavior that does not persist backend state | Mutations rejected by hidden rules |
| OAuth/OIDC | oauth/* with redirect/metadata e | Non-production IdP config with relaxed policies | Dynamic policy enforcement not in metadata |
| Rate Limit | rate_limit/* with burst/429 behavior | Global traffic shaping masks app-le behavior | Long-window limiters not triggered by short probe window |
| WebSocket | websocket/* with upgrade/origin checks | Public WS endpoints intentionally anonymous | Auth required headers not provided in probe |
| C | cve/<id>/<check> with template e | Fingerprint collision on generic endpoints | path/context not reached from seed URLs |
For check-by-check detail and remediation guidance, see docs/scanners.md and docs/findings.md.
The scanner docs now include a source-aligned Module Check Catalog and False-Positi Model.
Features
Passi Analysis
- Dynamic origin generation based on target domain
- Regex bypass testing (suffix/prefix attacks)
- Credential-aware se scoring
- Wildcard and null origin detection
- Missing/weak Content Security Policy detection
- Unsafe inline/e
- Wildcard source detection
- Policy bypass patterns
- Introspection query detection
- Sensitive type/field name analysis
- Query batching support detection
- Alias amplification (DoS) probing
- Acti fuzzing (
--acti, supports --dry-run)- GraphiQL/Playground exposure
- Algorithm confusion (alg=none, HS256→RS256)
- Weak secret detection (curated wordlist)
- Long-li detection (missing/excessive exp)
- Sensiti exposure
- Token extraction from headers and cookies
- Security scheme
- File upload endpoint detection
- Deprecated operation flagging
- Missing security definitions
- Spec caching for performance
- gRPC response metadata/content-type detection
- Protobuf surface hint detection from endpoint metadata/path shape
- Optional reflection/health acti signals on known gRPC paths
- AWS keys (AKIA*, secret keys)
- Google API keys (AIza*)
- GitHub tokens (ghp_*, github_pat_*)
- Slack tokens (xox*)
- Stripe keys (sk_live_*, pk_live_*)
- Database URLs, private keys, bearer tokens
- Context-aware (reduces false positives)
- HTTP method enumeration
- Debug endpoint detection
- Directory listing exposure
- Security.txt presence
- Response header analysis (HSTS, X-Frame-Options, etc.)
- Error message disclosure
Acti Testing (--acti)
- Unauthenticated access testing
- Response comparison via body fingerprints plus stable header snapshots
- ID enumeration (±2 range walk)
- Cross-user authorization bypass (dual-identity)
- Blind SSRF callback probing query params (
APIHUNTER_OAST_BASE, supports --dry-run)- Gateway fingerprint and bypass probing (
api_security/gateway-*)- Reflected sensiti injection
- Persisted state change detection
- Baseline→Mutate→Confirm
- Pri escalation injection
- Redirect URI bypass
- State parameter handling
- PKCE support detection
- Metadata configuration hardening
- Implicit flow and password grant detection
- Burst request probing
- Missing rate limit detection
- Retry-After header
- IP header spoofing bypass tests
- Upgrade acceptance on common paths
- Origin testing
- Missing authentication checks
- TOML-based template catalog
- Nuclei YAML import support
- Baseline differential matching
- Host+template deduplication
- Loader quality gates skip invalid/unsafe request templates (for example unresol placeholders)
- Segment-aware context matching reduces broad path-substring o
- Current local catalog: 168 templates (includes curated hardened checks such as C, C, C, C, C, C)
Discovery & Enumeration
- robots.txt parsing
- sitemap.xml parsing
- OpenAPI/Swagger spec import
- HAR file import (Excalibur integration)
- Postman/Insomnia collection import (
--collection)- Ja endpoint extraction
- Same-host filtering
- Fast pre-check to skip dead endpoints
- Configurable timeout
- Optional bypass with --no-filter
Performance & Reliability
- Automatic rate adjustment based on errors
- Additi (every 5s)
- Multiplicati on 429/503/timeouts
- User-Agent rotation from runtime pool (assets/user_agents.txt with 100+ real UAs)
- Embedded fallback UAs if file una
- Random delay jitter to avoid detection patterns
- Per-host timing enforcement (not global)
- Retry logic with exponential backoff
- Custom header injection (X-Forwarded-For, Referer, etc.)
- Adapti based on 429/503 responses
- Politeness mode for cooperati
- No scanner fingerprints in User-Agent or headers by default
- Semaphore-bounded parallelism
- Per-host HTTP client pools
- Connection reuse and pooling
- Configurable timeouts and retries
- Panic recovery
- Captured errors reported separately
- Graceful degradation on scanner failures
Output & Reporting
- Pretty JSON (human-readable)
- NDJSON (streaming, parseable)
- SARIF 2.1.0 (GitHub/GitLab Code Scanning)
- Generate baseline snapshots
- Compare scans to report only new findings
- Perfect for regression testing
--no-auto-report):- Saved to ~/Documents/ApiHunterReports/<timestamp>/
- findings.json (structured findings)
- summary.md (markdown report)
- scan.log (execution log)
- Stream findings as they're discovered
- NDJSON format for li
- Progress tracking
- Filter by minimum se (info/low/medium/high/critical)
- Fail-on threshold for CI/CD
- Exit code bitmask (0x01 findings, 0x02 errors)
Integration & Extensibility
- Implement Scanner trait to add modules
- Async-first design
- Independent scanner execution
- Panic isolation per scanner
- C catalog in assets/c/*.toml
- No code changes needed to add new checks
- Template-dri detection
- Community-shareable template format
- template-tool binary for YAML → TOML con
- Automatic matcher translation (status, word, regex, dsl)
- Safe preflight request-chain extraction
- Preser logic from upstream templates
- Code-based: Write Rust scanners implementing Scanner trait for complex logic
- Template-based: Write TOML templates for signature-based checks (CVEs, misconfigs)
- Best of both worlds: performance + flexibility
- Excalibur browser extension (HAR capture)
- BurpAPIsecuritysuite (manual testing)
- Workflow: Capture → Automate → Deep test
Configuration & Control
- File-based URL lists
- stdin (pipe from other tools)
- HAR file import
- Postman/Insomnia collection import
- OpenAPI spec import
- Enable/disable indi scanners
- Active mode
- Dry-run for acti
- Per-scanner configuration
- HTTP/HTTPS proxy support
- TLS certificate control
- Custom headers and cookies
- Configurable timeouts and retries
- quickscan.sh (fast, low-impact)
- deepscan.sh (comprehensi checks)
- inaccessiblescan.sh (re-check pre inaccessible targets with slower settings)
- baselinescan.sh (generate baseline)
- diffscan.sh (compare against baseline)
- authscan.sh (authenticated scanning)
- sarifscan.sh (CI/CD integration)
- scan-and-report.sh (run scan + print latest report path)
- split-by-host.sh (split targets by host and optionally fan out scans)
Comparison with Other Tools
| Feature | ApiHunter | Nuclei | ZAP | Burp Suite | ffuf |
|---------|-----------|--------|-----|------------|------|
| Language | Rust | Go | Java | Java | Go |
| Performance | ⚡⚡⚡ Async, adapti | ⚡⚡ Fast parallel | ⚡ Moderate | ⚡ Moderate | ⚡⚡⚡ Very fast |
| API-First Design | ✅ Built for APIs | ❌ General web | ⚠️ Hybrid | ⚠️ Hybrid | ❌ Fuzzing focus |
| False Positi | ✅ SPA detection, body , referer checks | ⚠️ Template-dependent | ⚠️ Many FPs | ✅ Good | N/A |
| CORS/CSP Analysis | ✅ Deep policy parsing | ⚠️ Basic templates | ✅ Good | ✅ Good | ❌ |
| GraphQL Introspection | ✅ Schema exposure + sensiti checks | ⚠️ Basic detection | ⚠️ Limited | ✅ | ❌ |
| OpenAPI/Swagger | ✅ Security scheme analysis | ❌ | ✅ Import only | ✅ Import + scan | ❌ |
| JWT Analysis | ✅ alg=none, weak secrets, expiry | ⚠️ | ⚠️ Limited | ✅ | ❌ |
| IDOR/BOLA Detection | ✅ 3-tier (unauth/range/cross-user) | ⚠️ Manual templates | ⚠️ Limited | ✅ Manual testing | ❌ |
| Secret Detection | ✅ Context-aware (frontend ) | ⚠️ Regex-based | ⚠️ Basic | ⚠️ Basic | ❌ |
| Acti | ✅ Opt-in (IDOR, mass-assignment, OAuth/OIDC, websocket, rate-limit, C) | ✅ Template-based | ✅ Active scan | ✅ Active scan | ✅ Fuzzing |
| WAF E | ✅ UA rotation, delays, retries, adapti | ⚠️ Basic | ⚠️ Limited | ✅ Good | ⚠️ Basic |
| CI/CD Integration | ✅ NDJSON, SARIF, exit codes | ✅ JSON, SARIF | ⚠️ XML reports | ⚠️ XML/JSON | ✅ JSON |
| Baseline Diffing | ✅ Built-in | ❌ External tools | ❌ | ❌ | ❌ |
| Auth Flows | ✅ JSON-based pre-scan login | ⚠️ Header injection | ✅ Session mgmt | ✅ Session mgmt | ⚠️ Header injection |
| Streaming Output | ✅ Real-time NDJSON | ❌ Batch only | ❌ | ❌ | ✅ |
| Resource Usage | 🟢 Low (Rust) | 🟢 Low (Go) | 🟡 High (Java) | 🟡 High (Java) | 🟢 Low (Go) |
| Learning Curve | 🟢 Simple CLI | 🟢 Template syntax | 🟡 GUI complexity | 🔴 Steep | 🟢 Simple |
| Extensibility | ✅ Rust trait system | ✅ YAML templates | ✅ Add-ons | ✅ Extensions | ⚠️ Limited |
| License | MIT (Free) | MIT (Free) | Apache 2.0 (Free) | Commercial | MIT (Free) |
| Best For | API security in CI/CD, regression testing, CORS/GraphQL/JWT analysis | General vuln scanning, C | Full web app pentesting | Manual pentesting, complex workflows | Directory/parameter fuzzing |
Key Differentiators
ApiHunter: API-first design, SPA detection, baseline diffing, 3-tier IDOR/BOLA, context-aware secrets, AIMD concurrency, stealth/WAF e (UA rotation, jitter, adapti), dual extensibility (TOML templates + Rust modules)
Nuclei: Broader C, YAML templates only, basic e
ZAP/Burp: Manual testing, proxy workflows, GUI-based extensions, limited stealth
ffuf: Pure fuzzing, content discovery, limited extensibility, basic e
Quick Start
Desktop Quick Start (Tauri + React)
ApiHunter also ships a desktop app in apps/desktop.
Desktop scan input supports:
Load CSV (max 307,200 bytes / 300 KiB)Quick Passive and Deep Activehttp/https URLs)OAST callback base) for actiAPI and gRPC/ProtobufSafety and Scan Behavior, Runtime Limits, and Scanner toggles are collapsed by defaultSave All Reports + per-run timestamped filenames; exports include per-target JSON bundles, NDJSON, SARIF, Insomnia collection, and Insomnia Runner dataSee HOWTO.md for detailed usage, docs/lab-setup.md for C labs, and docs/ for internals.
If you want a release desktop binary:
Install a clickable Linux app icon/launcher:
Note: desktop de now uses built frontend assets directly and does not require a separate localhost:1420 server.
See HOWTO.md for detailed usage, docs/lab-setup.md for C labs, and docs/ for internals.
Example NDJSON Finding
Architecture
Flow: CLI args → Config → Runner orchestrates Discovery + Scanners → HTTP Client (with Auth/WAF) → Reports
Template Tooling
ApiHunter supports dual extensibility: add checks via TOML templates (no code) or Rust modules (full control).
TOML Template Format
Create custom checks in
assets/c/*.toml:Import Nuclei Templates
Convert existing Nuclei YAML templates:
Add Custom Rust Scanners
Implement the
Scanner trait for complex logic:See HOWTO.md and docs/scanners.md for details.
Scan Scripts
ScanScripts/ contains con wrappers for common scan profiles:
--auth-flow, enables acti, WAF e, retries: 2, timeout: 15s, delay: 150ms)Usage Examples
All wrapper scripts except split-by-host.sh support --stdin and trailing ApiHunter flags.
Testing Strategy
ApiHunter testing is split by intent:
tests/*_scanner.rs, parser/config tests): scanner logic and edge cases.tests/integration_runner.rs, startup/CLI behavior): orchestration and runtime wiring.tests/c.rs, tests/crity.rs): replay real payloads and compare against pinned upstream templates.cargo test).See the dedicated Testing Guide for the full test matrix and co map.
Run focused suites:
Run full :
Run real-data integration gate (fixtures + li suites):
Li use default target in:
targets/-public.txttargets/real-world-integration-public.txtYou can o with:
APIHUNTER_LI or APIHUNTER_LIAPIHUNTER_LI or APIHUNTER_LIDocumentation
Complete documentation is a in docs/. Start with:
Roadmap
Completed (v0.7.0): Glass UI redesign, scan persistence (last-scan store), results analytics dashboard (se heatmap, worst-target card, scan efficiency, scanner co, check se breakdown), Enrich → Deep-Scan promote flow, Triage/threat-intel mode, Discovery configuration, WebSocket/Mass-Assignment/OAuth/Rate-Limit/C, expanded Nuclei importer, Docker image
Next: App.tsx component split, scan history ring-buffer, finding detail drawer, HTML/PDF report export, GitHub Actions nati, per-target timing in li
Installation
CLI Installation
Requires Rust stable (tested on 1.76+).
Prebuilt Release Artifacts
Tagged releases (v*) publish prebuilt apihunter binaries for:
x86_64-unknown-linux-gnu, aarch64-unknown-linux-gnu)x86_64-apple-darwin)x86_64-pc-windows-msvc)Each release also publishes supply-chain artifacts:
*.sha256)*.sig, *.pem, *.sigstore.json)apihunter-release-assets-sbom.spdx.json)Download from GitHub Releases.
Desktop Installation (Tauri + React)
Desktop app source lives in apps/desktop.
Build and run a production desktop binary:
For de mode:
Install a clickable Linux launcher icon:
Desktop features (brief):
Quick Passive and Deep ActiveDocker
Run a scan from files in your current directory:
CLI Reference
| Flag | Default | Description |
|---|---|---|
| --urls | required* | Path to newline-delimited URL file |
| --stdin | off | Read newline-delimited URLs from stdin |
| --har | off | Import likely API request URLs from HAR (log.entries[].request.url) |
| --collection | off | Import likely API request URLs from Postman/Insomnia collection export JSON |
| --output | stdout | Write results to a file instead of stdout |
| --format | pretty | Output format: pretty, ndjson, or sarif |
| --stream | off | Stream NDJSON findings as they arrive |
| --baseline | none | Baseline NDJSON for diff-only findings |
| --quiet | off | Suppress non-error stdout output |
| --summary | off | Print summary even in quiet mode |
| --no-auto-report | off | Skip writing local auto reports under ~/Documents/ApiHunterReports |
| --min-se | info | Filter findings below this level |
| --fail-on | medium | Exit non-zero at or above this se |
| --concurrency | 20 | Max in-flight requests |
| --max-endpoints | 50 | Limit scanned endpoints per site (0 = unlimited) |
| --delay-ms | 150 | Minimum delay between requests per host |
| --retries | 1 | Retry attempts on transient failure |
| --timeout-secs | 8 | Per-request timeout in seconds |
| --no-filter | off | Skip pre-filtering of inaccessible URLs |
| --filter-timeout | 3 | Timeout for accessibility pre-check (seconds) |
| --no-discovery | off | Skip endpoint discovery and scan only provided seed URLs |
| --waf-e | off | Enable WAF e heuristics |
| --user-agents | none | Comma-separated UA list (implies WAF e) |
| --headers | none | Extra request headers (e.g. Authorization: Bearer ...) |
| --cookies | none | Comma-separated cookies (e.g. session=abc,theme=dark) |
| --auth-bearer | none | Add Authorization: Bearer <token> |
| --auth-basic | none | Add HTTP Basic auth (user:pass) |
| --auth-flow | none | JSON auth flow file (pre-scan login) |
| --auth-flow-b | none | Second auth flow for cross-user IDOR checks |
| --unauth-strip-headers | none | Extra header names to strip for unauth probes |
| --session-file | none | Load/sa from Excalibur session JSON ({"hosts": {...}}) |
| --proxy | none | HTTP/HTTPS proxy URL |
| --danger-accept-in | off | Skip TLS certificate |
| --acti | off | Enable acti in) probes |
| --dry-run | off | Dry-run acti (report intended probes without sending mutation requests) |
| --response-diff-deep | off | Enable deeper response-diff probes in API checks |
| --per-host-clients | off | Use per-host HTTP client pools |
| --adapti | off | Adapti (AIMD) |
| --no-cors | off | Disable the CORS scanner |
| --no-csp | off | Disable the CSP scanner |
| --no-graphql | off | Disable the GraphQL scanner |
| --no-api-security | off | Disable the API security scanner |
| --no-jwt | off | Disable the JWT scanner |
| --no-openapi | off | Disable the OpenAPI scanner |
| --no-api- | off | Disable the API scanner |
| --no-grpc-protobuf | off | Disable the gRPC/Protobuf scanner |
| --no-mass-assignment | off | Disable the Mass Assignment scanner (acti) |
| --no-oauth-oidc | off | Disable the OAuth/OIDC scanner (acti) |
| --no-rate-limit | off | Disable the Rate Limit scanner (acti) |
| --no-c | off | Disable the C scanner (acti) |
| --no-websocket | off | Disable the WebSocket scanner (acti) |
*You must provide exactly one of --urls, --stdin, --har, or --collection.
Exit Codes
| Code | Meaning |
|---|---|
| 0 | No findings at/above --fail-on threshold and no errors |
| 1 | One or more findings at/above --fail-on threshold |
| 2 | One or more scanners captured errors |
| 3 | Both findings and errors |
Security & Legal Guardrails
--proxy does not disable TLS on its own. Certificate checks remain enabled unless --danger-accept-in is explicitly set.--danger-accept-in is intended for controlled lab/debug use only. ApiHunter emits an explicit runtime warning when this flag is enabled.--waf-e and acti may trigger IDS/WAF alerts. Run only with explicit written authorization and within agreed test windows.Related Projects
ApiHunter is part of a complementary security testing toolkit:
--har and --session-file flags.Workflow: Capture traffic with Excalibur → Automated baseline with ApiHunter → Deep manual testing with BurpAPIsecuritysuite
About
Author: Teycir Ben Soltane
Email:
Website: teycirbensoltane.tn
FAQ
Q: Why ApiHunter /ZAP/Burp?
A: API-first design, SPA detection, baseline diffing, 3-tier IDOR, context-aware secrets. Complementary to Nuclei (C) and ZAP/Burp (manual testing).
Q: Production-safe?
A: Yes. Use --delay-ms and lower --concurrency. Try quickscan.sh.
Q: Authenticated scans?
A: --auth-bearer, --auth-basic, or --auth-flow. For IDOR: --auth-flow-b.
Q: Speed comparison (1000 endpoints)?
Depends on endpoint latency, retries, target behavior, and enabled checks. Use --concurrency, --delay-ms, and --acti to tune throughput .
Q: Slow scan?
Increase --concurrency (default: 20), reduce --delay-ms (default: 150ms), enable --adapti.
Q: Output formats? pretty (default), ndjson (streaming), sarif (CI integration).
Q: CI/CD integration?
Q: Baseline diffing?
Q: Passive checks?
Passi): analyze responses. Active (--acti): send crafted requests (IDOR, mass-assignment, OAuth, rate-limit, C).
Q: CORS testing?
Dynamic origin generation: null, , , . Tests regex bypasses when reflected.
Q: IDOR detection?
3-tier: (1) unauthenticated fetch, (2) ID enumeration (±2), (3) cross-user (--auth-flow-b).
Q: Secret detection?
AWS/Google/GitHub/Slack/Stripe keys, bearer tokens, DB URLs, private keys. Context-aware .
Q: Cookies? --cookies "session=abc", --session-file excalibur.json, or --auth-flow login.json.
Q: Proxy? --proxy
Q: Debug logging? RUST_LOG=debug ./target/release/apihunter --urls targets/cc.txt
Q: Adapti?
AIMD: increases by 1 every 5s, halves on errors (429/503/timeouts). Enable with --adapti.
Q: Disable scanners? --no-cors, --no-csp, --no-graphql, --no-api-security, --no-jwt, --no-openapi, --no-api-, --no-mass-assignment, --no-oauth-oidc, --no-rate-limit, --no-c, --no-websocket.
Q: Is ApiHunter stealthy?
A: Yes. Features: UA rotation from 100+ real browsers (assets/user_agents.txt), randomized delays with jitter, per-host rate limiting, adapti on 429/503, no scanner fingerprints in headers, exponential retry logic, custom header injection. Enable with --waf-e.
Q: How does WAF e work?
A: Automatically rotates User-Agents from curated pool, adds random jitter to delays, enforces per-host timing (not global bursts), backs off exponentially on rate limits, and allows custom header injection to blend with legitimate traffic. No "scanner" strings in default headers.
See CONTRIBUTING.md for de guidelines.
License
MIT
项目信息
开发语言:Rust
Star 数:24
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ApiHunter - Async API security scanner in Rust for CORS, CSP, |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:53:04 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 351 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |