 安全软件
点击放大
patchbot - Vulnerability scanning with your own scanners and
项目说明
<di="center">
patchbot
scanning with your scanners, your threat feeds, and a coding agent that opens the fix PR.
![PyPI]()
![Python 3.11+]()
![CI]()


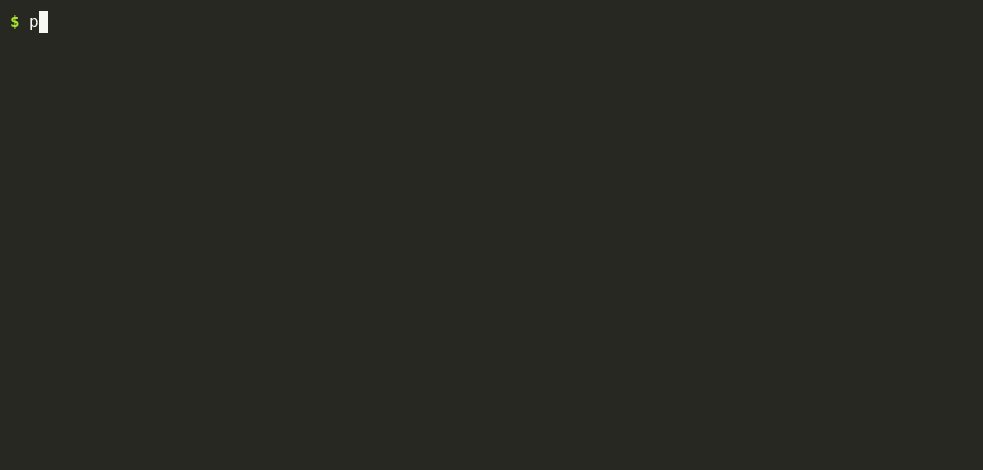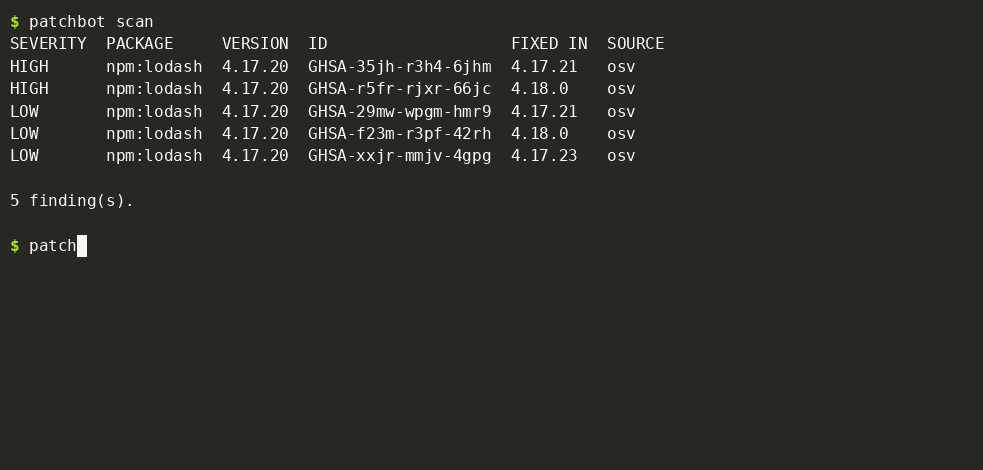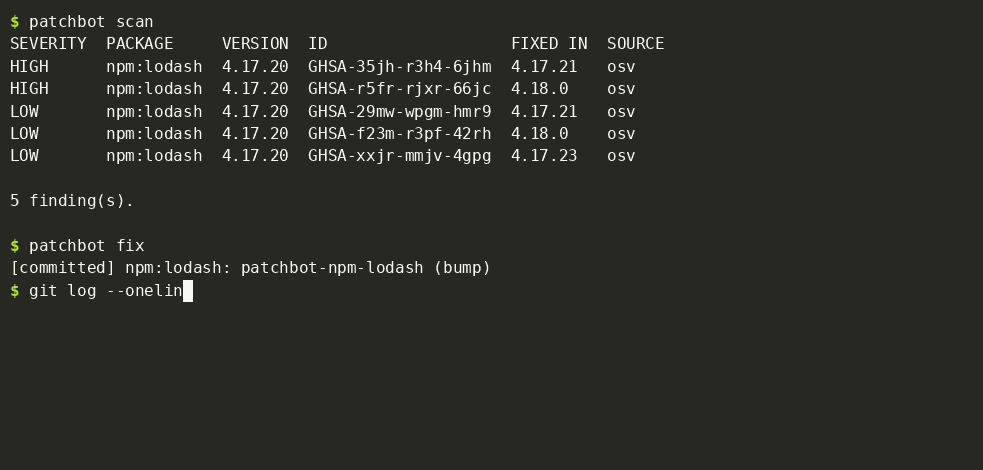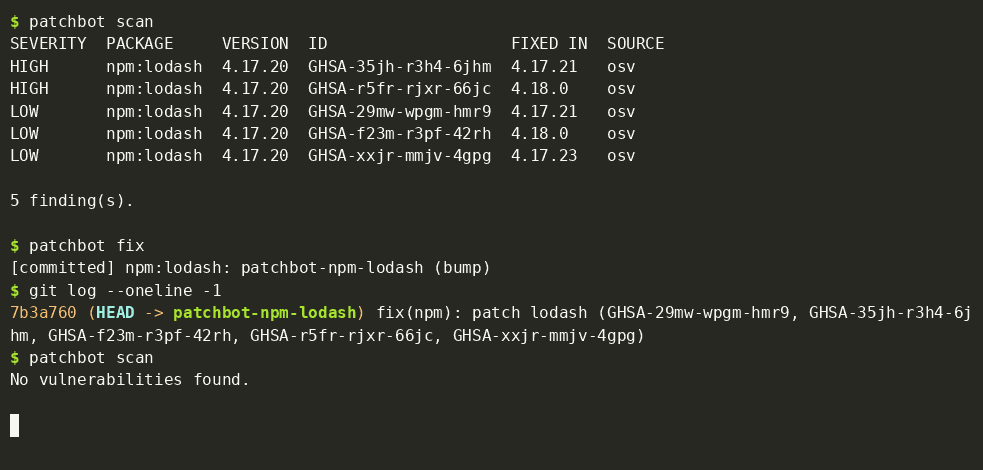
<img src="docs/img/patchbot-demo.gif" alt="patchbot finds 5 ad, fixes them, and re-scans clean" width="800">
</div>
---
patchbot in the packages in your repository, matches them against any threat feed, accepts findings from any scanner, and fixes what it finds. When a bump is enough, it bumps. When the bump breaks the build, it hands the failure to a coding agent. It re-scans before opening each pull request.
Run it as a CLI, as a GitHub Action, or as a scheduled Claude Managed Agents deployment with no CI in.
Why patchbot
| | Dependabot / Renovate | Trivy / Grype alone | patchbot |
|---|---|---|---|
| Bring your own threat feed (private ad, OS) | no | no | yes |
| Bring your own scanner (any tool that emits SARIF / Trivy / Grype JSON) | no | n/a | yes |
| bump + lockfile regeneration with no model call | yes | no | yes |
| Fixes that need code changes (breaking major bump, failing tests) | no | no | yes, agent tier |
| Re-scan before every PR | no | no | yes |
| Agent runs off the CI runner; secrets stay out of the sandbox | no | no | yes, Managed Agents |
| Works without CI (scheduled, any git host) | no | no | yes |
Installation
Requires Python 3.11 or newer. No other runtime dependencies.
Quick start
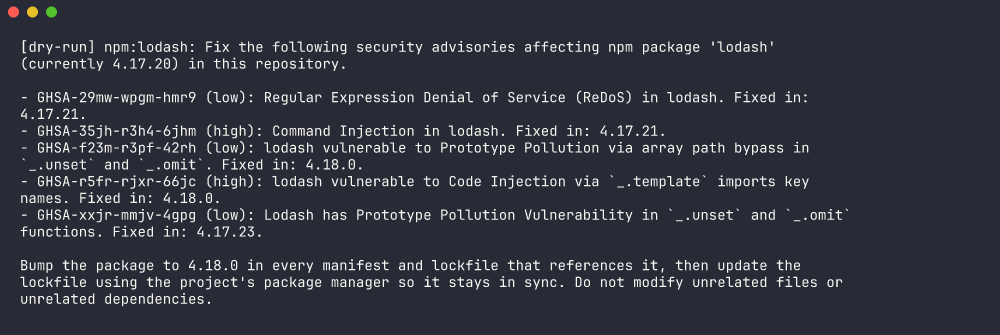
<img src="docs/img/fix-dry-run.png" alt="patchbot fix --dry-run" width="800">
How it works
In. Parsers for npm, pnpm, and yarn lockfiles, requirements*.txt, pyproject.toml, go.mod, and Cargo.toml. For other ecosystems, point patchbot at a CycloneDX SBOM from syft, cdxgen, or your own tooling.
Feeds. OSV.dev is on by default. To add a private feed, ser JSON from a file or URL. You keep one format.
Scanners. Wrappers for trivy, grype, and os. The command scanner runs any tool that writes SARIF, Tri, or os JSON to stdout.
Fix. One branch per package, in four steps:
1. Bump. patchbot rewrites the pin to the lowest that clears every ad and regenerates the lockfile with the ecosystem's own tool. No model call.
2. . patchbot re-scans, runs test_cmd, and rejects any diff that reaches outside the dependency surface (CI config, dotfiles).
3. Escalate. If step 2 fails, patchbot briefs the agent with the failure itself: "bumped lodash to 4.18.0; tests fail with ...". The agent fixes the code.
4. again. Then commit, push, and open the PR with the ad table in the body.
--agent none skips step 3 and gives you bump-only mode.
Commands
| Command | What it does |
|---|---|
| patchbot scan [paths...] | Run the pipeline and print a report. Exits 1 when any finding meets --fail-on (default high). |
| patchbot fix [paths...] | Run the fix loop. --dry-run previews; --pr pushes and opens pull requests through gh. |
| patchbot plugins | List each registered feed, scanner, and agent, built in and third party. |
| patchbot managed ... | Set up (init) and schedule (deploy, list, pause, unpause) the Managed Agents backend. |
<details>
<summary><code>patchbot scan</code></summary>
<br>
<img src="docs/img/scan.png" alt="patchbot scan" width="800">
</details>
<details>
<summary><code>patchbot scan --format json</code></summary>
<br>
<img src="docs/img/scan-json.png" alt="patchbot scan --format json" width="800">
</details>
<details>
<summary><code>patchbot plugins</code></summary>
<br>
<img src="docs/img/plugins.png" alt="patchbot plugins" width="800">
</details>
Configuration
Put patchbot.toml in the repository root. CLI flags o the file.
Choosing an agent backend
| Backend | Runs where | Needs | Use it for |
|---|---|---|---|
| claude / codex | Your machine or runner, through the CLI on PATH | The CLI, logged in | Local de |
| api | Your runner, in process | pip install patchbot[api], ANTHROPIC_API_KEY | CI without Node |
| openai | Your runner, in process | pip install patchbot[openai], OPENAI_API_KEY | CI without Node, on OpenAI models |
| command | Wherever your tool runs | Any agent that accepts a prompt (aider, opencode, ...) | Non-Anthropic models |
| managed | Anthropic's sandbox, off your runner | patchbot managed init once, three IDs as secrets | CI where the agent must not see repo secrets |
Managed Agents, the recommended CI backend
An agent with a shell on your CI runner sits next to your repository secrets. The managed backend moves the agent into a Claude Managed Agents sandbox. Anthropic's git proxy authenticates git push; a GitHub MCP credential creates the pull request. Your GitHub token stays outside the sandbox. patchbot then re-scans the pushed branch on your side before it treats the fix as done.
GitHub Actions
Scan and publish to the Security tab
<img src="docs/img/code-scanning.jpg" alt="Code scanning alerts detected by patchbot" width="800">
Auto-fix with Managed Agents (no Node, no agent on the runner)
Auto-fix with the in-runner api backend
Weekly, against a private feed
action.yml documents each input. .github/workflows/patchbot-fix-example.yml is a complete workflow you can copy.
A pull request opened by patchbot fix --pr:
<img src="docs/img/fix-pr.jpg" alt="A pull request opened by patchbot" width="800">
Scheduled deployments (no CI)
patchbot managed deploy creates a cron-scheduled Managed Agents session that clones your repositories, scans, fixes, and opens pull requests. Nothing in it depends on GitHub Actions, so it works with GitLab and Bitbucket too.
Manage it with patchbot managed list | pause | unpause. Anthropic jitters scheduled runs by up to nine minutes, and 1 to 3 AM local wall-clock times can skip or double-fire across DST changes. Schedule outside that window, or use UTC.
Extending patchbot
Register a scanner, feed, or agent from your own package through entry points. No fork needed.
If you would rather not write Python, [scanners.*] type = "command" and [feeds.*] type = "url" | "file" cover most cases. cmd run through your shell, so point them at tools you trust.
FAQ
Why did a fix report failed? patchbot prints the reason: the ad still reproduces after the bump or the agent run, test_cmd failed (with the log tail), or the change touched files outside the dependency surface. patchbot discards the branch and commits nothing.
What sets the exit code? scan exits 1 when any finding meets --fail-on or worse; none exits 0. fix exits 1 if it could not fix any package.
How do I suppress one ad? [report] ignore = ["GHSA-..."].
Do I need Node in CI? Only for --agent claude or codex. The api, openai and managed backends need Python alone.
Which ecosystems include transiti? npm, pnpm, and yarn, through their lockfiles. For Python, Go, and Rust, set [in] sbom to a CycloneDX file to scan the full resolved tree.
De
examples/demo-npm ships with a lodash on purpose. The repository's own CI scans it, so the Security tab always shows li.
License
MIT
项目信息
开发语言:Python
Star 数:21
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Vulnerability scanning with your own scanners and threat feeds, plus a coding agent that opens the fix PR. CLI, GitHub Action, or scheduled Managed Agents deployment.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | patchbot - Vulnerability scanning with your own scanners and |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:53:54 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 247 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |