 安全软件
点击放大
opena2a - One scan for AI risk. `opena2a review` checks an A
项目说明
opena2a-cli

> OpenA2A: CLI · HackMyAgent · Secretless · AIM · Browser Guard · DVAA
Unified CLI for the OpenA2A security toolchain. One command finds credential leaks, shadow AI, unsigned configs, and ungo agents, then fixes them. Apache 2.0.
![npm ]()

Website · Docs · Demos · Discord
Quick start
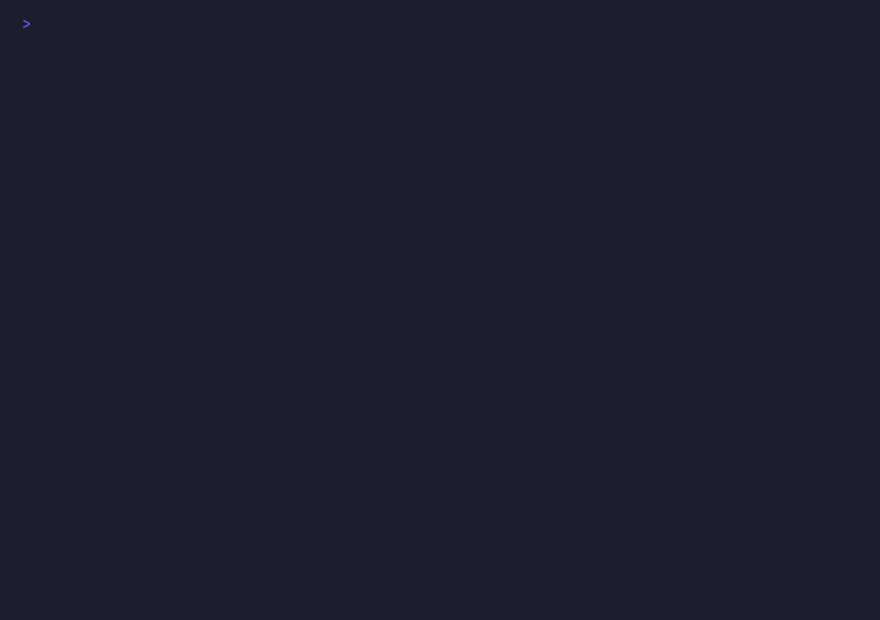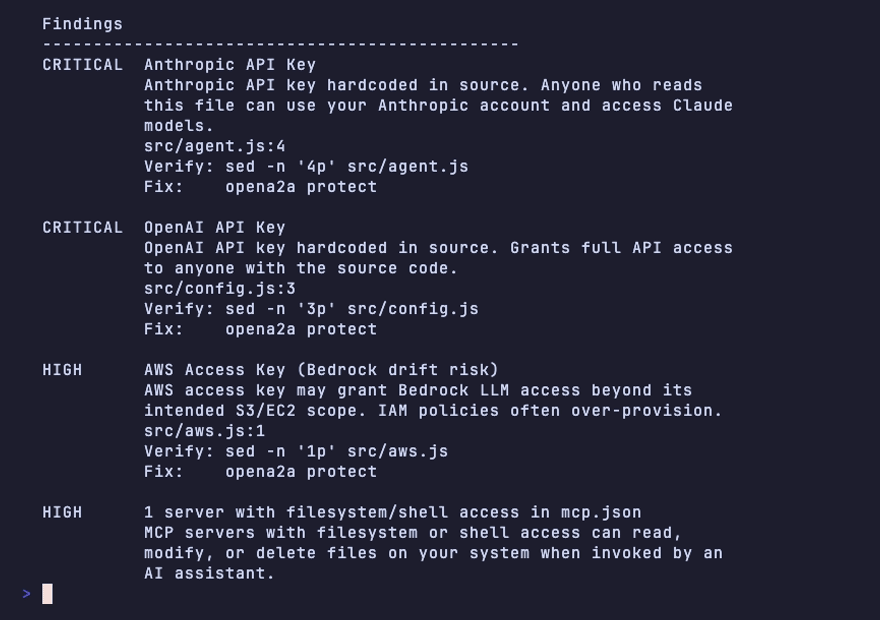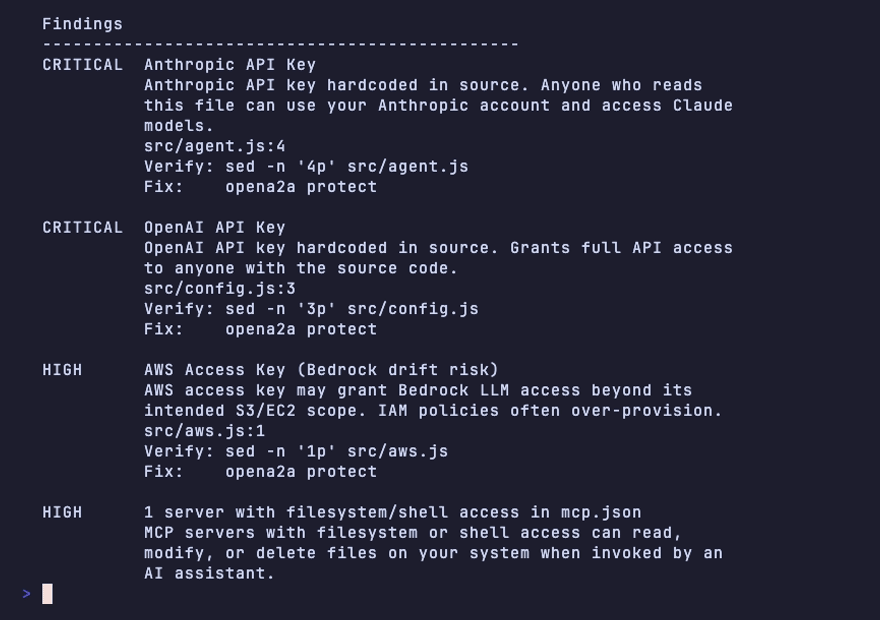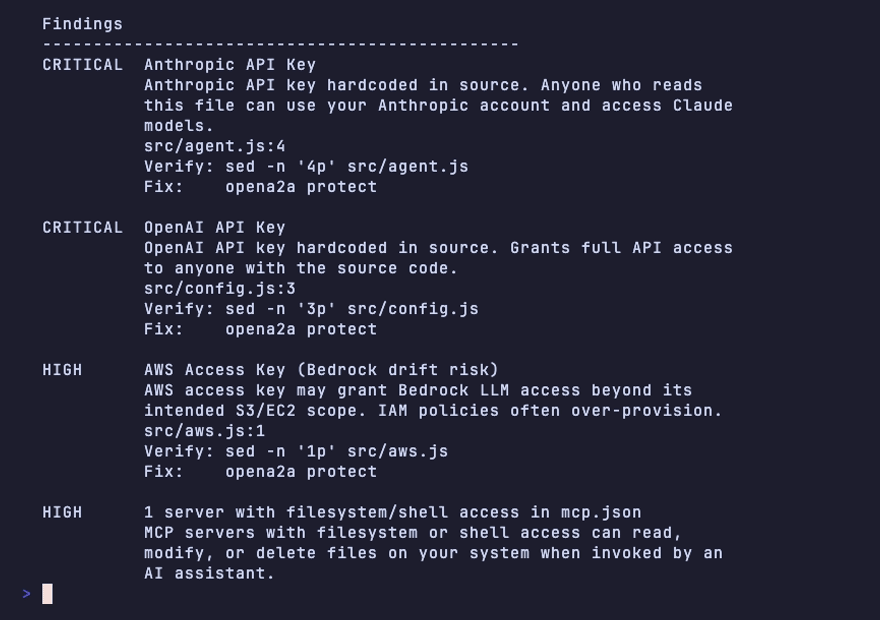
What init prints (captured from opena2a-cli 0.10.13 on a small demo project, trimmed):
!opena2a review
Install
npm
Requires Node.js 18 or later.
Homebrew
From source
This repo is a TypeScript turborepo. Clone and build if you want to inspect the source, contribute, or run an unreleased .
The workspaces. packages/cli is the binary; the rest are libraries it consumes.
The CLI also depends on three sister packages published from their own repos (declared as runtime deps in packages/cli/package.json): hackmyagent, secretless-ai, and ai-trust. opena2a scan delegates to hackmyagent. opena2a secrets delegates to secretless-ai. opena2a trust queries via ai-trust.
what was installed
Every from 0.8.24 on has been published from GitHub Actions through npm Trusted Publishing, with SLSA v1 pro; earlier carry no attestation. The publishing workflow references no npm token; GitHub Actions exchanges its OIDC token with npm at publish time. The command below prints, without anything, the pro type and attestation URL the registry lists for the latest opena2a-cli (append @<> for another; an unattested prints nothing). npm audit signatures checks the registry's signatures and attestations for installed , not the installed files or who built them, and does not flag a without an attestation.
For local CLI integrity (post-install tamper), opena2a status reports the binary signature state. opena2a shield selfcheck runs the full self-attestation against the embedded manifest.
Identity files (~/.opena2a/aim-core/identity.json) are written mode 0600. OAuth tokens live in the OS keychain by default. ~/.opena2a/auth.json stores metadata only.
Which OpenA2A CLI do I want
There are four published CLIs in the toolchain. opena2a is the unified front door. Each underlying tool can also be installed and run standalone if that fits better.
| You want to... | Use | Standalone install |
|---|---|---|
| Run one command and get a security assessment of your project | opena2a init | (front door) |
| Scan a specific MCP server, skill, npm package, or GitHub repo | opena2a scan <target> or hackmyagent check <target> | npm install -g hackmyagent |
| Wrap any subprocess with credentials injected at runtime | opena2a secrets run --only KEY -- <cmd> or secretless-ai run --only KEY -- <cmd> | npm install -g secretless-ai |
| Check the trust posture of an npm or PyPI package before installing | opena2a trust <pkg> or ai-trust <pkg> | npm install -g ai-trust |
| Give your agent a cryptographic identity and local audit log, no server | opena2a identity create --name X | (bundled in opena2a-cli) |
| Benchmark a security tool against the OASB attack scenarios | opena2a benchmark | (uses OASB internally) |
If you're not sure where to start, run opena2a init in your project root. It tells you what's wrong and which underlying tool to invoke for the fix.
Built-in help
Commands
Three job categories: assess, protect, operate. Run any with --help for full flags.
Assess
| Command | What it does |
|---|---|
| opena2a init | Read-only security assessment with a trust score for your project. Start here. |
| opena2a review | Full security dashboard. 6-phase assessment, HTML report. First run downloads the NanoMind model files; --no-open skips the browser. |
| opena2a detect | Shadow AI discovery. Finds undeclared agents, MCP servers, AI configs. Returns a go score. |
| opena2a scan <target> | Static, semantic, and ad checks (current counts: hackmyagent --help). Targets: local repo, npm package, GitHub repo, MCP server, skill, or standalone SOUL.md. |
| opena2a check <target> | Pre-install trust check. Queries the OpenA2A Registry and runs HMA locally. |
| opena2a scan-soul <path> | Go controls across every ABGS domain, profile-aware. |
| opena2a trust <pkg> | Read-only Registry lookup for an npm or PyPI package. |
| opena2a benchmark | Run the OASB benchmark against your security tool. |
Protect
| Command | What it does |
|---|---|
| opena2a protect | Migrate hardcoded credentials to env-, masked previews, rollback manifest. Adds .gitignore patterns. Signs configs. |
| opena2a harden-soul | Generate a SOUL.md go file from your project state. |
| opena2a harden-skill <path> | Frontmatter , permission scoping, integrity pinning on a Claude or Cursor skill. |
| opena2a guard sign | Sign and watch config files (mcp.json, claude_desktop_config.json, etc.). Alerts on unauthorized changes. |
| opena2a shield init | One-shot 11-step setup: review, protect, identity, guard, secrets, runtime, policy, hooks. |
#### Optional AAP gate on protect
protect can be gated by the Agent Authorization Protocol. When --grant is set, the CLI presents an ATX and a grant reference to the local Secretless broker before any scan runs. The broker is the policy decision point; the CLI proceeds only if the broker authorizes.
Outcomes:
~/.secretless-ai/policies/. Per AAP §6.6 the denial is opaque; reasons live only in the broker's signed audit log.secretless broker start hint.--grant flag -> protect runs exactly as before; the gate is opt-in.This integration newly defends T-3002 (cross-tenant grant leakage), T-3003 (o credential scope), T-3006 (credential leaking into agent context), and T-8002 (audit attribution gap) at the CLI surface. The broker is the integrity-protected decision and audit point; the CLI carries no policy state.
Operate
| Command | What it does |
|---|---|
| opena2a identity create --name X | Generate an Ed25519 keypair locally. Writes ~/.opena2a/aim-core/identity.json. |
| opena2a identity integrate | Wire up cross-tool bridges so Secretless, HMA, ConfigGuard, Shield, and ARP events flow into one unified audit log. |
| opena2a identity audit [--limit N] | Read back the unified audit log. The query path for incident response. |
| opena2a identity trust | Local 8-factor posture score. |
| opena2a identity sign --data X | Sign arbitrary bytes with the agent's Ed25519 key. |
| opena2a runtime tail [-c N] | Tail the HMA ARP runtime event stream for the current project. |
| opena2a secrets ... | Credential management . add, list, run, revoke. |
| opena2a mcp ... | MCP ser: audit, sign, . |
| opena2a status | What's running, what's protected, what's missing. |
| opena2a login | OAuth 2.0 device flow against AIM Cloud or your self-hosted server. |
| opena2a whoami | Current auth status. |
| opena2a skill create <name> | Scaffold a new secure skill with signing and heartbeat. |
| opena2a train | Boot DVAA, the deliberately AI agent, for security training. |
Full command reference: opena2a.org/docs.
Post-incident review
Once opena2a identity integrate runs once, every event the OpenA2A toolchain captures auto-bridges into a single local audit log. No decorator in your agent code. No server. When something goes wrong:
The audit log lives at ~/.opena2a/aim-core/audit.jsonl. Append-only. Rotation at 50 MB, last 5 generations kept. Forward to Splunk or Sentinel via the standard tail-and-forward pattern.
Encryption at rest is filesystem-level. The JSONL stores unencrypted so grep and jq work without ceremony. For compliance use cases, encrypt ~/.opena2a/ with FileVault on macOS, LUKS on Linux, or BitLocker on Windows, or ship to a KMS-backed log aggregator.
Self-host or AIM Cloud
opena2a-cli works offline by default. The optional server path:
opena2a login and you're done.agent-identity-management. REST API, dashboard, Postgres-backed audit log, OAuth, 9-factor real-time trust scoring with NanoMind, 5-step Fine-Grained Authorization pipeline. Run bash quickstart.sh to bring it up.Local-only mode covers identity, audit, capability policies, and trust scoring. Server adds real-time enforcement, multi-machine fleet management, the dashboard, and MCP attestation. The CLI is the same in both modes. --server switches it.
Use cases
| Guide | Time |
|---|---|
| De using AI coding tools | 5 min |
| Security team assessing AI risk across a fleet | 10 min |
| MCP ser shipping safely | 15 min |
| CI/CD pipeline integration | 20 min |
Full index: docs/USE-CASES.md.
Contributing
Apache 2.0. PRs from outside the org welcome. CONTRIBUTING.md has the dev loop, the test con, and what to expect on a pull request opened from a fork.
Security issues: (coordinated disclosure, response within 24 hours).
Links
Part of the OpenA2A security platform.
License
Apache-2.0. See LICENSE.
项目信息
开发语言:TypeScript
Star 数:21
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕One scan for AI risk. `opena2a review` checks an AI project across credentials, shadow agents, MCP servers, and dependencies, returns a score, and routes each finding to the tool that fixes it. Open source.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | opena2a - One scan for AI risk. `opena2a review` checks an A |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:54:02 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 233 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |