 安全软件
点击放大
k8scan - An advanced, read-only Kubernetes security scanner
项目说明
<h1 align="center">k8scan</h1>
<p align="center">
<img src=" alt="Go ">
<img src=" alt="Kubernetes">
<img src=" alt="License">
<img src=" alt="">
</p>
<p align="center">
<b>Kubernetes Security Scanner</b>
</p>
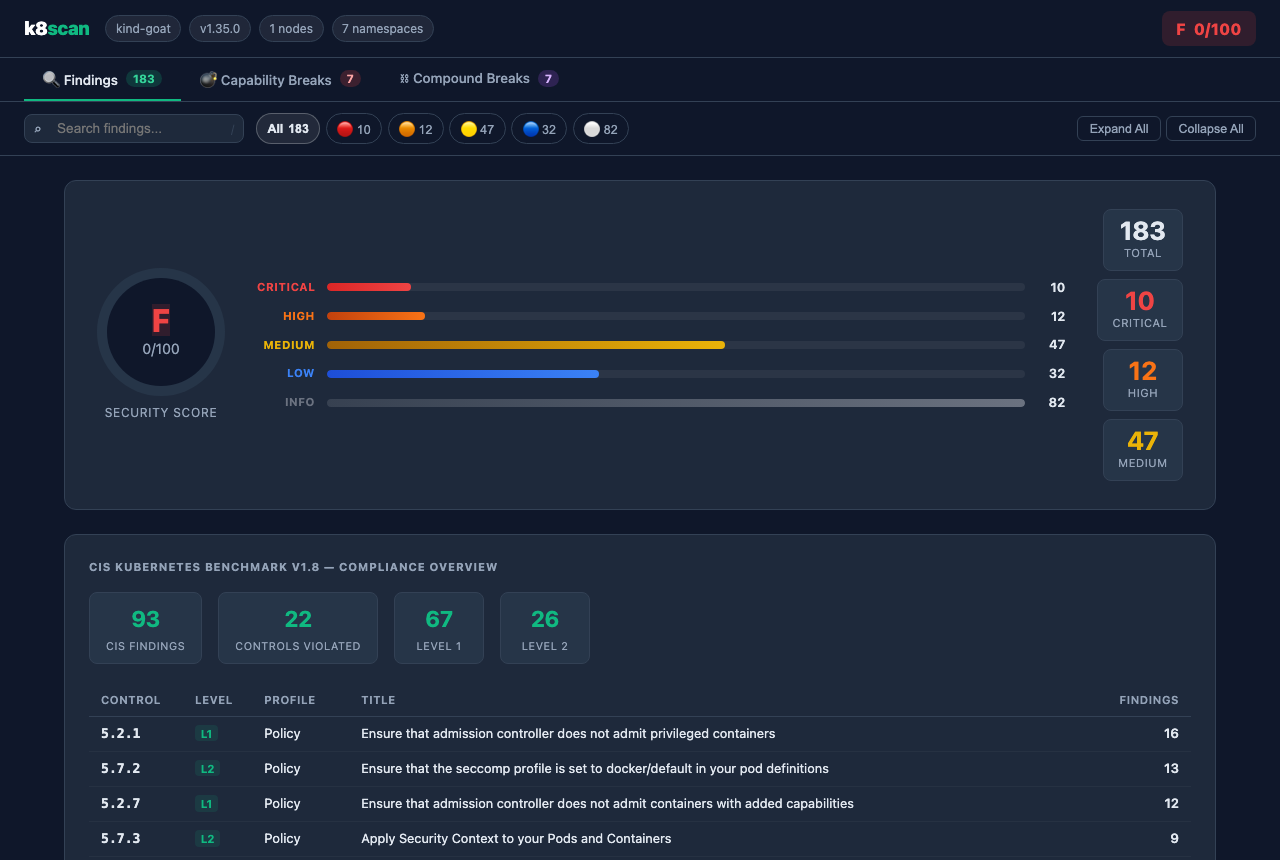
!HTML Report
<p align="center">
A fast, read-only Kubernetes security scanner written in Go. Detects misconfigurations, pri escalation paths, exposed secrets, and container escape — then correlates findings into <b>Capability Breaks</b> and <b>Compound Attack Paths</b> with Proof-of-Concept commands.
</p>
---
What it Finds
123+ checks across 8 categories:
| Category | Examples |
|---|---|
| Container Security | Pri pods, dangerous capabilities (SYS_ADMIN, BPF), hostPID/IPC/Network, sensiti mounts, writable root filesystem |
| RBAC | Wildcard permissions, pod/exec access, system:masters binding, cross-namespace SA grants, cluster-admin to non-system subjects |
| Secrets | Hardcoded AWS keys, GitHub tokens, private keys in env vars or ConfigMaps, empty passwords, expired TLS certificates |
| Network | Exposed NodePorts, missing NetworkPolicies, permissi/egress, cloud metadata API exposure, LoadBalancer without source ranges |
| Control Plane | Anonymous API ser, kubelet read-only port, etcd without auth/TLS, admission webhook failurePolicy: Ignore, audit logging disabled |
| Workload | Missing PodDisruptionBudget, no resource limits, Recreate update strategy, single replica, missing HPA |
| Image | Images not pinned to digest, potentially untrusted registries |
| Runtime Threats | Crypto miner detection, Docker-in-Docker, no runtime security monitoring |
---
Capability Break Analysis
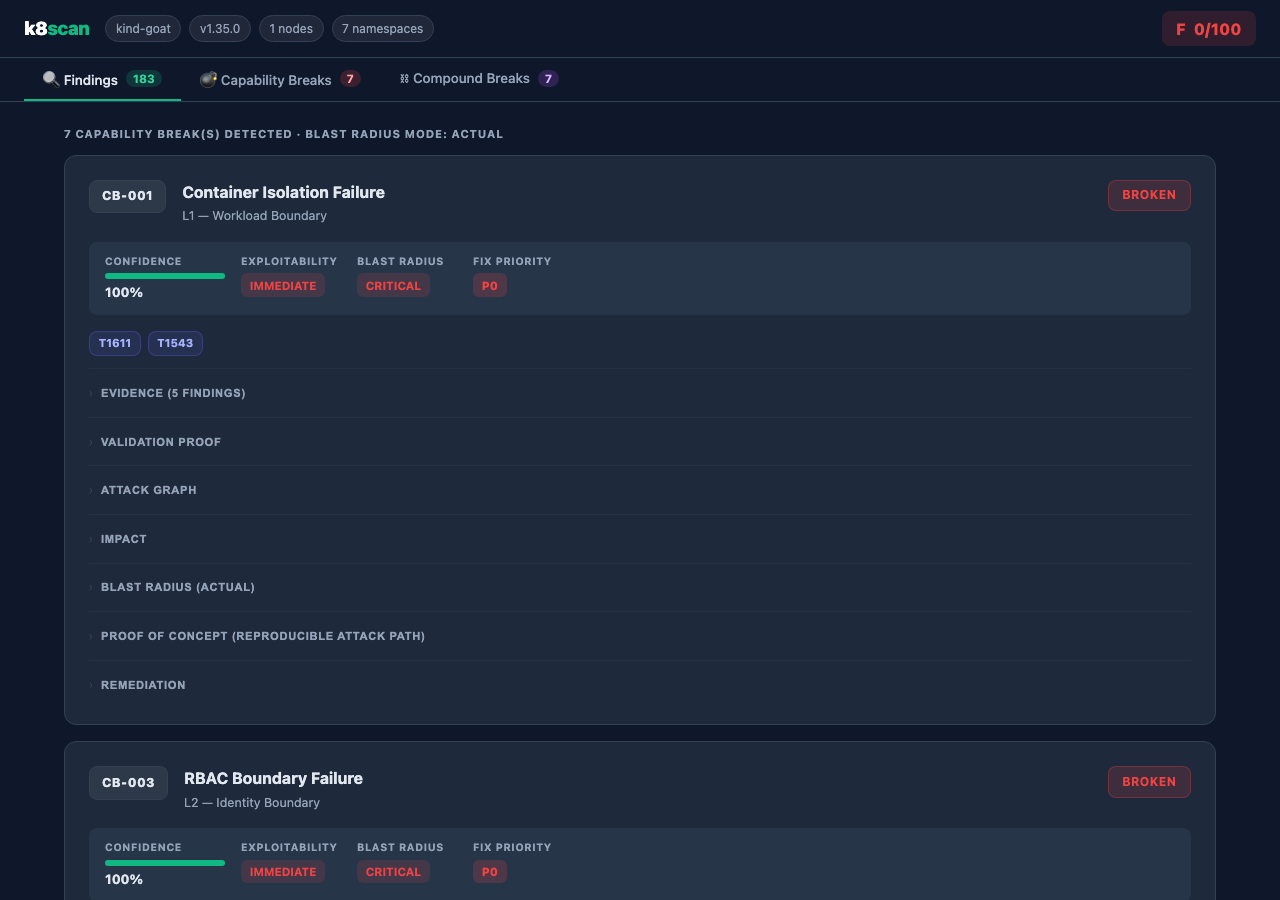
k8scan goes beyond indi findings. It correlates misconfigurations into Capability Breaks — structured proof that a named security boundary (container isolation, namespace isolation, RBAC boundary, etc.) is broken by the current cluster state.
!Capability Breaks
Each Capability Break includes a Proof — a deterministic table of signals showing exactly which findings prove the boundary is broken, their indi significance, and a combined explaining the full impact.
! Proof
Attack Graph
Each Capability Break and Compound Break renders an interacti graph showing the lateral mo path from initial access to the final target.
!Attack Graph
---
Compound Break Analysis
When two or more Capability Breaks chain together, k8scan surfaces a Compound Break — a complete multi-stage attack path with weighted confidence, blast radius, and MITRE ATT&CK mapping.
!Compound Breaks
---
Proof-of-Concept Commands
Every Capability Break ships a PoC — read-only kubectl commands that confirm the misconfiguration exists without modifying cluster state.
!Proof of Concept
---
Key Features
get, list, watch API calls; safe for productionk8scan lint scans YAML, Helm charts, and Kustomize o without a li--fail-on CRITICAL exits with code 2 when findings meet threshold; SARIF output integrates with GitHub Ad Security.k8scan-ignore.yaml to silence known-accepted findingsdeploy/k8scan-export.sh bundles cluster manifests + image list into a single zip for upload to k8scan.com---
Installation
Binary (Recommended)
> Requires Go 1.24+ and kubectl configured with cluster access.
Cross-Platform Release Builds
Docker
Or build locally:
The image is built on distroless/static-debian12:nonroot — no shell, no package manager.
In-Cluster (Job / CronJob)
This applies the provided Namespace, RBAC, one-off Job, and scheduled CronJob manifests. For GitOps workflows, create a Kustomize o that uses deploy/ as a base and patches the schedule, image, or RBAC resources without editing these tracked manifests.
You can also apply the raw YAML files indi:
---
Usage
---
Commands
k8scan scan
Scan a li cluster.
| Flag | Description | Default |
|---|---|---|
| --namespace, -n | Namespaces to scan (repeatable) | all |
| --category | Filter by category: container, rbac, secrets, network, control-plane, workload | all |
| --min-se | Minimum se: CRITICAL, HIGH, MEDIUM, LOW, INFO | INFO |
| --output-html | Write HTML report to file | — |
| --output-json | Write JSON report to file | — |
| --output-sarif | Write SARIF 2.1.0 report (GitHub Ad Security) | — |
| --output-md | Write Markdown report to file | — |
| --fail-on | Exit code 2 if findings at or abo exist | — |
| --group | Collapse identical findings — show count per title | false |
| --cis-report | Print CIS Benchmark compliance summary | false |
| --no-exploits | Skip PoC enrichment | false |
| --ignore-file | Suppression rules file | .k8scan-ignore.yaml |
| --parallel | Run scanners concurrently | true |
| --timeout | Scan timeout in seconds | 120 |
k8scan lint [paths...]
Statically analyse manifests without a li.
| Flag | Description |
|---|---|
| --helm <path> | Render a Helm chart with helm template before scanning |
| --helm-, -f | Additional Helm files (repeatable) |
| --kustomize <path> | Render with kubectl kustomize before scanning |
| --output-html/json/sarif/md | Same as scan |
| --fail-on | Same as scan |
k8scan categories
List all a scan categories with supported output formats.
k8scan
Print and build information.
---
Suppression Rules
Create .k8scan-ignore.yaml to silence accepted risks:
---
Cloud Scanning (k8scan.com)
If you prefer not to run the CLI locally, use k8scan-export.sh to bundle your cluster state and upload it to the k8scan cloud platform.
What gets exported:
images.txt — unique container image list for optional image correlationmeta.yaml — cluster context and export timestampWhat does NOT leave your cluster: secrets, persistent data, runtime state, logs.
> For en where data cannot leave the network, use the on-prem deployment instead.
---
CI/CD Integration
GitHub Actions
SARIF output is compatible with GitHub Ad Security, GitLab Security Dashboard, and any SARIF 2.1.0 consumer.
---
Contributing
1. Fork the repository
2. Create a feature branch (git checkout -b feature/new-check)
3. Add your check in internal/scanners/ and a corresponding PoC in internal/exploits/
4. Run go test ./... -race and go build ./...
5. Open a Pull Request
---
License
Licensed under the Elastic License 2.0. Source code is a for personal use, internal security auditing, and contributions. You may not provide k8scan as a hosted or managed service to third parties without a commercial agreement.
For commercial licensing inquiries:
Disclaimer
This tool is designed for detecting misconfigurations in Kubernetes en. The author is not responsible for any misuse. Always obtain proper authorization before scanning en you do not own or manage. The tool performs read-only API calls and does not modify cluster state.
---
<p align="center">
Built for security engineers by <a href="
</p>
项目信息
开发语言:Go
Star 数:20
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕An advanced, read-only Kubernetes security scanner for identifying misconfigurations and vulnerabilities.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | k8scan - An advanced, read-only Kubernetes security scanner |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:54:17 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 186 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |