 安全软件
点击放大
作者:admin
发布:2026-10-05
Hepheastus - Web Application Vulnerability Scanner
项目说明What Is Hepheastus?Hepheastus is a Multi-Web Application Scanner written in Perl, most of his scans are accurate!Incoming FeaturesWe are now scrip…
资源可下载
免费下载
0 条讨论
会员资源
开通会员后即可下载全部资源。
348浏览量
0讨论
2下载链接
可下载资源状态
内容可验证
更新 2026-10-05
人工审核发布
评论区答疑
项目说明
What Is Hepheastus?
Hepheastus is a Multi-Web Application Scanner written in Perl, most of his scans are accurate!
Incoming Features
We are now scripting a CMS(Content Manager System) detecter! We are also adding a Dork searcher :)
Important
we are currently working on it, if you have any bugs, issues or suggestions please report in the issues section in Github!
Any Perl Module Error?
<p>
In some cases Perl may say that you are missing an module if that happens run that:
cpan -i LWP::Simple && cpan -i Getopt::Long && cpan -i Term::ANSIColor
If cpan is missing search on google how to install CPAN in your fa distribution (Mine is Debian <3)
</p>
Functions
<p>
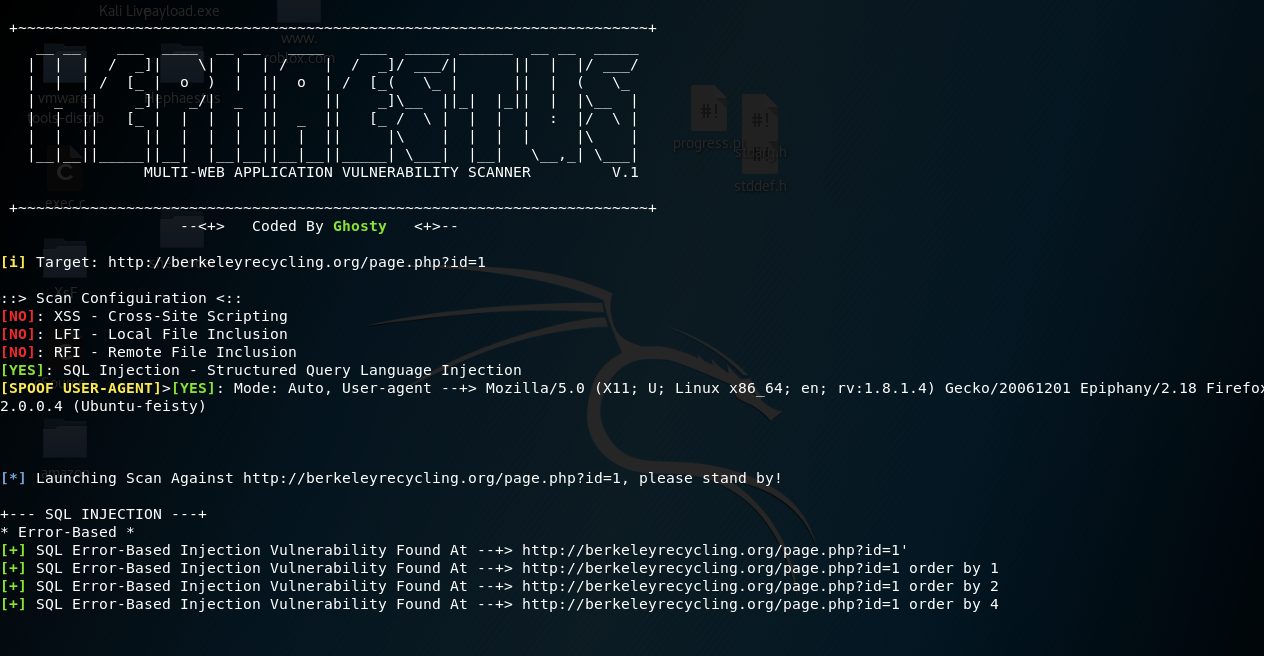
Hepheastus can scan for XSS, LFI, RFI and SQL , he can also spoof your user-agent to make your more anoymous.
Of course more the tool is supported and loved, more we will update it!
</p>
How to use?
<p>
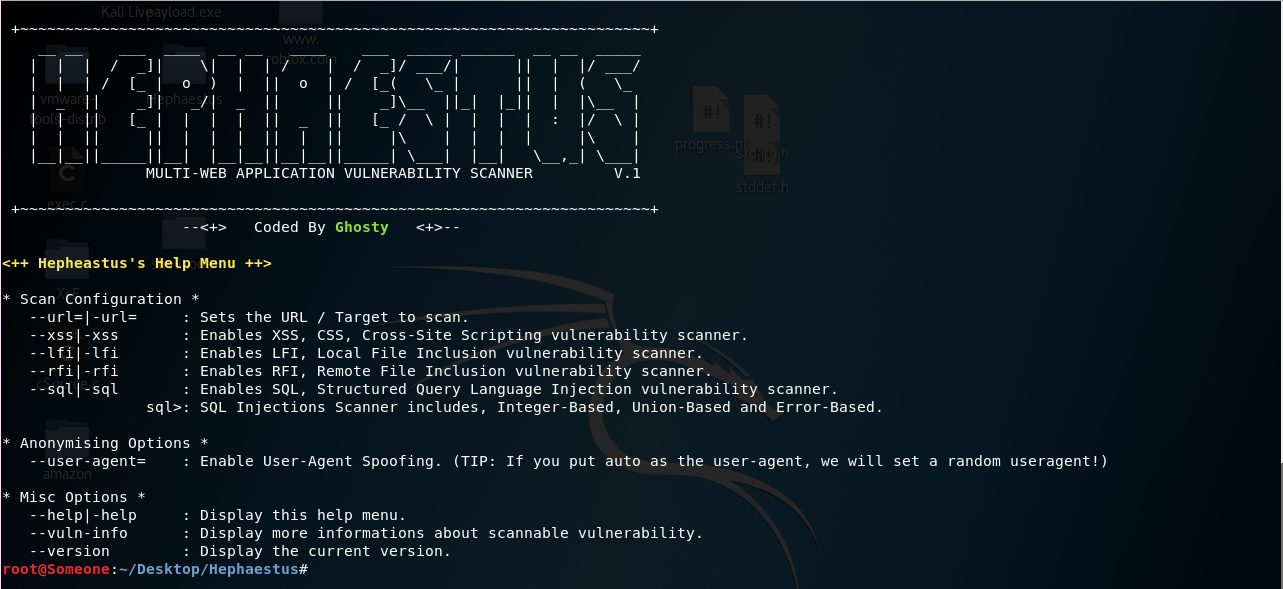
Simple run:
perl hepheastus.pl --help
This will display the help menu :)
</p>
Screenshots
!Examples
!Examples
!Examples
!Examples
项目信息
开发语言:Perl
Star 数:19
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Web Application Vulnerability Scanner展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Hepheastus - Web Application Vulnerability Scanner |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:54:50 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 348 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |
本资源免费,登录后即可在本页「下载链接」区域获取全部附件。
请在评论区留言说明具体链接,或联系作者补档。楼主更新后本页会同步最新的下载地址。
请先阅读正文中的授权说明;未注明的默认仅限站内学习交流,禁止直接搬运到其他站点二次售卖。
还没有讨论,快来抢沙发~
登录 后才能参与讨论