 安全软件
点击放大
apiscanner - APISCAN is a Swagger-driven API security tool for
项目说明
<meta content="sWEXZTEBbaynlEKCWRE" name="google-site-">
APISCAN OWASP 5.01 APIscanner by Perry Mertens
Author: Perry Mertens ()
Year: 2026 Perry Mertens
: 5.0.1 (Release)
License: GNU Affero General Public License v3.0 (AGPL-v3.0)
APISCAN is an API scanner that proactively identifies security risks by testing against the OWASP API Security Top 10 (2023).
It uses your OpenAPI/Swagger specification to generate realistic attack payloads and detect issues such as Broken Object Le (BOLA),
Broken Authentication, Excessive Data Exposure, and other critical API .
It understands OpenAPI/Swagger, supports multiple authentication flows, provides a plan/ workflow, includes a generic sanitizer/rewrites, and writes HTML artifacts.
APISCAN: AI-assisted API security for specialists.
APISCAN is not a scanner that guesses; it proves.
It tests. It observes. Then models explain the risk with e attached.
That’s how you make AI useful in security.
License
APISCAN is licensed under the AGPL-v3.0.
If you modify APISCAN and make it a as a hosted service, you must make the complete corresponding source code a under the same license.
What is APISCAN
APISCAN focuses on API-specific risks instead of generic web scanning.
It is built for testing APIs against the OWASP API Security Top 10 (2023), with one module per risk area and HTML reporting suitable for auditors and de.
What's New in v5.0.1
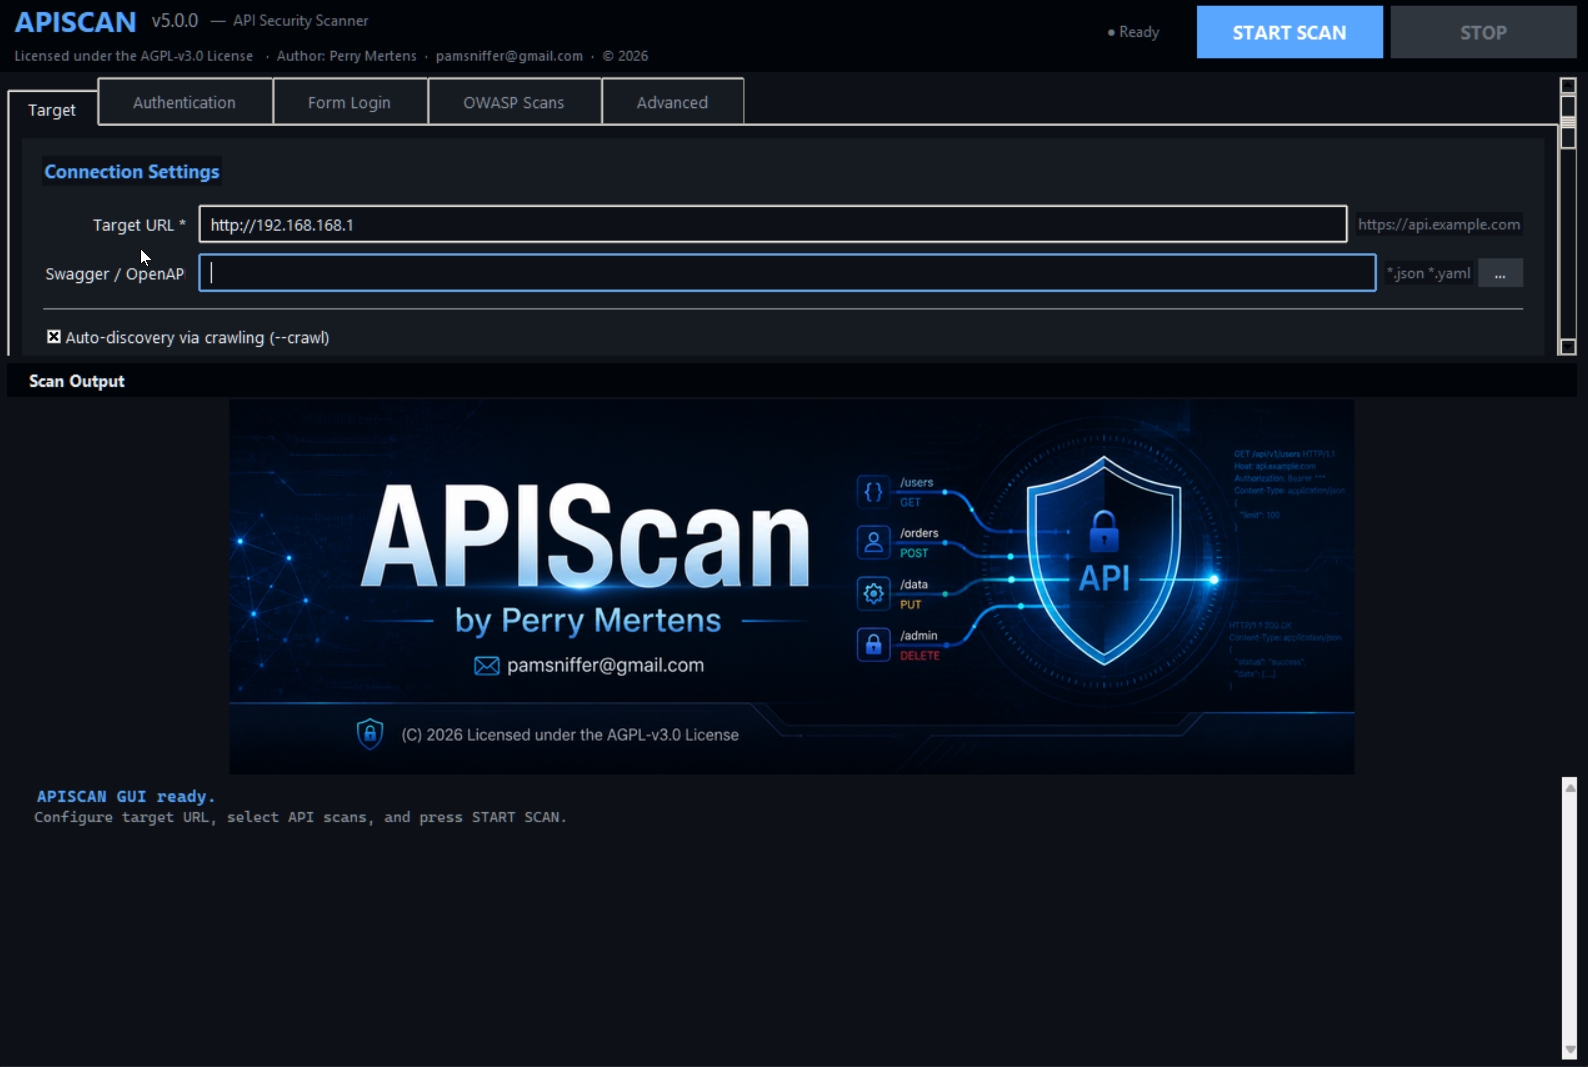
!APISCAN v5.0.1 GUI
--flow form --login-username ... --login-password ... or the GUI Auto-Detect button.--crawl- (on), --no-crawl-, --crawl- balanced|strict, --crawl- N. From 71→4 endpoints on Juice Shop.APISCAN_DEEP_SCAN=1 auto-switches to full payloads, high intensity, no quick mode. All injection types including SSTI, LDAP, XXE, RCE with injection_payloads.json.python apiscan_gui.py) with Target, Authentication, Form Login (Auto-Detect), and Ad tabs. Crawl controls built in.--chain-mode with optional --chain-depth 1-3 for recursi escalation chains. Generates api_chain_escalation_report.html.Install
Setup and en
Before running APISCAN, configure your en and optional AI tooling.
En setup
LLM / AI pro (optional)
Quick start
Quick mode and full scan
API10 (Unsafe Consumption of APIs) runs in quick mode by default. This keeps normal scans fast by limiting Phase 2 to the most promising endpoints and capping quick SQL testing.
Defaults:
APISCAN_API10_QUICK=1APISCAN_API10_QUICK_MAX_ENDPOINTS=30APISCAN_API10_QUICK_SQL_MAX_TESTS=10APISCAN_API10_QUICK_DIRTRA=8APISCAN_API10_QUICK_HPP_MAX_PARAMS=3APISCAN_API10_QUICK_REDIRECT_MAX_TESTS=6APISCAN_RATE_LIMIT=0| Mode | Endpoints | Tests/endpoint | Totaal | Tijd |
|---|---|---|---|---|
| Quick (default) | 30 | ~15 | ~450 | ~3-5 min |
| Deep scan | 15 | ~26 | ~390 | ~25-35 min |
> Deep scan: APISCAN_DEEP_SCAN=1 + optioneel APISCAN_DEEP_MAX_ENDPOINTS=15 (default).
PowerShell:
Bash/Linux/macOS:
Usage examples
Bearer token
API key
OAuth2 Client Credentials
Proxy / Burp
Plan-only
Ad usage
Extra headers
IDs file
Sanitizer and rewrites
AI-assisted analysis
Output and reports
results.db apiscan_*.logNotes
--plan-only to avoid accidental traffic.Links
---
© 2026 Perry Mertens . Released under the AGPL-v3.0 License.
---
项目信息
开发语言:Python
Star 数:17
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕APISCAN is a Swagger-driven API security tool for security specialists and auditors, focused on OWASP API Top 10 coverage and evidence-based reporting.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | apiscanner - APISCAN is a Swagger-driven API security tool for |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:56:03 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 132 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |