 安全软件
点击放大
getobserver - Finds what's wrong — and shows you the fix. Code,
项目说明
Observer
Finds what's wrong — and shows you the fix.
*Code, dependencies, config, and infra — one scan, one report. Offline, single binary, no account.*
!License: MIT
!Go
!Platforms
!Single binary
⬇️ Get Observer
Grab the single binary for your OS — no runtime, no dependencies, no account:
| Windows | macOS (Apple Silicon) | macOS (Intel) | Linux |
|:---:|:---:|:---:|:---:|
| Download | Download | Download | Download |
<sub>Prefer a package manager? Scoop · Homebrew · go install — see Installation. On macOS/Linux: chmod +x observer_*.</sub>
Then point it at any project:
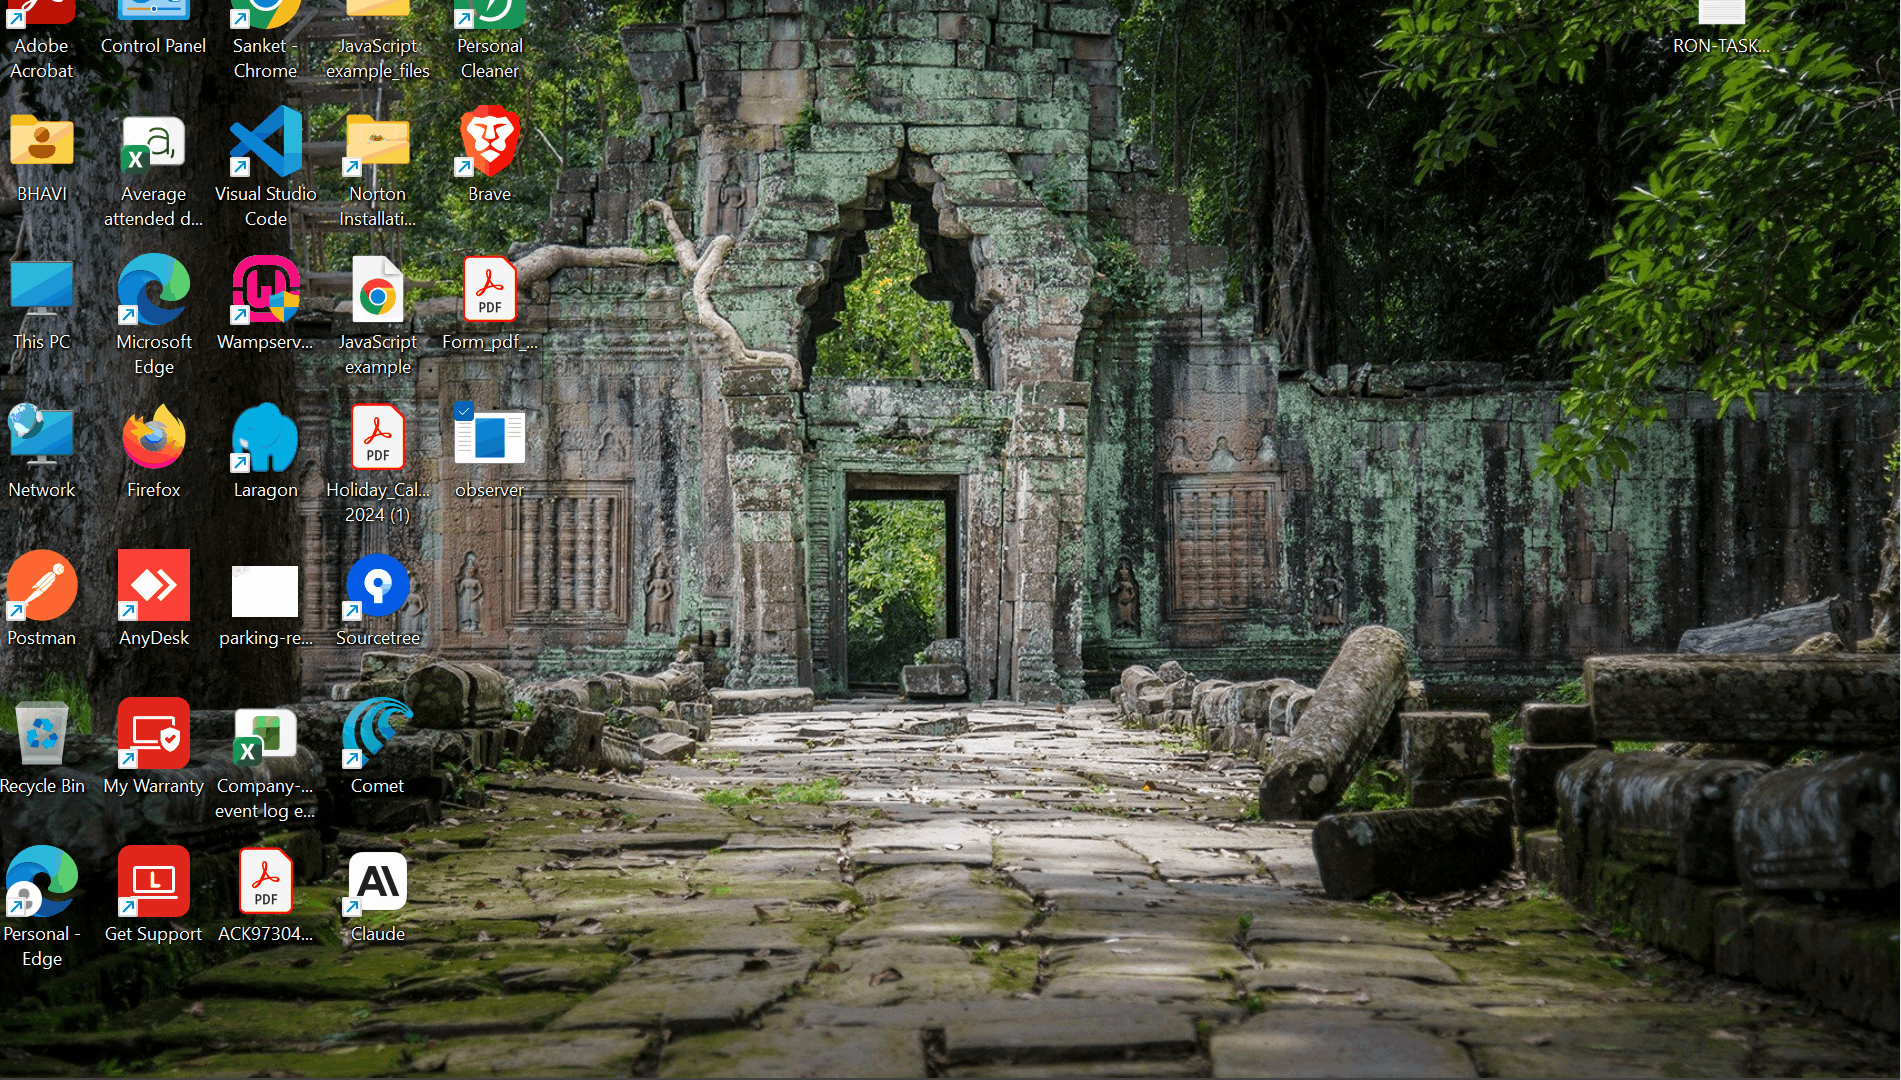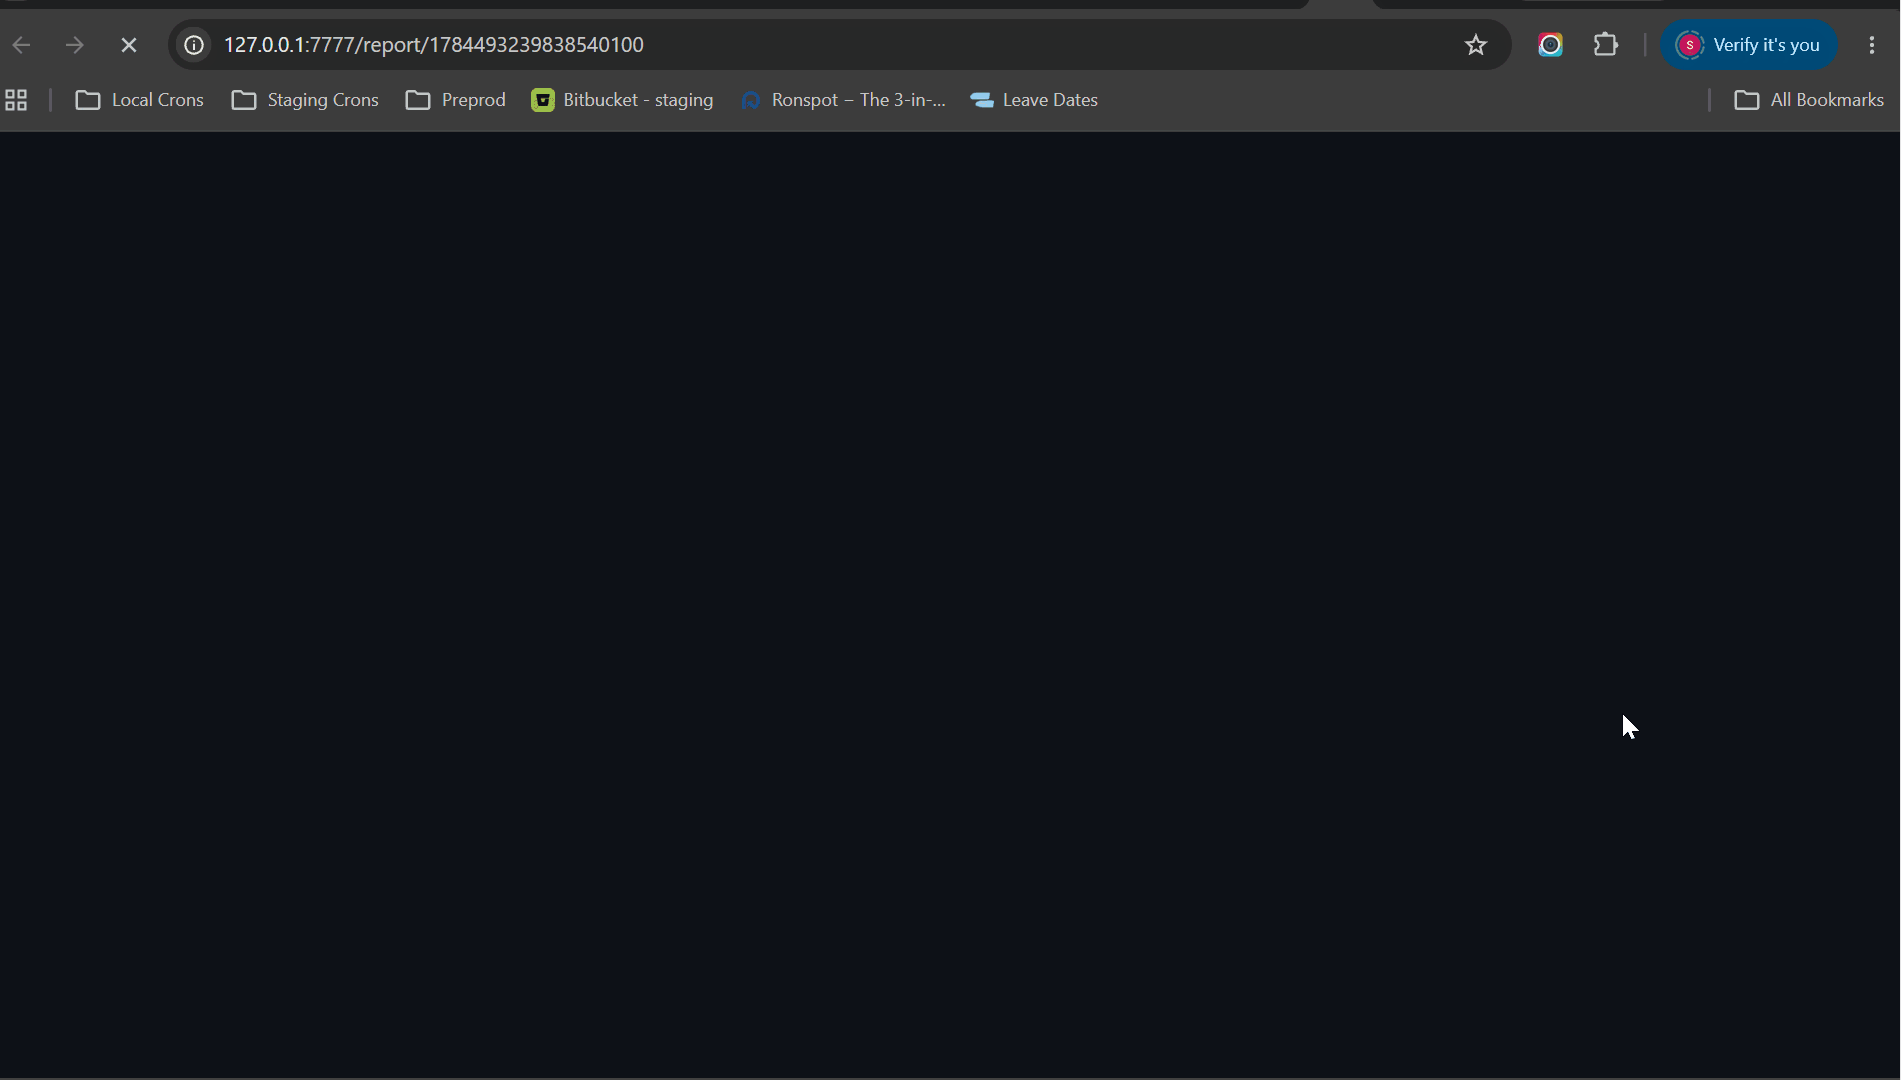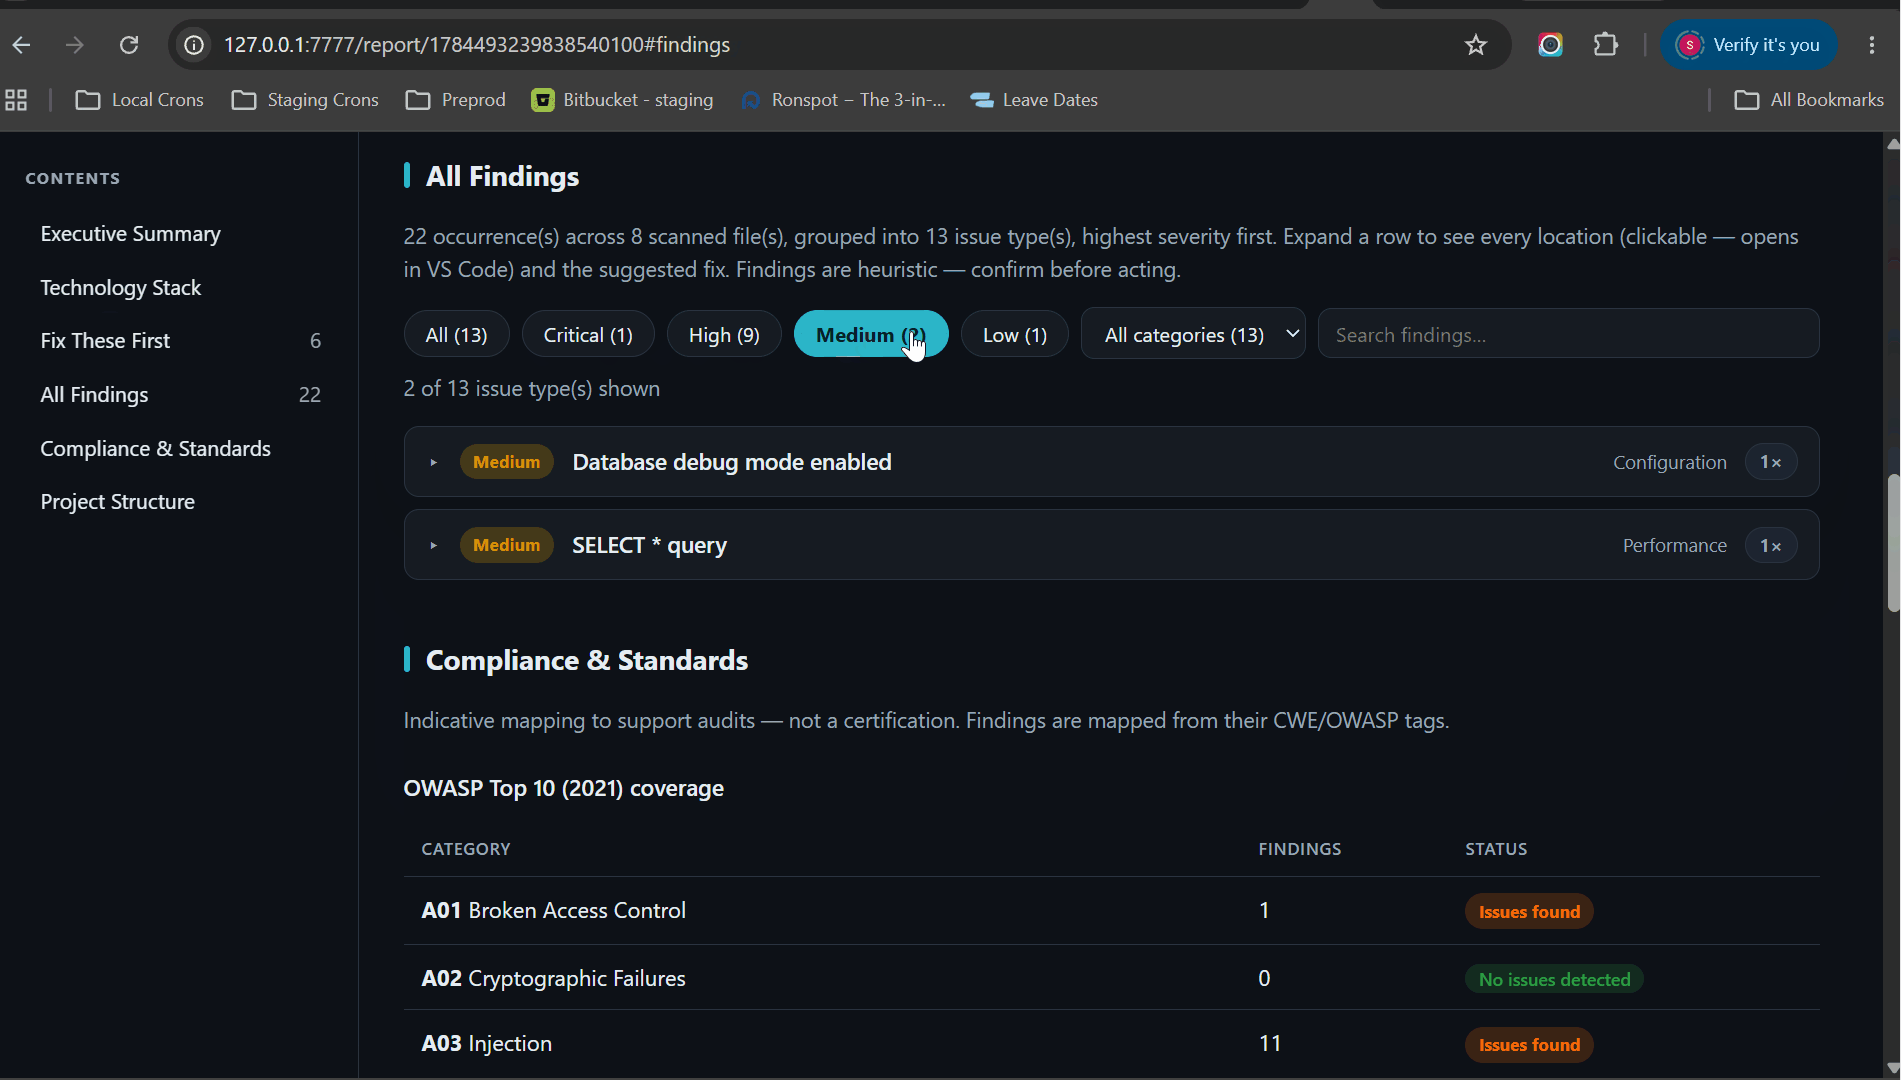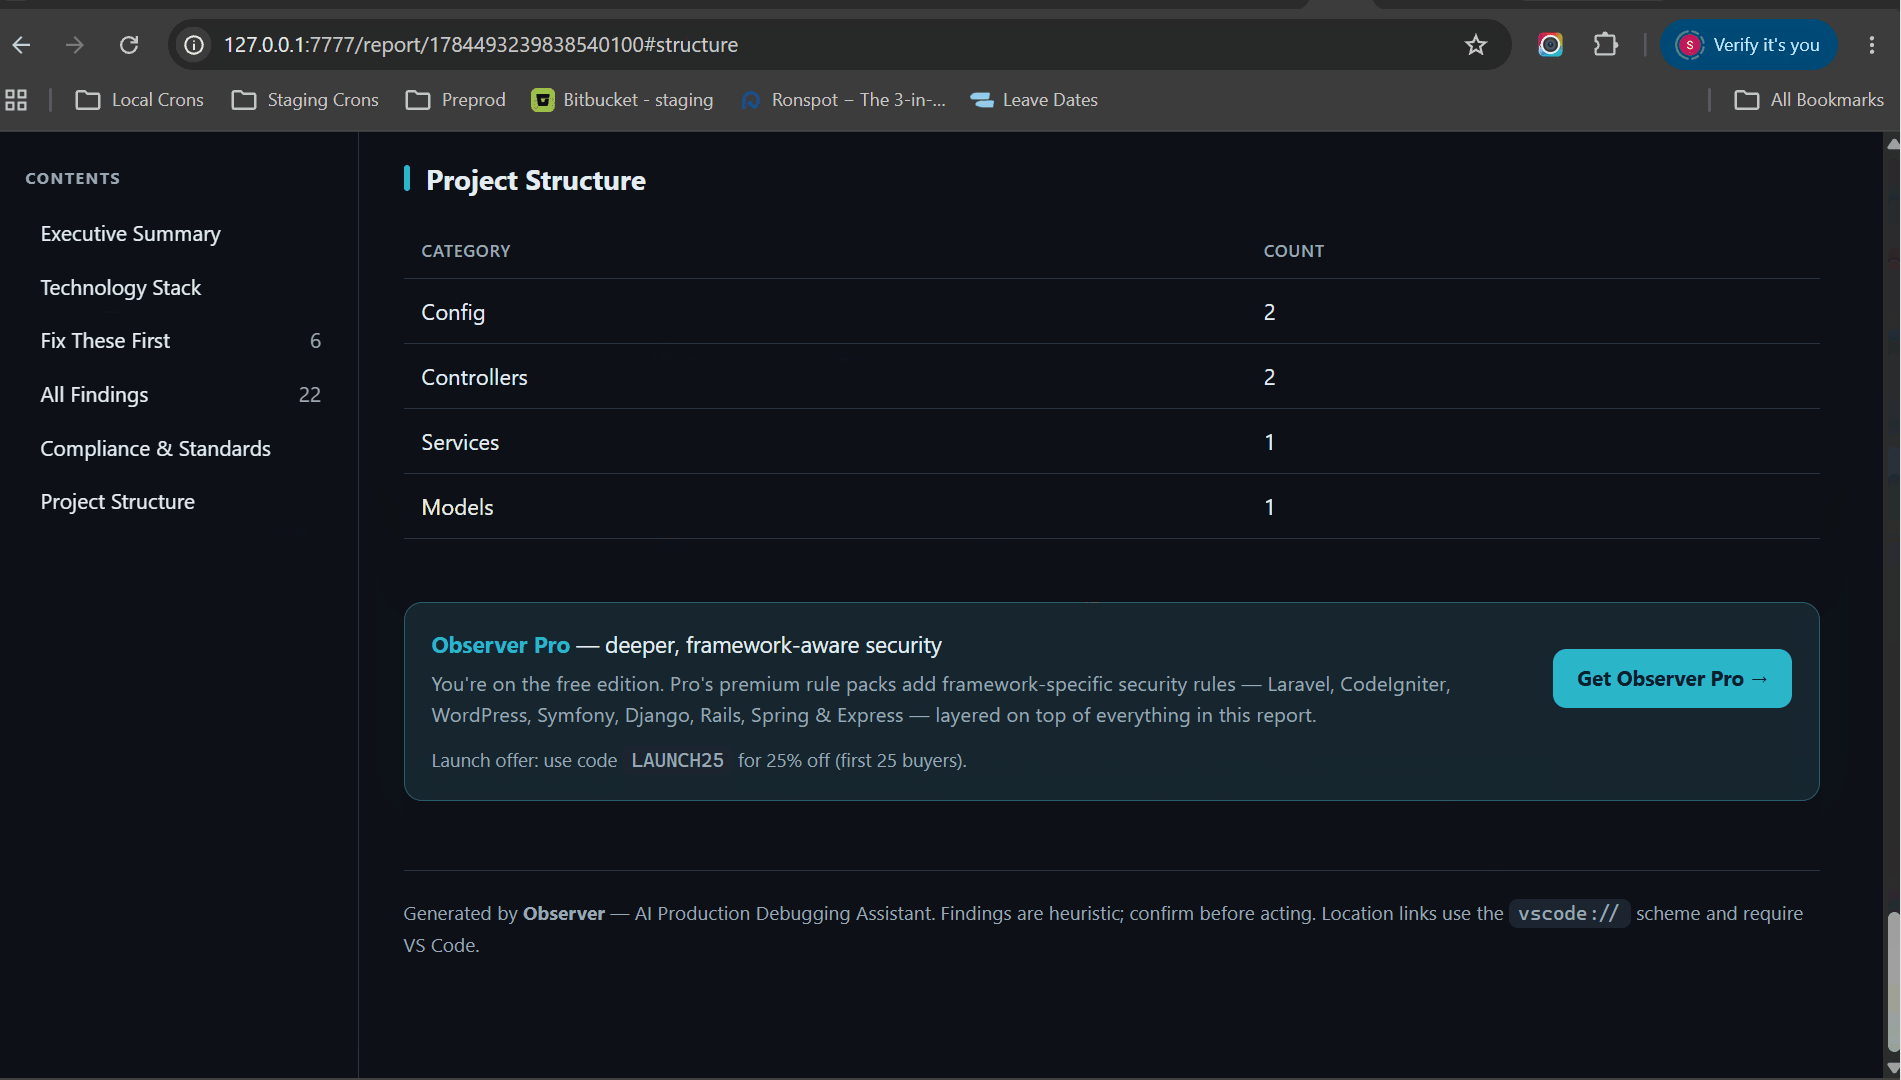
You get one self-contained report.html — grouped findings, a standards-aligned Security Rating (A–E), and a suggested fix for every issue. Fully offline; open it in a browser or print to PDF.
---
> A de tool that analyzes an application/codebase and generates a
> production health report - combining static analysis, technology detection,
> runtime error analysis, log analysis, dependency analysis, infrastructure and
> config checks (Dockerfile / compose / Kubernetes / .en), and
> optional AI-powered explanations.
The goal: help de quickly identify production issues without manually
searching through huge codebases and server logs.
The CLI binary is named observer.
> Status: The local CLI, technology detection, static analysis, runtime and
> log analysis, HTML reporting, packaging, dashboard, opt-in dependency CVEs, and
> CI workflow are implemented. Observer Pro adds local reporting and repeat-audit
> workflow features; no hosted service is required.
---
Demo
!Obser a project and opening the production-health report
Point it at any codebase and get one self-contained HTML report - no server, no
account, no instrumentation:
Obser the stack, flags security, runtime, and dependency issues with
se and suggested fixes, scores the project on Security and **Code
Health**, and writes a shareable report.html you can open or print to PDF.
Obser is free and MIT licensed and produces detailed HTML, JSON, CSV, and SARIF outputs. Observer Pro adds an organization-ready PDF with document control, grouped remediation planning, bookmarks, hyperlinks, optional client branding, and repeat-audit workflow features without a hosted dependency.
---
How Obser
Observer is a local audit snapshot, not a replacement for a full semantic SAST
platform or production monitoring service. It combines lightweight built-in
heuristics with optional local tools and produces one report without requiring
an account.
| | Observer | Full SAST platforms | Cloud security tools | Production monitoring |
|---|---|---|---|---|
| Primary job | Private audit snapshot and hando | Deep continuous code analysis | Hosted code/dependency analysis | Li and telemetry |
| Setup | One local binary | Local, self-hosted, or cloud setup | Account and cloud workflow | Application instrumentation |
| Analysis depth | Curated heuristics; optional local engines | Deeper language and data-flow analysis | by | Runtime rather than source audit |
| Offline use | Default; enforce with --assert-offline | A in some products/editions | Usually cloud-dependent | Usually cloud-dependent |
| Best fit | Client audits, legacy reviews, handovers, air-gapped work | Large continuous engineering programs | Managed security programs | Operating li |
Use Observer when privacy, fast setup, and a readable point-in-time report matter.
Use a deeper SAST platform when you need broad semantic analysis, centralized
policy management, or large-team go. The tools can complement each
other.
---
Gate AI-generated code
AI writes a lot of code now — and it ships the exact issues Obser catches
(hardcoded secrets, injection, weak crypto, risky deps) at a higher rate than hand-written
code. Observer is an offline safety net for those changes: instead of re-scanning the
whole project, scan only what changed.
Add --attest attestation.json to emit a machine-readable local scan record for
a PR or audit trail. It records the tool , scope, finding counts, and gate
outcome. Observer Pro can add an HMAC companion file for local workflow integrity;
this is not a third-party signature or certification.
---
Privacy & air-gapped use
Observer runs fully offline by default — nothing about your code e your
machine. There is no account, no telemetry, and no phone-home. The only features that
touch the network are explicitly opt-in: --cve (OSV.de lookup), --semgrep when using auto or registry rules, and --ai
*with* an OPENAI_API_KEY, and the --email / --slack / --teams / --webhook
notifiers. Leave them off and the scan is entirely local.
For regulated, air-gapped, or client-confidential work you can make that guarantee
enforceable:
--assert-offline refuses network-capable options, requires SEMGREP_CONFIG to point to an existing local file or directory when --semgrep is used, and unsetsOPENAI_API_KEY so the AI layer stays on its local heuristic.
Inspect the privacy contract and a optional local engines without scanning:
During an enforced scan, ObserOffline mode: no network I/O. so the enforced mode is in an audit log. Ideal for finance,
healthcare, go/defense, or auditing a client's code under NDA — the code stays
put.
---
Architecture
The product is built around a single Diagnostic Core Engine that every
interface (CLI today; API and an enterprise agent later) reuses.
Repository layout
---
Installation
Download a prebuilt binary (recommended)
Obser as a single self-contained executable — no runtime, no
dependencies, nothing installed on your system. Download the binary for your OS
from the Releases page and run it:
| OS | File |
|---|---|
| Windows | obser.exe |
| macOS (Apple Silicon) | obser |
| macOS (Intel) | obser |
| Linux | obser / obser |
On macOS/Linux, make it executable: chmod +x observer_* (optionally rename to observer).
Binaries are currently unsigned — your download against SHA256SUMS.txt on the
release. (Signed/notarized builds are on the roadmap.)
Install via a package manager
Windows — Scoop:
macOS / Linux — Homebrew:
Both install the observer command onto your PATH and the download's SHA-256.
Build from source
Requires Go 1.26+.
On Windows the output is observer.exe. To cross-compile release binaries for all
platforms: pwsh scripts/build-release.ps1 (or ./scripts/build-release.sh).
---
Usage
Email configuration (Phase 8)
--email attaches the HTML report and sends a summary via SMTP. Configure with env vars:
| | Purpose | Default |
|---|---|---|
| SMTP_HOST | SMTP server host | _(required to send)_ |
| SMTP_PORT | Port (587 STARTTLS, 465 implicit TLS, 25) | 587 |
| SMTP_USER / SMTP_PASS | Credentials (omit for an open relay) | _(none)_ |
| SMTP_FROM | From address | SMTP_USER |
| OBSER | Set to 1 to compose a .eml file instead of sending (no ser) | _(off)_ |
AI configuration
The --ai flag explains findings. It is pro and works offline:
OPENAI_API_KEY set → uses OpenAI; falls back to local on any error.| | Purpose | Default |
|---|---|---|
| OPENAI_API_KEY | Enable the OpenAI provider | _(unset → local mode)_ |
| OPENAI_MODEL | Model id | gpt-4o-mini |
| OPENAI_BASE_URL | O API endpoint (for proxies/testing) | OpenAI |
| OBSER | Set to local to force offline mode even with a key | _(auto)_ |
Scan timeout
Deep scans (PHPStan + Semgrep o of files) run under a single time budget.
Raise or lower it with OBSER — a Go duration string like 15m or 30m:
| | Purpose | Default |
|---|---|---|
| OBSER | Max time for a deep scan before it is stopped (the engine process tree is killed on timeout, so no orphaned processes) | 15m (hard cap 60m) |
Example output
It also writes a self-contained report.html with the technology o,
detected signals, code structure, and file-type breakdown.
---
Roadmap
| Phase | Scope | Status |
|------:|-------|--------|
| 1 | Core CLI — scan a project, emit HTML report | ✅ Done |
| 2 | Technology detection (framework / DB / infra) | ✅ Done |
| 3 | Static code analysis (security & perf issues) | ✅ Done |
| 4 | Runtime error collection (obser) | ✅ Done |
| 5 | Log analyzer (obser) | ✅ Done |
| 6 | AI analysis module (OpenAI + pluggable pro) | ✅ Done |
| 7 | Professional multi-section HTML report | ✅ Done |
| 8 | Email reporting (SMTP) | ✅ Done |
| 9 | Packaging & distribution — cross-platform single-binary builds | ✅ Done |
| 10 | GitHub quality (README, badges, download/build, contributing) | ✅ Done |
| 11 | obser — local web dashboard (multi-project, history, deltas) | ✅ Done |
| 12 | Dependency C (OSV.dev — PHP/npm/PyPI/Go) | ✅ Done |
| 12+ | Optional engine wrappers — Semgrep / PHPStan / Bandit / gosec / ESLint ✅ (auto-detected) | ✅ Done |
| 13 | CI & team workflow (SARIF, quality gate, baseline, GitHub workflow) | ✅ Done |
| 14 | Changed-code scanning — --diff gate + attestation + pre-commit hook (AI-code safety net) | ✅ Done |
| 15 | Deeper local analyzers and additional runtime agents | Planned |
For the product , editions, and positioning see PRODUCT.md.
---
Observer Pro
The CLI and local dashboard are free forever. Observer Pro adds optional paid
features — one-time purchase, activated with a license key, fully offline after acti:
Or get e in the All-Access bundle — $89.
Activate with observer pro activate <key>.
> 🎉 Launch offer — 25% off with code LAUNCH25 at checkout (one-time, first 25 buyers).
> No pressure: run the free tool first, and if it earns a spot in your workflow, the discount's here when you want it.
---
Contributing
See CONTRIBUTING.md. Issues and PRs welcome.
License
MIT
项目信息
开发语言:Go
Star 数:15
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Finds what's wrong — and shows you the fix. Code, deps, config & infra — one offline scan, one report.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | getobserver - Finds what's wrong — and shows you the fix. Code, |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:57:38 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 227 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |