 安全软件
点击放大
VulnerAppDLH - VulnerAppDLH is a vulnerable Android application s
项目说明
Droid-LLM-Hunter
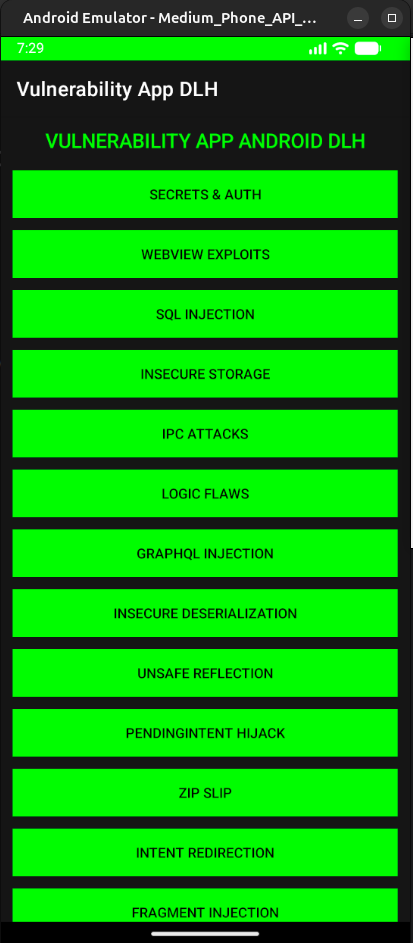
is a deliberately insecure Android application designed as a training ground and testbed for the Droid-LLM-Hunter security analysis tool. It implements a wide range of common Android based on the OWASP Mobile Top 10 and MASVS standards, serving as a perfect target to demonstrate DLH's detection capabilities.
> v2.0.0 — Testbed Expansion. This release adds 8 new classes (Insecure Deserialization, Unsafe Reflection, PendingIntent Hijacking, Zip Slip, Intent Redirection, Fragment Injection, StrandHogg, Hardcoded Secrets in XML), bringing the app to 15 isolated modules. It is against Droid-LLM-Hunter's semantic golden test at 25/25 recall.
📚 Documentation &
This repository includes detailed reports generated by Droid-LLM-Hunter:
* 🛡️ GENERATE_EXPLOIT.md: Contains the full list of , mapping to report folders, and executed exploit scripts (Python/Shell/HTML/JS).
* 📘 .md: A technical encyclopedia of all rules supported by DLH, including technical impact, detection logic, and the ground-truth map (rule → file) used by the golden test.
<di="center">
<p>
<img src=" alt=" 2.0.0">
<img src=" alt="Android Kotlin">
<img src=" alt="">
<img src=" alt="Tool">
</p>
</div>
<p align="center">
<img src=".png" width="350">
</p>
---
📋 Table of Contents
---
💀 Implemented
contains the following intentional security flaws, each isolated in its own Activity for clear demonstration. Modules 1–7 are the original set; modules 8–15 were added in v2.0.0.
1. Hardcoded Secrets & Insecure Storage
* Component:
SecretsActivity* :
* Hardcoded AWS Access Keys and API Tokens in source code.
* Storing sensitive user credentials (plaintext) in
SharedPreferences.* Logging sensiti to
Logcat.* MASVS: MAS, MAS
2. SQL Injection
* Component:
SQLInjectionActivity* :
* Constructs SQL queries using raw string concatenation with user input.
* Allows attackers to manipulate database queries (e.g.,
' OR '1'='1).* MASVS: MAS
3. WebView Exploits
* Component:
Web* :
* Cross-Site Scripting (XSS): Ja enabled (
setJa(true)).* Local File Access: Access to file system allowed (
setAllowUni(true)).* Ja: Exposes sensiti methods (
getSecrets) to web content — a hardcoded token bridged to Ja.* Deep Link: to loading malicious URLs via
dlh://webview.* MASVS: MAS, MAS
4. GraphQL Injection
* Component:
GraphQLInjectionActivity* :
* Constructs GraphQL queries by concatenating user strings directly into the query body.
* Susceptible to query injection/mutation attacks.
* MASVS: MAS
5. Insecure File Operations
* Component:
InsecureFileActivity* :
* World-Readable Files: Creates files with
MODE_WORLD_READABLE / setReadable(true, false) (deprecated but dangerous).* Path Tra: allows reading arbitrary files user input filenames.
* MASVS: MAS, MAS
6. Weak Cryptography & Auth Bypass
* Component:
CryptoActivity* :
* Weak Randomness: Uses
java.util.Random for Session Tokens (predictable).* Auth Bypass: Simulates biometric authentication that sets a simple boolean flag in memory (client-side trust — a logic flaw).
* MASVS: MAS, MAS
7. IPC & Exported Components
* Component:
UnprotectedExportedActivity, SpoofableReceiver* :
* Deep Link Hijacking:
://* accepts any host, prone to intent interception.* Intent Spoofing: Exported Broadcast Recei actions from any app without permission checks.
* MASVS: MAS
8. Insecure Deserialization 🆕
* Component:
DeserializationActivity* :
* Deserializes attacker-supplied bytes from an Intent extra via
ObjectInputStream.readObject() with no ObjectInputFilter/allowlist — object injection / gadget-chain RCE.* MASVS: MAS
9. Unsafe Reflection 🆕
* Component:
ReflectionActivity* :
* Instantiates an arbitrary class named by an untrusted Intent extra via
Class.forName(...).newInstance().* MASVS: MAS
10. PendingIntent Hijacking 🆕
* Component:
PendingIntentActivity* :
* Creates a mutable
PendingIntent (FLAG_MUTABLE) wrapping an implicit Intent — a receiving app can redirect it and act with this app's identity.* MASVS: MAS
11. Zip Slip 🆕
* Component:
ZipSlipActivity* :
* Extracts archi with
new File(targetDir, entry.getName()) and no canonical-path check — a ../ entry name o arbitrary files.* MASVS: MAS
12. Intent Redirection 🆕
* Component:
IntentRedirectionActivity* :
* Forwards a nested, attacker-supplied Intent (
getParcelableExtra) via startActivity() without — a confused-deputy path to this app's non-exported components.* MASVS: MAS
* Note: This module drove a new detection rule (
intent_redirection) in Droid-LLM-Hunter.13. Fragment Injection 🆕
* Component:
FragmentInjectionActivity* :
* An exported
PreferenceActivity whose is() returns true for any name — an attacker loads arbitrary fragments via :android:show_fragment.* MASVS: MAS
14. StrandHogg (Task Hijacking) 🆕
* Component:
HijackTargetActivity (declared in AndroidManifest.xml)* :
* Exported activity with a custom
android:taskAffinity + android:launchMode="singleTask" — a malicious app sharing the affinity can hijack the task and o/phish the user.* MASVS: MAS
15. Hardcoded Secrets in Resources 🆕
* Component:
res//strings.xml* :
* Sensitive keys embedded in resources (
google_api_key, aws_secret_access_key, stripe_secret_key) — tri extractable from resources.arsc.* MASVS: MAS
---
🛠️ Build & Installation
You need a JDK 17 and Gradle 8.x (or Android Studio). The project uses the Android Gradle Plugin 8.2 (compileSdk 34), which requires JDK 17.
1. Build the APK
Use the Gradle wrapper to build the debug APK:
> If your machine has no local.properties, point Gradle at your Android SDK:
> echo "sdk.dir=$HOME/Android/Sdk" > local.properties
2. Locate the APK
The output APK will be located at:
app/build/outputs/apk/debug/app-debug.apk3. Install on Device/Emulator
---
🚀 Scanning with Droid-LLM-Hunter
To analyze this app using Droid-LLM-Hunter (DLH) and the :
1. Preparation
Copy the built APK into the root of
droid-llm-hunter (the golden test expects .apk), then enable the rules you want in config/settings.yaml.2. Run the Scan
3. View Results
DLH writes a JSON report to the
output/ directory. Modules exercised by this app map to rules such as:*
hardcoded_secrets, hardcoded_secrets_xml, insecure_storage*
sql_injection, graphql_injection, path_tra, zip_slip*
web, insecure_webview, web, web*
insecure_random_number_generation, biometric_bypass, uni*
exported_components, intent_spoofing, deeplink_hijack, strandhogg*
insecure_deserialization, unsafe_reflection, pending_intent_hijacking, fragment_injection, intent_redirection> Golden test: DLH's opt-in semantic test (pytest -m llm) scans this APK and asserts a 25/25 recall contract against the ground-truth map in .md.
---
🗺️ De Roadmap
Completed in v2.0.0
* ✅ 8 new modules (see modules 8–15 above), including the new
intent_redirection class co-de with DLH.Future Updates
* Dynamic Rule Updates: This application is updated with new scenarios as new detection rules are added to Droid-LLM-Hunter (DLH).
Deferred / High-Risk Features
* Jetpack Compose Security (
jetpack_compose_security) 🔴* Status: Deferred to a separate, dedicated Compose app.
* Reasoning: This project deliberately stays on the standard XML ("Legacy View") system so the framework matches the original testbed. Adding Compose would require enabling
compose true and pulling hea UI / Material3 / compiler dependencies into build.gradle, which is out of scope for this app.---
📝 Technical Details
* : 2.0.0 ( 2)
* Package Name: com.dlh.
* Min SDK: 24
* Target / Compile SDK: 34
* Language: Kotlin
* UI: Standard XML Views + programmatic layouts (no Jetpack Compose)
> Disclaimer: This application is INTENTIONALLY . Do not install it on a production device containing sensitive data. Do not use portions of this code in real applications.
项目信息
开发语言:Python
Star 数:14
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕VulnerAppDLH is a vulnerable Android application specifically created to test Droid-LLM-Hunter. It serves as a comprehensive testbed for validating the scanner's detection capabilities across various vulnerability categories. 展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | VulnerAppDLH - VulnerAppDLH is a vulnerable Android application s |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:57:57 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 82 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |