 安全软件
点击放大
GmapsXploit - GmapsXploit audits Google Maps, Places, Roads, and
项目说明
GmapsXploit
GmapsXploit audits exposed or unrestricted Google API keys and turns them
into high-impact findings. It tests a key against Google Maps, Places, Roads,
the newer Routes and Aerial View endpoints, and several Cloud services, then
shows the real risk: what the key can reach and what it costs. Instead of a
low se note, you get a clear impact and a ready-to-submit report.
<p align="center">
<img src="logo.png" alt="GmapsXploit" width="340">
</p>
<br>
What is GmapsXploit?
It is a single Bash script for bug bounty hunters, penetration testers, and
researchers who find Google API keys in web apps, mobile apps, or extensions.
It probes the key across more than thirty endpoints, detects restrictions such
as IP or referer limits, estimates billing impact from request , and
writes a Markdown report suitable for a program.
<br>
> An exposed Google API key is not a low finding when it is unrestricted and
> bills someone else's account.
Why this matters
Unrestricted Google API keys, especially with Places or the ad APIs
enabled, allow anyone to run up a bill on the owner's account. There are
public cases where costs reached tens of thousands of dollars in a short
time. GmapsXploit shows that impact with real numbers and a working proof.
Co
Ele, Timezone.
Photos.
Geolocation, Firebase Dynamic Links, Address .
Features
Installation
Bash 4.0 or later. No external dependencies.
Usage
1. Enter the target Google API key.
2. Watch the reconnaissance phase.
3. Review the financial impact results.
4. Use the generated report for submission.
Output
Each run writes two files:
gmapsxploit_report_*.txt - the full technical detail.bounty_report_*.md - a submission-ready report.Example
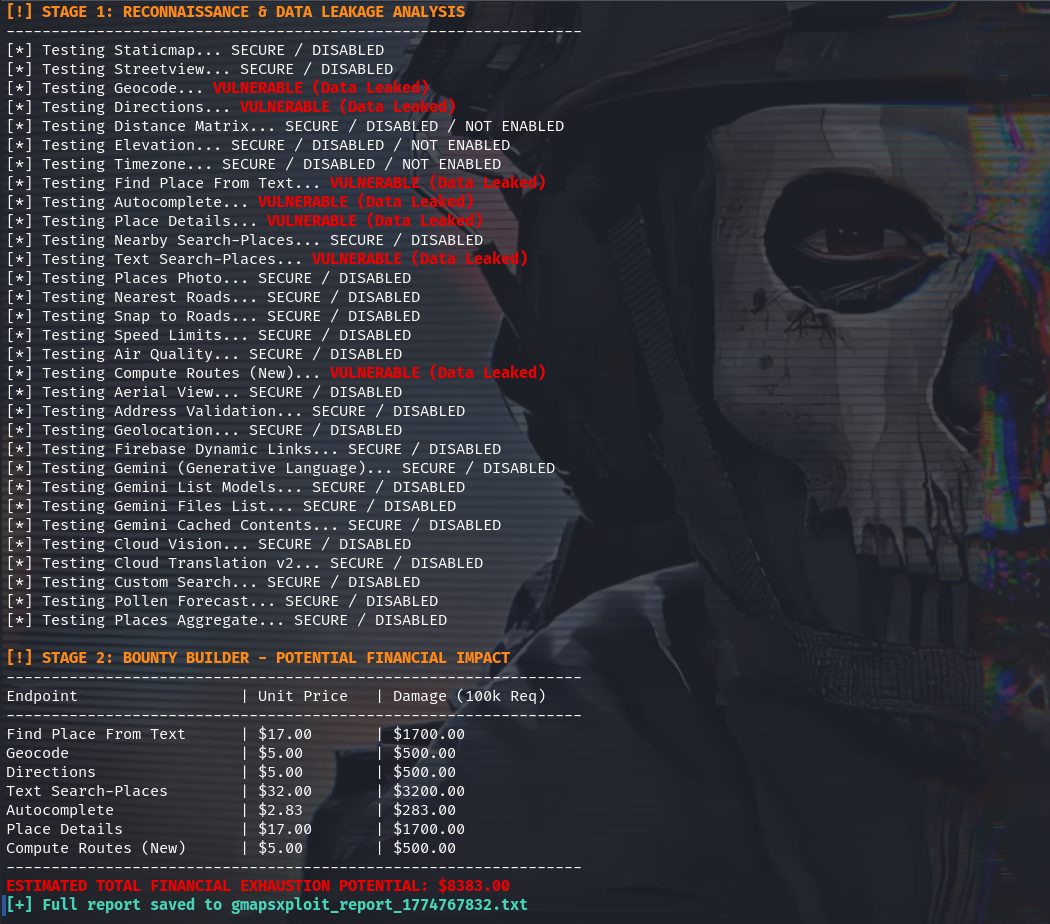
!Demo output
| Endpoint tested | Status |
|-----------------|--------|
| Static Maps | |
| Places Nearby | |
Generated report: gmapsxploit_report_1774767832.txt.
A sample report is in
examples/gmapsxploit_report_sample.txt.
Detection and defensi
Indicators of exposure to look for:
Mitigations:
Repository structure
Limitations
cap or bill differently.
References
Responsible use
GmapsXploit is built for authorized security testing. Run it only against
keys and accounts you own or ha permission to test. Using it
against systems without authorization may law.
Credits
Author: D34thSh0tX_X (github.com/DeathShotXD).
License
MIT. See LICENSE.
项目信息
开发语言:Shell
Star 数:13
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕GmapsXploit audits Google Maps, Places, Roads, and other API keys to find leaks, data exposure, and potential billing abuse, helping bug bounty hunters escalate low severity findings to critical with ready-to-submit reports.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | GmapsXploit - GmapsXploit audits Google Maps, Places, Roads, and |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:59:06 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 137 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |