 安全软件
点击放大
WAVS - WAVS: Web App Vulnerability Scanner [CS416 (Found
项目说明
WAVS: Web App Scanner
Course Project for CS416 (Foundations of Network Security and Cryptography)
O
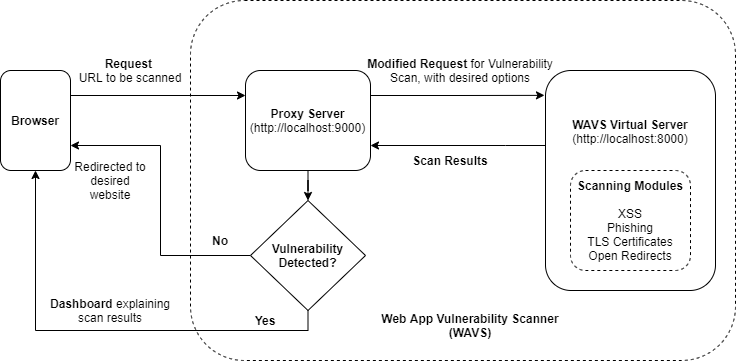
WAVS (Web App Scanner) is a tool to scan & test URLs for certain & security issues by simply inspecting the corresponding client-side website. The o system would include a server with modules for detecting the different , along with a proxy server, to direct requests from a browser to the ser while a website. The proxy could warn the user before redirecting to the website if some are found during the scan done by our server.
!WA
We intend to identify & assess the following security issues that a website may suffer from:
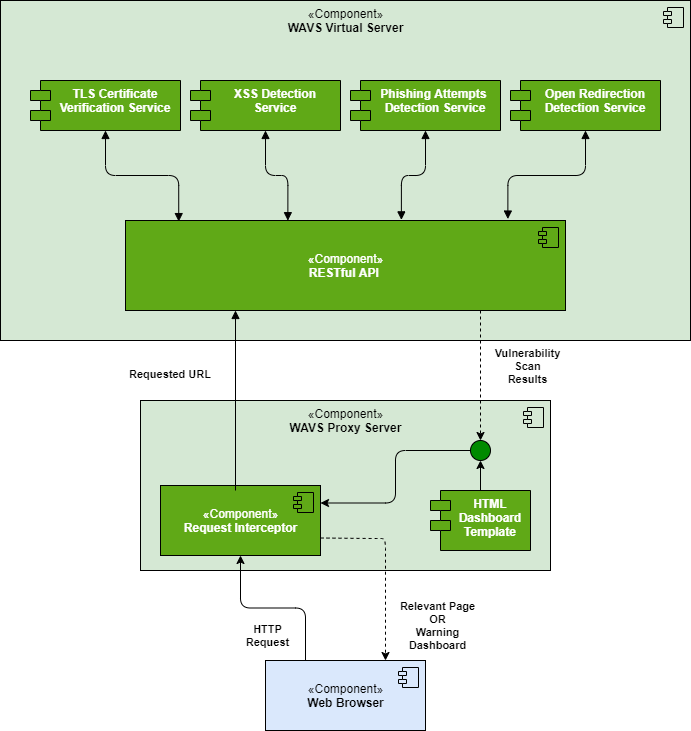
System Architecture
!WA Architecture
Usage
1. Fire up a terminal, clone this repository using git clone & cd into it
2. Start the WA using the following steps _(Python 3 required)_:
This will start the WA server at
3. Fire up another terminal & start the WA using the following steps _(Node.JS required)_:
This will start the WA at with default settings (full scan). To start the proxy for a selective scan, use the following:
4. Now open a browser & type in the address bar. This will open up the WA page which should look as follows:
!Landing Page Image
5. To perform a scan for any URL, just append /<URL> to the proxy address in the address bar.
For example, if you wish to perform a scan for , the contents of the address bar should look like:
WAVS will perform the scan within 10-20 s & return a dashboard containing the details of the potential present in the website.
WA
After performing a scan, WA a dashboard containing details about the . Following are the results of a scan performed on
<di="text-align: center;">
<img src="./figures/dashboard/.png" width="96%">
<img src="./figures/dashboard/cert_details.png" width="48%">
<img src="./figures/dashboard/xss_details.png" width="48%">
</div>
(Dummy) Website
To demonstrate the full capacity of WAVS at once, we created a dummy website, with some inherent that WAVS can detect:
?url= query parameter in the addressThe website was de using express (Node.js) & deployed on Heroku. It can be accessed at:
The code for this website can be found here.
Reports
***
<p align="center">Created with ❤️ by <a href=" target="_blank">Tezan Sahu</a>, <a href=" target="_blank">Shreya Laddha</a>, <a href=" target="_blank">Saa</a> & <a href=" target="_blank">Amol Shah</a></p>
项目信息
开发语言:Jupyter Notebook
Star 数:12
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕WAVS: Web App Vulnerability Scanner [CS416 (Foundations of Network Security and Cryptography) Project]展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | WAVS - WAVS: Web App Vulnerability Scanner [CS416 (Found |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:59:36 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 450 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |