 安全软件
点击放大
aactl - Google Container Analysis data import utility, sup
项目说明
aactl
Google Artifact Analysis (AA) service data import utility, supports OSS scanner reports, SLSA pro, and sigstore attestations.
AACTL is a sample tool that shows Google Cloud customers who use Artifact Registry how they can ingest detected by supported scanning tools into Artifact Analysis. Once ingested, will be stored & managed alongside detected by Artifact Analysis. are within Artifact Registry UI, SDS Security Insights, gcloud, and Artifact Analysis API (Container Analysis).
AACTL can also ingest SLSA Build Pro generated by SLSA GitHub Generator.
> Detailed installation instruction are a here.
Usage
aactl supports imports of two data types: and attestation.
> In addition to CLI, aactl can also be used in your CI/CD pipeline as a Google Cloud Build builder (example) or GitHub Actions action (examples).
To import output by either grype, snyk, trivy scanners, start by exporting the report in JSON format:
* grype
grype --add-cpes-if-none -s AllLayers -o json --file report.json $image
* snyk
snyk container test --app-vulns --json-file-output=report.json $image
* trivy
tri --format json --output report.json $image
Once you have the file, importing that file into AA using aactl:
> The $image in the abo is the fully qualified URI of the image including its digest (e.g. us-docker.pkg.de/repo/image:397d453...).
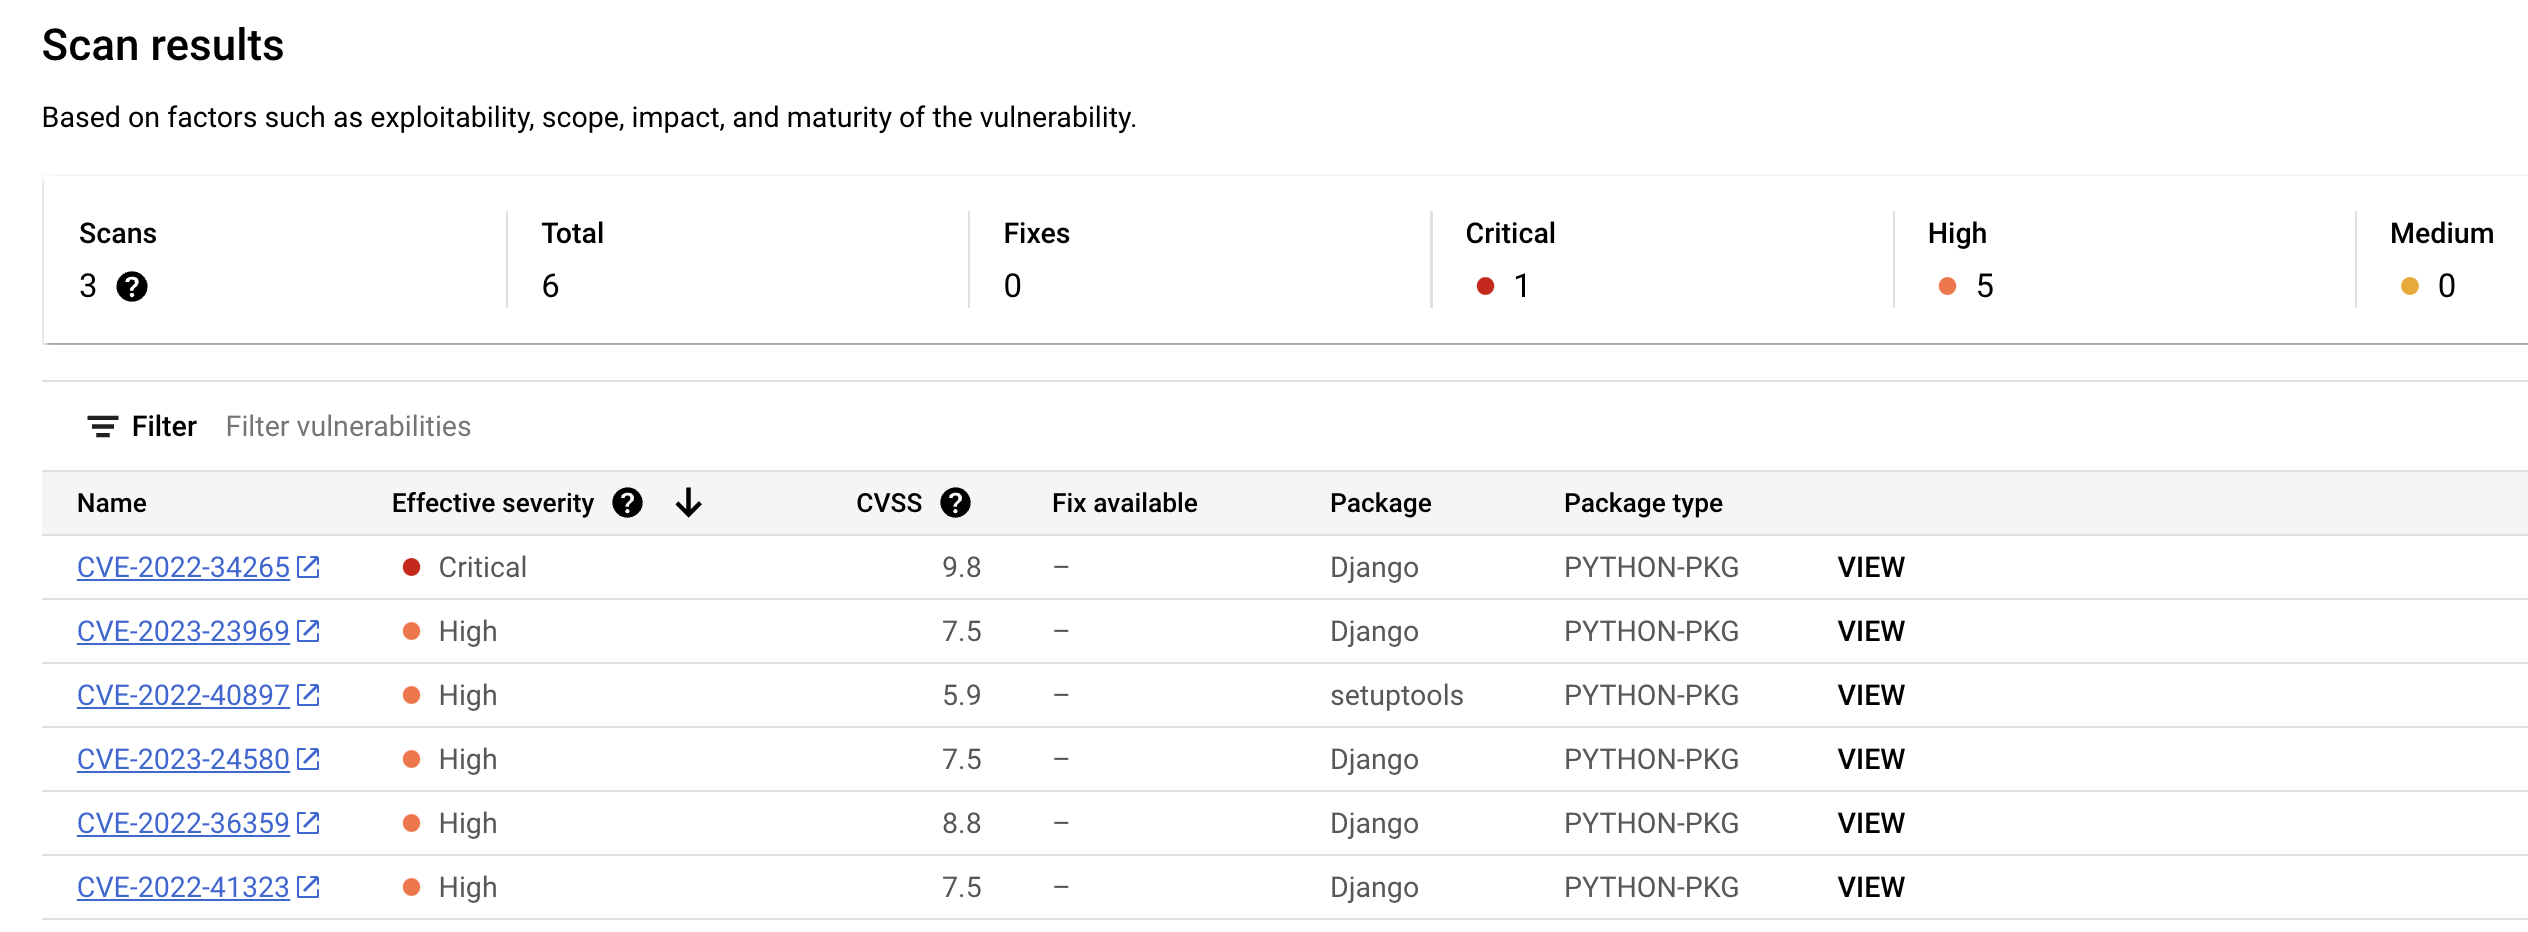
To review the imported in GCP:
You can also na to Artifact Registry to view the there.

Attestation
In addition to , aactl can also import sigstore attestations:
> The $image in the abo is the fully qualified URI of the image including its digest (e.g. us-docker.pkg.de/repo/image:397d453...).
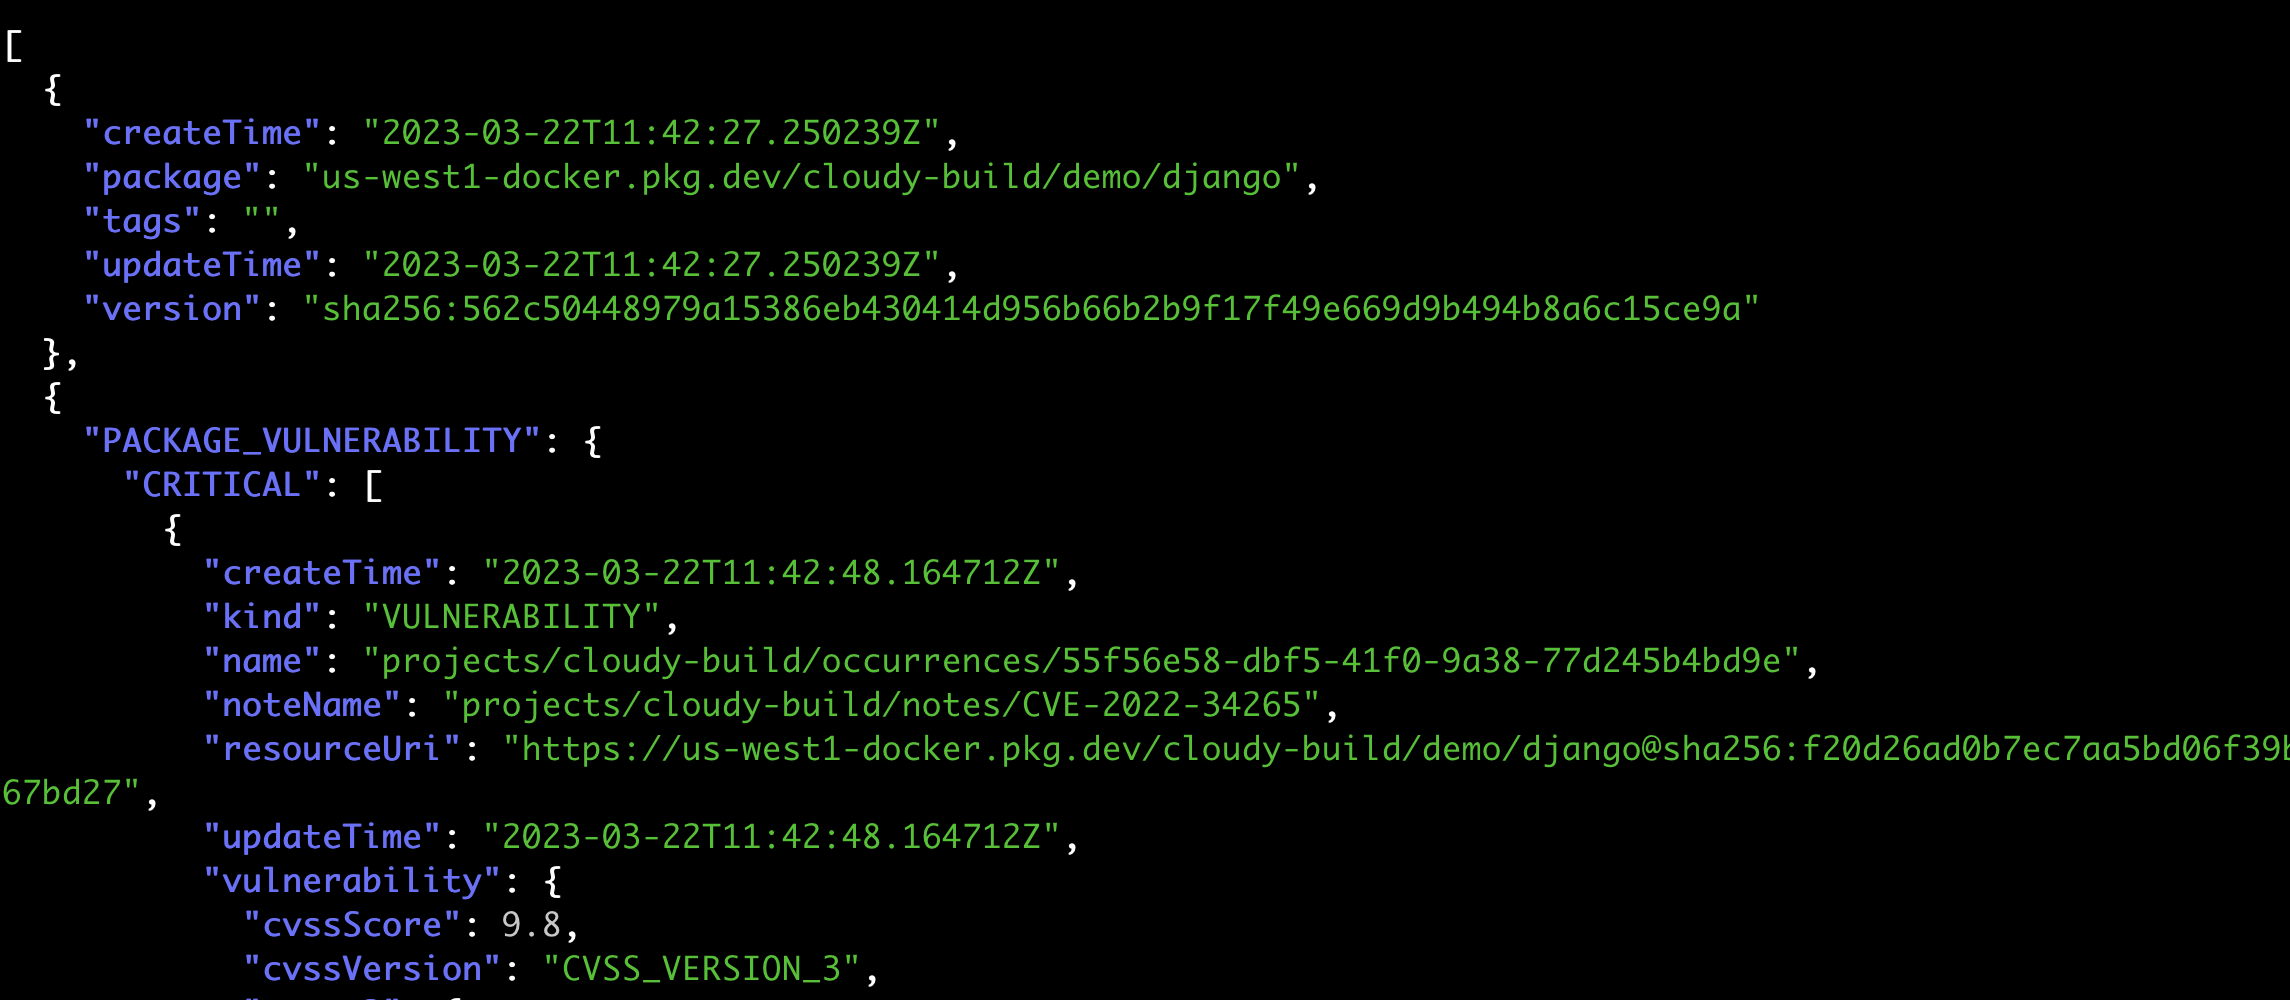
The imported data can be accessed using gcloud:
The resulting JSON will look something like this:

The data can also be in Software Delivery Shield side panel:

> SLSA level is currently not parsed properly, WIP.
Contributing
Entirely new samples are not accepted. Bug fixes are welcome, either as pull
requests or as GitHub issues.
See CONTRIBUTING.md for details on how to contribute.
Licensing
Code in this repository is licensed under the Apache 2.0. See LICENSE.
项目信息
开发语言:Go
Star 数:12
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Google Container Analysis data import utility, supports OSS vulnerability scanner reports, SLSA provenance and sigstore attestations.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | aactl - Google Container Analysis data import utility, sup |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 22:59:38 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 416 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |