 安全软件
点击放大
Xninjaz - Xninjaz is a powerful and versatile multi-vulnerab
项目说明
Xninjaz
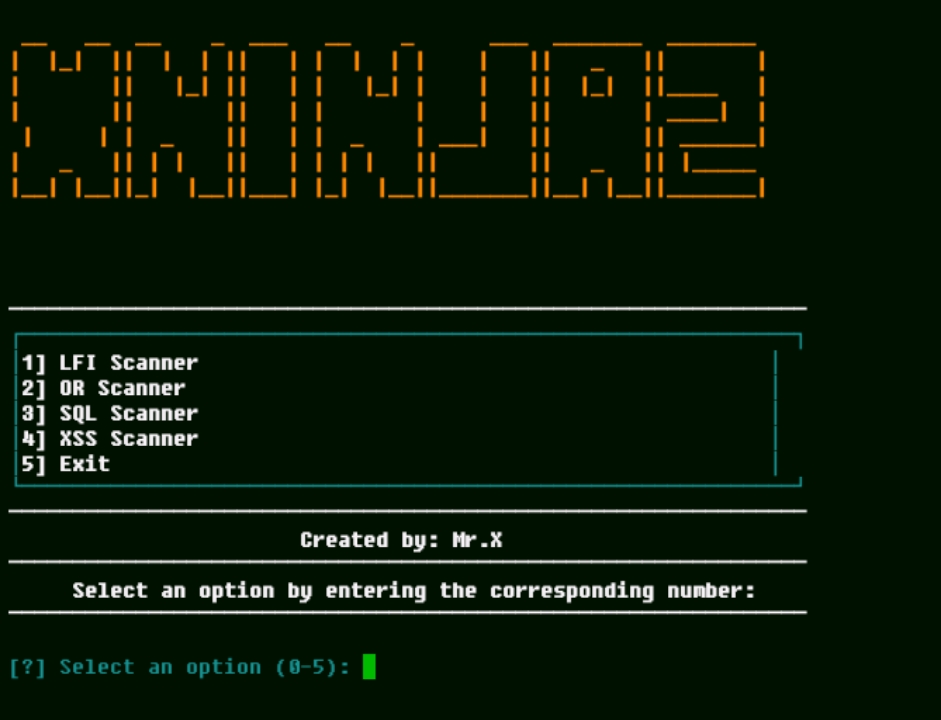
!Xninjaz preview
introduction
Xninjaz is a powerful and multi- scanner designed to detect web application , including Local File Inclusion (LFI), Open Redirects (OR), SQL Injection (SQLi), and Cross-Site Scripting (XSS). This tool was created by Mr.X
Instalations
Features
Requirements
webdri==4.0.2selenium==4.24.0aiohttp==3.10.5beautifulsoup4==4.12.3colorama==0.4.6rich==12.6.0requests==2.28.1Instructions
Input Information:
After the scan completes, you will have the option to save the URLs found to be to a file for future reference.
Customization
Xninjaz allows for levels of customization to fit your specific testing needs:
Obser
This is a tool for education only, I am not responsible for any misuse
Original Author
<a href=" src=" alt=""/></a>
<<< If you copy , Then Give me The Credits >>>
CONNECT WITH ME :
![Instagram]()
![Instagram]()
![Instagram]()
![Instagram]()

![Instagram]()
If you want to donate, click on the button
<a href=" title="Donate" src="
---
<p align="left">
<img src=" alt="Thanks badge"/>
</p>
---
项目信息
开发语言:Python
Star 数:12
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Xninjaz is a powerful and versatile multi-vulnerability scanner designed to detect various web application vulnerabilities, including Local File Inclusion (LFI), Open Redirects (OR), SQL Injection (SQLi), and Cross-Site Scripting (XSS). This tool was created by Mr.X展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Xninjaz - Xninjaz is a powerful and versatile multi-vulnerab |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:00:01 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 465 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |