 安全软件
点击放大
aur_checker - 🔍 A CLI tool for security analysis of Arch AUR PKG
项目说明
aur_checker
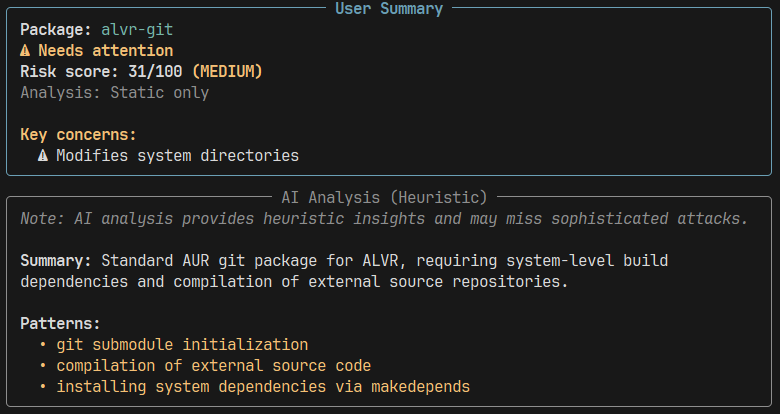
!demo
A command-line tool for analyzing Arch Linux AUR PKGBUILD files to identify security risks. Uses static analysis with optional AI-powered inspection.
![Build Status]()
![CodeQL]()

![Python 3.10+]()
O
aur_checker inspects PKGBUILD files for security and suspicious patterns before you build packages. It combines context-aware static analysis with optional AI review to produce explainable risk assessments.
Analysis pipeline:
Key features:
Installation
Requires Python 3.10 or later.
Quick Start
Configuration
API Key (Optional)
AI analysis is optional. aur_checker works without an API key using static analysis only.
To enable AI analysis, set your Google Generative AI API key:
Optional Settings
| | Purpose | Default |
|----------|---------|---------|
| AURCHECKER_AI_MODEL | AI model to use | gemini-3.1-flash-lite |
| AURCHECKER_AI_TIMEOUT | Request timeout (milliseconds) | 120000 |
How It Works
Analysis Process
1. Fetch - Downloads PKGBUILD from AUR CGit
2. Static Analysis - Context-aware pattern detection (skips comments, distinguishes legitimate operations)
3. Metadata - Retrieves AUR RPC v5 package information (maintainer, votes, age)
4. Trust Signals - E maintainer history, popularity, update patterns, out-of-date status
5. Scoring - Computes 0-100 risk score with explainable breakdown of contributing factors
6. AI Review (optional) - Heuristic analysis for additional context if API key is set
7. - Final assessment: Safe to review / Needs attention / High risk
Risk Assessment
| Score | Risk Level | Recommendation | Exit Code |
|-------|-----------|-----------------|-----------|
| 0-20 | Low | Safe to review | 0 |
| 21-50 | Medium | Manual review recommended | 2 |
| 51-100 | High | Do not use | 1 |
Note: Without AI, static score is used directly (more conser). With AI enabled, final score is 70% static + 30% AI.
Output Modes
Human output (default):
--JSON output (--json):
Exit Codes (for CI integration)
Security Signals
The static analyzer detects:
| Signal | Pattern | Risk Weight | Rationale |
|--------|---------|-------------|-----------|
| remote_exec | Downloads piped to shell (curl/wget → bash) | 50-70 | Direct code execution from internet |
| obfuscation | Base64, hex, eval, encoding layers | 15-35 | Attempts to hide behavior |
| system_mod | Writes to /etc, /boot, /usr/lib/systemd | 30 | Modifies sensiti locations |
| maintainer_changed | Maintainer change detected | 15 | Increased risk during transitions |
| orphan_adopted | Package without acti | 10 | No owner to respond to issues |
| pkg_manager | npm, pip, cargo, go, gem (outside deps) | 8-12 | Risk if used in build scripts |
| external_calls | Non-source HTTP/HTTPS URLs in execution | 5-15 | Network activity in build context |
Trust Signals
| Signal | Description |
|--------|-------------|
| Package age | Days since first submission |
| Maintainer history | stable / changed / orphan_adopted / new |
| Update frequency | Days since last update |
| Popularity | Vote count, >100 votes = popular |
| Out of date | Flagged by users as outdated |
What aur_checker Can and Cannot Detect
✅ CAN detect:
curl | bash)❌ CANNOT detect:
See SECURITY.md for the complete threat model, limitations, and recommendations.
De
Running Tests
Project Structure
Limitations
Always read PKGBUILDs manually before building AUR packages.
Contributing
Contributions welcome. Please open an issue or pull request on GitHub.
License
MIT License. See LICENSE.md for details.
Security
See SECURITY.md for the threat model, what aur_checker can and cannot detect, and how to report security issues.
---
Maintainer:
Repository: github.com/programmersd21/aur_checker
项目信息
开发语言:Python
Star 数:12
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕🔍 A CLI tool for security analysis of Arch AUR PKGBUILDs展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | aur_checker - 🔍 A CLI tool for security analysis of Arch AUR PKG |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:01:12 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 266 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |