 安全软件
点击放大
Shield-Eye-Core - Network security scanner. Nmap-powered port scanni
项目说明
<di="center">
🛡️ ShieldEye Core
Network Security Scanner for Linux
*Port scanning • CMS detection • Security headers analysis*
![License: MIT]()
![Python]()
![GTK]()
![Nmap]()
Features • Quick Start • Screenshots • Documentation • Architecture
---
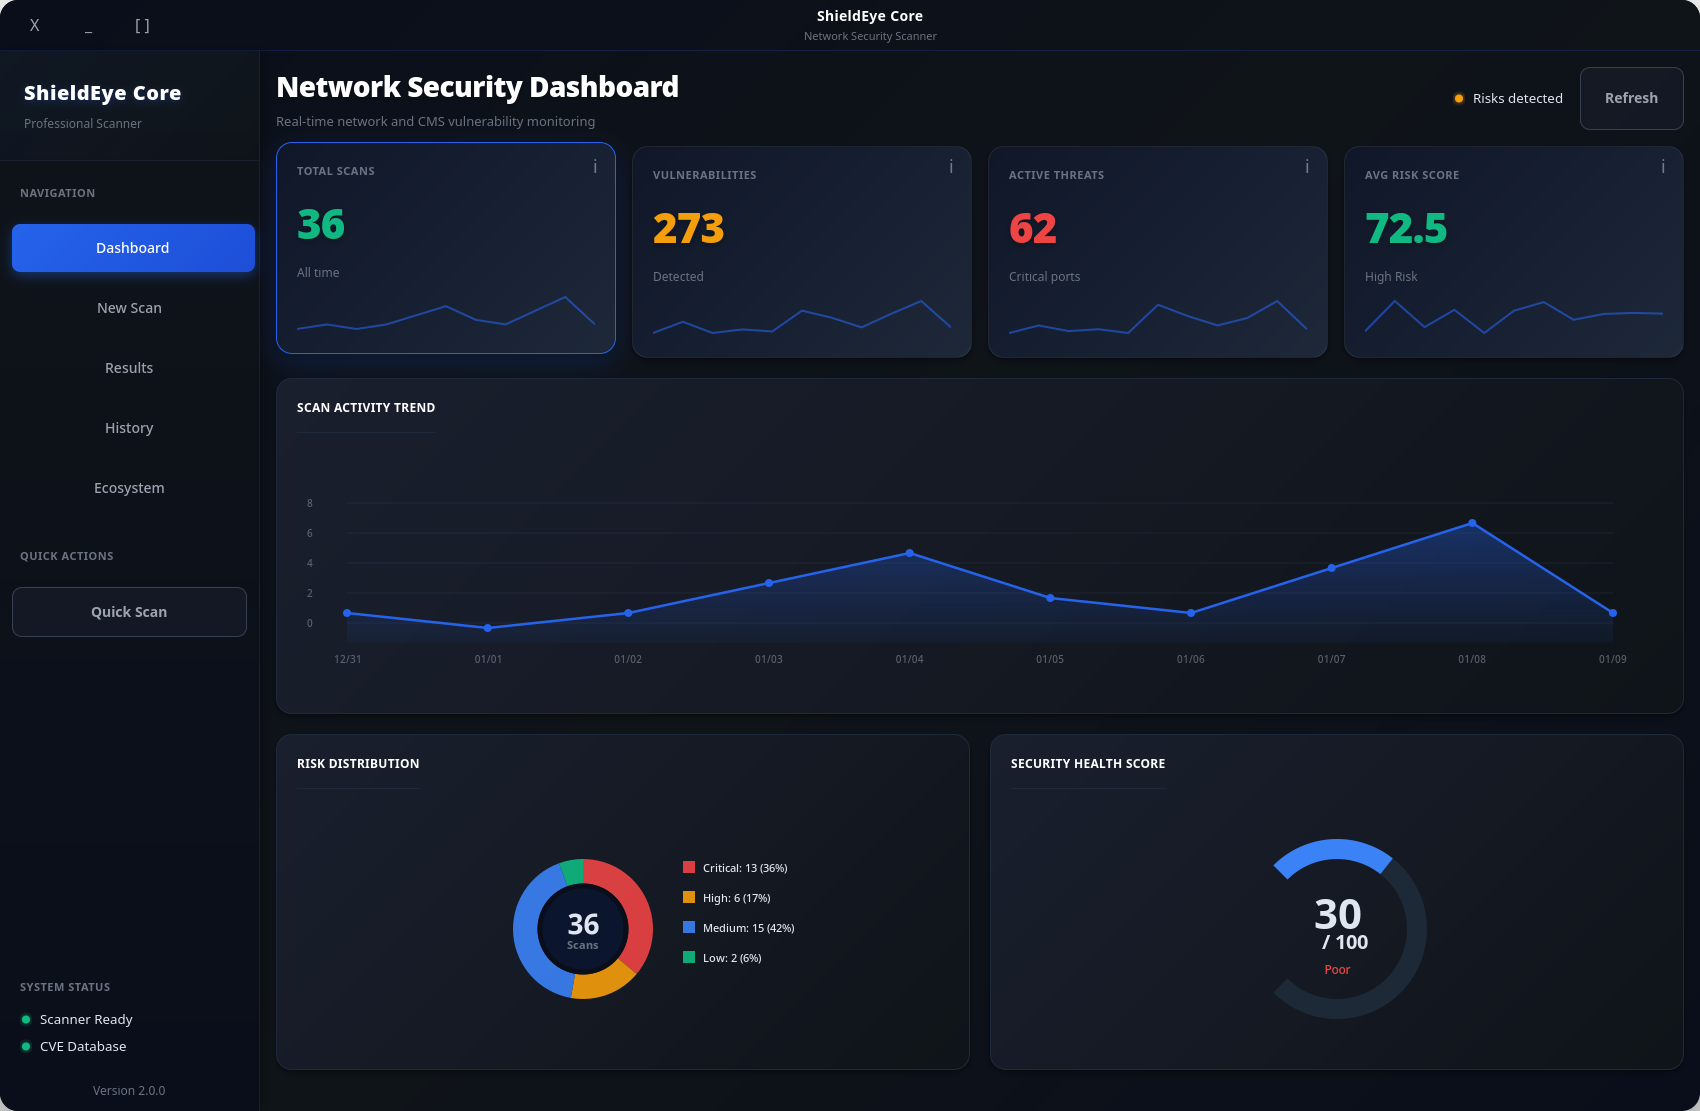
!ShieldEye Core Dashboard
</div>
---
What is ShieldEye Core?
ShieldEye Core is a desktop network security scanner. It wraps Nmap for port and
service discovery, fingerprints common CMS platforms and cross-references their
against the CIRCL C, and grades a site's HTTP security
headers. Results are shown in a native GTK 4 GUI (there is also a CLI).
It's aimed at security researchers, pentesters, and sysadmins who want a quick,
local read on a host or a small network, not a replacement for a full
suite.
> ⚠️ Authorized use only. Only scan systems you own or ha written
> permission to test. Port scanning and probing can be disruptive
> and, in many jurisdictions, illegal without consent.
---
Features
<table>
<tr>
<td width="50%">
Scanning
192.168.1.0/24, up to /16)</td>
<td width="50%">
Web Analysis
</td>
</tr>
<tr>
<td width="50%">
Interface
</td>
<td width="50%">
Safety & robustness
cloud-metadata addresses are rejected, and HTTP redirects are re-checked
pytest)</td>
</tr>
</table>
---
Screenshots
<di="center">
| Dashboard | Scan Configuration |
|:---------:|:------------------:|
| !Dashboard | !Scan Config |
| *Security posture and recent activity* | *Scan setup with single / network / full modes* |
| Results | History |
|:-------:|:-------:|
| !Results | !History |
| *Findings with se levels* | *Scan timeline and trends* |
</div>
---
Architecture
A modular Python backend behind a native GTK frontend:
Tech Stack
| Layer | Technology |
|-------|------------|
| Frontend | GTK 4.0, Python 3.10+, PyGObject |
| Backend | Python 3.10+, Nmap, Requests |
| Scanning | python-nmap, BeautifulSoup4 |
| Security | OpenSSL, cryptography, dnspython |
| Reports | ReportLab (PDF generation) |
| CVE Data | CIRCL C API |
---
Quick Start
Prerequisites
| Requirement | | Notes |
|-------------|---------|-------|
| Python | 3.10+ | |
| GTK | 4.0+ | system package (not pip) |
| PyGObject | - | system package, see below |
| Nmap | recent | system installation |
| Linux | - | tested on Arch, Ubuntu/Debian, Fedora |
1. Install system dependencies
GTK and PyGObject (gi) are provided by your distro, not by pip:
2. Get the code and install Python deps
The easiest path is the launcher, which creates the **with access to
the system GTK bindings** and installs e:
Prefer to do it by hand? The --system-site-packages flag is required so the
venv can see the system gi/GTK modules:
3. Grant Nmap capabilities (optional but recommended)
Some Nmap features (SYN scan, OS detection) need raw-socket pri. Granting
capabilities once avoids running the whole app as root:
4. Launch
5. CLI mode
---
Using run.sh
run.sh is an interacti (no subcommands) with four options:
Tests are run directly with pytest (see De).
---
Configuration
Scan parameters, rate limits, timeouts, and alert thresholds live inbackend/config.py. See STRUCTURE.md for the layout.
Core dependencies: python-nmap, requests, beautifulsoup4, cryptography,reportlab, plus system PyGObject/GTK. Full list in requirements.txt.
---
Documentation
---
API Usage
---
De
---
Contributing
Contributions are welcome.
1. Fork the repository
2. Create a branch (git checkout -b my-change)
3. Commit your changes
4. Push and open a Pull Request
Please keep to PEP 8, add type hints where they help, and cover new behavior
with tests.
---
License
MIT - see LICENSE.
For educational and authorized security testing only.
---
Acknowledgments
---
Related Projects
Part of the ShieldEye set of tools:
---
<di="center">
Report a Bug • Request a Feature
</div>
项目信息
开发语言:Python
Star 数:11
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕Network security scanner. Nmap-powered port scanning, CMS detection with live CVE lookup (CIRCL), security headers scoring and SSL/TLS analysis. GTK4 desktop GUI. Part of the ShieldEye toolkit.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | Shield-Eye-Core - Network security scanner. Nmap-powered port scanni |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:01:59 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 494 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |