 安全软件
点击放大
ms17_010_scanner - This simple SMB vulnerability MS17-010 scanner is
项目说明
ms17_010_scanner
This simple SMB __MS17-010__ scanner is de to help security professionals to quickly check if a computer is
to __MS17-010__ which is used by WannaCry and Petya malwares.
What this scanner will do:
* Connect to the target computer using port 445.
* Send __"SMB_COM_NEGOTIATE"__ and __"SMB_COM_SESSION_SETUP_ANDX"__ packets to establish an SMB session.
* Connect to the IPC$ share on the target computer by sending __"SMB_COM_TREE_CONNECT_ANDX"__ packet with TreeID set
to __\\<TARGET COMPUTER's IP>\IPC$__ and UserID set to the value returned by the server in the previous response.
* Check for __MS17-010__ by sending an __"SMB_COM_TRANSACTION"__ packet, containing PeekNamedPipe subcommand set to FileID = 0.
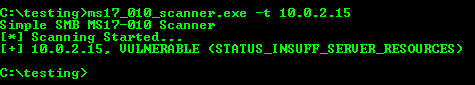
* Check for the error response code __0xC0000205 (STATUS_INSUFF_SER)__. If the code is found that means the target computer's Windows operating system is to __MS17-010__.
Downloads
ms17_010_scanner Windows executable file can be downloaded here
Usage
* Scan a target computer
* Scan a list of computers
Screenshots
<img align="center" src="./1.PNG" alt="Screenshot #1" />
Contact
项目信息
开发语言:Python
Star 数:10
技术要点
该项目属于安全软件方向的开源资源,代码结构清晰,适合安全研究人员学习参考。项目围绕This simple SMB vulnerability MS17-010 scanner is developed to help security professionals to quickly check if a computer is vulnerable to MS17-010 vulnerability which is used by WannaCry and Petya malwares.展开,提供了可运行的实现,对理解相关安全机制、工具原理与攻防技术具有较高的研究价值。
从技术实现角度看,此类项目的核心在于对底层原理的深入理解与工程化落地。开发者在研究过程中可以结合官方文档与社区讨论,梳理项目的初始化流程、核心模块职责与数据流转,逐步掌握其中的技术细节与设计思路。
使用与学习建议
1. 下载源码压缩包,解压到本地环境。
2. 根据项目类型准备对应的运行环境与依赖。
3. 按照 README 中的步骤完成配置与部署。
4. 在隔离的测试环境中运行验证,避免影响生产系统。
免责声明
本资源来源于开源社区,仅供安全研究、技术学习与合法授权范围内的攻防演练使用,请勿用于任何非法或侵害他人权益的用途。使用本项目产生的一切后果由使用者自行承担。
| 资源标题 | ms17_010_scanner - This simple SMB vulnerability MS17-010 scanner is |
| 所属分类 | 安全软件 |
| 发布作者 | admin |
| 发布时间 | 2026-10-05 23:02:18 |
| 下载权限 | 免费下载 |
| 附件数量 | 2 个下载链接 |
| 浏览次数 | 142 |
| 讨论数量 | 0 |
| 主题状态 | 正常讨论中 |